
CrackQL
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
api-security-testingfuzzingpassword-attacks+2
353
nicholasaleks/crackqlGraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
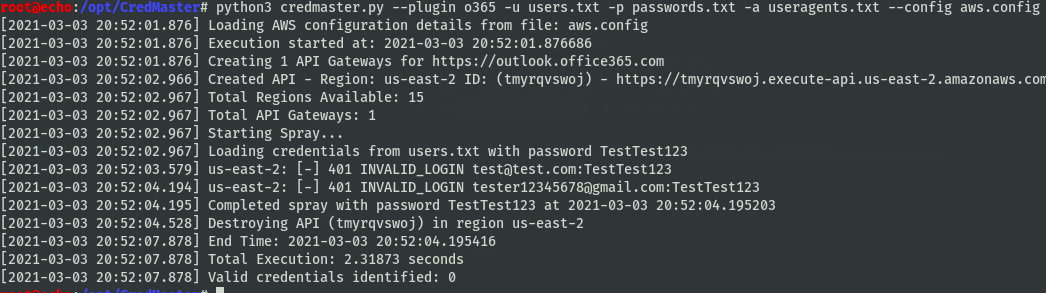 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
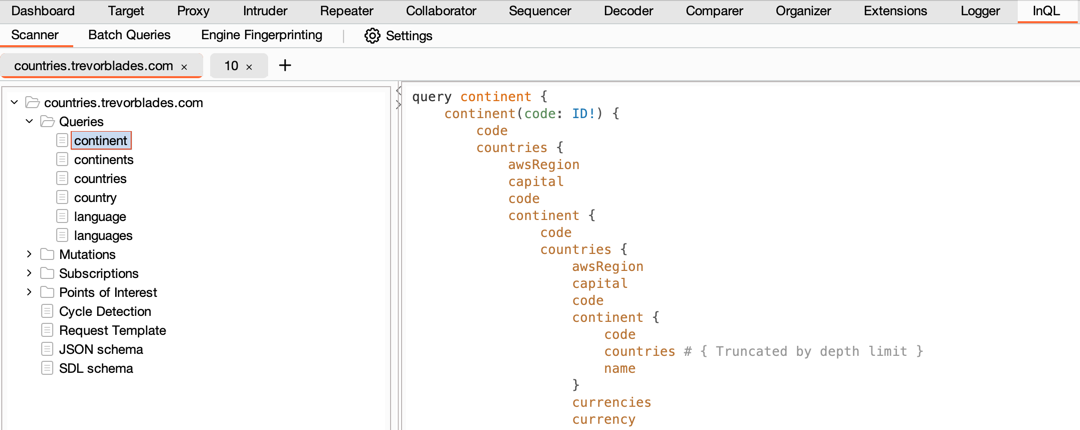 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
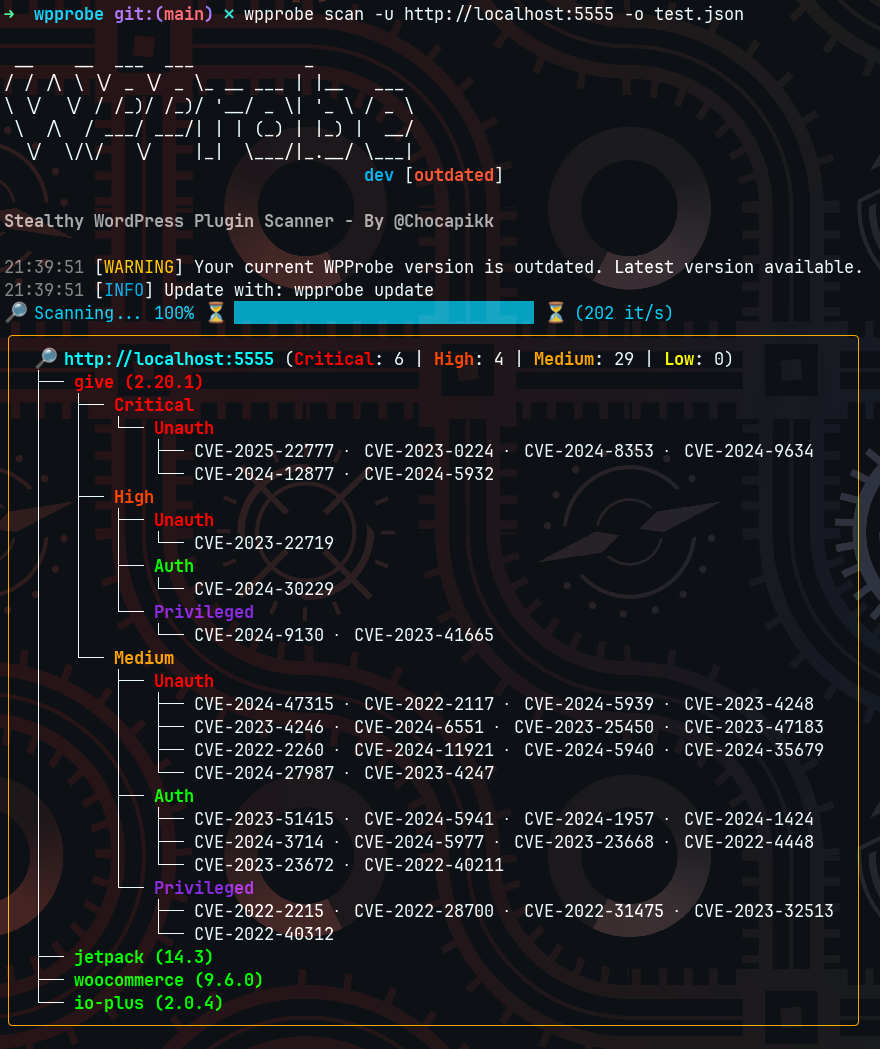 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
 sn1r/mass-assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…
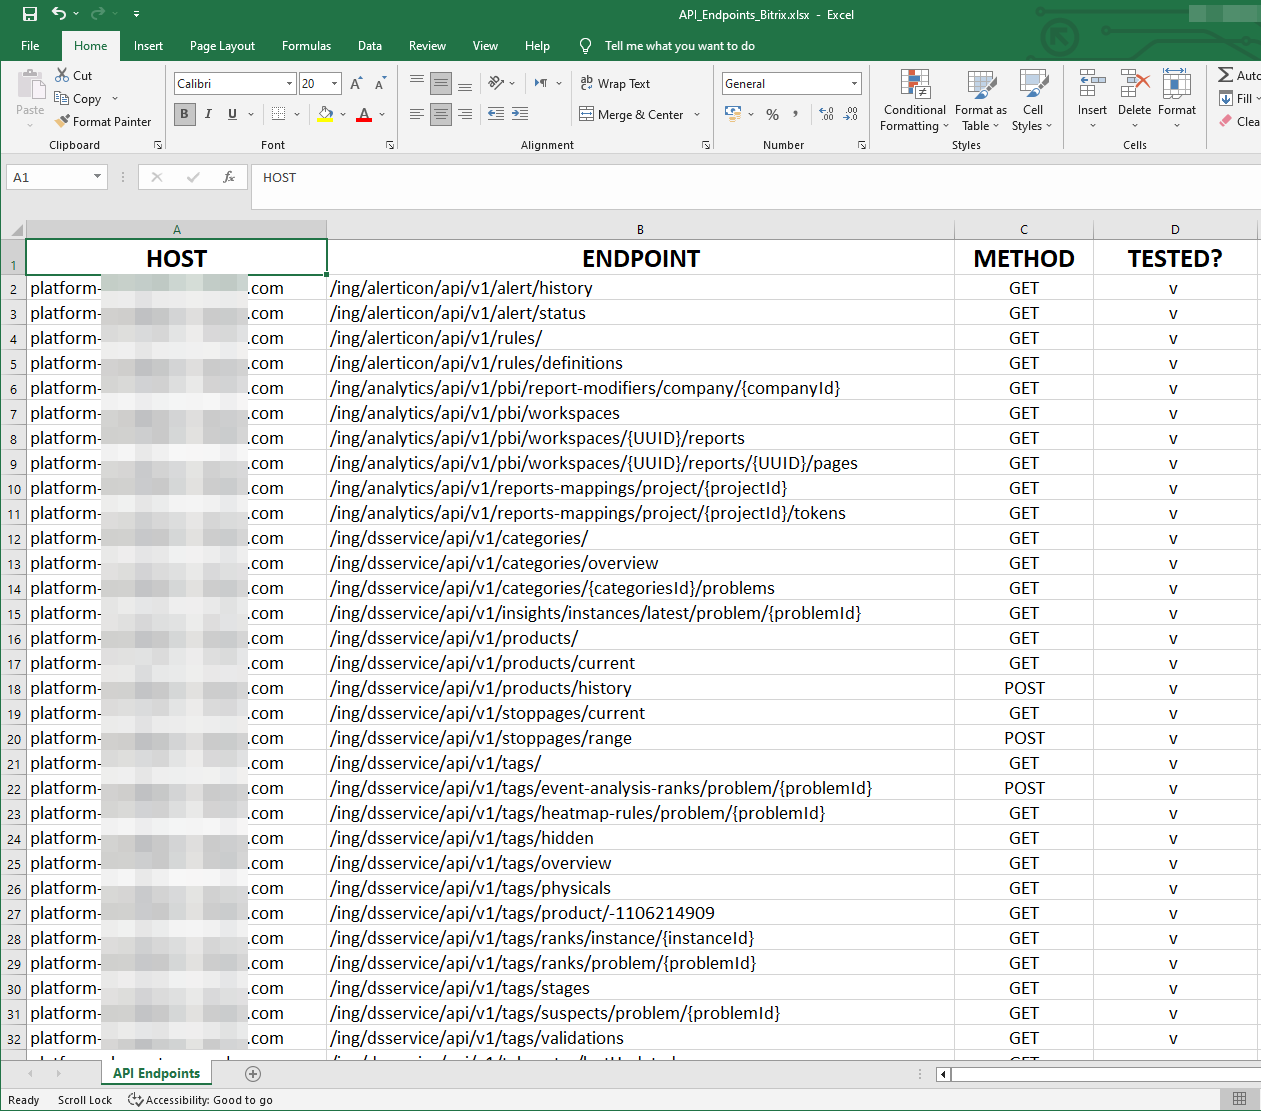 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
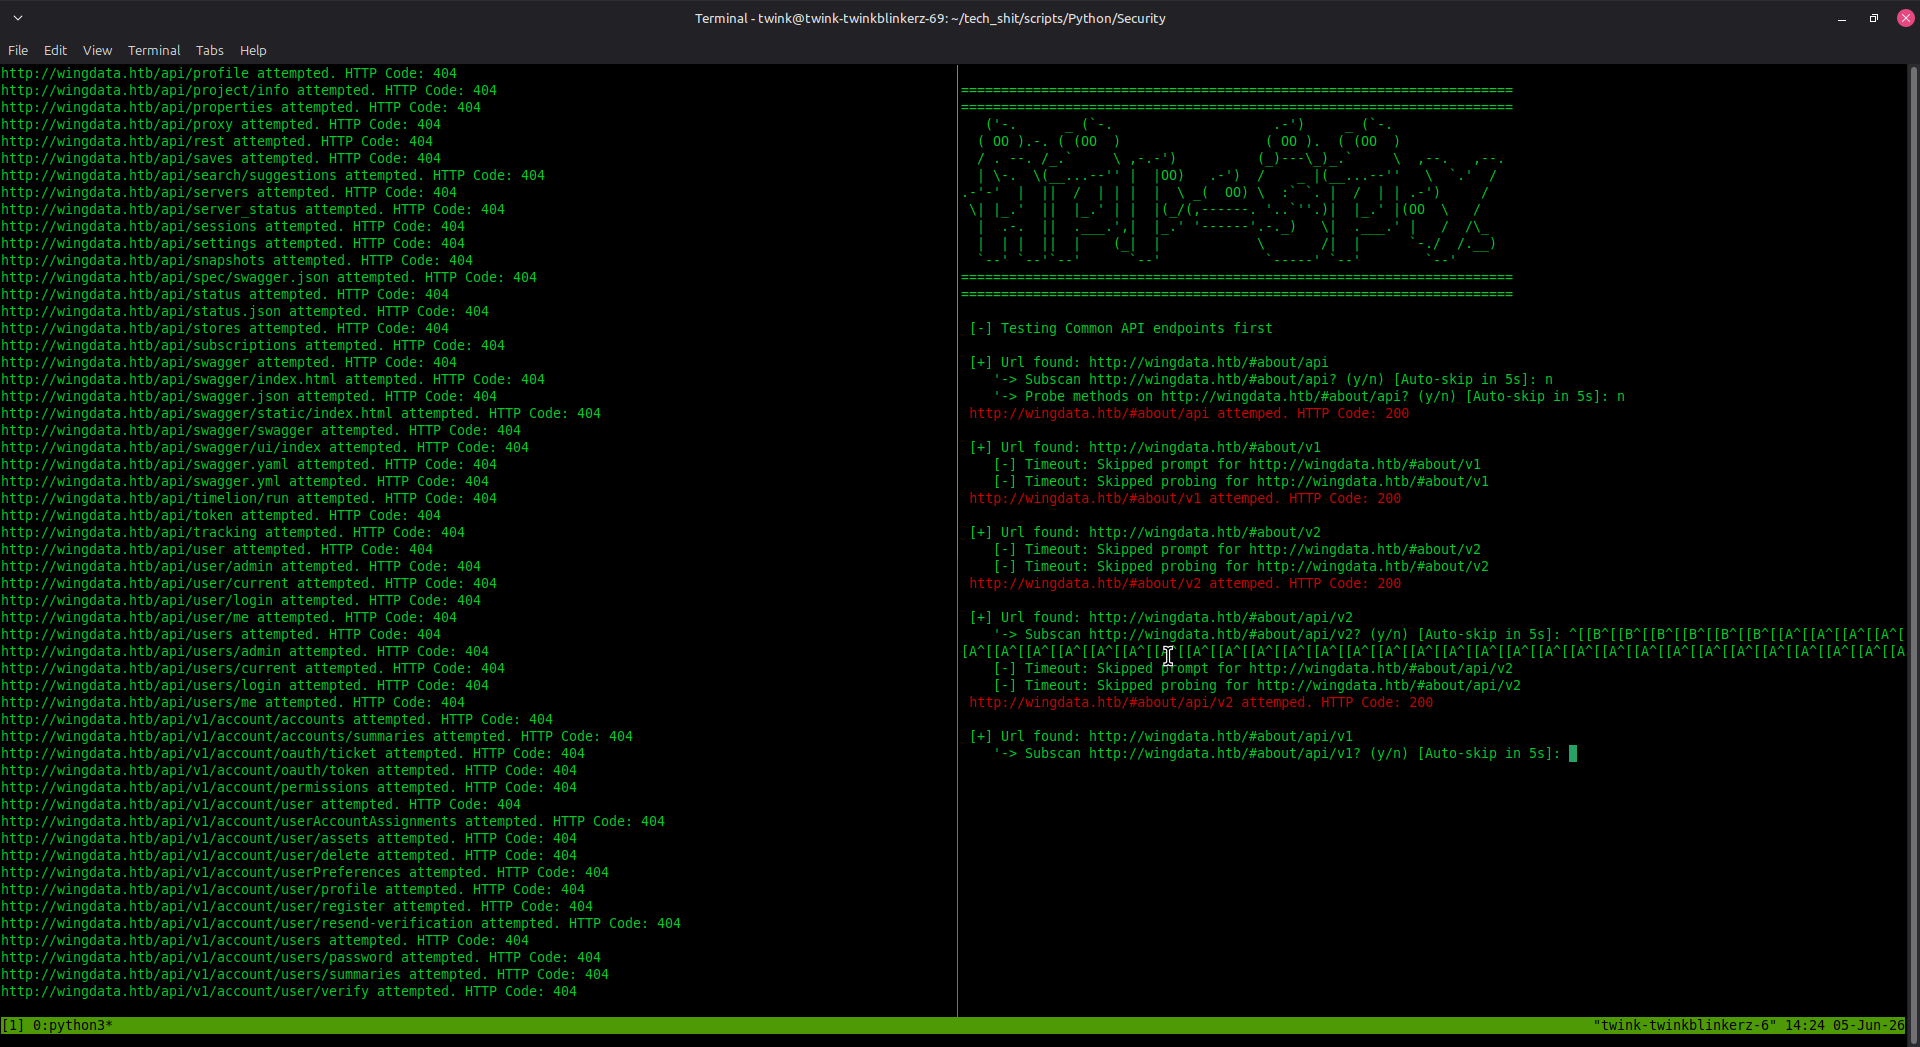 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
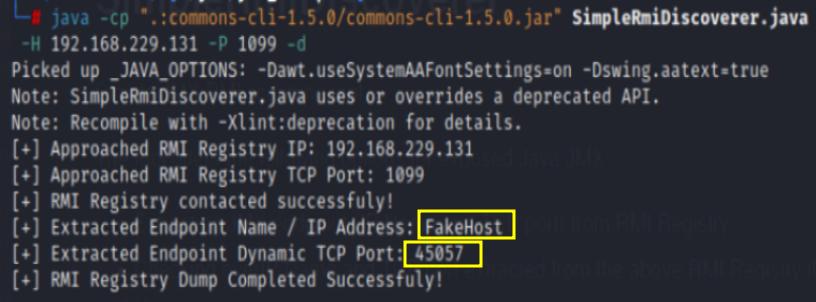 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool