
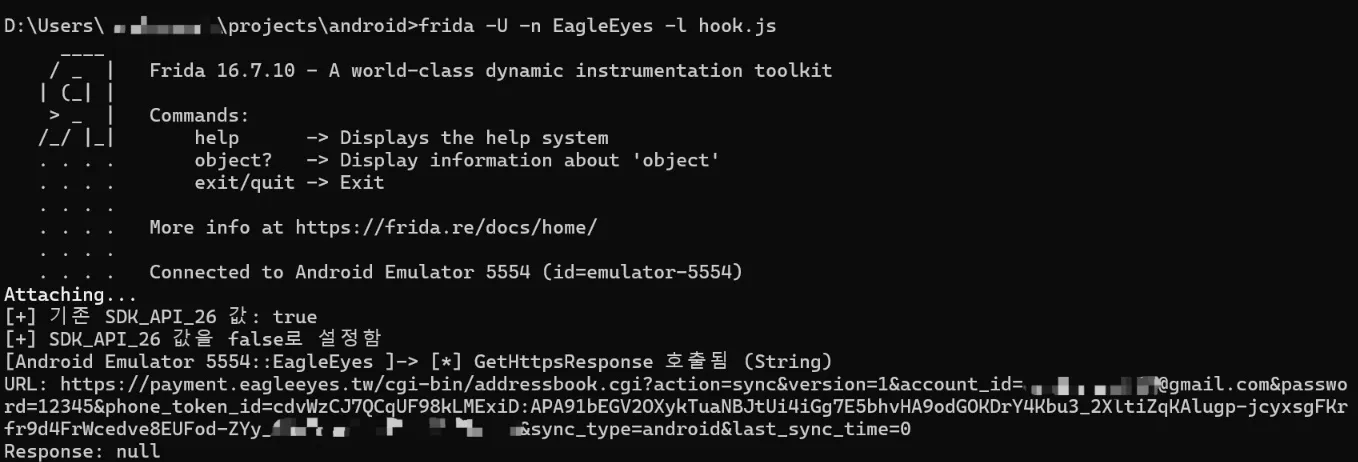
CVE-2025-46408
 shinycolumn/cve-2025-46408
Improper Hostname Verification in EagleEyes Lite Android Application
android-securityeducationexploitation+3
21 year ago
shinycolumn/cve-2025-46408Improper Hostname Verification in EagleEyes Lite Android Application
 koozxcv/cve-2014-7911
PoC and exploit for CVE-2014-7911, a privilege escalation vulnerability in Android. Provides a working exploit for security testing and vulnerability…
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 iwallplace/cve-2026-26897-ecoonline-deeplink
Public advisory & PoC for CVE-2026-26897 — Deep Link Bypass in EcoOnline EHS Android (com.airsweb.v10), fixed in 0.2.500
 shaikusaf/packages_apps_settings_aosp10_r33_cve-2020-0416
Android Settings app patch for CVE-2020-0416, addressing a security vulnerability in AOSP 10.
 satheesh575555/packages_apps_settings_aosp10_r33_cve-2020-0416
Android Settings package with security patch for CVE-2020-0416, addressing a vulnerability in AOSP 10.
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 sunnyjiang/shellshocker-android
This is an Android Application that helps you detect if your machine that run bash is vulnerable by CVE-2014-6271
 dsp-security-workflows/cve-2022-20223
A simple bash script for exploiting Android 10/11/12 using cve-2022-20223.
 kimocoder/android_kernel_oneplus_avicii
OnePlus Nord (avicii) NeverSettle Kernel Source
 seqred-s-a/cve-2019-14326
Privilege escalation in Andy emulator
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
 nanopathi/framework_base_aosp10_r33_cve-2021-0472
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…
 m00ddy/cve-2026-0073-android-client-tls-auth-bypass
translating original python exploit to C
 webpage-gh/cve-2025-10184-poc
Proof-of-concept exploit for CVE-2025-10184, demonstrating a permission bypass in the OxygenOS Telephony provider on Android devices.
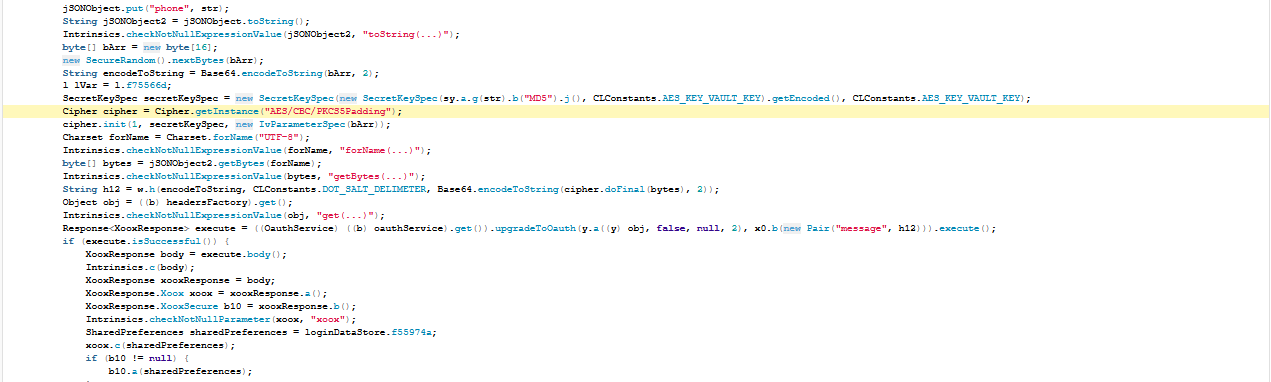 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…