
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/lienby/pssroot
Android SecurityPrivilege EscalationVulnerability AnalysisExploitationPenetration TestingMobile Security
GitHublienby/pssroot

PSSRoot

One-Click-Root program based on CVE-2016-5195, that works on the old 'PlayStation Certified' android devices

View Repository
21291 year agoNot yet reviewed
Share

One-Click-Root program based on CVE-2016-5195 or "DirtyCOW";

this should work with the PlayStation Certified devices, but it may come in handy for other old android devices too;

Tested on :

Xperia Play (Android 2.3; Kernel 2.6.32.9)
Xperia S (Android 4.1.2; Kernel 3.4.0+1.0.21100-313065)
Sony Tablet P (Android 3.2; Kernel 2.6.36.3)
Sony Tablet S (Android 4.0.3; Kernel 2.6.39.4)

you may need the adb drivers for your device, in the case of sony's one its: https://developer.sony.com/open-source/aosp-on-xperia-open-devices/downloads/drivers you will also need USB Debugging enabled;

CVE-2016-5195 lets you overwrite any file that you have read access too, regardless of if it has write permission; we use this to temporarily overwrite /system/bin/run-as which always runs as root, to then install su for this reason its recommended to not close the application and ensure a good connection to ADB;

LiveOverflow did a video on this particular vulnerability

reason this can't be its own standalone app is that /system/bin/run-as is the only SUID binary present in older android versions; and it's only readable and executable from the 'shell' user, not within apps; meaning you have to trigger it from ADB Shell.

NOTE: Exploit relies on a race condition; please give it a few minutes to run
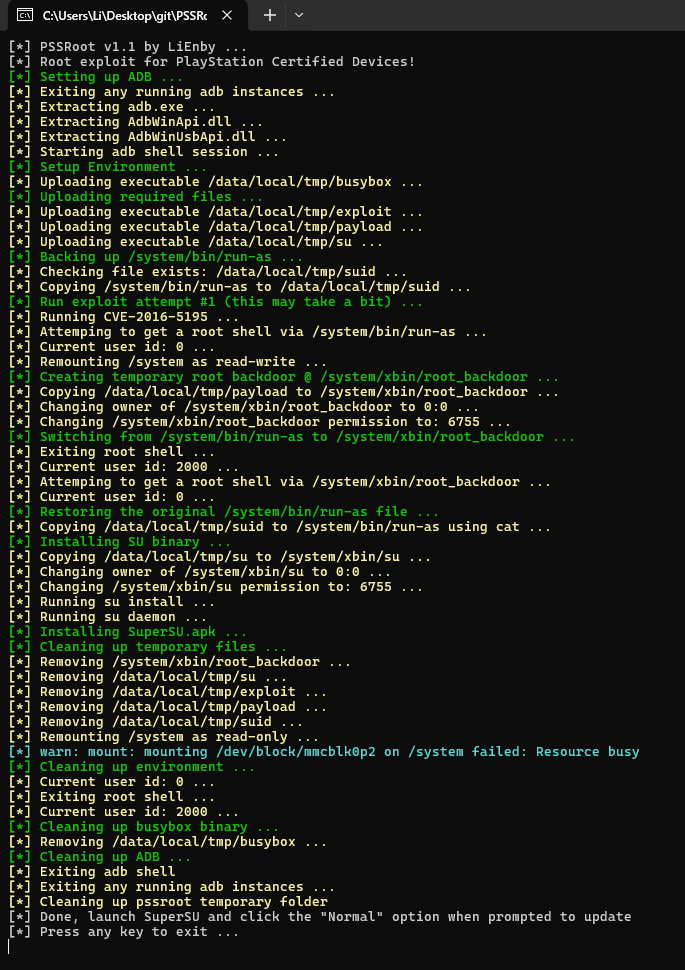
PSS Root Success Output

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →






