

CVE-2024-23108
 horizon3ai/cve-2024-23108
CVE-2024-23108: Fortinet FortiSIEM Unauthenticated 2nd Order Command Injection
command-and-controlexploitationpenetration-testing+3
34
horizon3ai/cve-2024-23108CVE-2024-23108: Fortinet FortiSIEM Unauthenticated 2nd Order Command Injection
 nccgroup/jdser-ngng
A Burp Extender plugin, that will deserialized java objects and encode them in XML using the Xtream library.
 orangmuda/cve-2021-20837
XMLRPC - RCE in MovableTypePoC
 jeromeyoung/log4j2burpscanner
CVE-2021-44228,log4j2 burp插件 Java版本,dnslog选取了非dnslog.cn域名
 perimeterx/cve-2020-6519
Proof-of-concept exploit for CVE-2020-6519, a Content Security Policy bypass vulnerability in Chromium 83, enabling full CSP bypass across platforms.
 petergottesman/pwnkit-exploit
Local privilege escalation exploit for CVE-2021-4034 in pkexec, providing a proof-of-concept that drops a root shell on vulnerable systems.
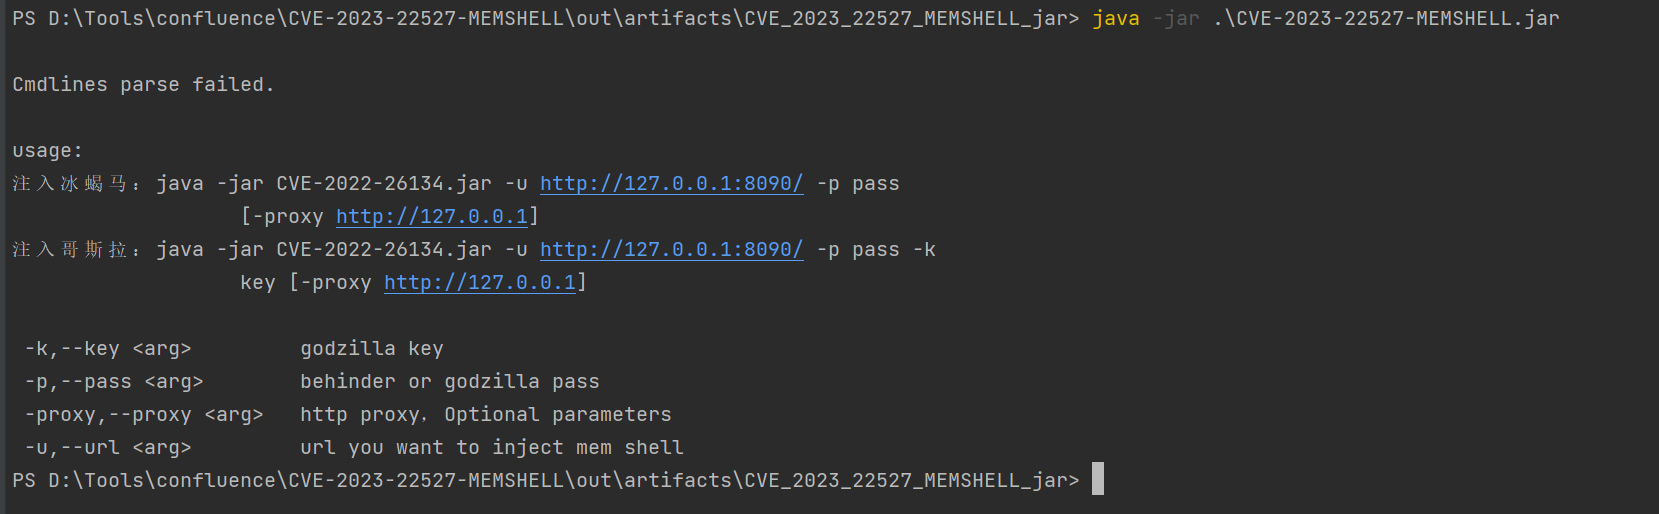 m0untainshley/cve-2023-22527-memshell
confluence CVE-2023-22527 漏洞利用工具,支持冰蝎/哥斯拉内存马注入,支持设置 http 代理
 emerinohdz/facebrute
Facebook brute forcer script
 qingxp9/cve-2019-6203-poc
PoC for CVE-2019-6203, works on < iOS 12.2, macOS < 10.14.4
 jas502n/cve-2020-1947
Apache ShardingSphere UI YAML解析远程代码执行漏洞
 firosolutions/cve-2020-7247-exploit
Python exploit of cve-2020-7247
 jm33-m0/cve-2018-7750
an RCE (remote command execution) approach of CVE-2018-7750
 rxerium/cve-2025-61882-cve-2025-61884
Detection for CVE-2025-61882 & CVE-2025-61884
 xyl2k/black-eye-rsa-attacking-toolkit-v0.1f-compiled
The great RSA Attacking Toolkit compiled for Windows
 pyn3rd/cve-2019-3396
Confluence Widget Connector RCE
 hasherezade/bunitu_tests
Scripts for communication with Bunitu Trojan C&Cs
 generaleg/cve-2019-15858
Unauthenticated RCE at Woody Ad Snippets / CVE-2019-15858 (PoC)