
BLT
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
curated-resourcesdevsecopseducation+7
11 day ago
owasp/bltMonorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 beefproject/beef
The Browser Exploitation Framework Project
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 horkimhab/cve-2026-68121
Proof-of-concept for CVE-2026-68121 (PPPoEject), providing a Python exploit implementation for authorized security research and lab testing.
 owasp/securityshepherd
Web and mobile application security training platform
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 ashishb/android-security-awesome
A collection of android security related resources
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
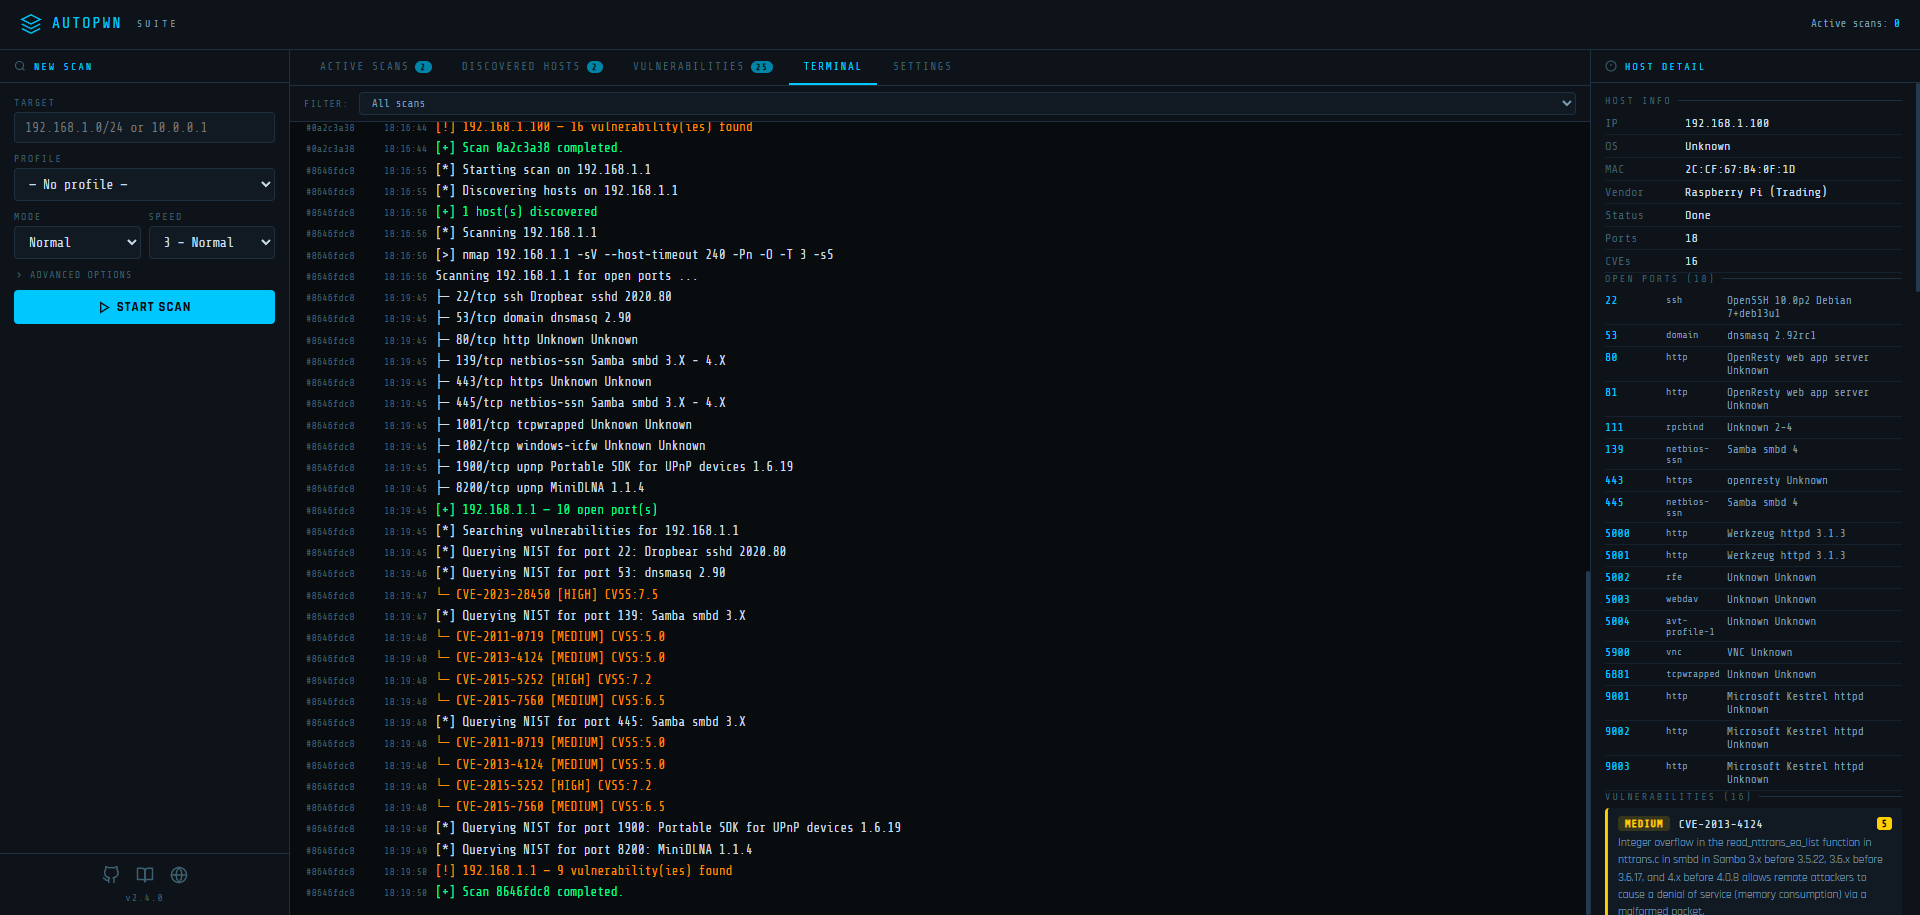 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
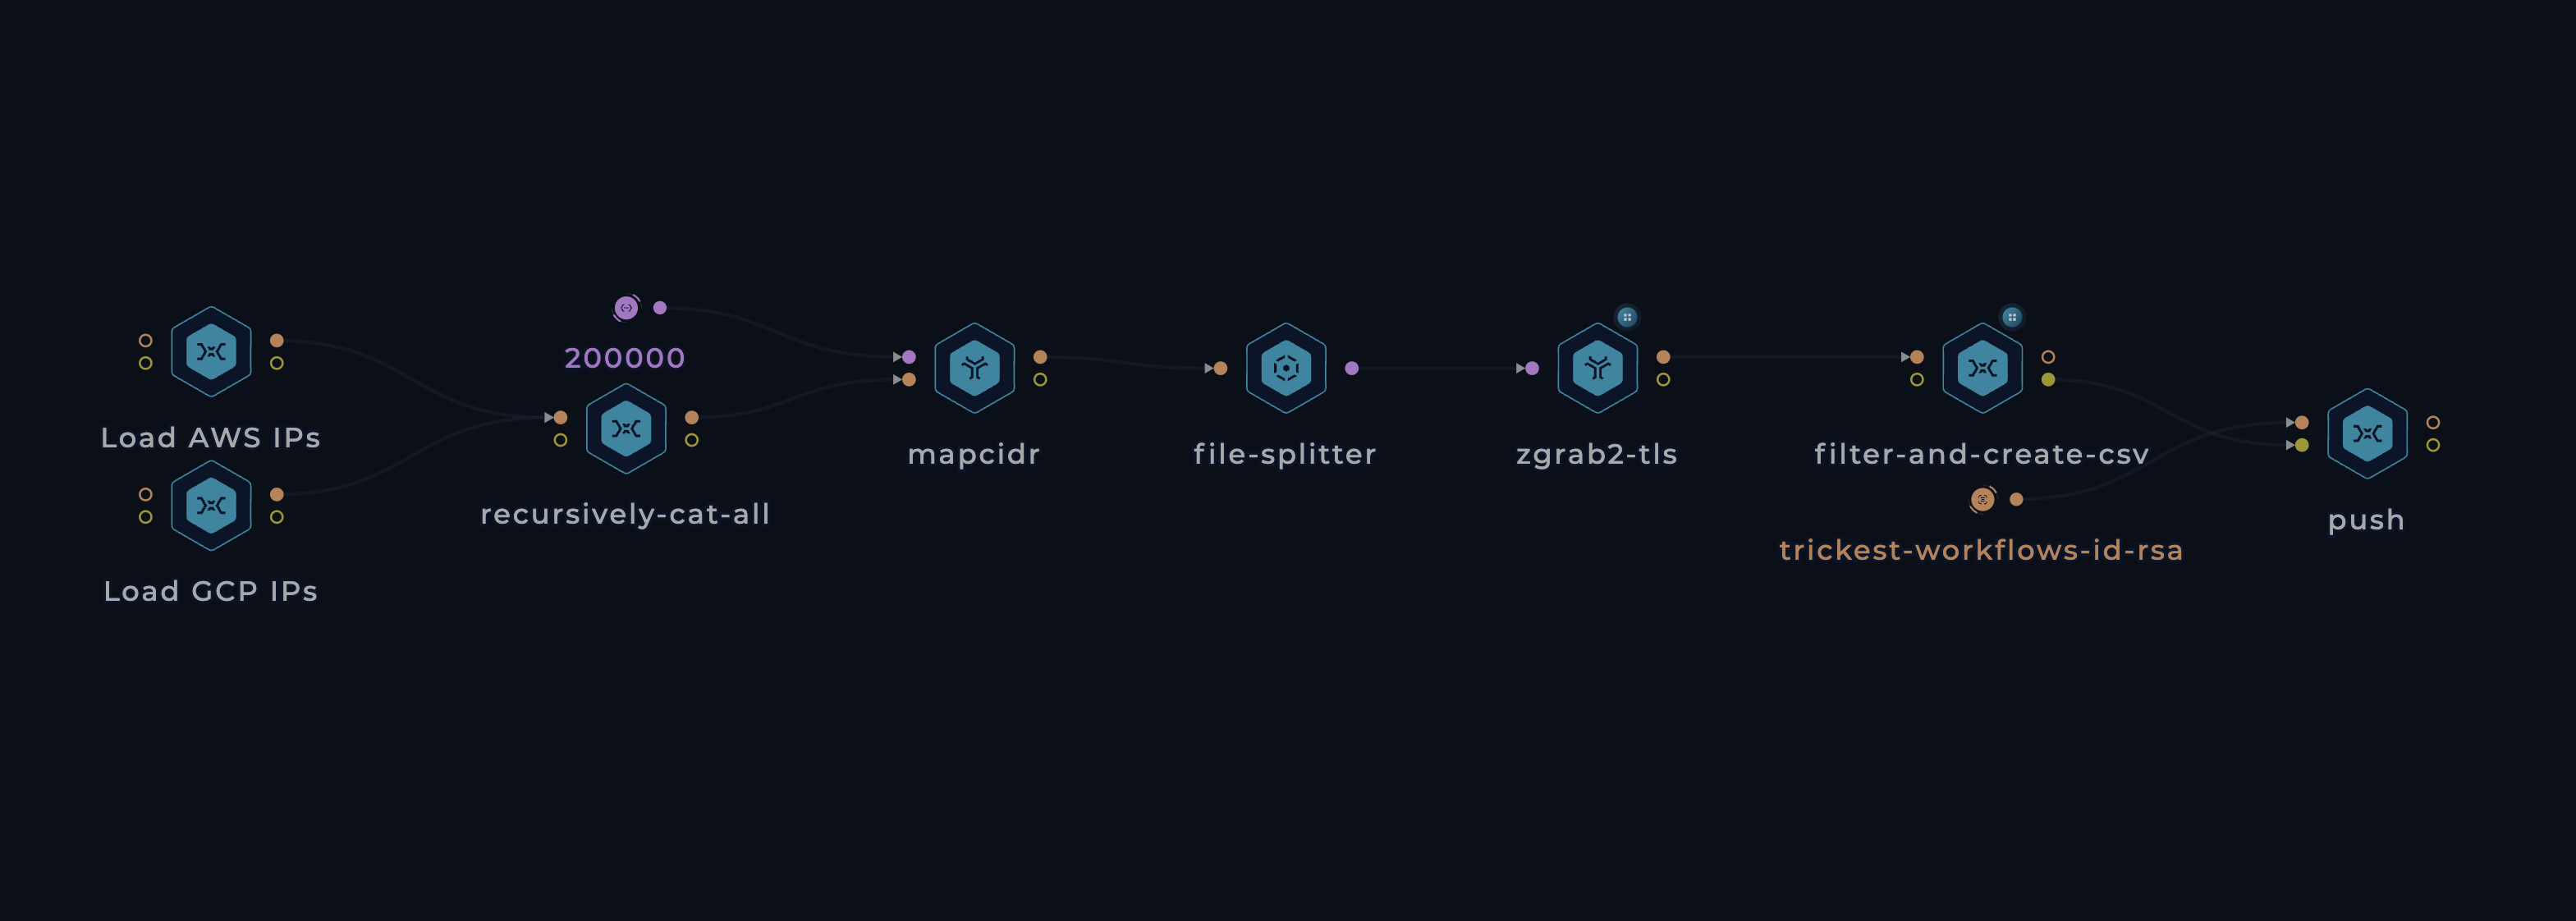 trickest/cloud
Monitoring the Cloud Landscape
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
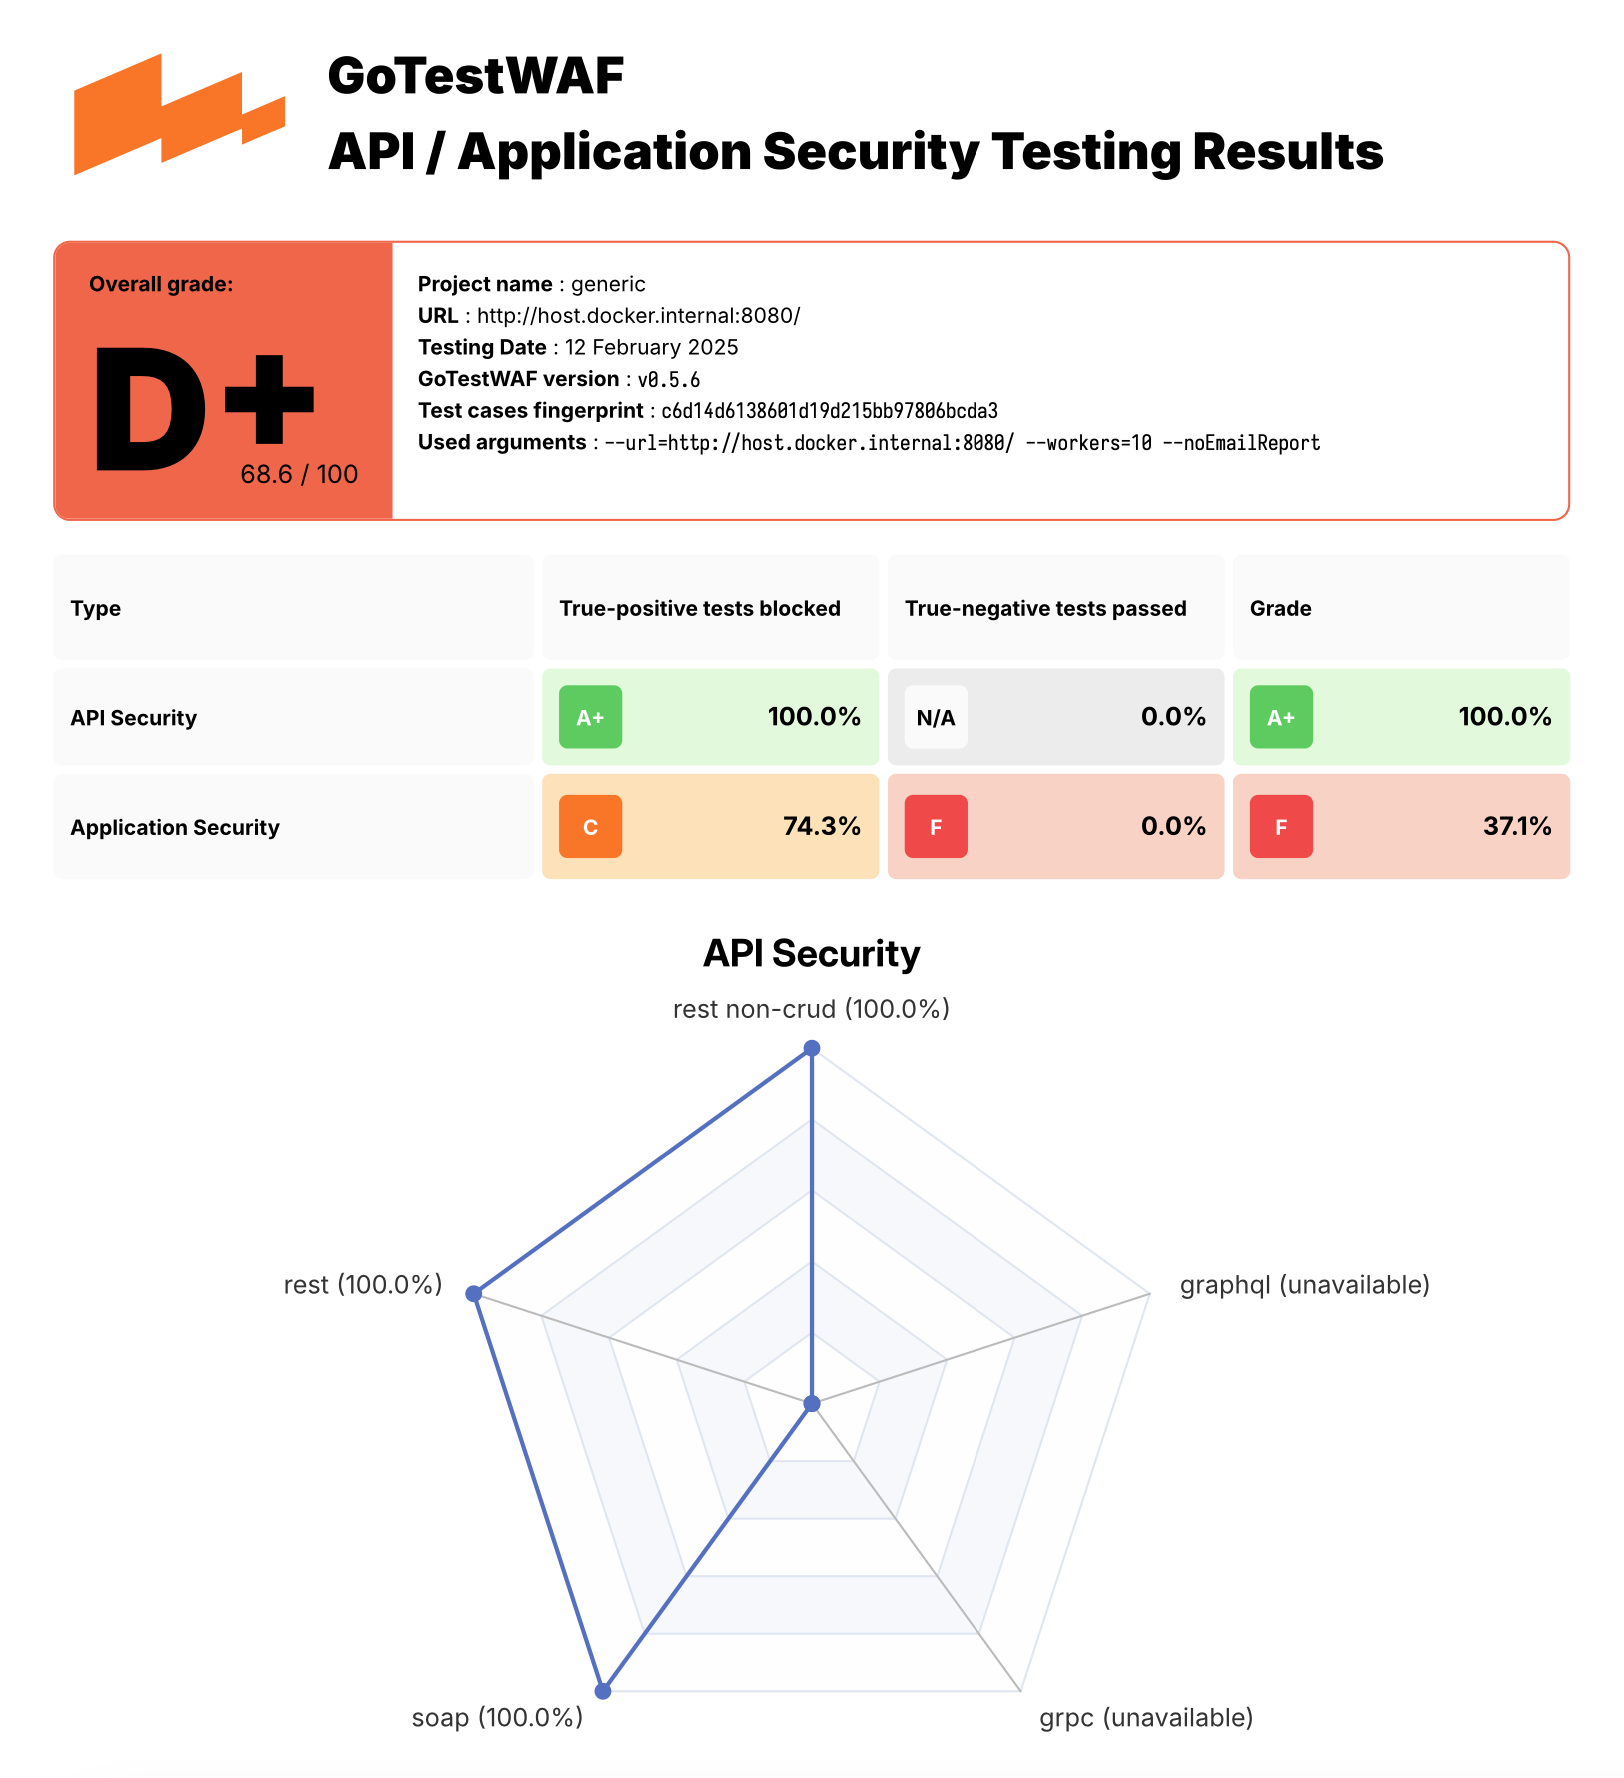 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 rianhanft/marauderbox
A fork of the marauder firmware with Nyan box capabilities
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…