
pystinger
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell
command-and-controlexploit-frameworksids-ips-evasion+5
funnywolf/pystingerBypass firewall for traffic forwarding using webshell
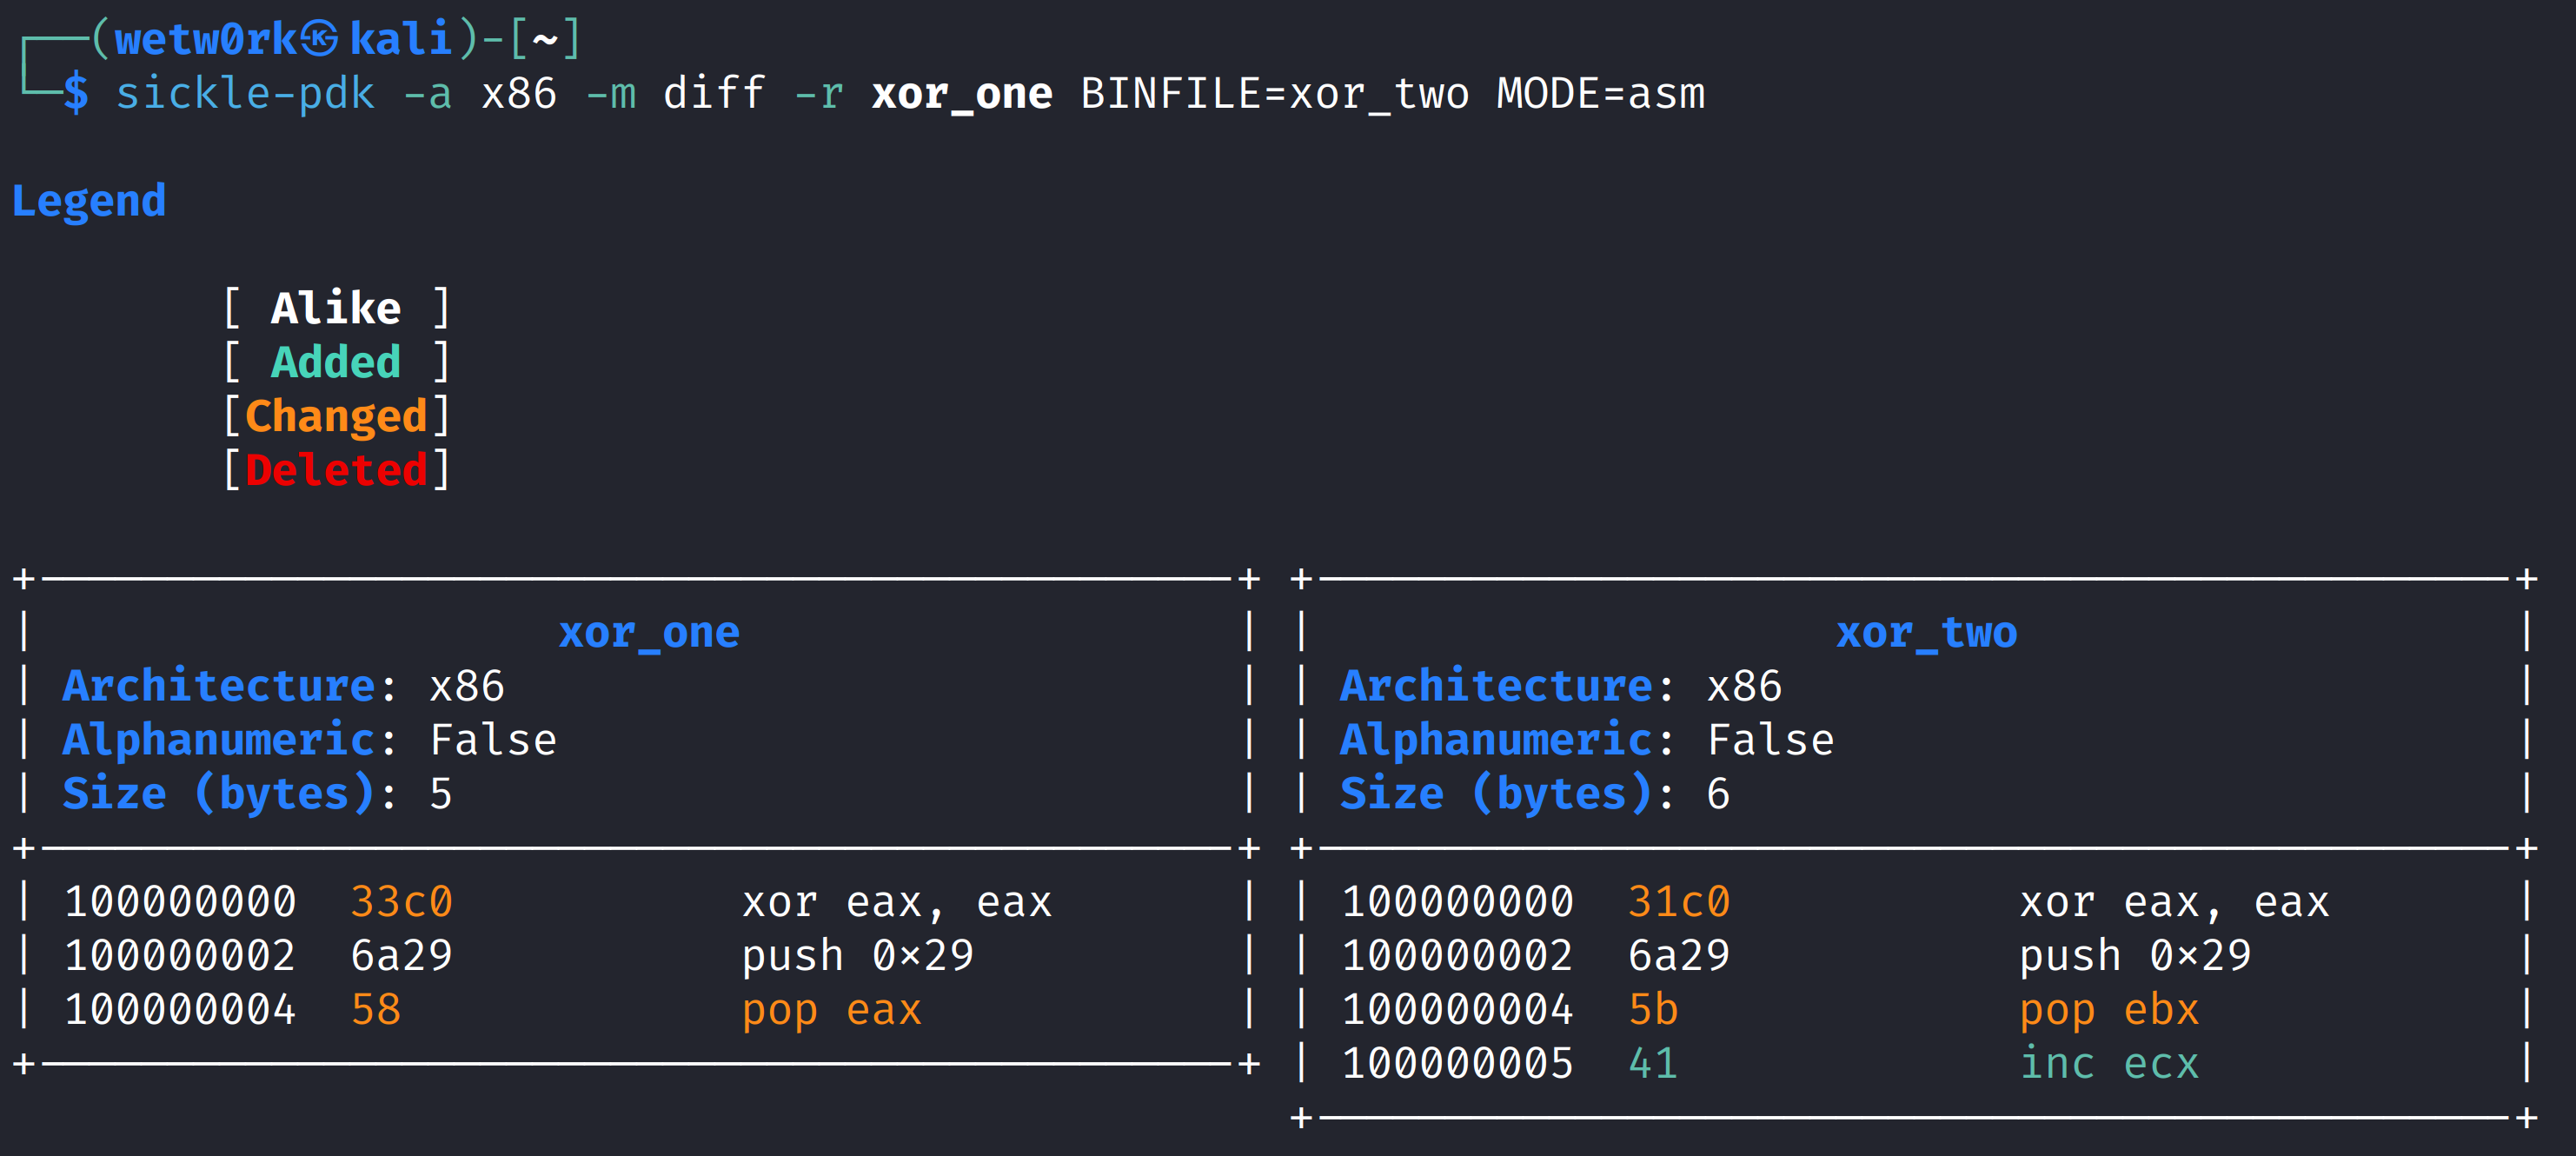 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
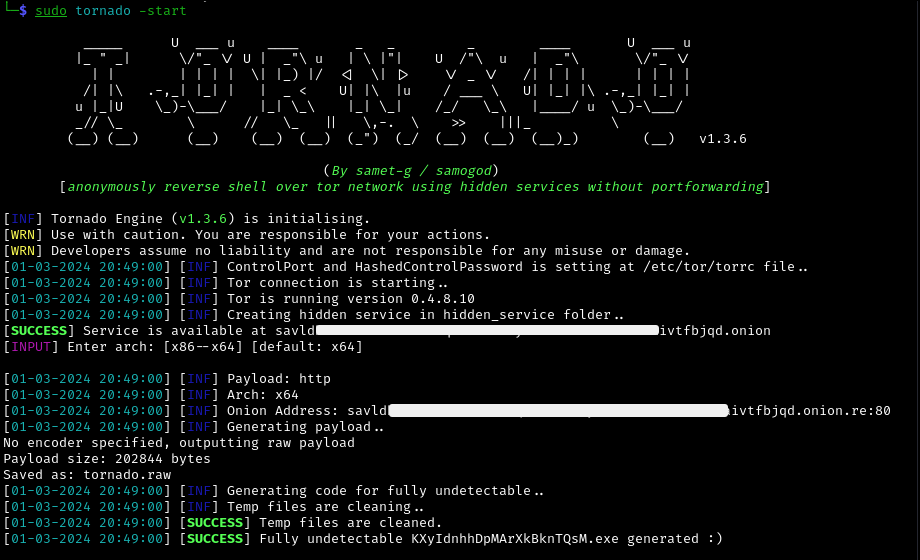 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
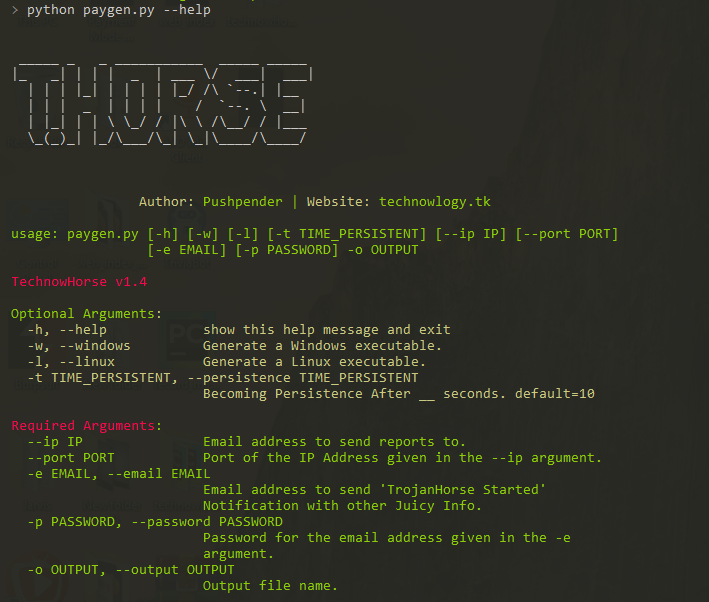 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
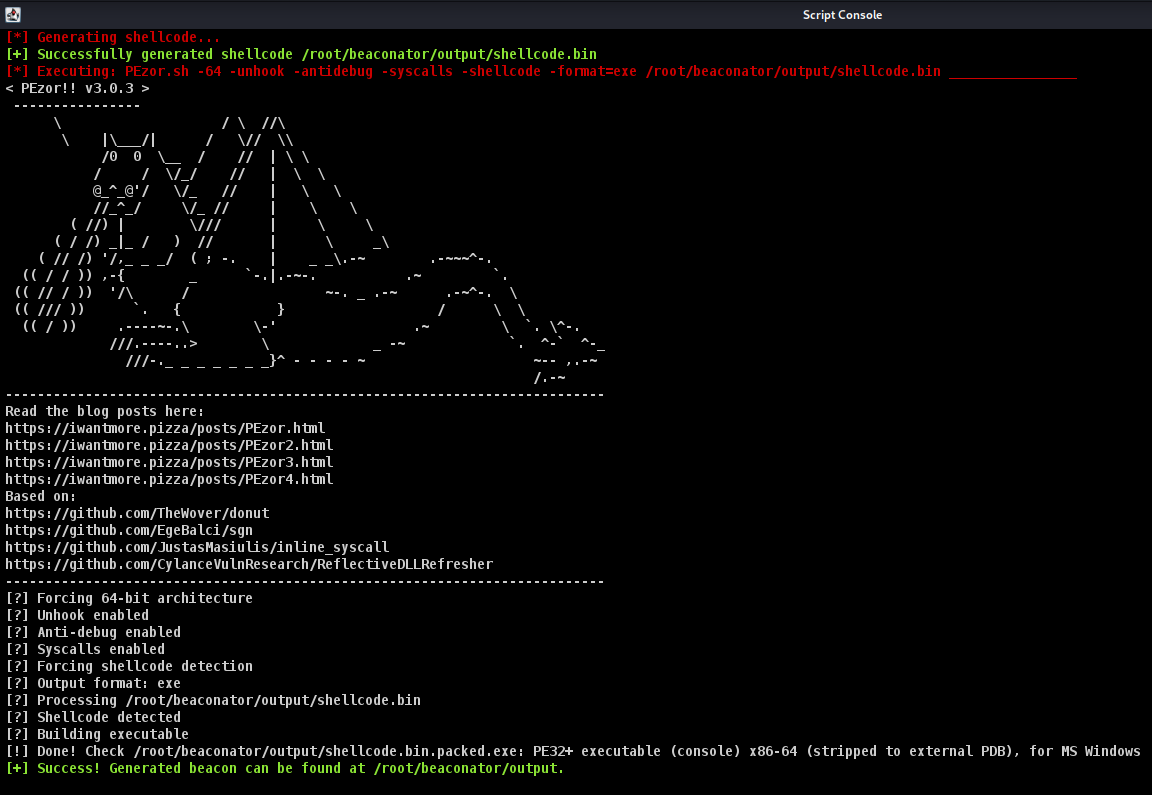 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
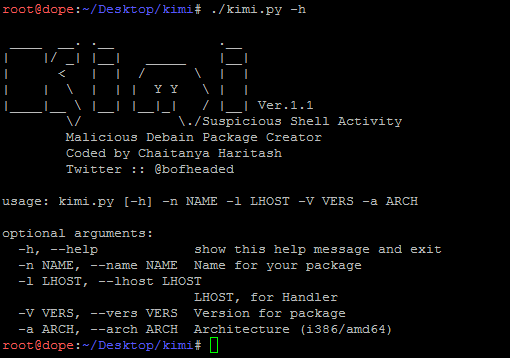 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…