
Archived
AhMyth-Android-RAT
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
android-securitycommand-and-controlpayload-generation+3
ahmyth/ahmyth-android-ratAndroid Remote Administration Tool
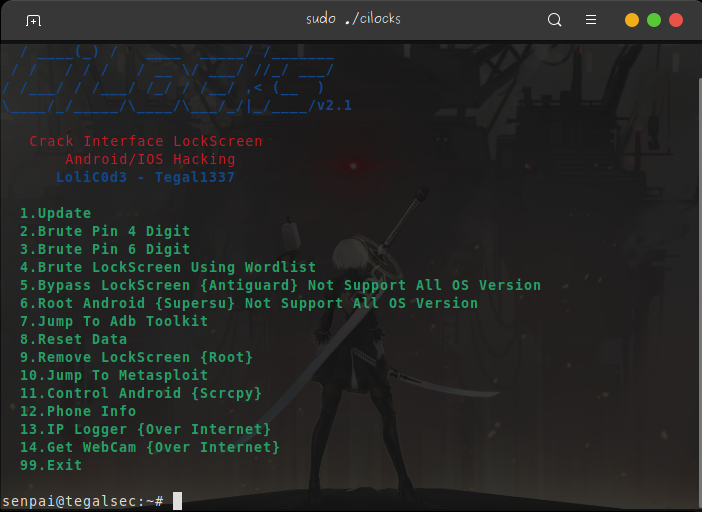 tegal1337/cilocks
Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
 ghxstsec/php2shell-poc
Python exploit for CVE-2026-109618: abuses PHP session.upload_progress heap corruption to overwrite zend_call_function and achieve remote command…
 k4n3co/lab-rats-v1.6
An advanced, lightweight Android Remote Admin Framework engineered for real-time monitoring, stealth interaction, and remote management through a…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 threekiii/awesome-redteam
一个攻防知识库。A knowledge base for red teaming and offensive security.
 jonaschen0103/cve-2026-33439-poc
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…
 bishopfox/sliver
Adversary Emulation Framework
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 liaomilk/cve-2025-69212-for-myself
just record for myself
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 netw0rknoob/vulnclaw
基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads