
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
41 results
nullmap preview

nullmap

GitHubsamueltulach/nullmap

Using CVE-2023-21768 to manual map kernel mode driver
binary-exploitationexploitationmemory-forensics+3
2023 years ago
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
command-and-controlexploitationids-ips-evasion+6
2431 year ago
Lastenzug preview

Lastenzug

GitHubcodewhitesec/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
command-and-controlids-ips-evasionpayload-development+3
2354 years ago
ExecIT preview

ExecIT

GitHubflorylsk/execit

Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2282 years ago
Hwacha preview

Hwacha

GitHubn00py/hwacha

Deploy payloads to *Nix systems en masse
command-and-controlexploitationlateral-movement+7
1086 years ago
KINGSOFT-WPS-Office-LPE preview

KINGSOFT-WPS-Office-LPE

GitHubhadimed/kingsoft-wps-office-lpe

CVE-2022-25943
binary-exploitationexploitationlateral-movement+4
584 years ago
teletunnel preview

teletunnel

GitHubmhdgning131/teletunnel

Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !

command-and-controldata-exfiltrationids-ips-evasion+7
457 months ago
RedRoot preview

RedRoot

GitHubagampreet-singh/redroot

RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
ctfexploit-frameworksfuzzing+9
188 days ago
dicerosbicornis preview

dicerosbicornis

GitHubmaldevel/dicerosbicornis

A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
169 years ago
Lastenzug preview

Lastenzug

GitHubps1337/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
ids-ips-evasionpayload-developmentpost-exploitation+3
264 years ago
NetSpy preview

NetSpy

GitHubdereeqw/netspy

NetSpyC2 – Python C2 Server with RSA Key Exchange and AES-GCM Encrypted Sessions
command-and-controleducationencryption-decryption-tools+3
69 months ago
CVE-2026-14266 preview

CVE-2026-14266

GitHubliyuxuan504-byte/cve-2026-14266

7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
binary-analysisbinary-exploitationcode-analysis+7
33 months ago
Linksys-WRT54GL-Exploitation preview

Linksys-WRT54GL-Exploitation

GitHubumbertodellamonica/linksys-wrt54gl-exploitation

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
binary-analysisdebuggerseducation+9
25 months ago
CVE-2025-55182-React2Shell-Async-Scanner preview

CVE-2025-55182-React2Shell-Async-Scanner

GitHubinferiorak/cve-2025-55182-react2shell-async-scanner

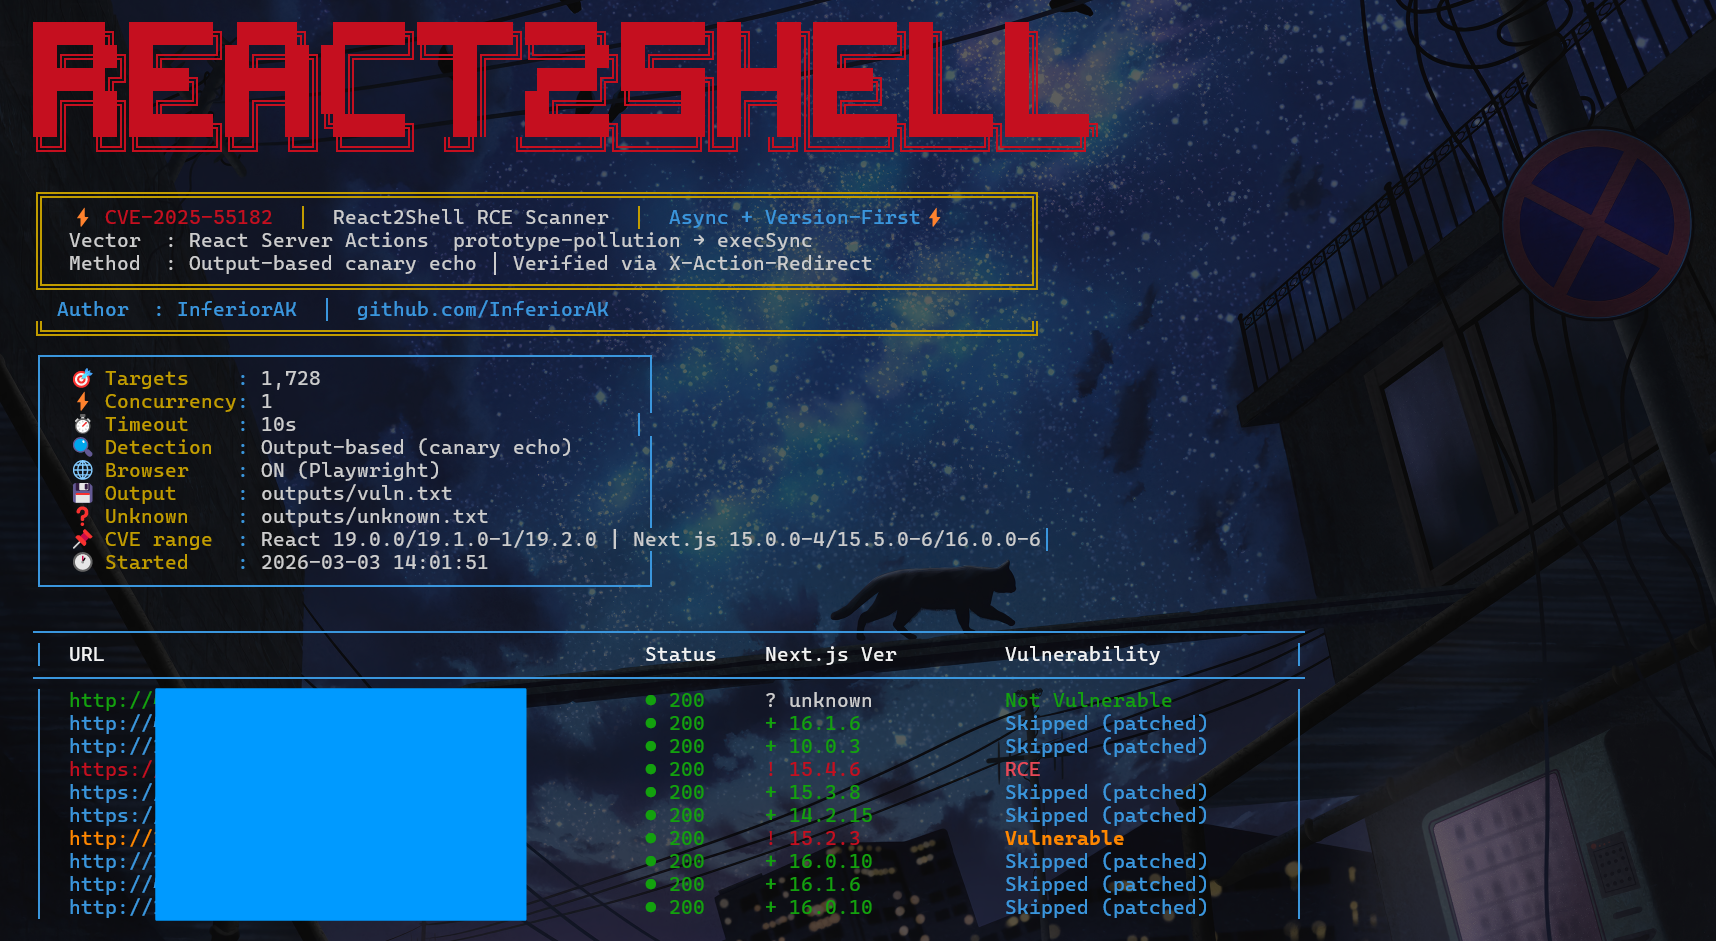
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
code-analysisctfdynamic-analysis-sandboxing+8
37 months ago
FUXAPWN preview

FUXAPWN

GitHubhann1bl3l3ct3r/fuxapwn

POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
exploitationinformation-gatheringlateral-movement+8
25 months ago
CVE-2017-14980 preview

CVE-2017-14980

GitHubgodoy-sec/cve-2017-14980

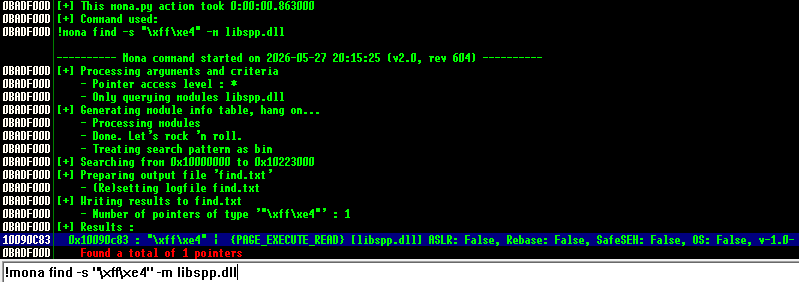
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
binary-exploitationdebuggerseducation+5
12 months ago
CVE-2023-37941 preview

CVE-2023-37941

GitHubbarroqueiro/cve-2023-37941

Exploit on the default cache of superset by using pickle
code-analysisexploitationpayload-development+3
13 years ago
lwip-snmpv3-stack-overflow-cve-2026-8836-critical-embedded-rce preview

lwip-snmpv3-stack-overflow-cve-2026-8836-critical-embedded-rce

GitHubhunt-benito/lwip-snmpv3-stack-overflow-cve-2026-8836-critical-embedded-rce

CVE-2026-8836 — lwIP SNMPv3 stack-based buffer overflow PoC (CVSS 9.8)

binary-exploitationembedded-systems-securityexploitation+4
4 months ago
Previous123Next