
CVE-2026-20841
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
command-and-controlexploitationpayload-development+3
1
hamzamalik3461/cve-2026-20841🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
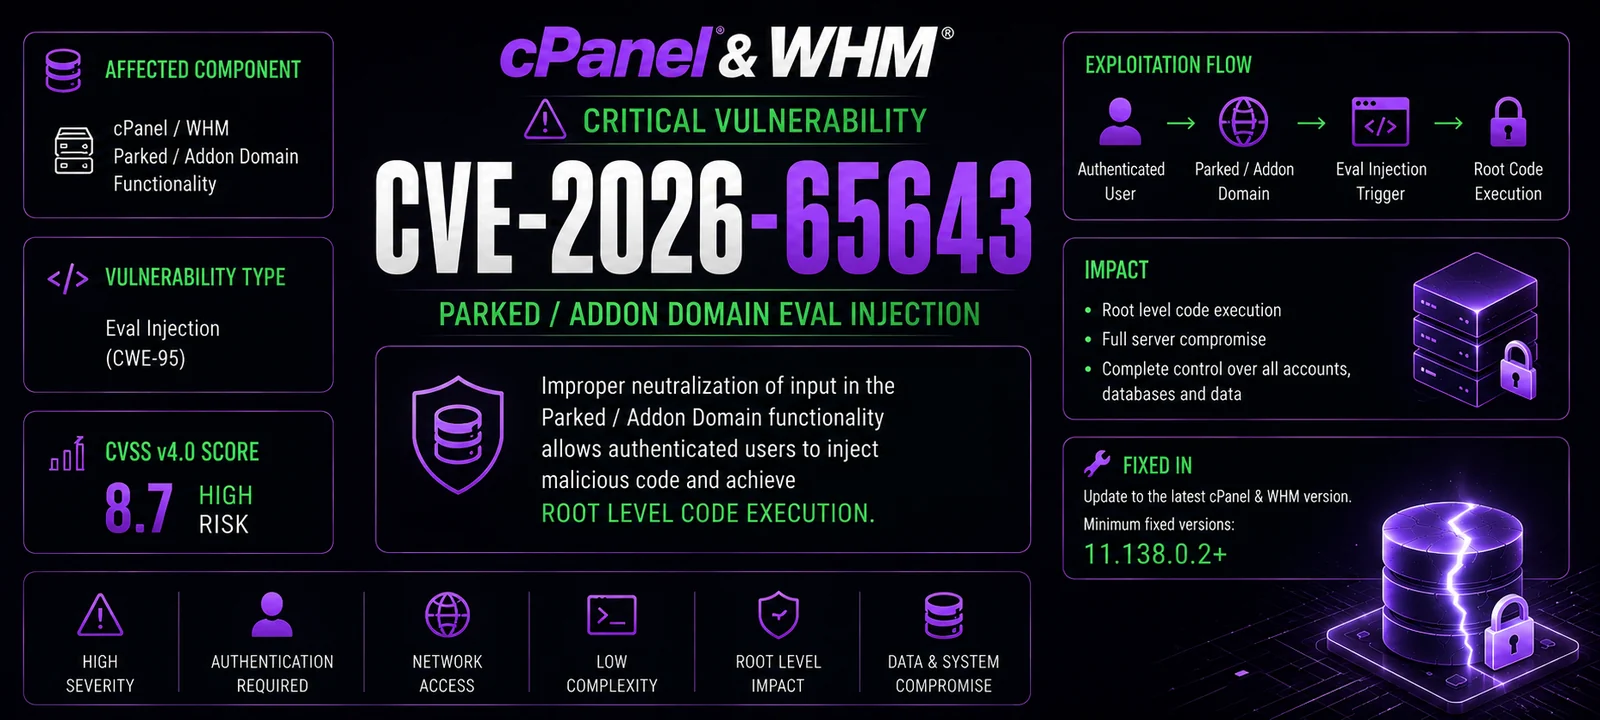 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 beefproject/beef
The Browser Exploitation Framework Project
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 shadowforge-cyber/cve-2026-104286-poc
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…
 petriqore/cve-2026-26026_poc
PoC script for CVE-2026-26026 GLPI versions 11.0.0 through 11.0.5
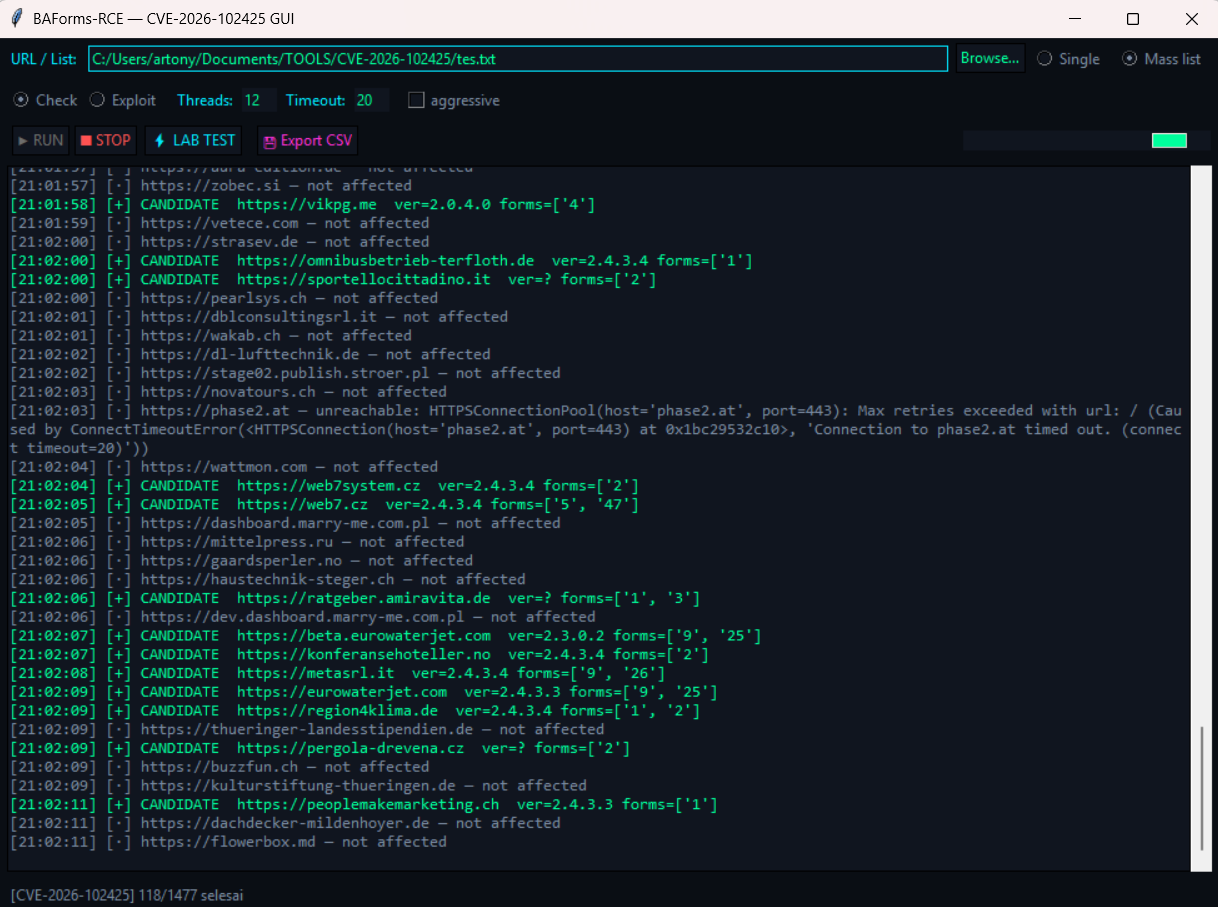 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 abraxas/cve-2026-75650
Disclosure pack and lab reproduction script for CVE-2026-75650, an unauthenticated SSTI RCE in Magento Open Source GraphQL email templates.
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 bombobombone/cve-2026-103441
Local proof-of-concept and sanitized report for CVE-2026-103441, a PHP object-injection flaw in the MediaWiki action=parse API that can reach RCE via…
 murrez/cve-2026-102427
Python 3 PoC for CVE-2026-102427, an unauthenticated upload RCE in OrdaSoft Joomla CCK (com_os_cck) via task=getContent and site/uploader.php using a…
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction