

php-cve-2026-115560-demo
 prnjlksingh/php-cve-2026-115560-demo
Local intentionally vulnerable PHP lab demonstrating CVE-2026-115560: session serialize_handler mismatch leading to unserialize() gadget RCE, with a…
educationexploitationlabs-practice+4
prnjlksingh/php-cve-2026-115560-demoLocal intentionally vulnerable PHP lab demonstrating CVE-2026-115560: session serialize_handler mismatch leading to unserialize() gadget RCE, with a…
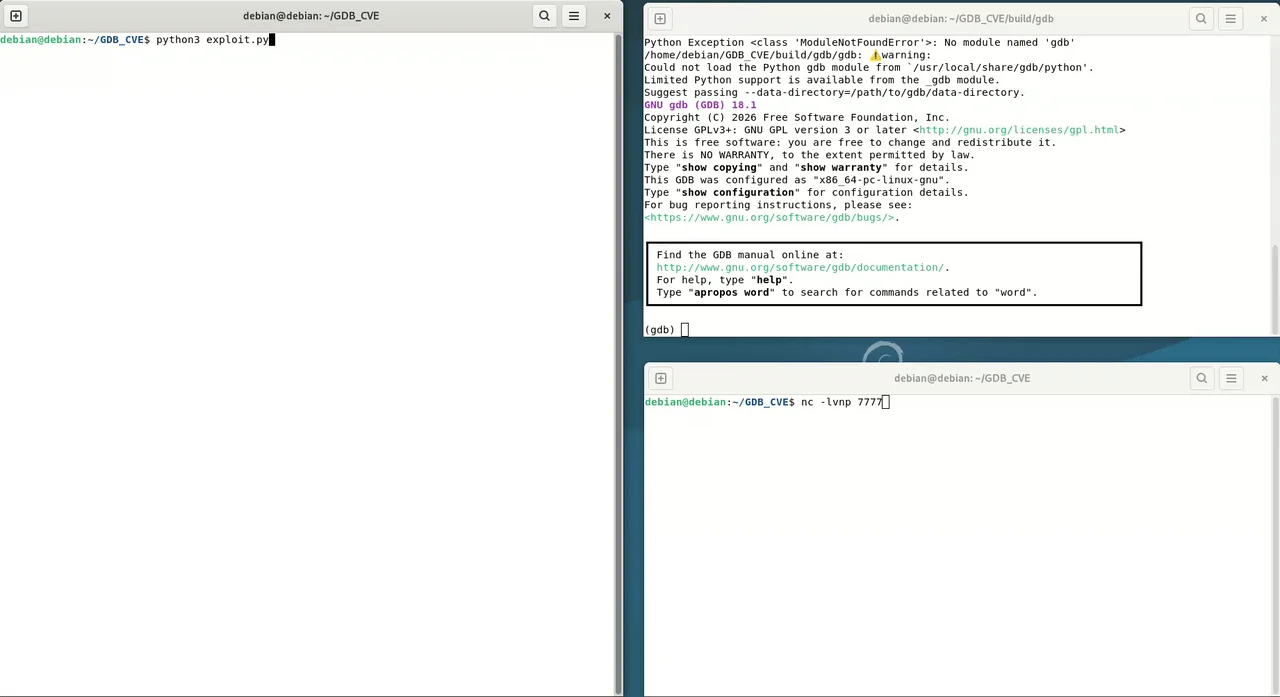 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 ivancabrera02/admintosystem-http.sys
Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…
 dntaskmehow/marabuse
Exploit framework for CVE-2026-39987, an unauthenticated RCE in Marimo, with a reverse shell, NKAbuse blockchain botnet payload, and Ruby C2 server.
 theendofabbys/cve-2026-48908
Python PoC for CVE-2026-48908: unauthenticated ZIP upload in Joomla SP Page Builder (com_sppagebuilder) leading to remote code execution via a PHP…
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
 eqstlab/cve-2026-109619
Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 si13nttt/cve-2025-24813
Python PoC exploiting Apache Tomcat CVE-2025-24813 partial PUT deserialization RCE, with auto variant detection, ysoserial gadget chains, and reverse…
 si13nttt/cve-2025-32432
Python PoC exploiting CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii DI gadget injection, with assetId scanning, reverse shell, and…
 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 yym8538/cve-2026-33017
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 eqstlab/cve-2026-6951
Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…