

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
37
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
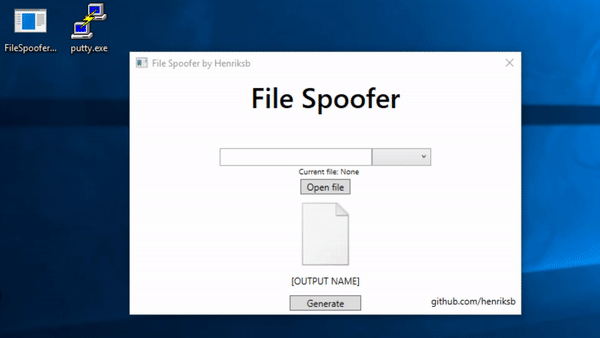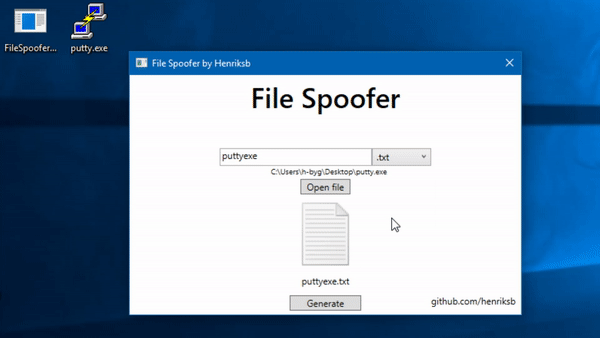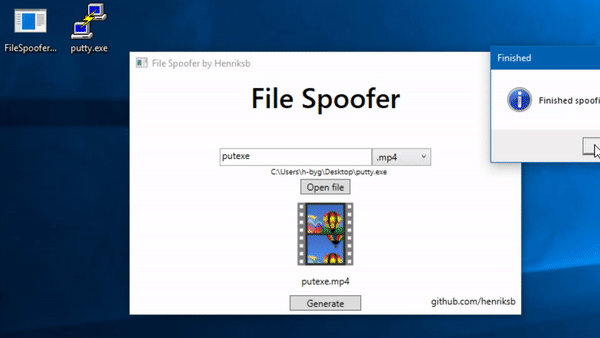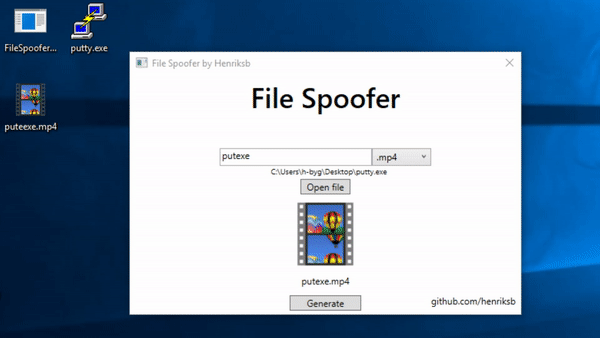 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 s3cur3th1ssh1t/amsi-bypass-powershell
This repo contains some Amsi Bypass methods i found on different Blog Posts.
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 rsmudge/malleable-c2-profiles
Malleable C2 is a domain specific language to redefine indicators in Beacon's communication. This repository is a collection of Malleable C2 profiles…
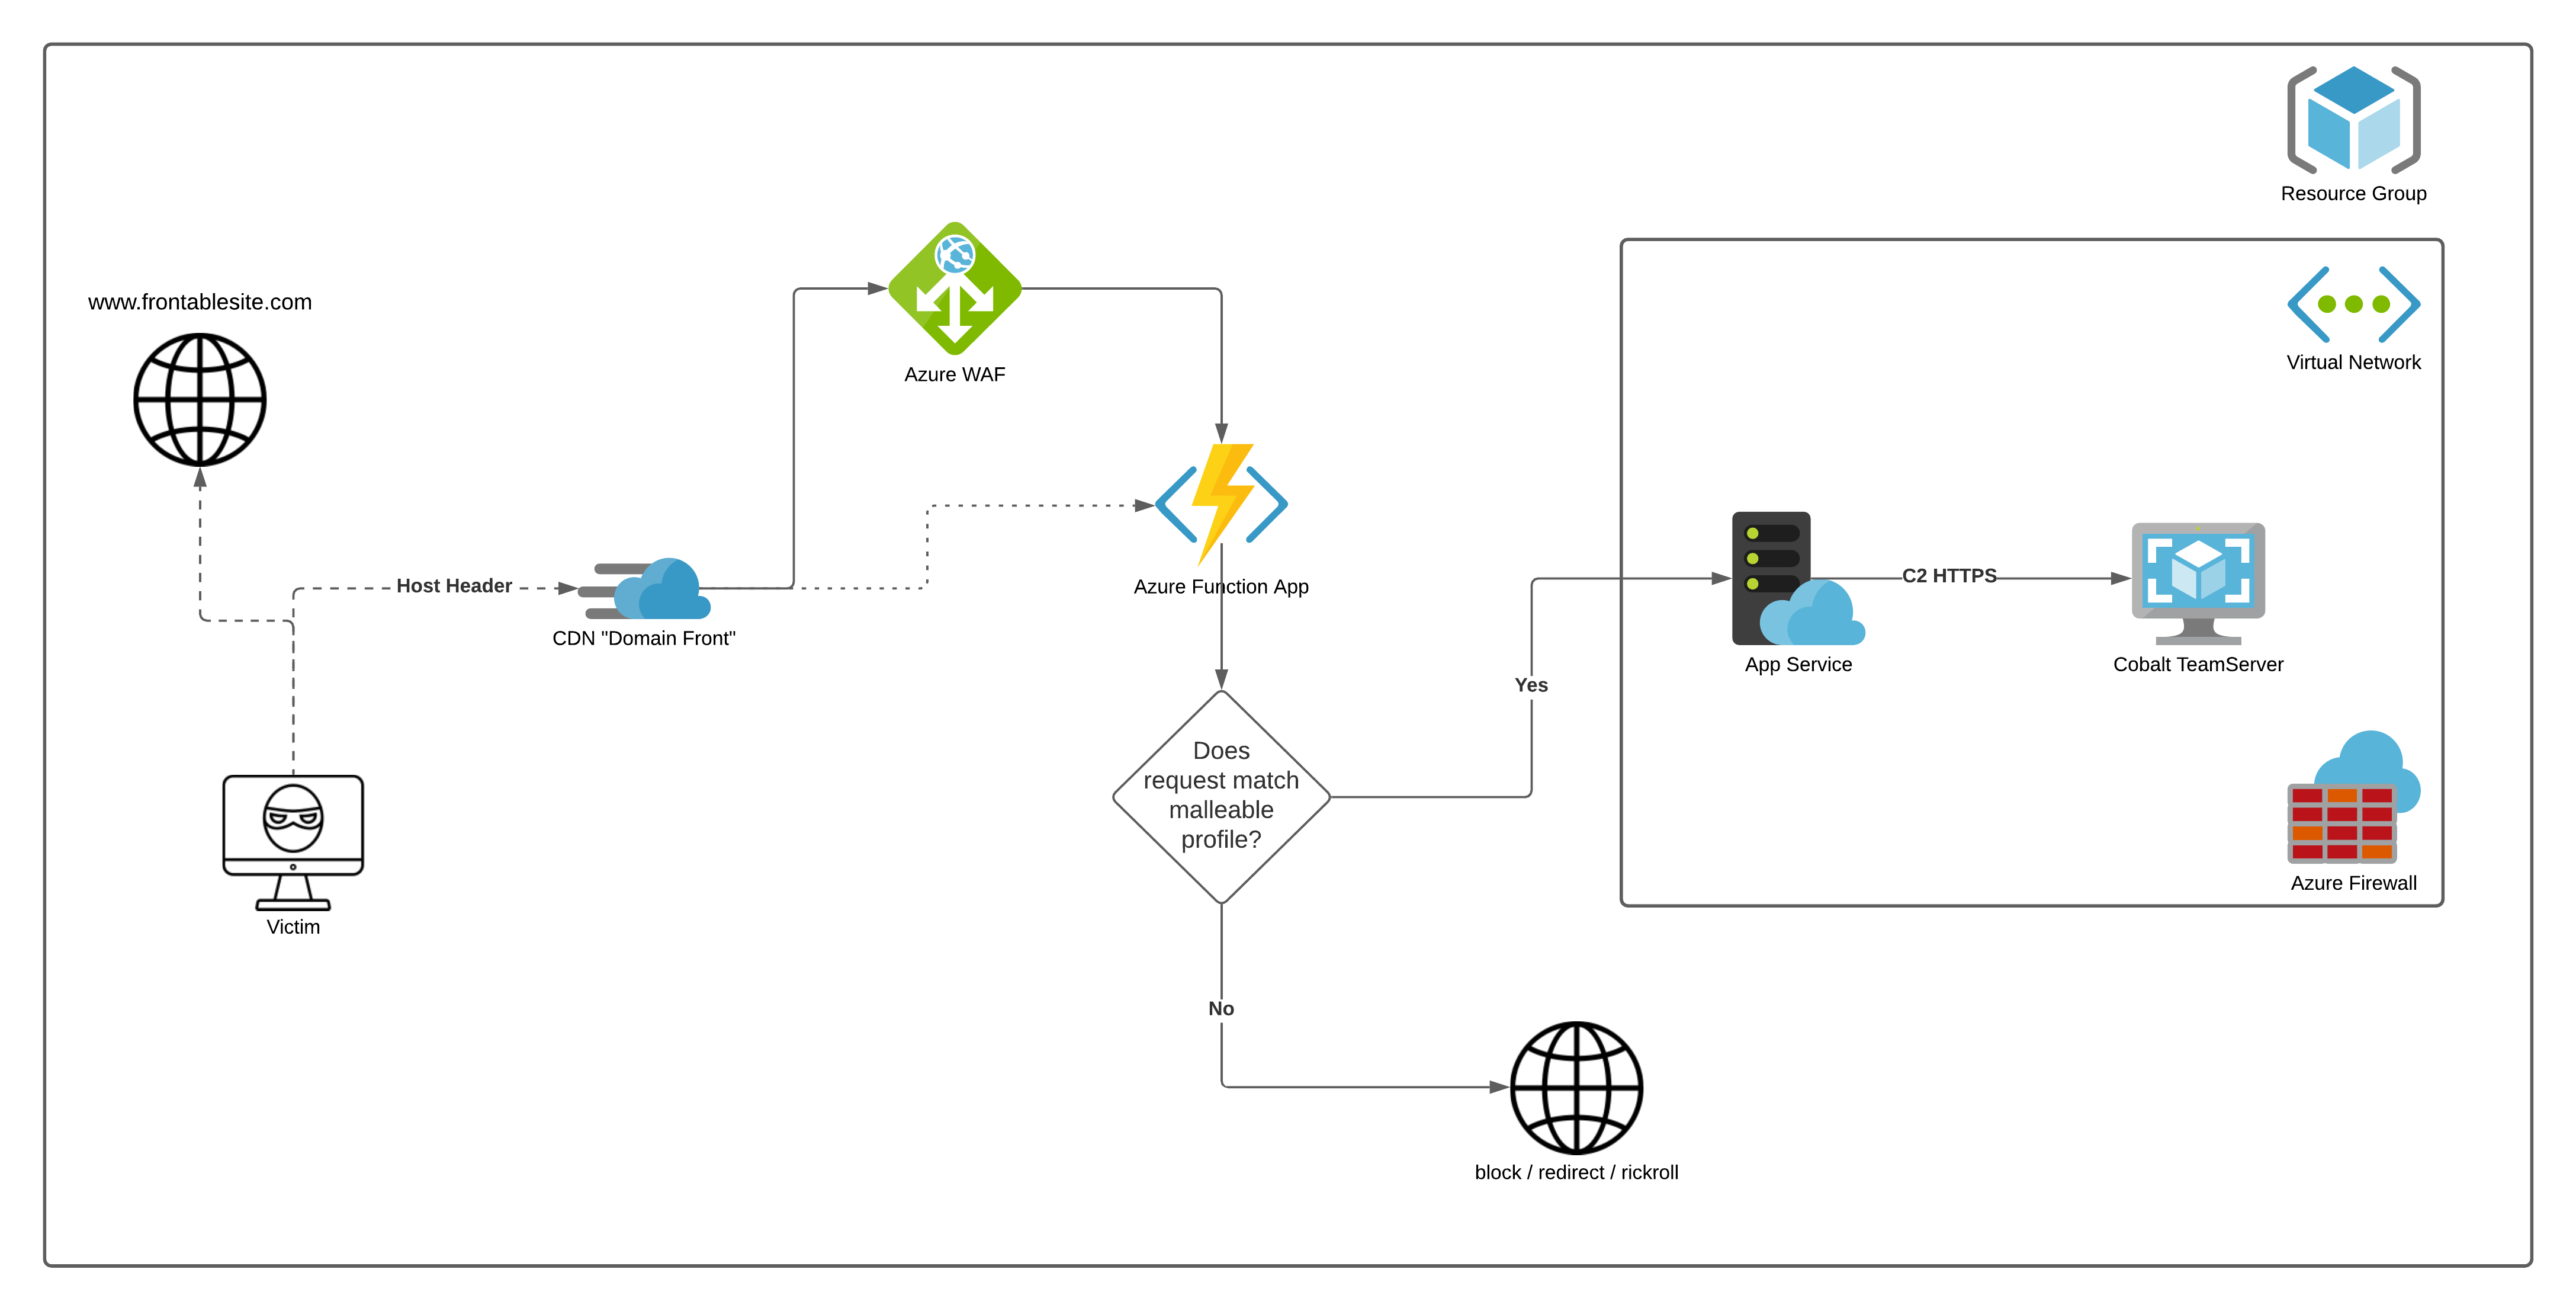 flangvik/azurec2relay
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.