
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
21 results
Sudo-Agent-CTF- preview

Sudo-Agent-CTF-

GitHubnyxrecon/sudo-agent-ctf-

Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
ctfeducationexploitation+7
2 months ago
poc-CVE-2019-9053 preview

poc-CVE-2019-9053

GitHubrideckszz/poc-cve-2019-9053

PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
ctfeducationlabs-practice+3
14 months ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubjeanback1/cve-2019-9053-exploit

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
exploitationinformation-gatheringpassword-cracking+3
5 months ago
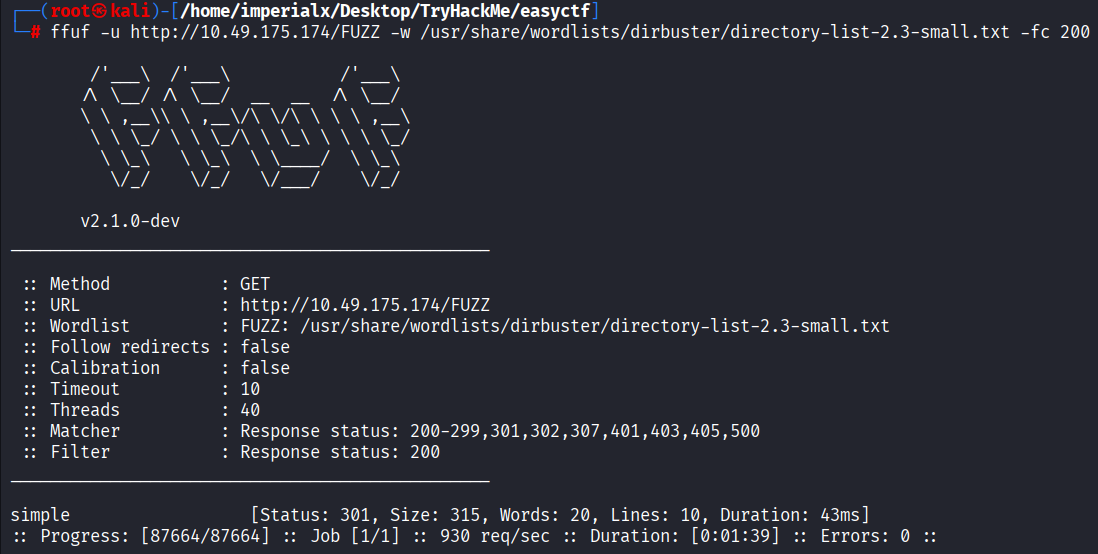
Simple-CTF-Writeup preview

Simple-CTF-Writeup

GitHubimperialx1104/simple-ctf-writeup

Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
ctfeducationexploitation+6
5 months ago
CVE-2018-14847 preview

CVE-2018-14847

GitHubthemalwareguardian/cve-2018-14847

Analysis and PoC for CVE-2018-14847, MikroTik RouterOS Winbox information disclosure vulnerability allowing unauthenticated read access to the…
embedded-systems-securityexploitationinformation-gathering+3
6 months ago
CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit preview

CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

GitHubelizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
exploitationpassword-crackingpenetration-testing+2
56 months ago
CVE-2018-12633-TPLink-Auth-Bypass preview

CVE-2018-12633-TPLink-Auth-Bypass

GitHubwiliam227user/cve-2018-12633-tplink-auth-bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
data-exfiltrationeducationembedded-systems-security+8
110 months ago
CVE-2019-9053-POC preview

CVE-2019-9053-POC

GitHubcaelumisme/cve-2019-9053-poc

Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
educationexploitationpassword-cracking+3
1 year ago
Venom-JWT preview

Venom-JWT

GitHubz-bool/venom-jwt

针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
exploitationfuzzingpassword-cracking+3
2871 year ago
-exploit-lab preview

-exploit-lab

GitHubhackheart-tech/-exploit-lab

Exploits Python cve-2019-9053– by HackHeart
exploitationpassword-crackingpenetration-testing+2
1 year ago
CVE-2019-9053-port-py3 preview

CVE-2019-9053-port-py3

GitHubdel0x3/cve-2019-9053-port-py3

CVE-2019-9053.
educationexploitationpassword-cracking+3
1 year ago
CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053- preview

CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053-

GitHubhf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
exploitationinformation-gatheringpassword-cracking+3
1 year ago
CVE-2019-9053-Exploit-Python-3 preview

CVE-2019-9053-Exploit-Python-3

GitHubmahamedm/cve-2019-9053-exploit-python-3

The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
exploitationpassword-crackingpenetration-testing+2
81 year ago
SimpleCTF-UpdatedExploit preview

SimpleCTF-UpdatedExploit

GitHubdh4nuj4/simplectf-updatedexploit

This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
exploitationpassword-crackingpenetration-testing+2
62 years ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubdavcwikla/cve-2019-9053-exploit

Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…
exploitationpassword-crackingpenetration-testing+2
2 years ago
CVE-2019-9053 preview

CVE-2019-9053

GitHub4nner/cve-2019-9053

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
113 years ago
Cisco-Smart-Exploit preview

Cisco-Smart-Exploit

GitHubalrikrr/cisco-smart-exploit

Cisco SmartInstall Exploit [CVE-2018-0171]
configuration-auditingexploitationnetwork-security+3
183 years ago
crestron_getsudopwd preview

crestron_getsudopwd

GitHubaxcheron/crestron_getsudopwd

Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices

embedded-systems-securityexploitationhardware-security+4
276 years ago
Previous12Next