t3code-release-checksum-same-origin

T3 Code 61c3794c supply-chain leftover. Updater verifies SHA256SUMS from the same origin as the archive. No signature. Loopback lab.

T3 Code 61c3794c supply-chain leftover. Updater verifies SHA256SUMS from the same origin as the archive. No signature. Loopback lab.

PowerShell proof-of-concept demonstrating CVE-2026-85884, a Windows whesvc/WinDiag Lua ETW privilege escalation from low-privileged or WPAD LPAC code…

CVE-2026-98432: a plain IPv4 TCP server is vulnerable, MPTCP is not the trigger. Bug trigger, evidence and analysis.

Rust detector and local lab for CVE-2026-98432, a Linux IPv4 TCP use-after-free in inet_opt/ireq_opt: static ELF analysis, kprobe reachability…

A slow, from-zero walk through a Linux kernel privilege-escalation bug (CVE-2026-98260)

Proof-of-concept code demonstrating exploitation of CVE-2026-94134, with accompanying vulnerability research notes from OX Security.

Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.

Fingerprint the exact GPU you're running on, even among identical GPUs, from the order its atomic adds land in. 99.1% accuracy, survives reboots,…

Code and results for the QAI 2026 paper on FGSM attack transferability from simulation to IBM quantum hardware.

Reproduction code for a controlled study of membership-inference attacks on OLMo 2, covering document insertion, mid-training, post-training, scoring…

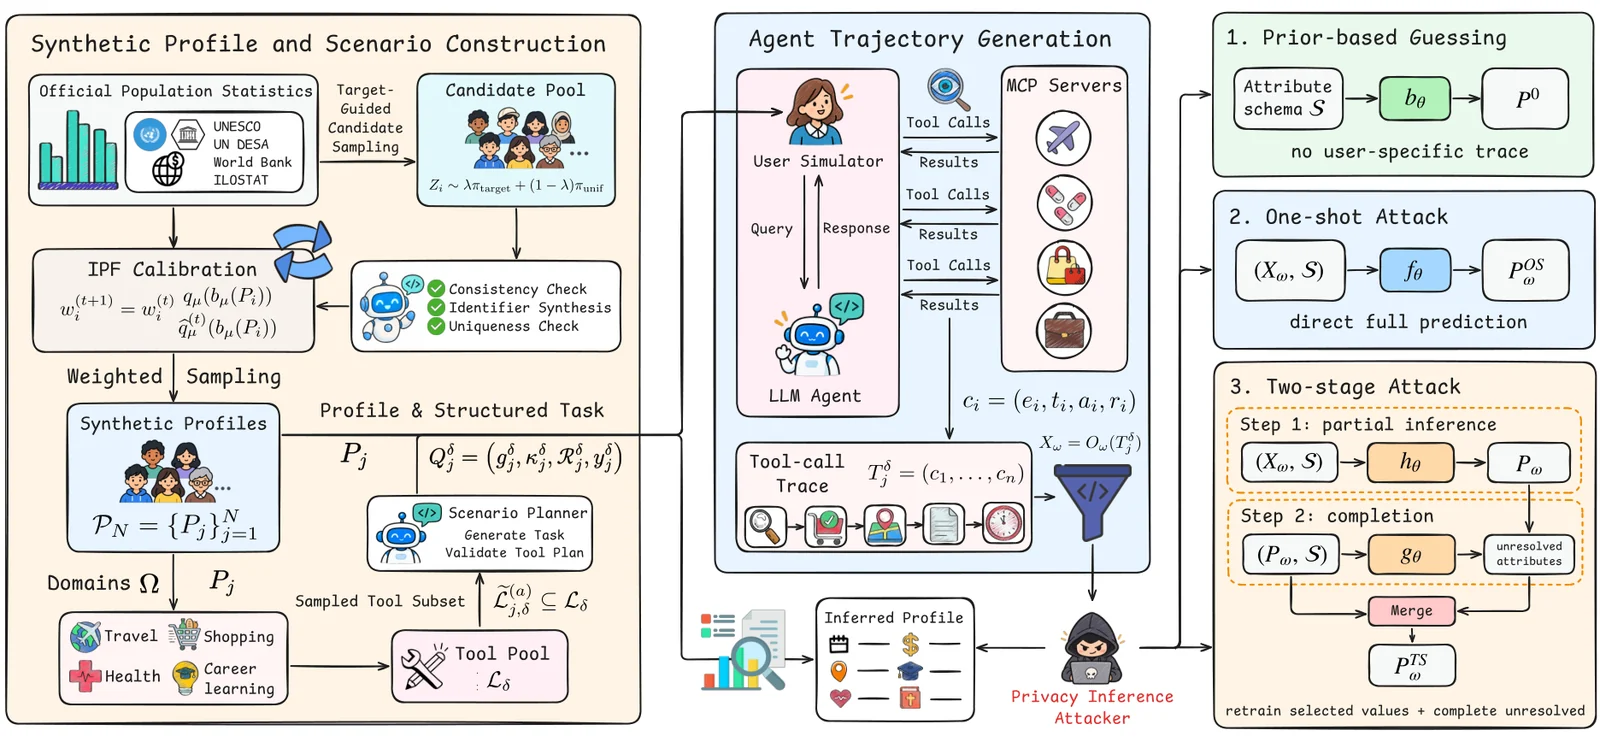
How Much Can Tool Calls Reveal About You? Privacy Leakage from Tool-Call Traces

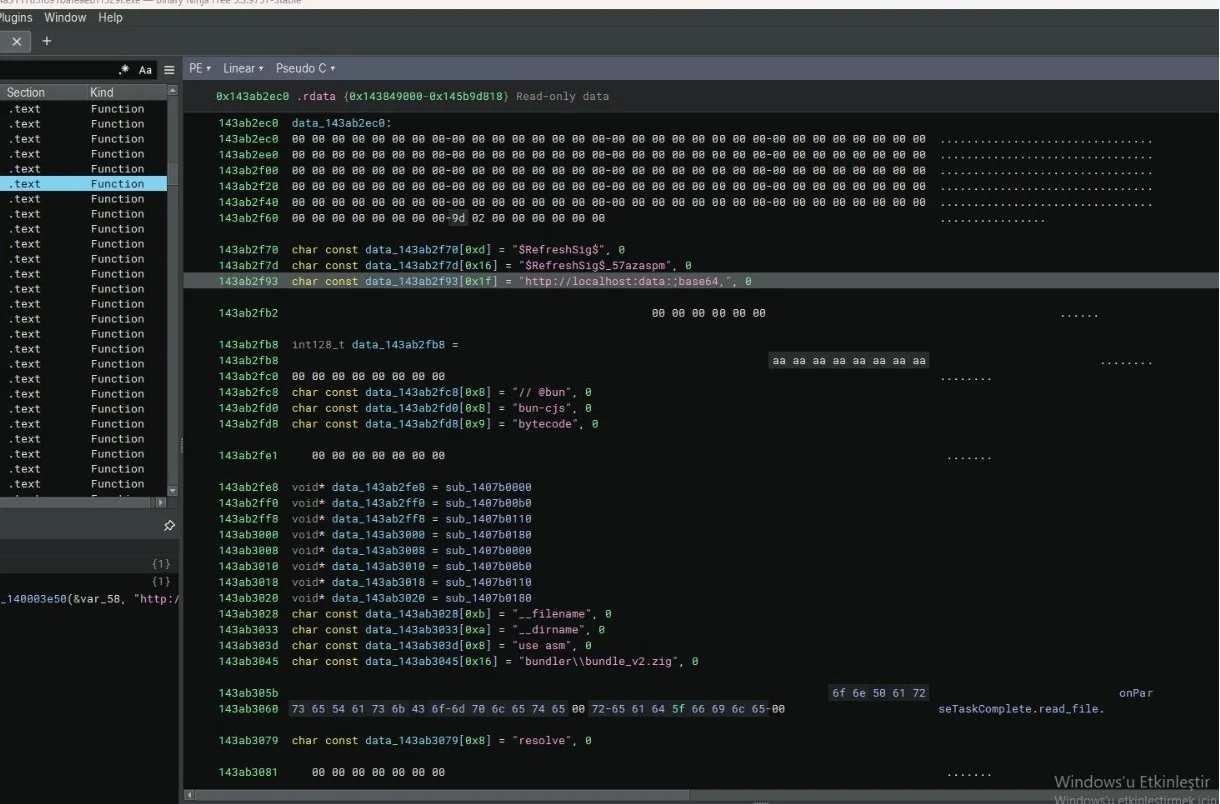
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Code artifacts from research paper implementations

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…

CVE-2026-72704 — Rocq Guard Checker Trusts Corrupted Recursive Tree After Transport

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

Code, aggregate data and LaTeX source for 'Who Patches the Lightning Network? Evidence from Release Lines in Gossip, 2023-2026' (arXiv:2610.30350)

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…