
CVE-2026-101259
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
defensive-toolseducationinformation-gathering+3
oscerd/cve-2026-101259Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
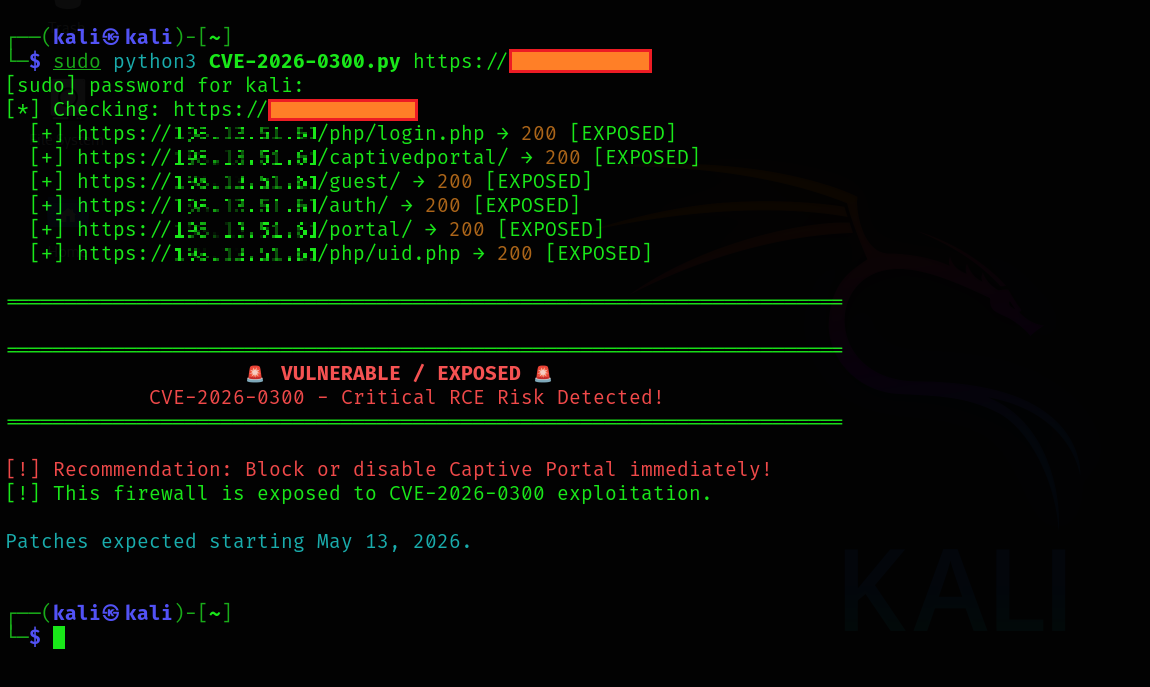 0xredash/cve-2026-0300
Advisory and technical analysis of CVE-2026-0300, a critical unauthenticated buffer overflow RCE in Palo Alto PAN-OS User-ID portals, with affected…
 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 itm-kitware/alignment-cage-challenge-2
CybORG CAGE 2 environment updated for the paper "Alignment of Autonomous Cyber Defense Agents via Adaptive Policy Shaping"
 isec-tugraz/cjag
C implementation of a cache-based jamming agreement that establishes a cross-VM cache covert channel between co-located virtual machines for research…
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 0xblackash/cve-2026-101767
Advisory and technical research analysis of CVE-2026-101767, a critical unauthenticated RCE in Oracle E-Business Suite Application Object Library,…
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 4rdr/proofs
Collection of CVE findings, proof-of-concept references, and vulnerability research notes, including ExploitDB entries and credited security…
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 abraxas/qemu-xhci-complete-uaf
QEMU 11.1.2 - High - Local - UAF - xhci_complete leftover of CVE-2026-17588 doorbell DMA
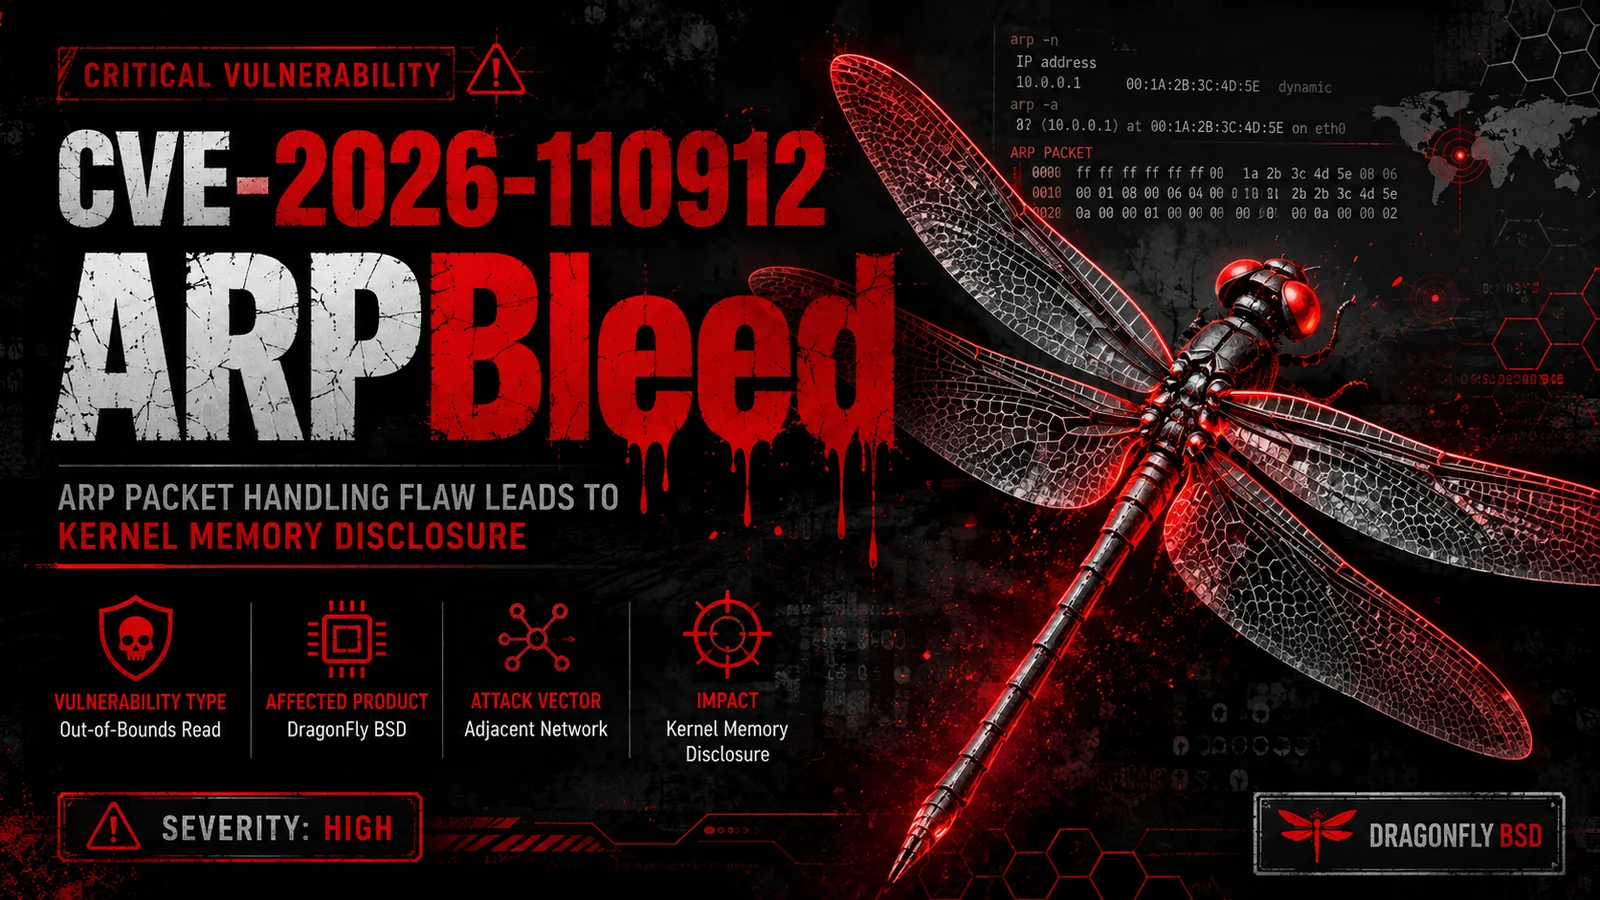 0xblackash/cve-2026-110912
Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 abraxas/pfsense-api-example-ssl-verify
pfSense Plus MIM API toolkit b4acd7ca - Medium - Remote - Privilege leftover - official samples verify_ssl=False
 abraxas/spark-history-zip-symlink
Apache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink