
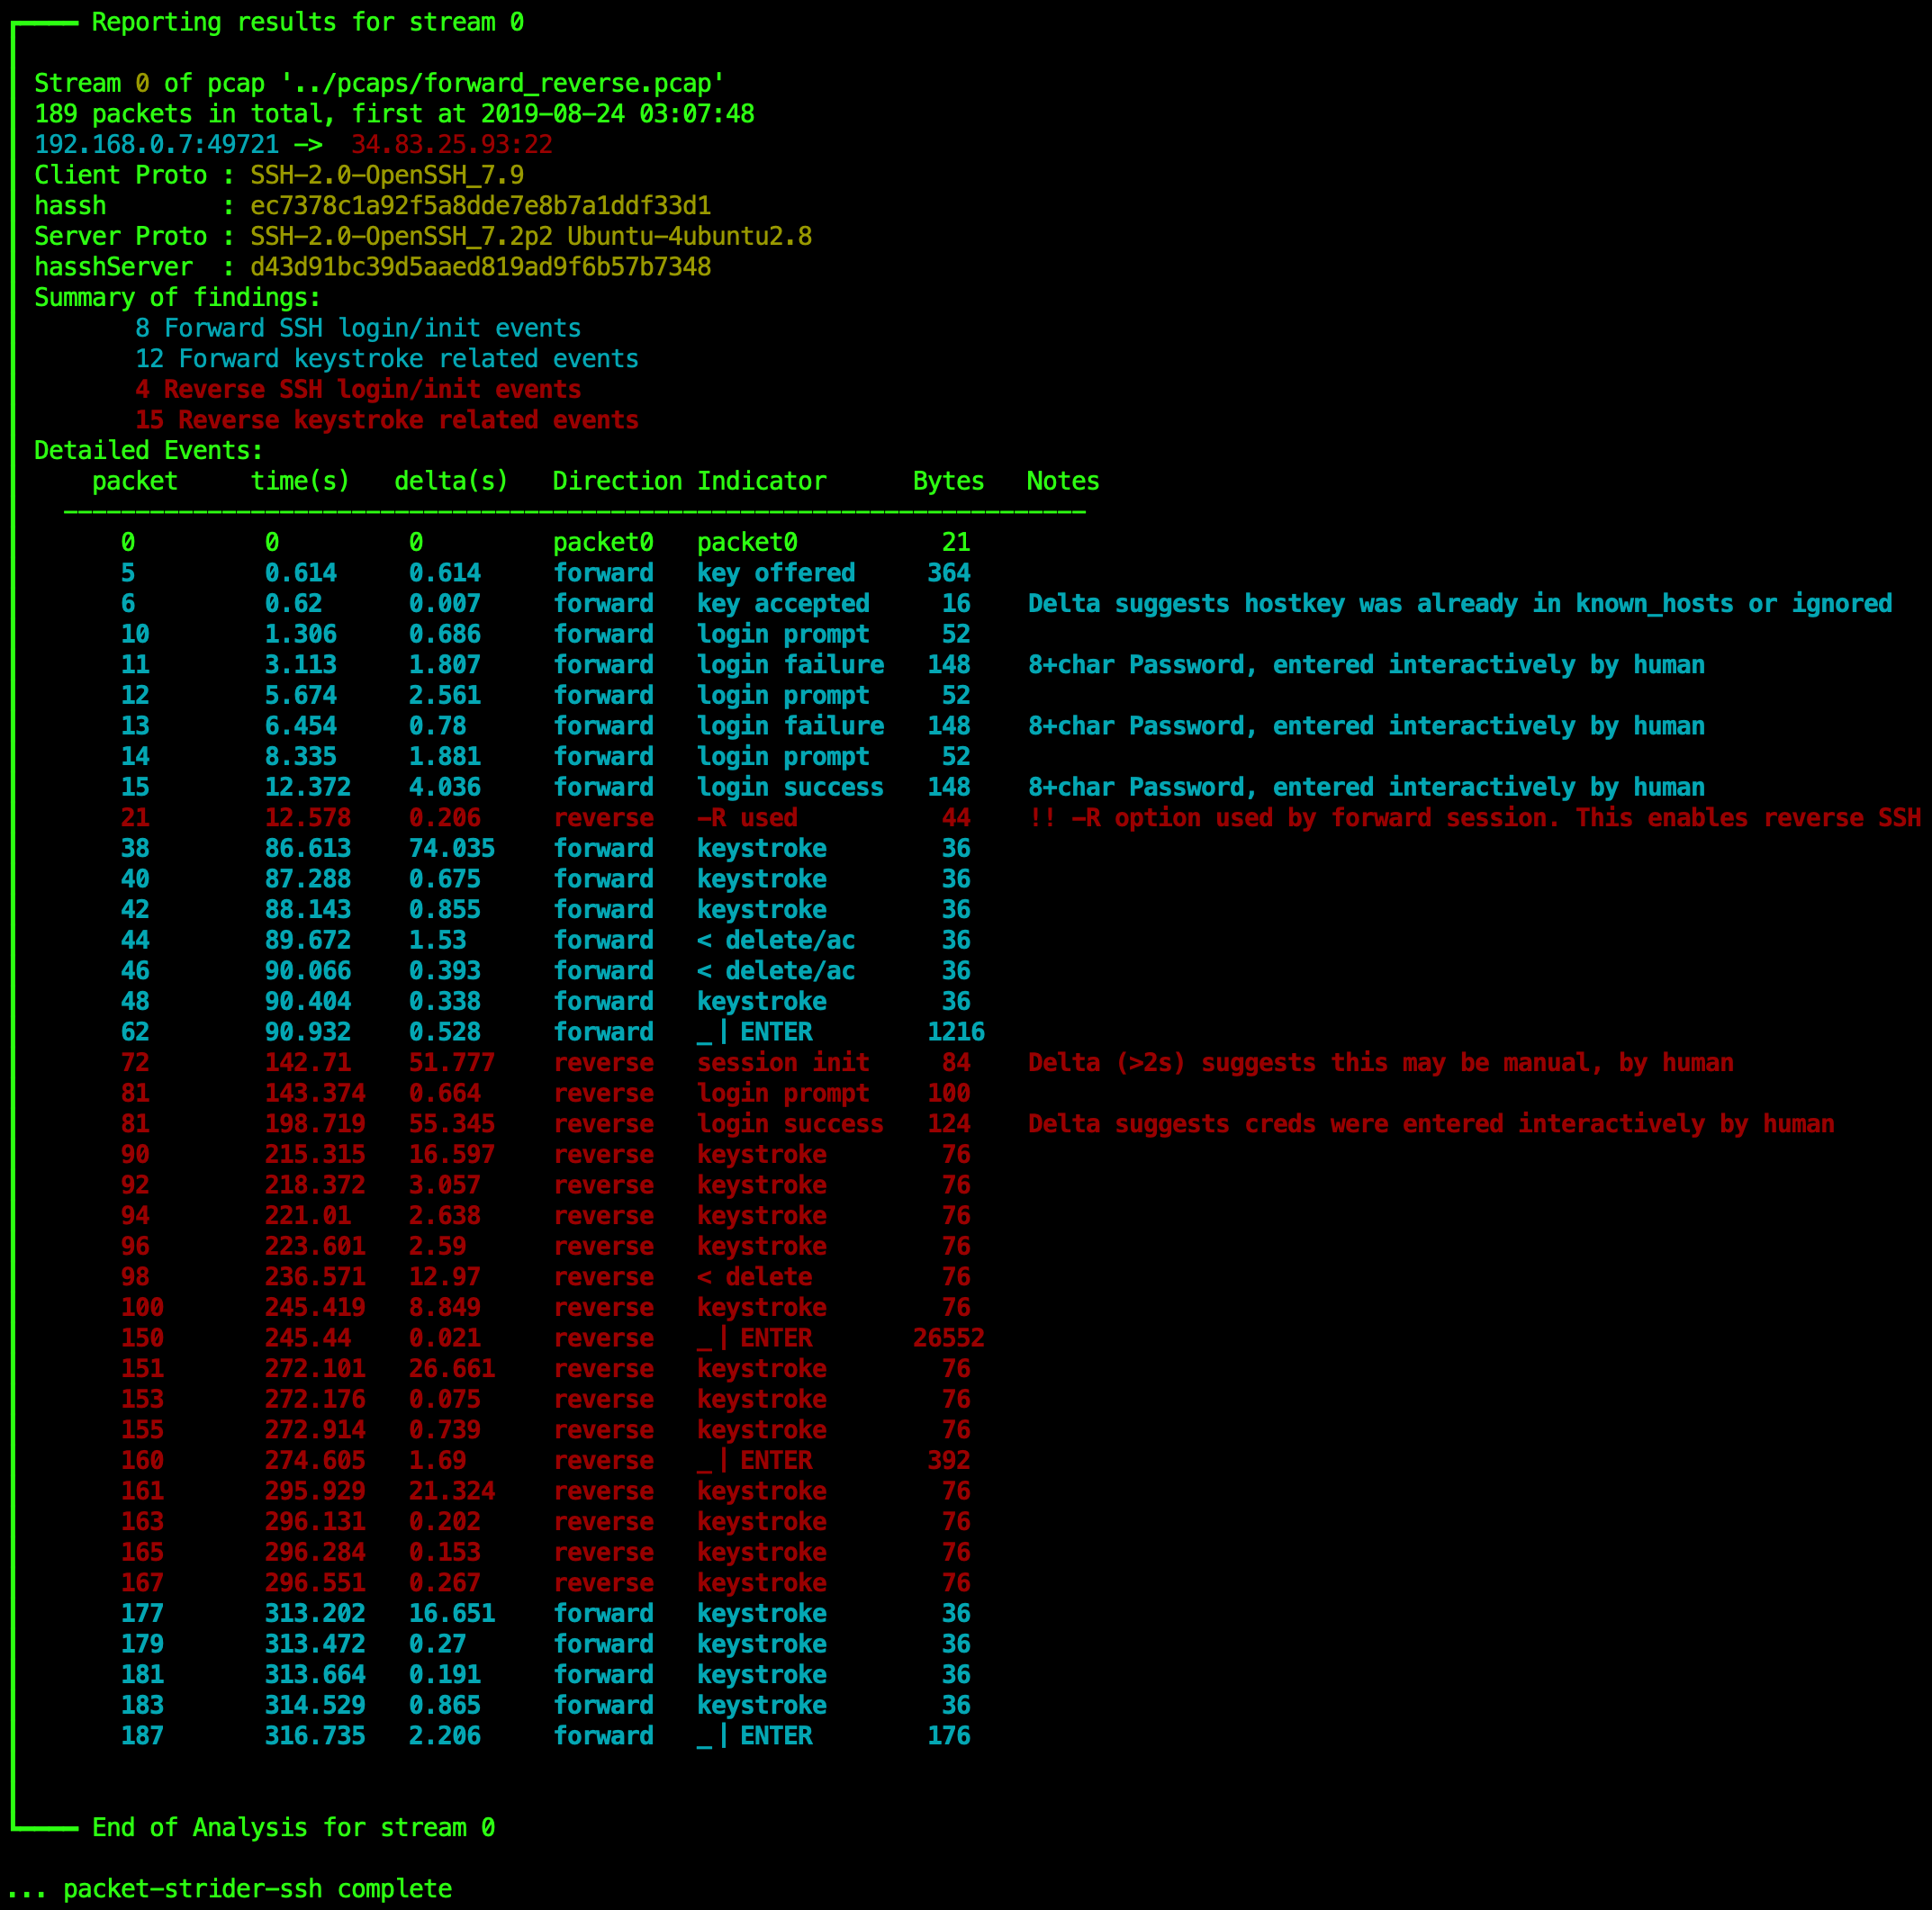
packetStrider
 benjeems/packetstrider
A network packet forensics tool for SSH
anomaly-detectionforensicsintrusion-detection+5
benjeems/packetstriderA network packet forensics tool for SSH
 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…
 shadowy-pycoder/arpspoof
A tool to perform ARP spoofing
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
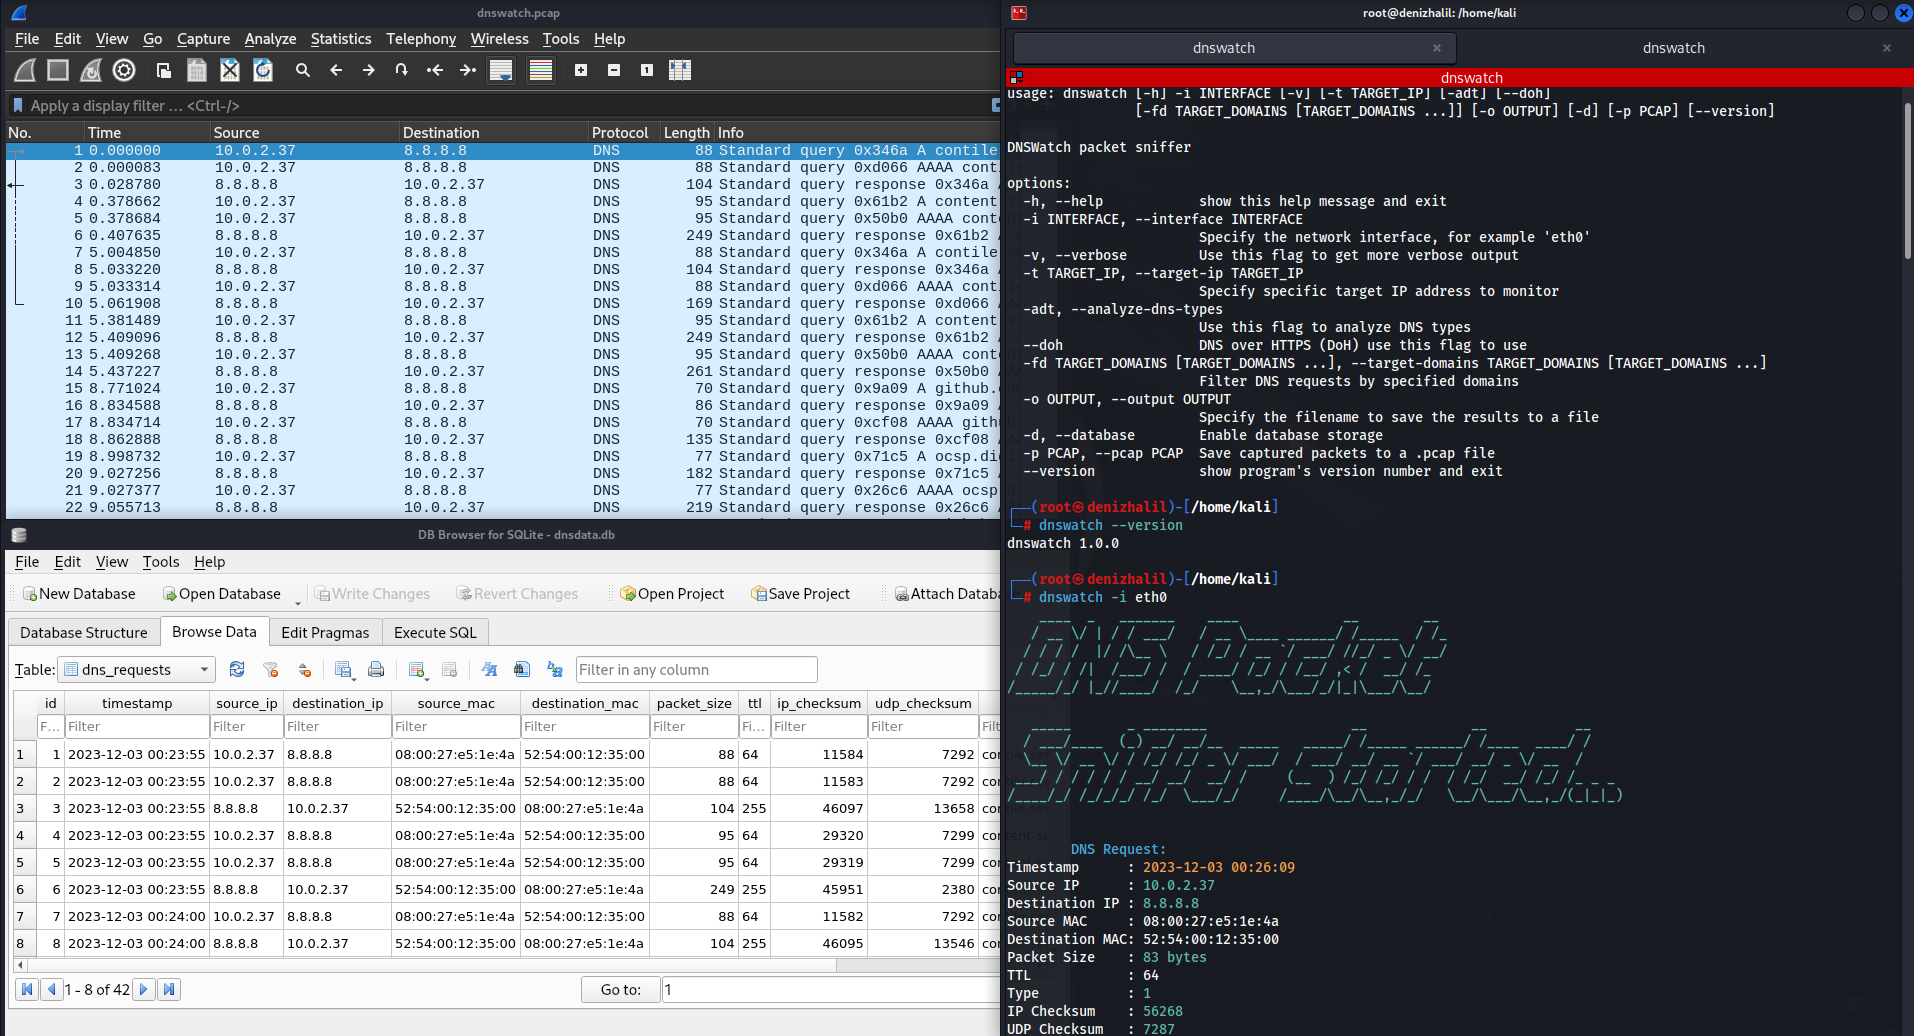 halildeniz/dnswatch
DNS traffic sniffer and analyzer for monitoring, filtering, and detecting anomalies in DNS queries. Features include PCAP export, DoH support, and a…
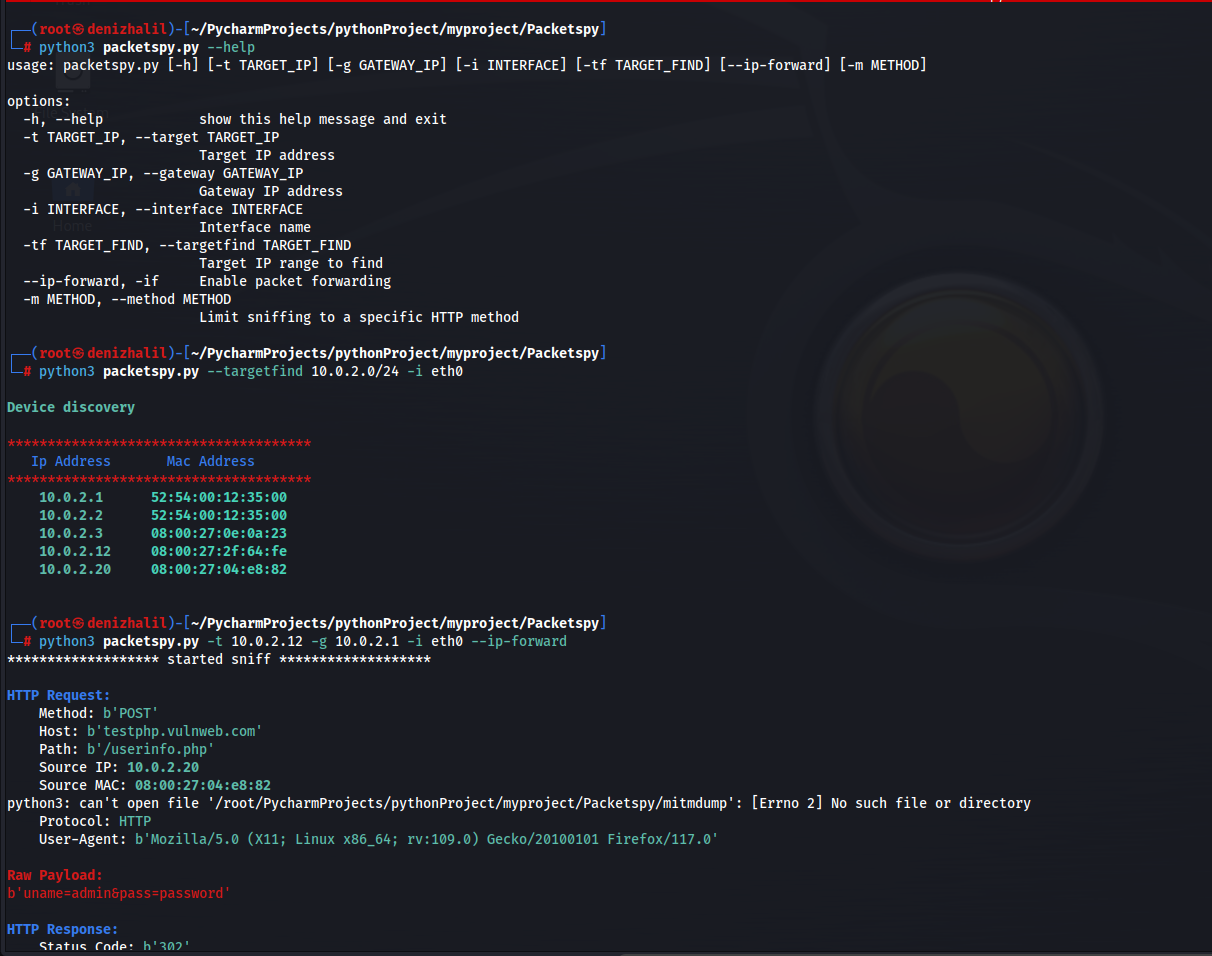 halildeniz/packetspy
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
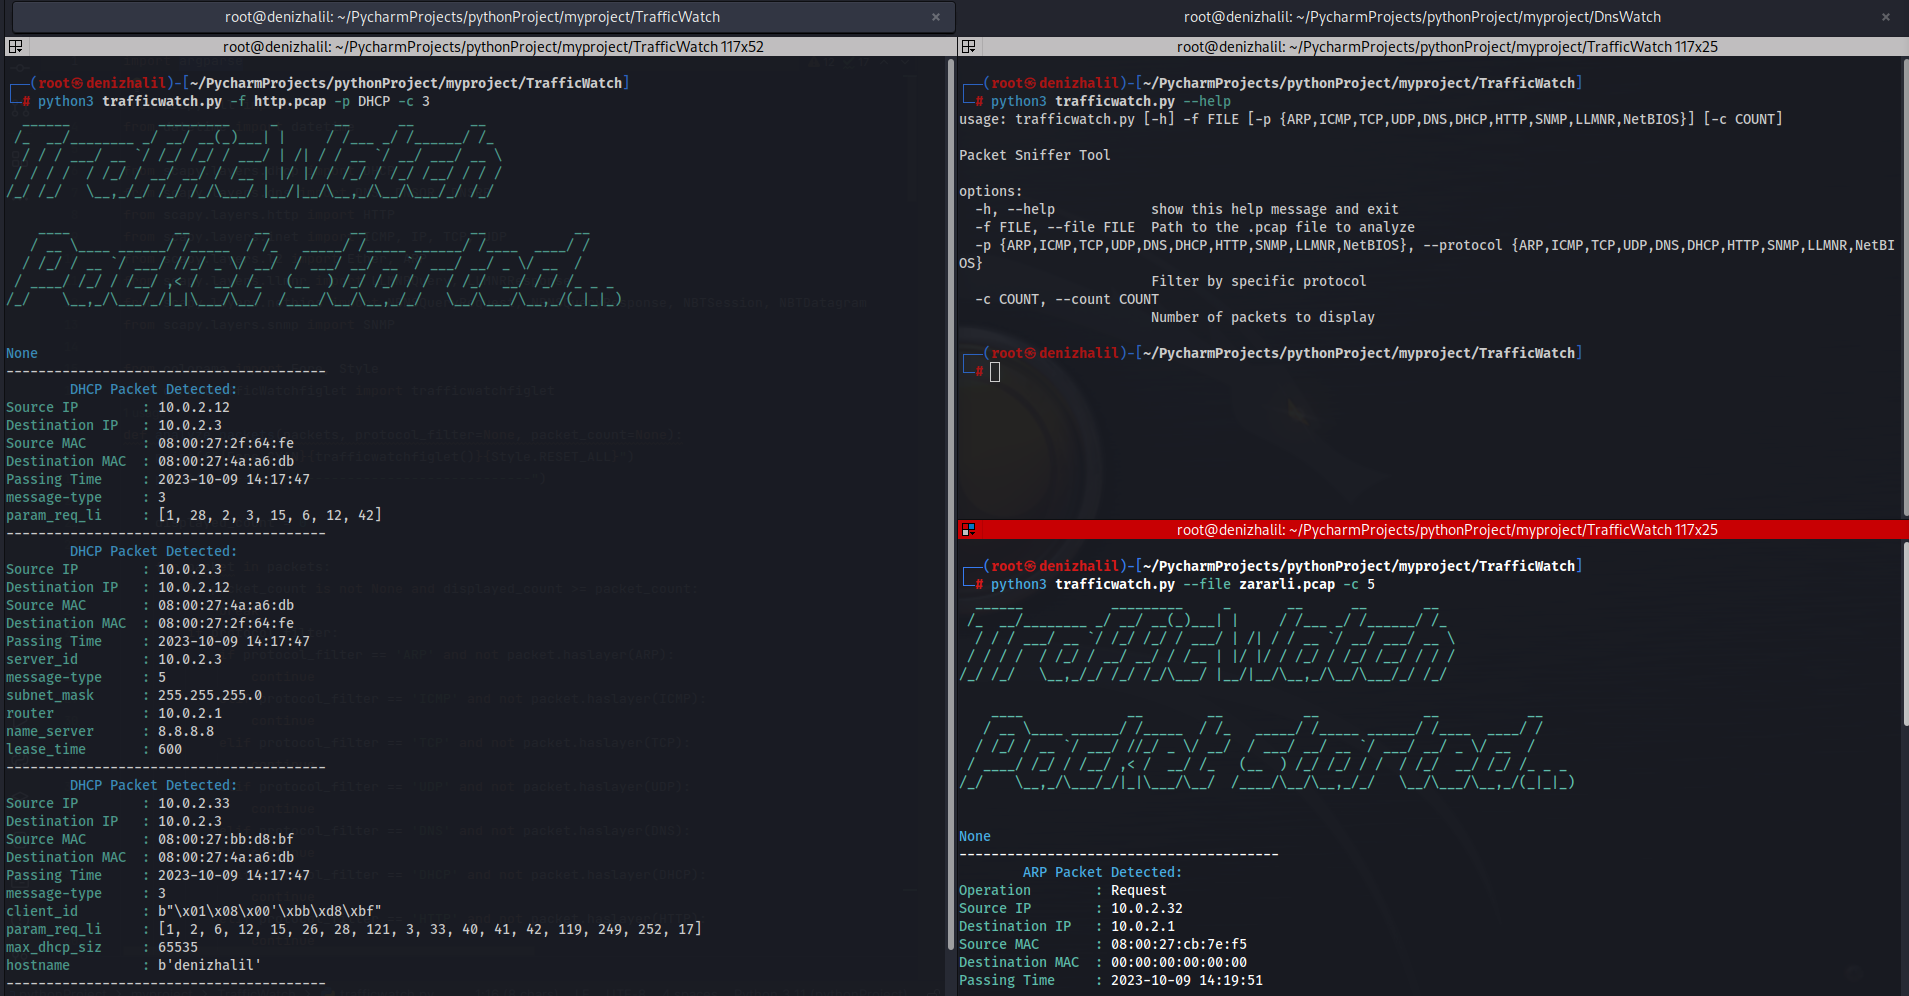 halildeniz/trafficwatch
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 jip-0-0-0-0-0/cve-2024-38063-scanner
A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…
 impostorkeanu/eavesarp
Analyze ARP requests to identify intercommunicating hosts and stale network address configurations (SNACs)
 ivanvza/arpy
Mac OSX ARP spoof (MiTM) tool that can also plug into Gource
 royhills/arp-scan
Fast ARP-based network scanner for discovering and fingerprinting IPv4 hosts on local networks, with vendor lookup, adjustable scan rates, and…
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 halildeniz/dosinator
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
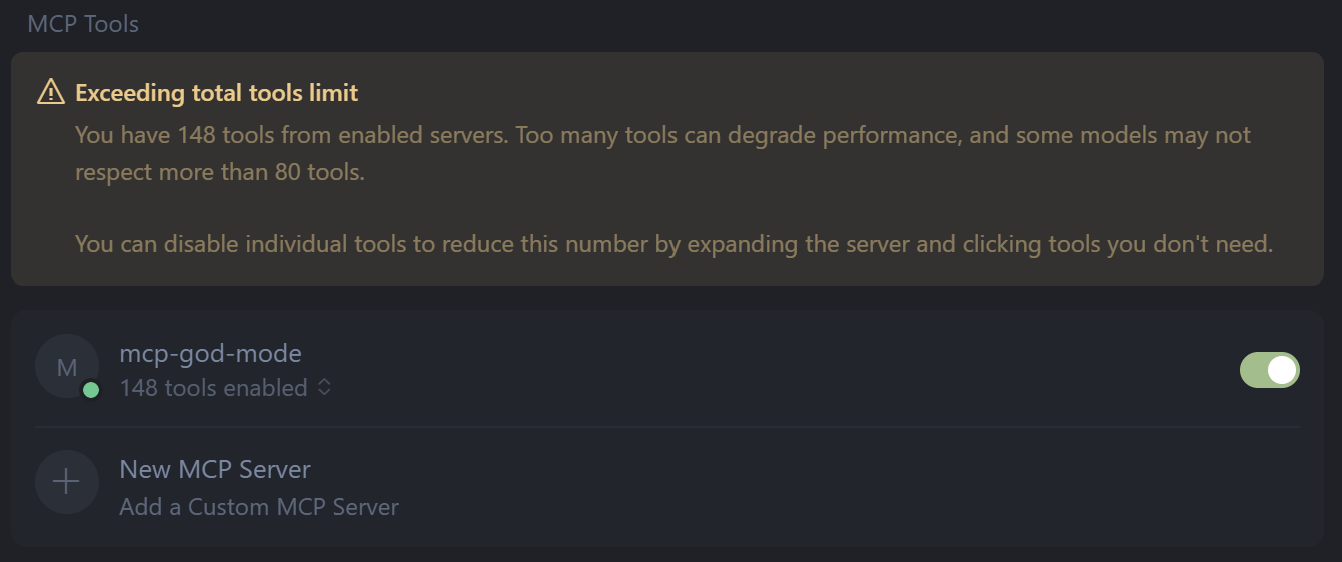 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.