
android
 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
android-securityexploit-frameworksmobile-security+4
3.7k5 years ago
csploit/androidcSploit - The most complete and advanced IT security professional toolkit on Android.
 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 lele394/dnsnitch
DNSnitch is a local, privacy-first DNS server that puts you in complete control of your network traffic. Unlike passive blocklists, DNSnitch operates…
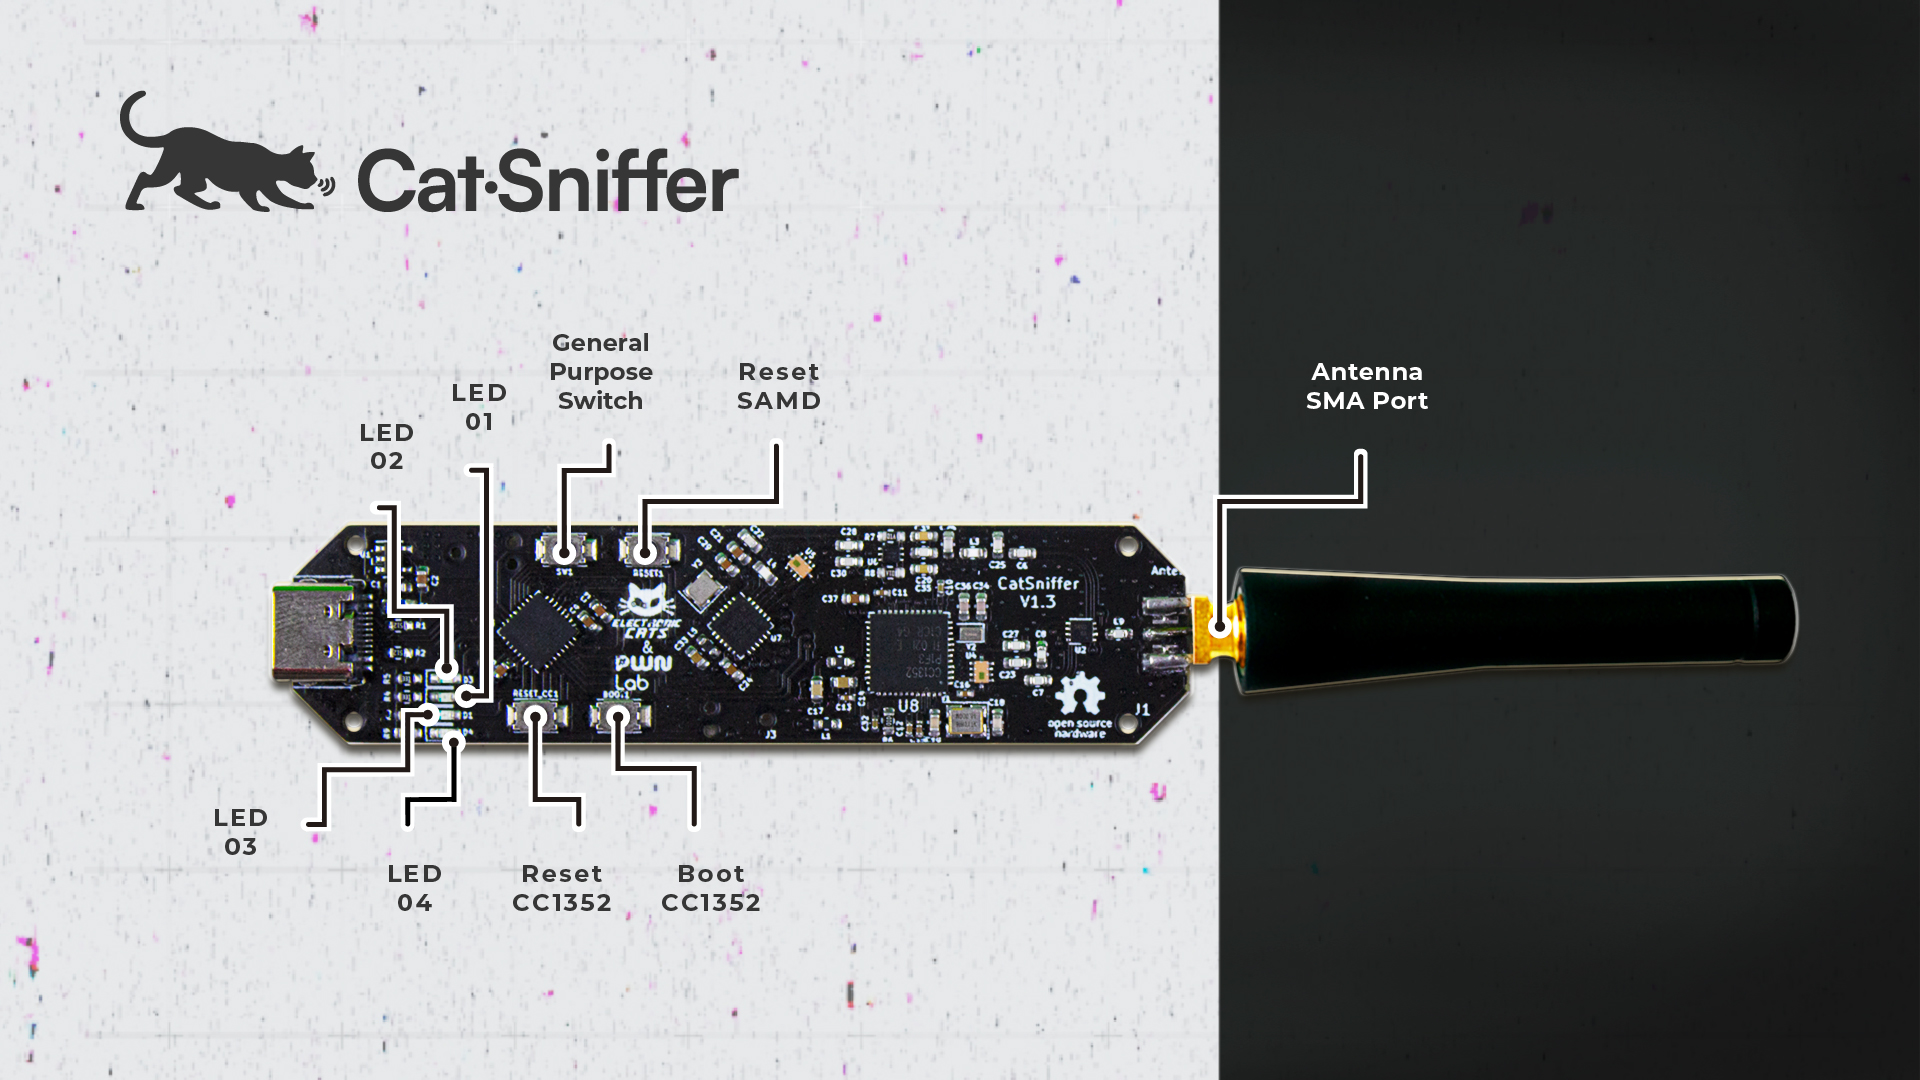 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
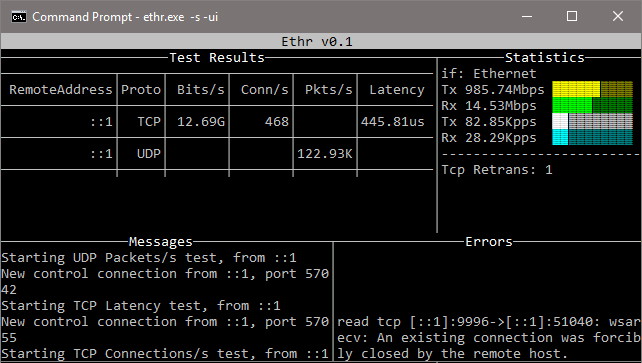 microsoft/ethr
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
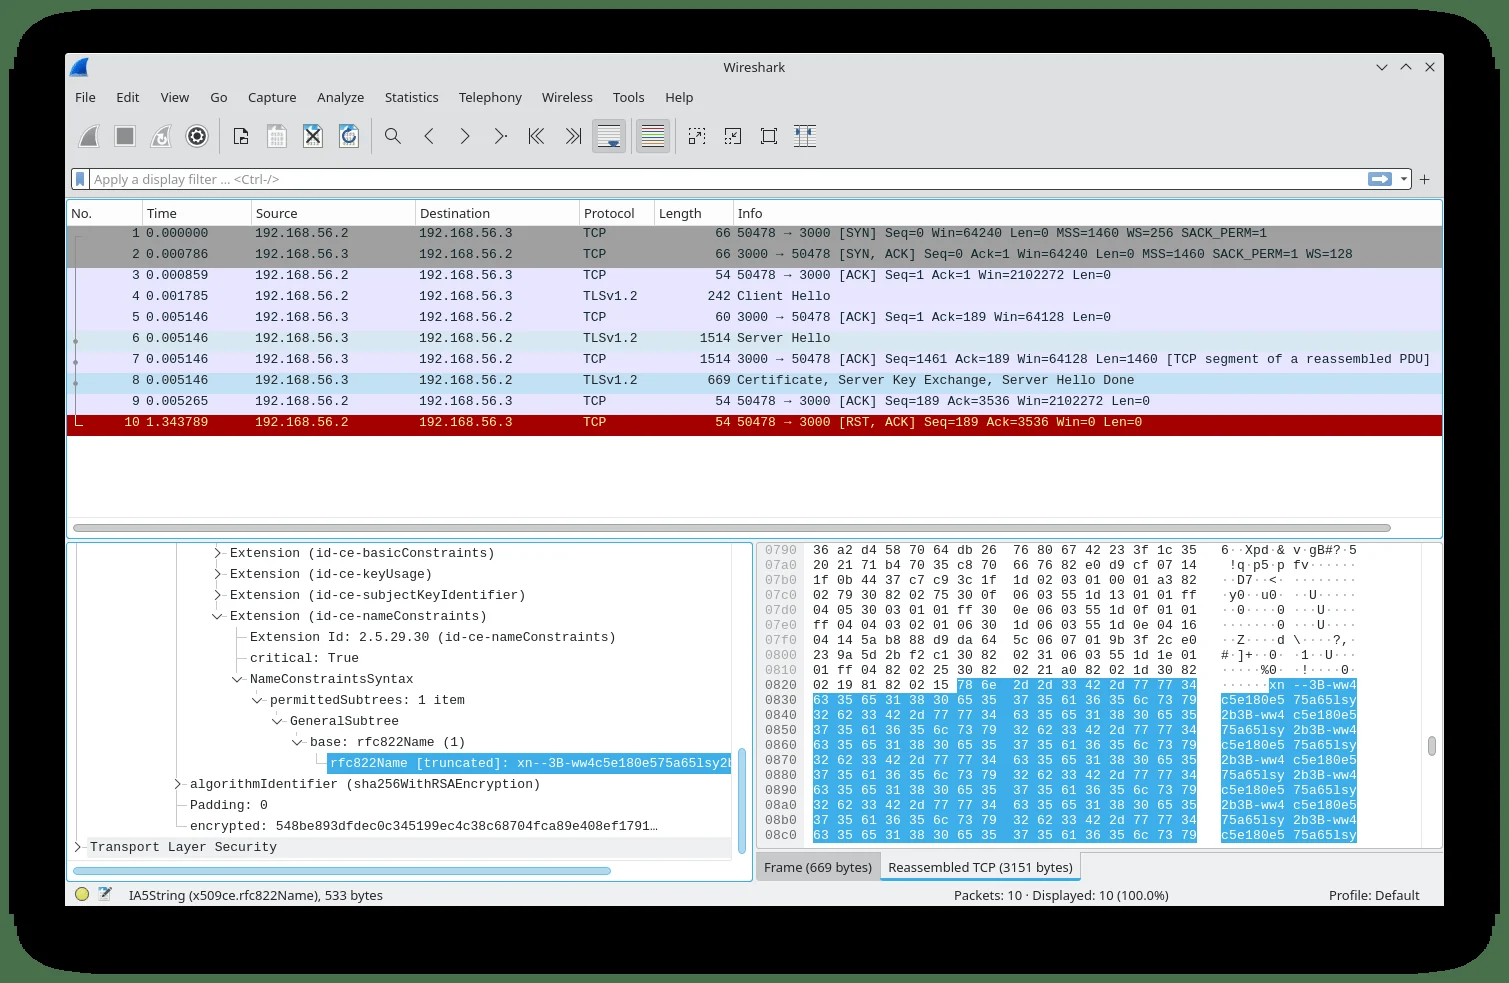 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 lixiang957/cve-2021-33959
Proof-of-concept exploit for CVE-2021-33959 demonstrating UDP reflection amplification attack against Plex Media Server via crafted M-SEARCH packets…
 jtripper/sslnuke
Transparent proxy that decrypts SSL traffic and prints out IRC messages.
 hengyoush/kyanos
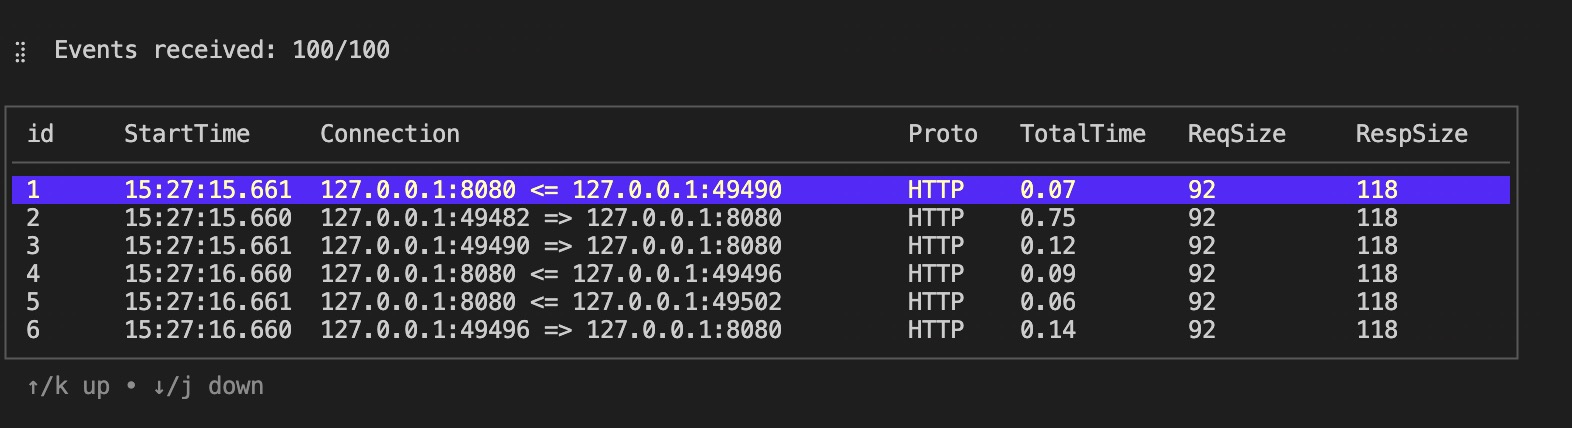
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
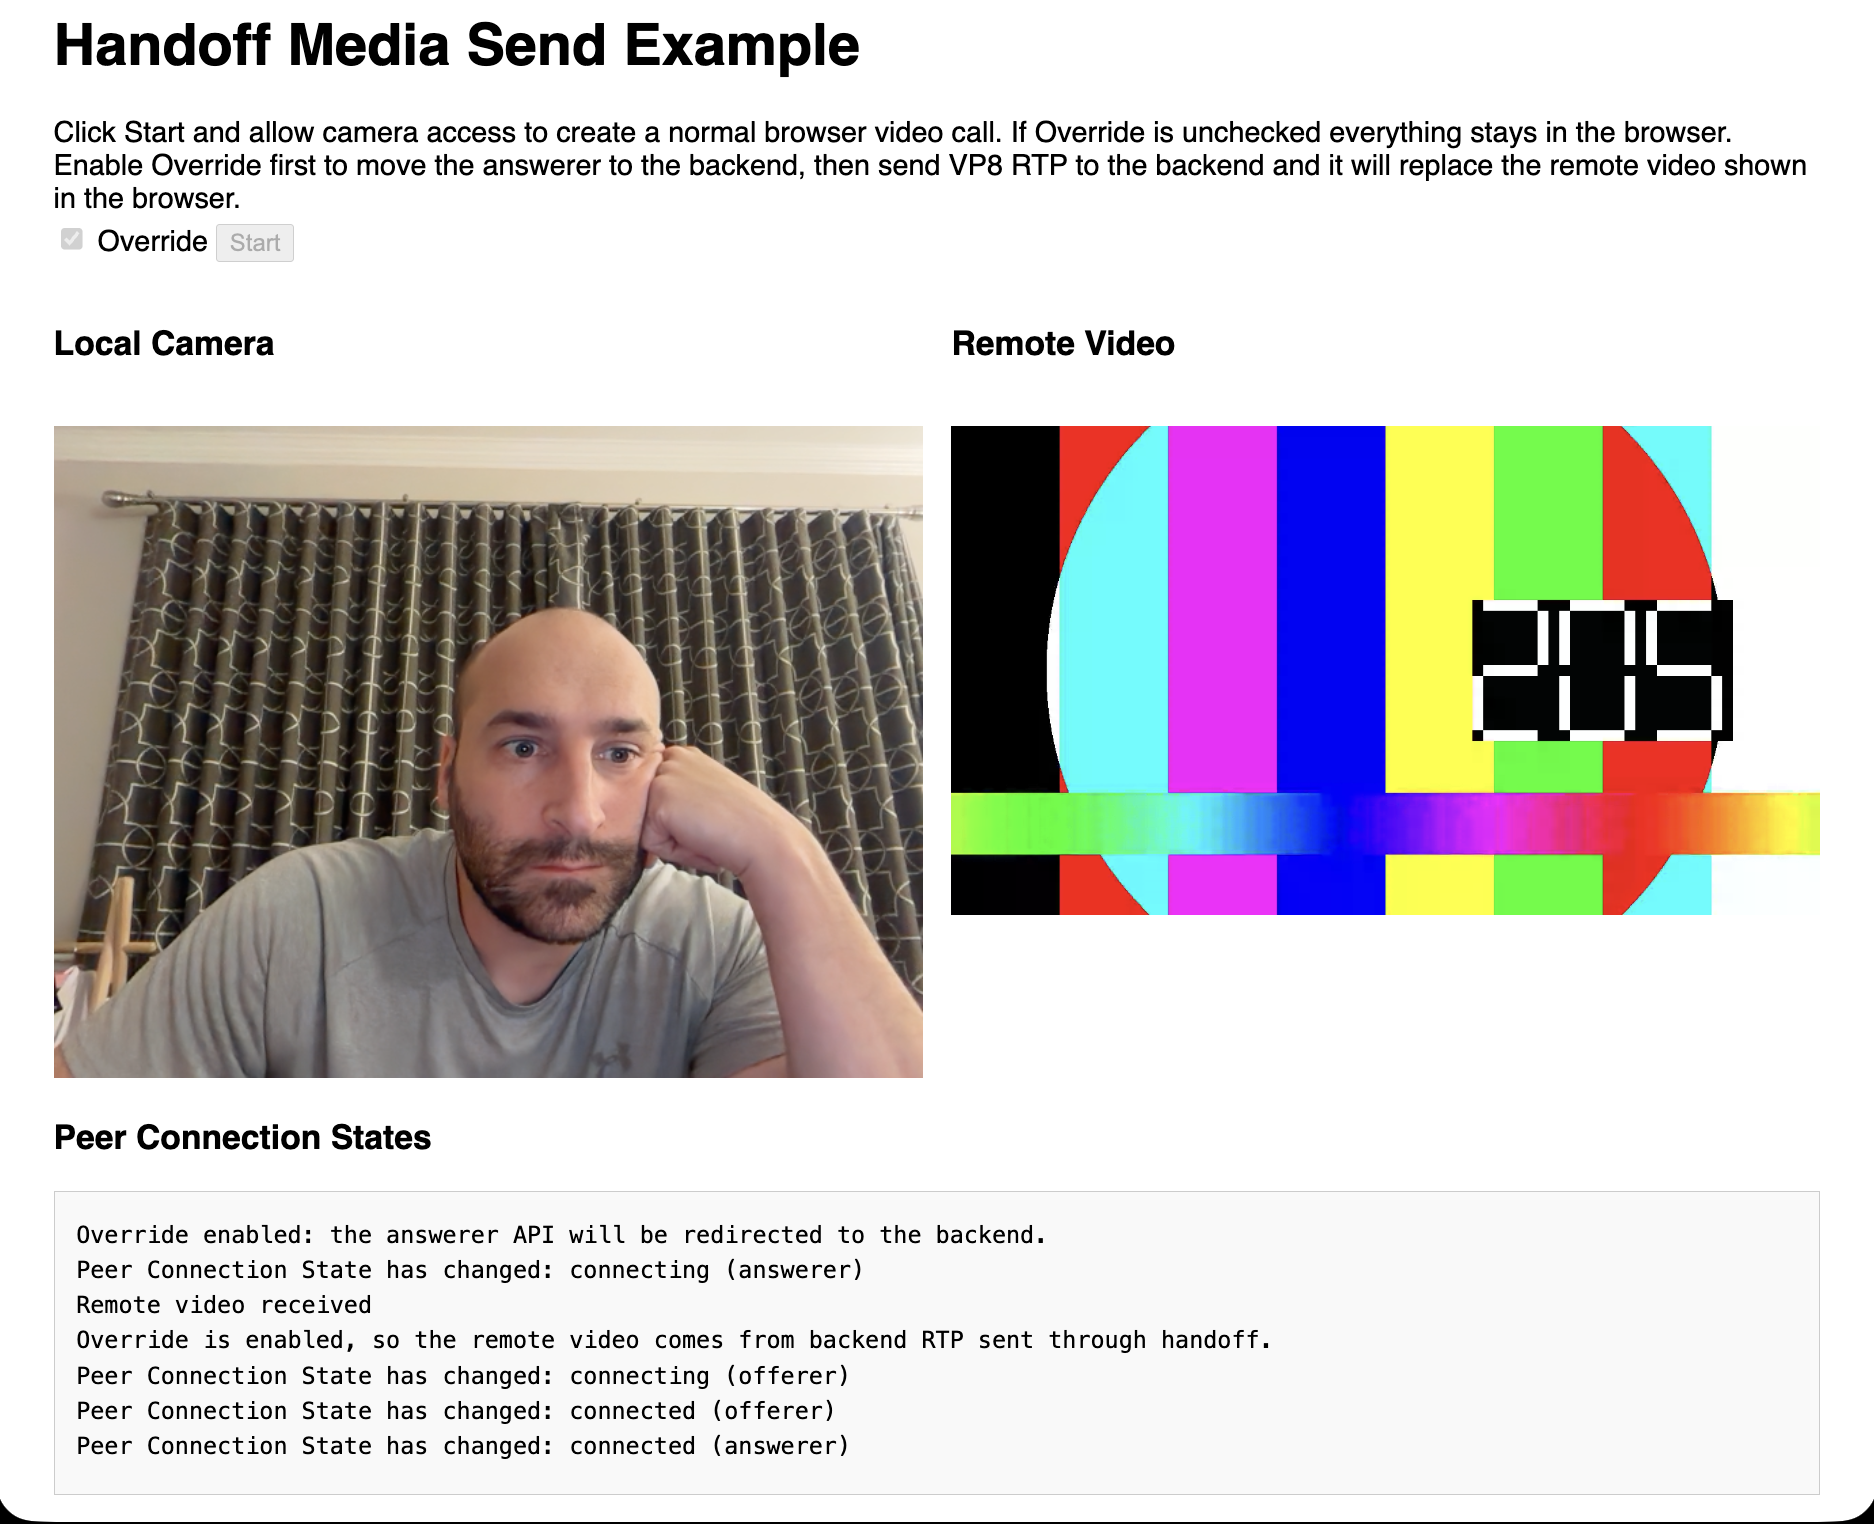 pion/handoff
Start WebRTC in the browser—run it somewhere else