
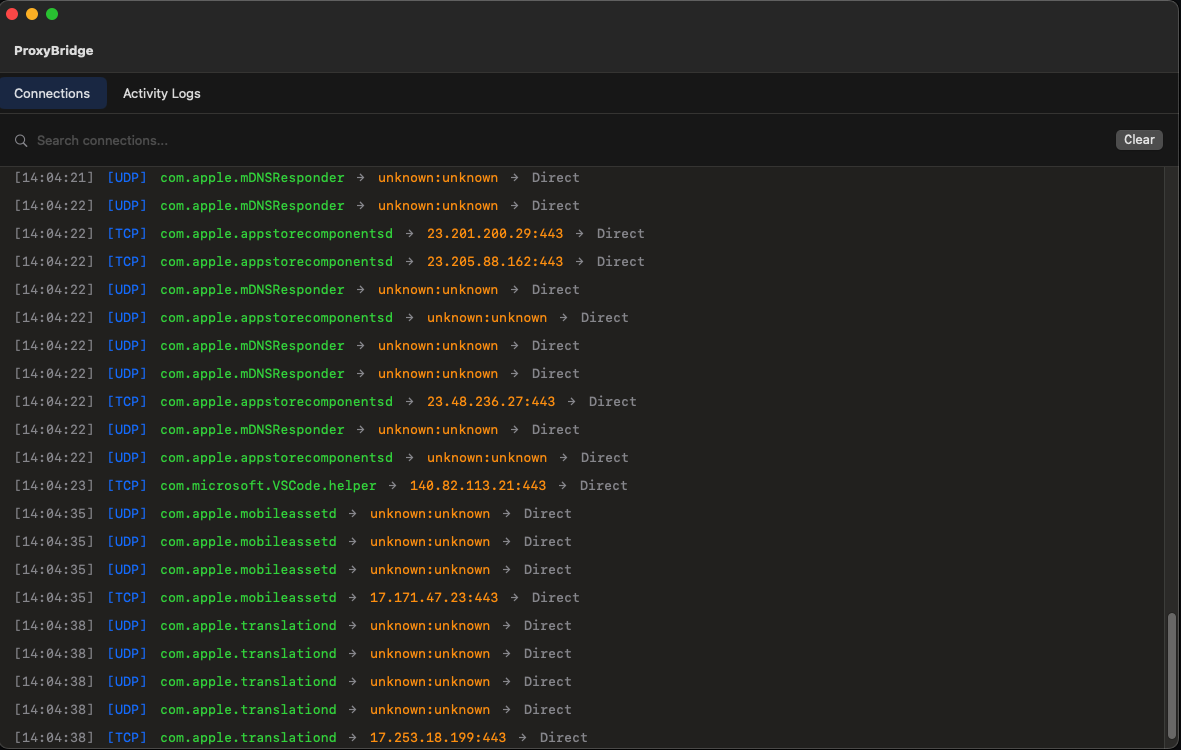
ProxyBridge
 interceptsuite/proxybridge
Force Proxy to any Windows/MacOS/Linux Application TCP and UDP traffic
network-securitypacket-sniffing-analysispenetration-testing+3
5.7k
interceptsuite/proxybridgeForce Proxy to any Windows/MacOS/Linux Application TCP and UDP traffic
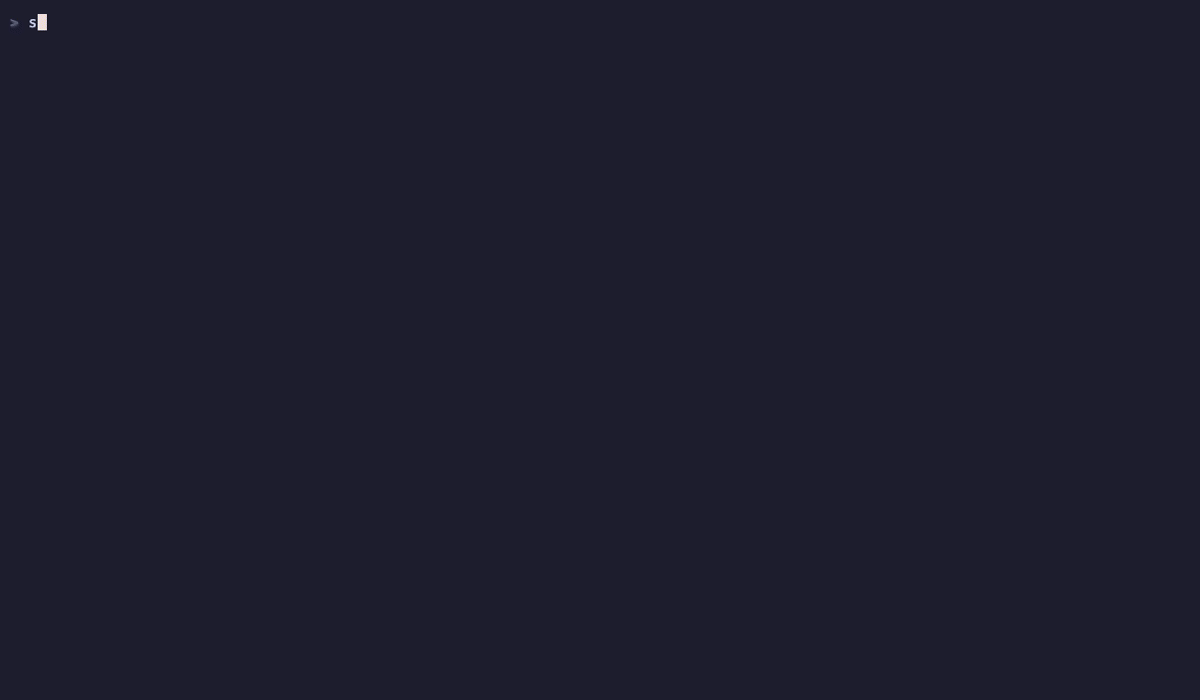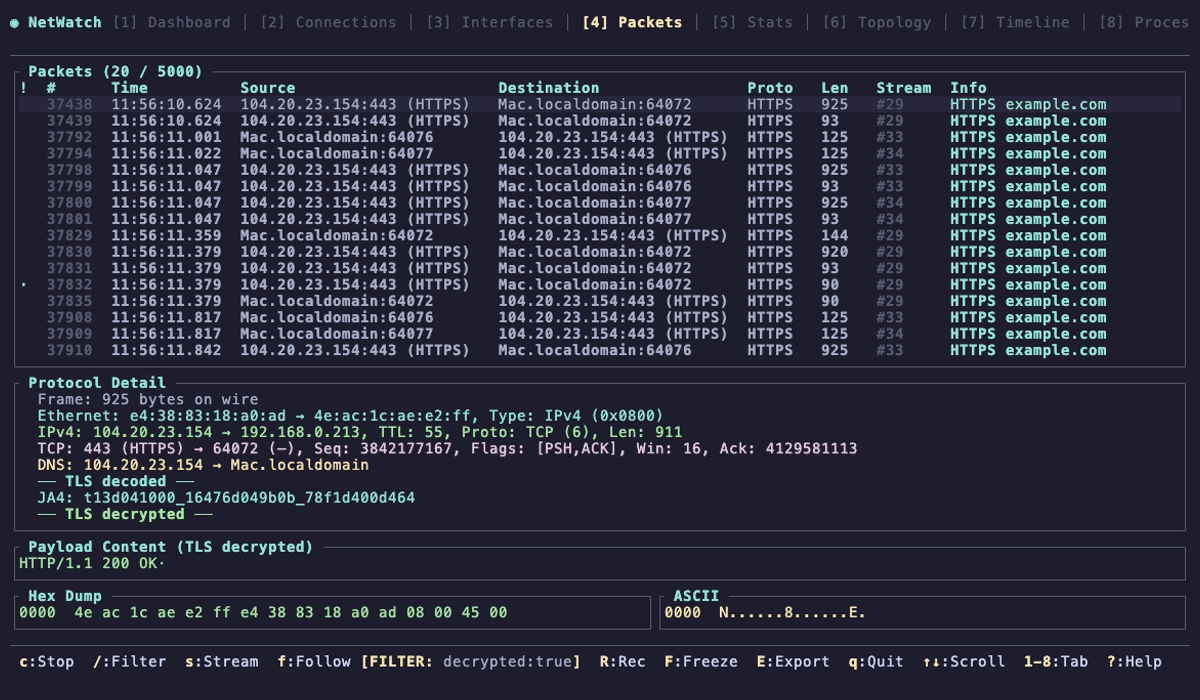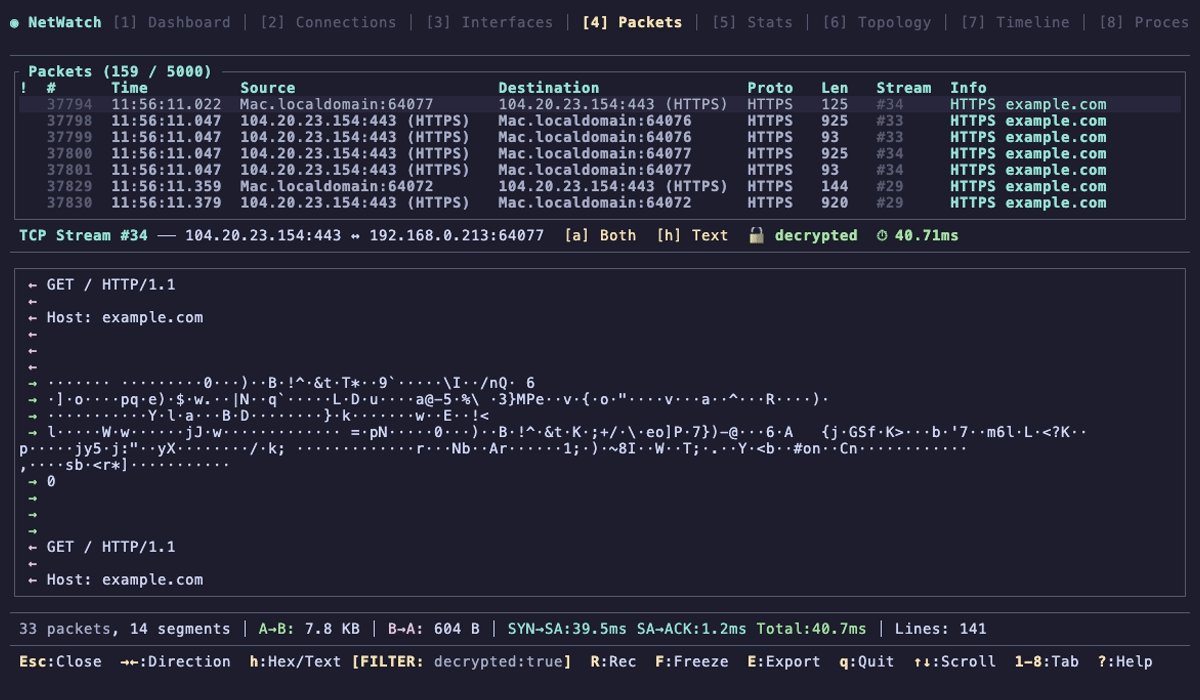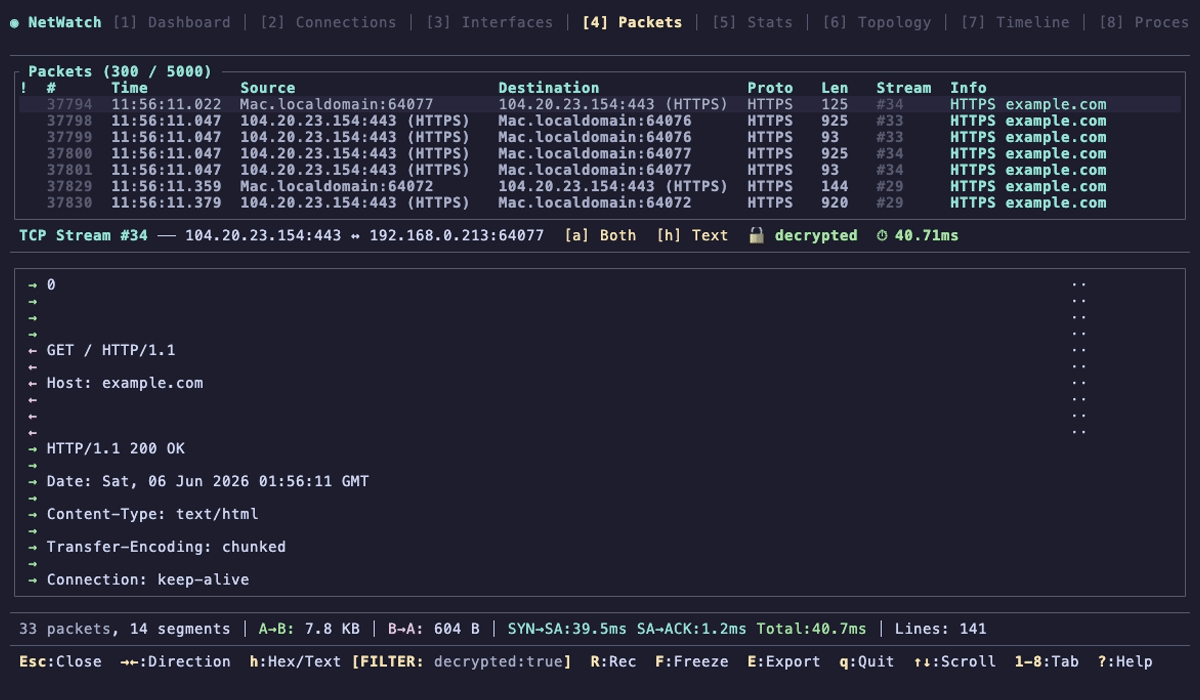 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
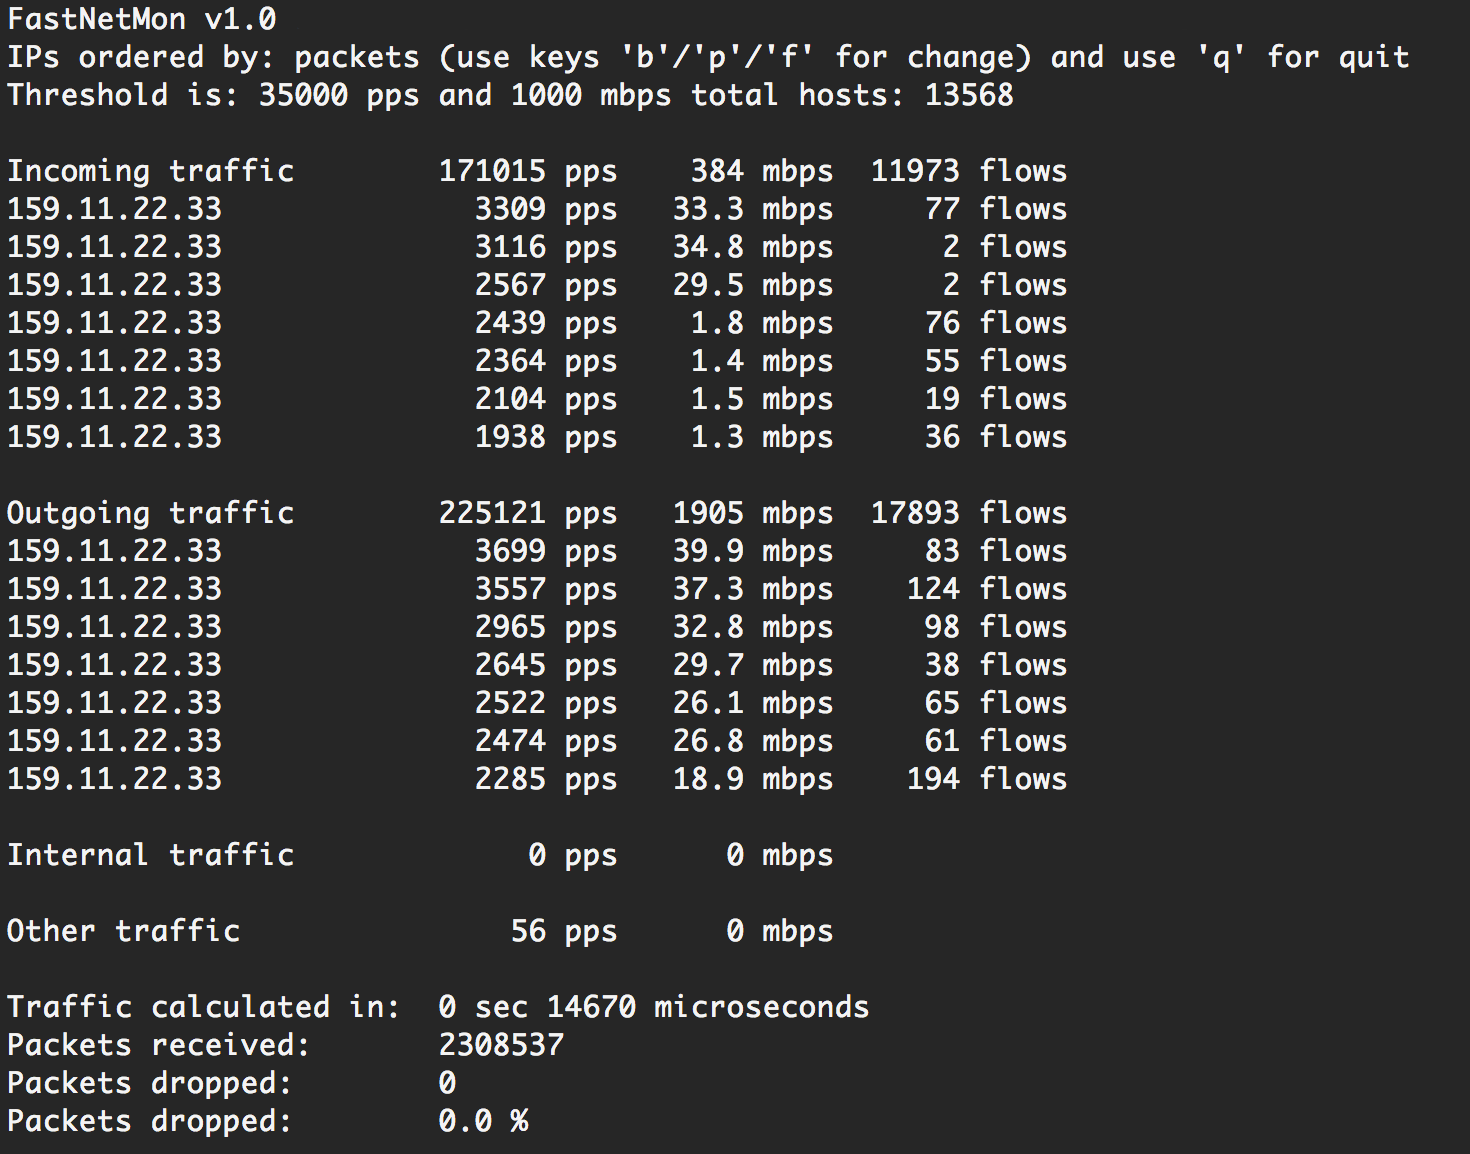 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 projectdiscovery/proxify
A versatile and portable proxy for capturing, manipulating, and replaying HTTP/HTTPS traffic on the go.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
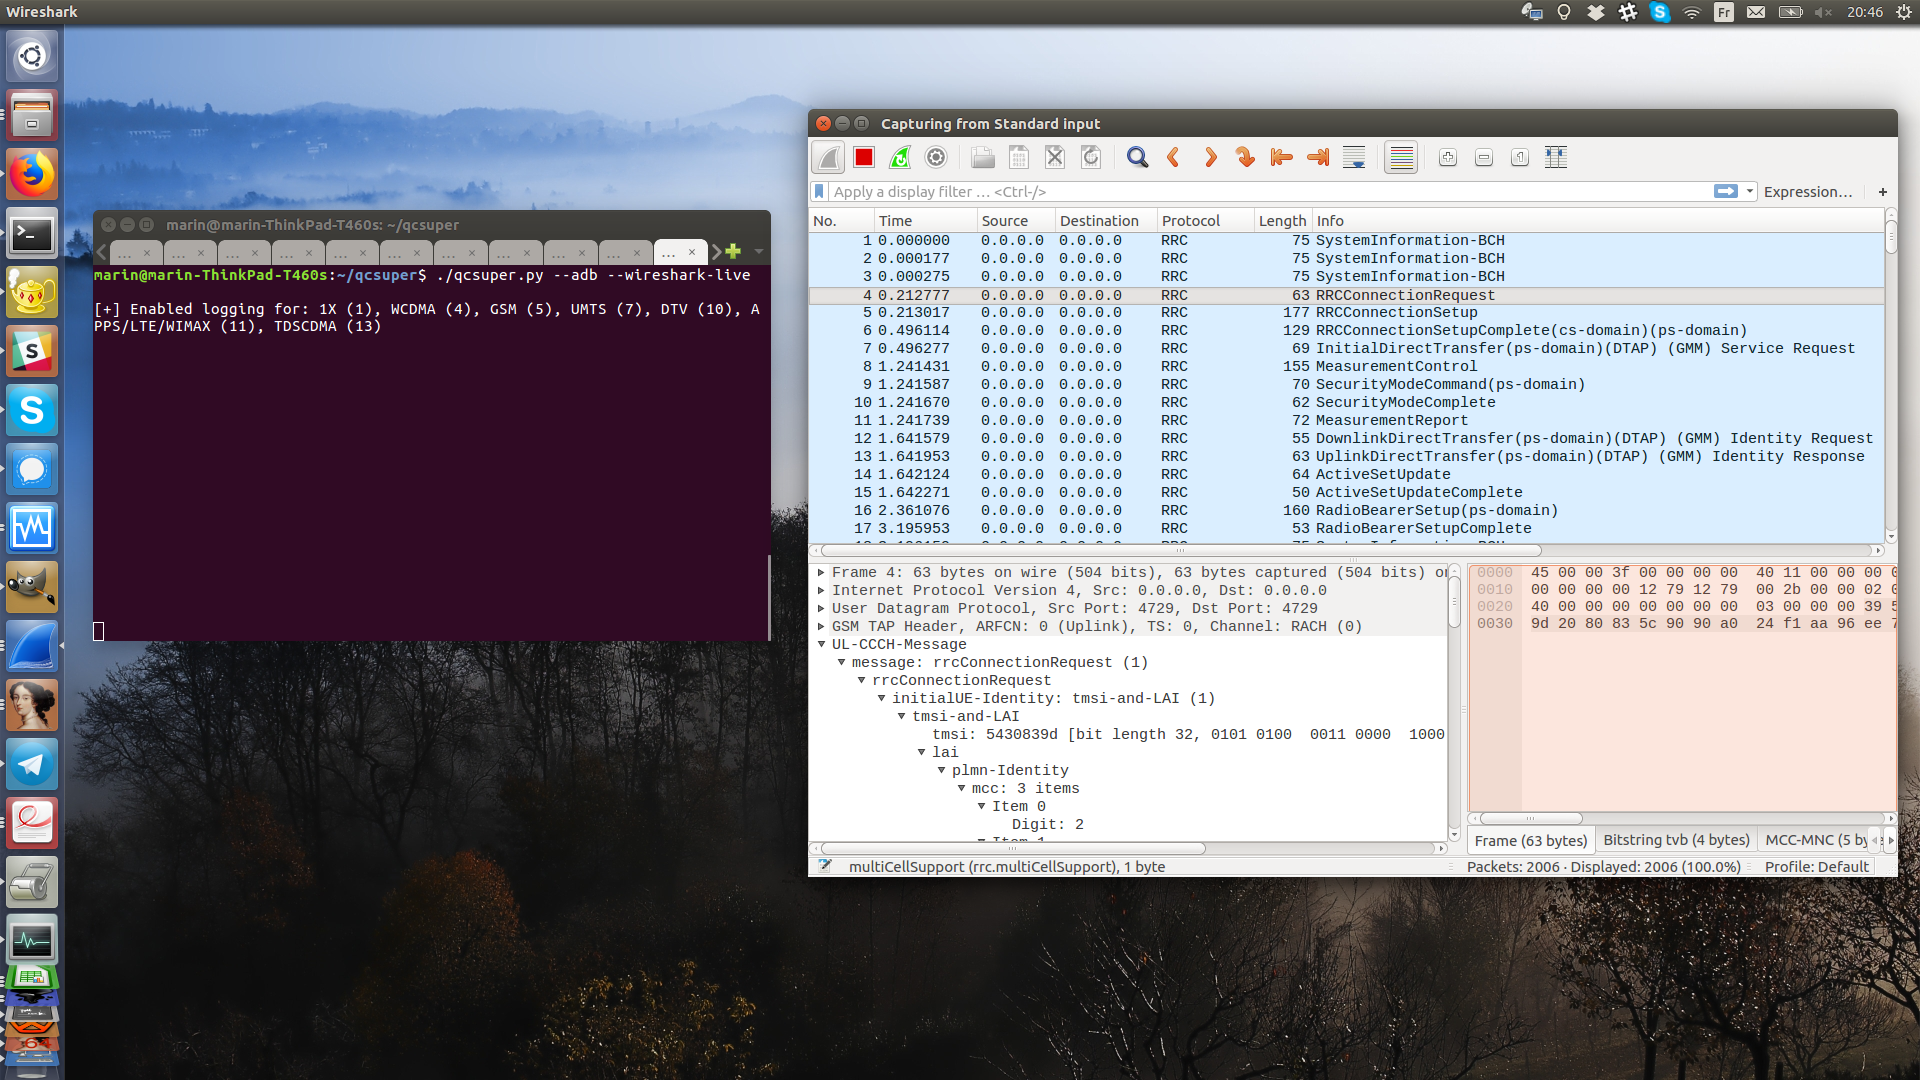 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 occasionpuffbird12/airstrike
Audit Wi-Fi security on Linux with monitor mode, handshake capture, and offline WPA/WPA2 password testing in one guided GUI
 0ct0sec/m5porkchop
ON NO! Someone put an RPG in a packet sniffer
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…