

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
45.1k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
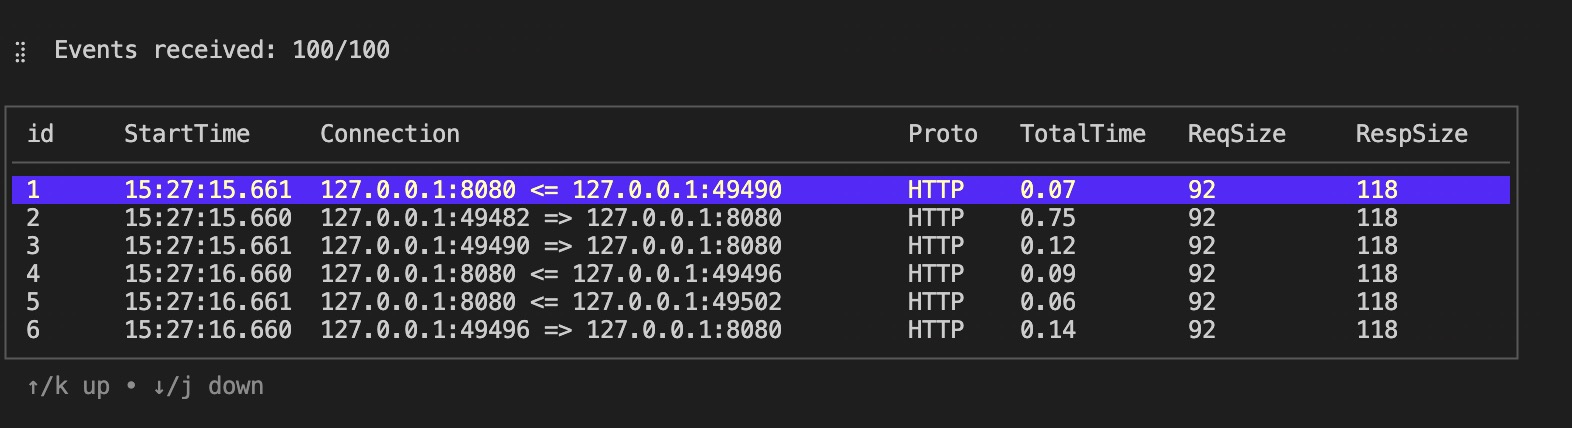 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
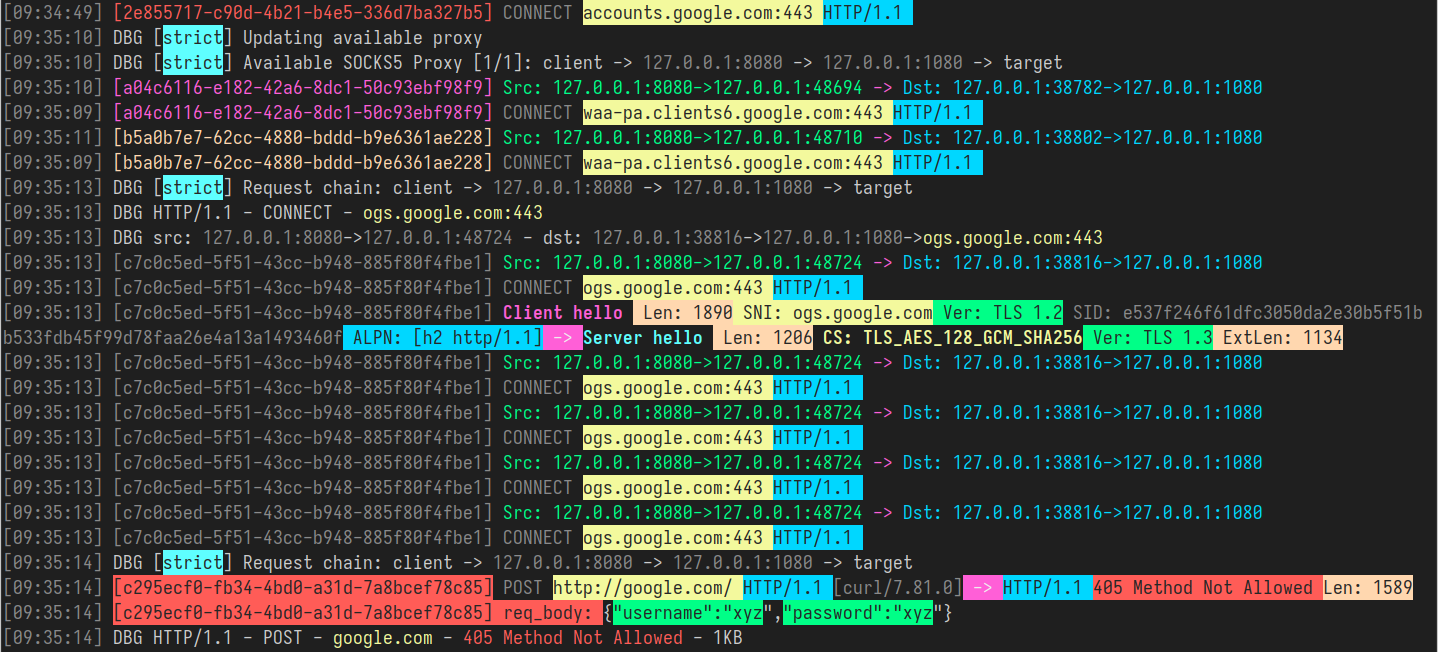 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
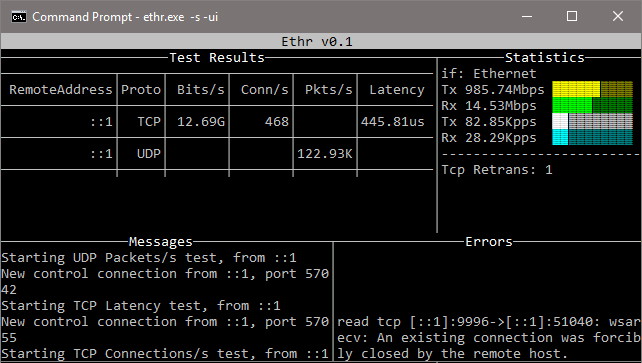 microsoft/ethr
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 omriher/captipper
Malicious HTTP traffic explorer
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
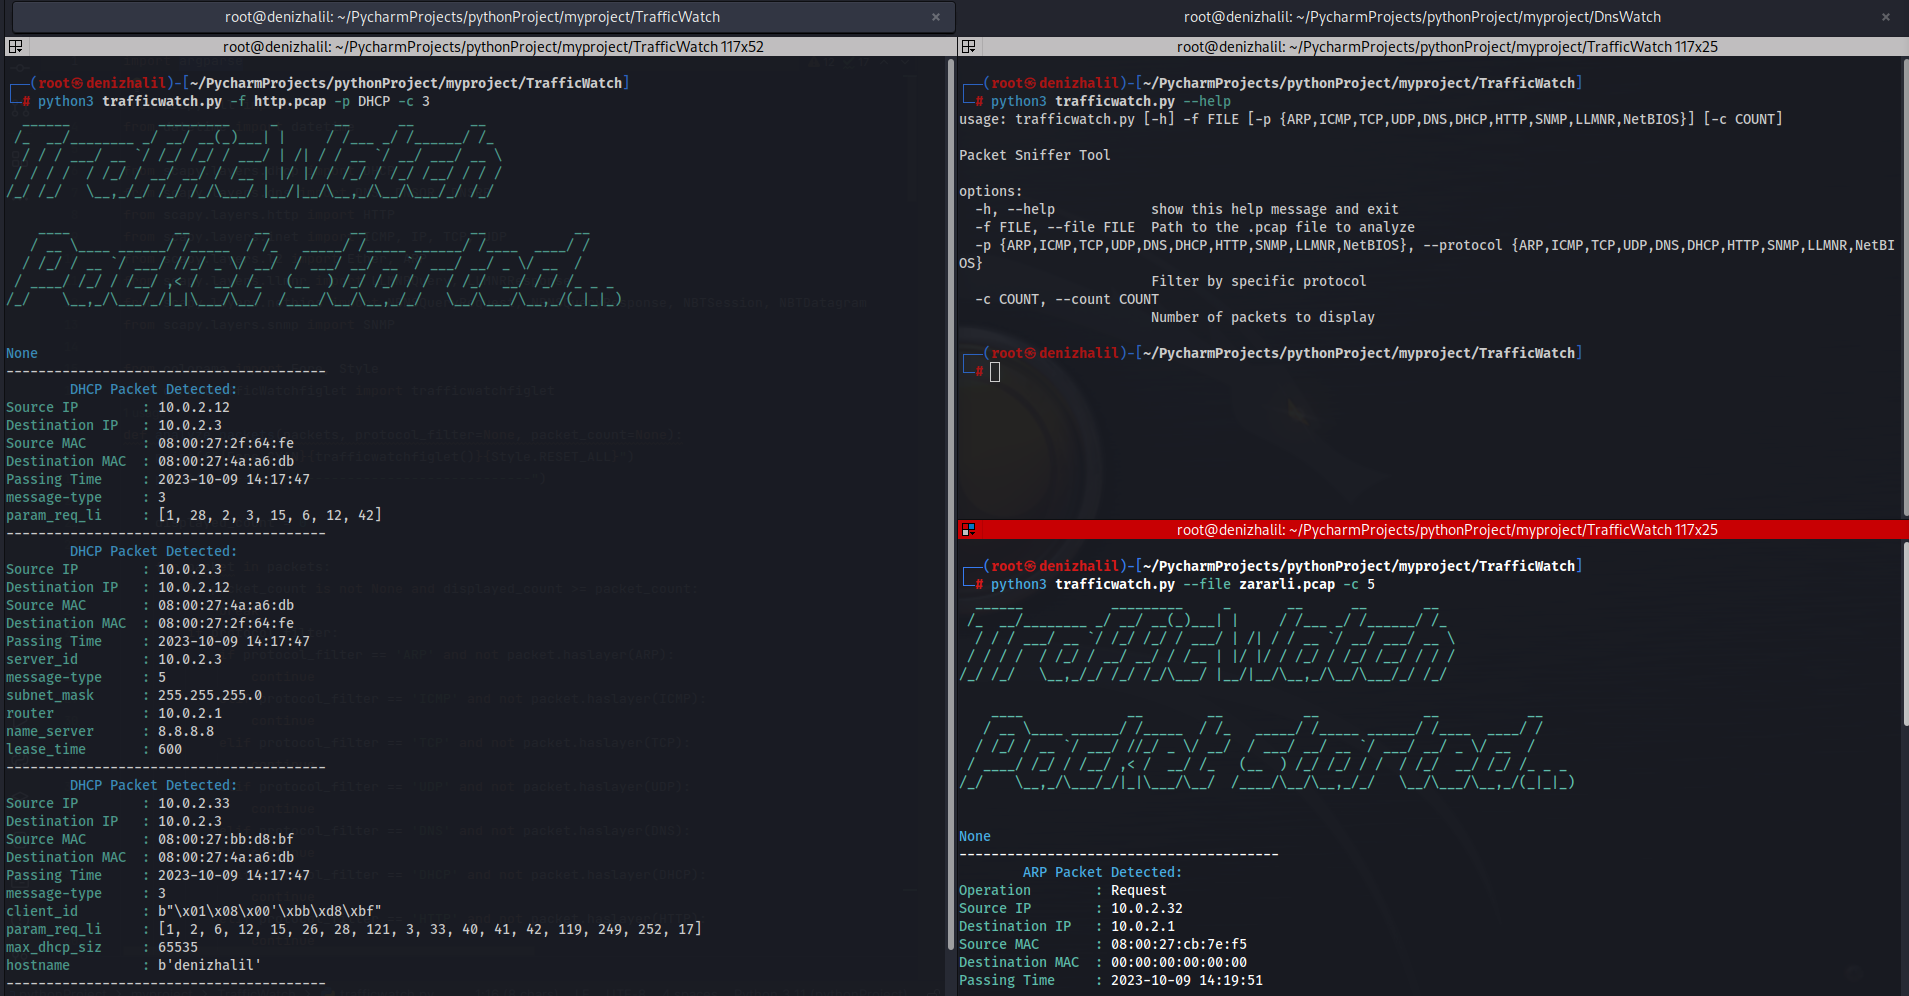 halildeniz/trafficwatch
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
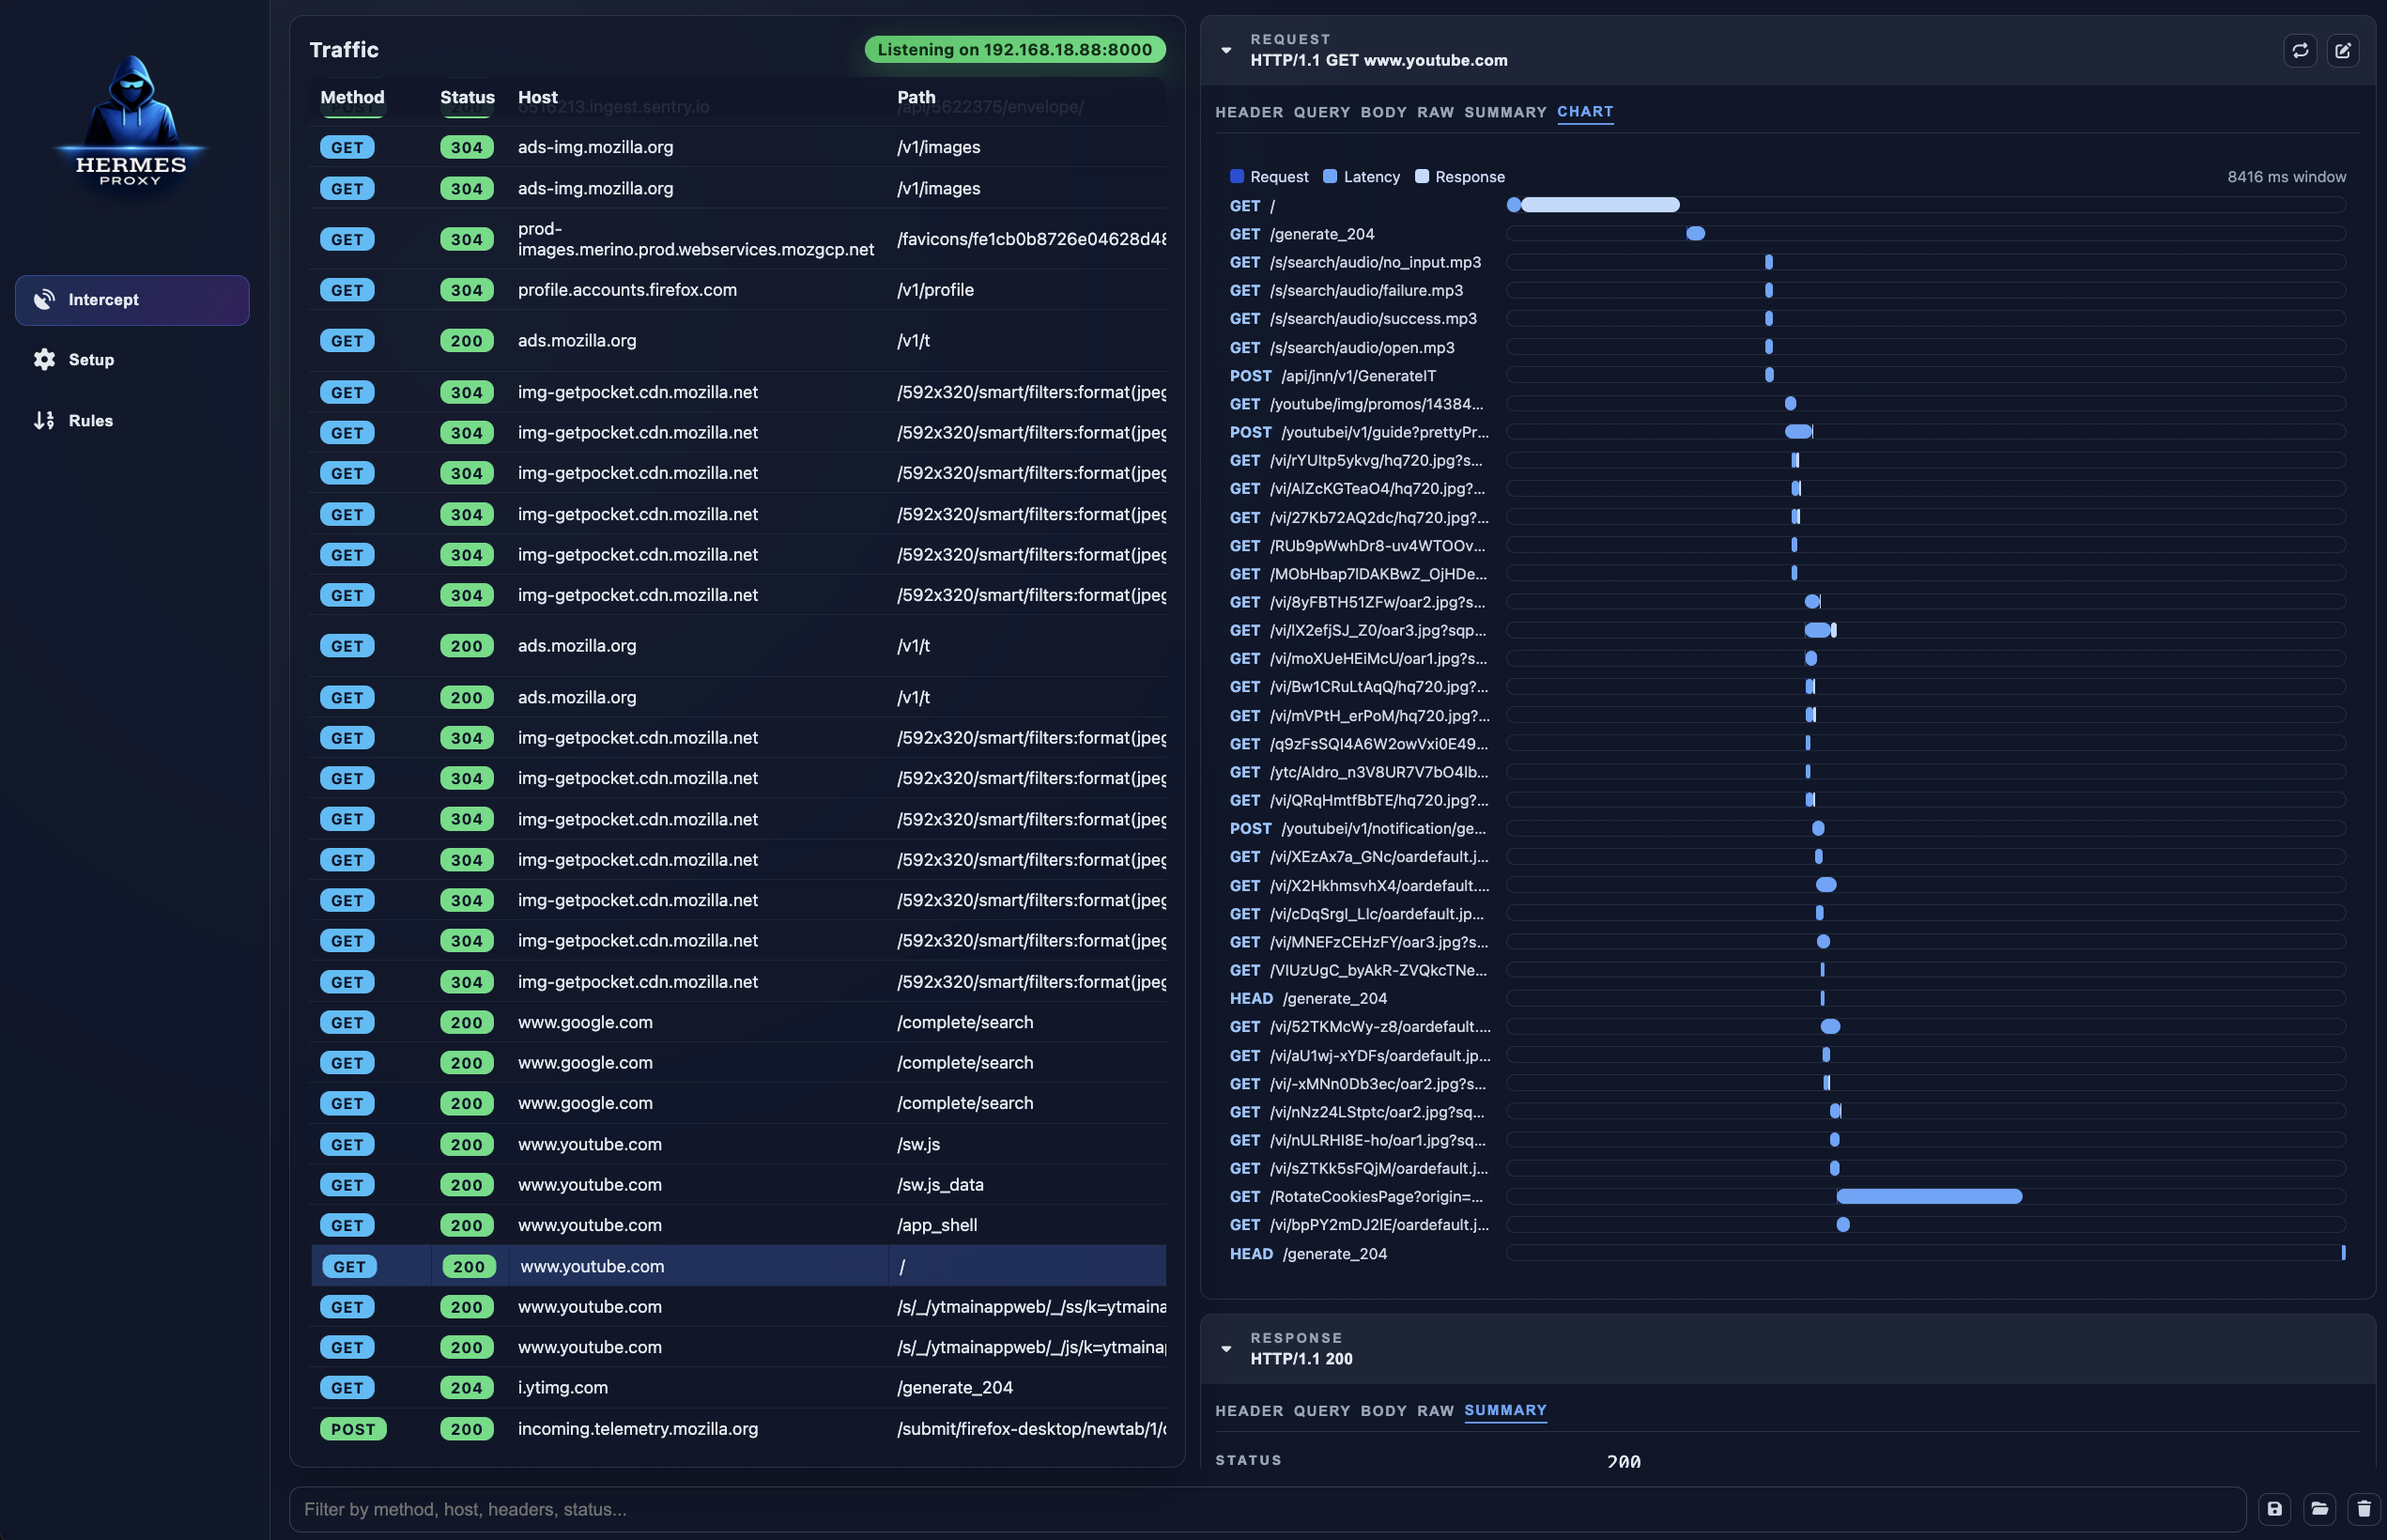 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
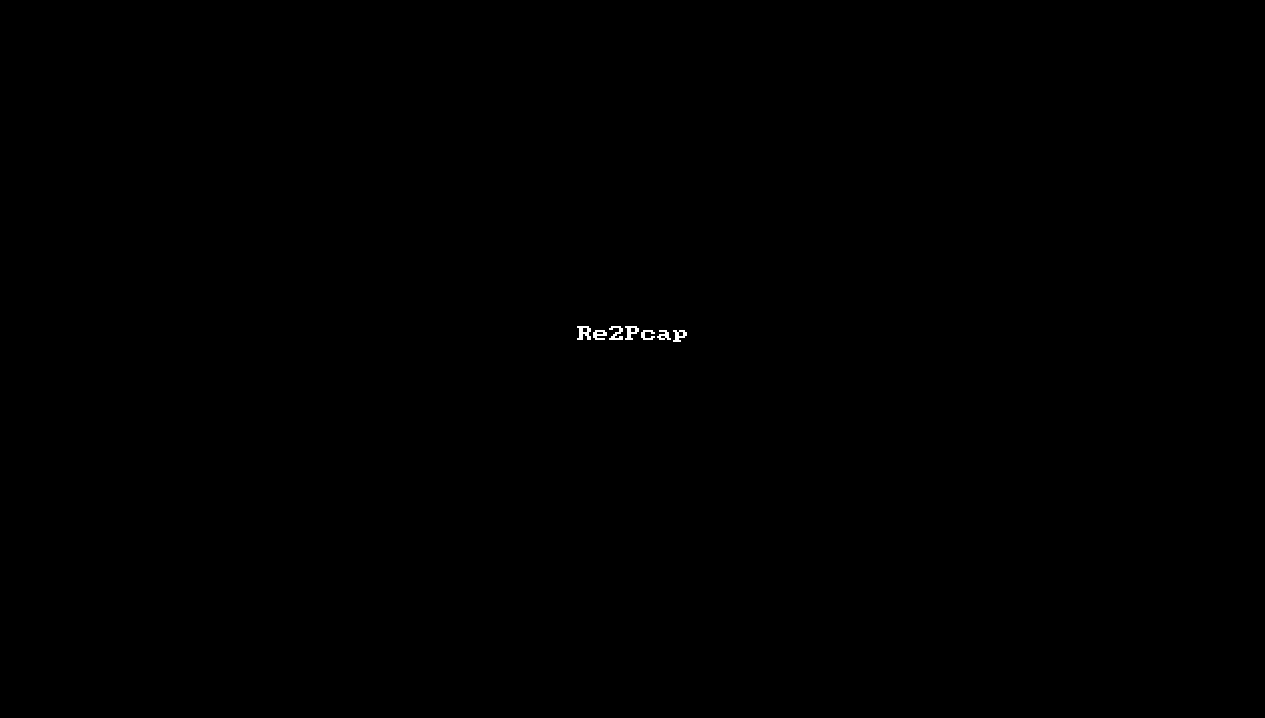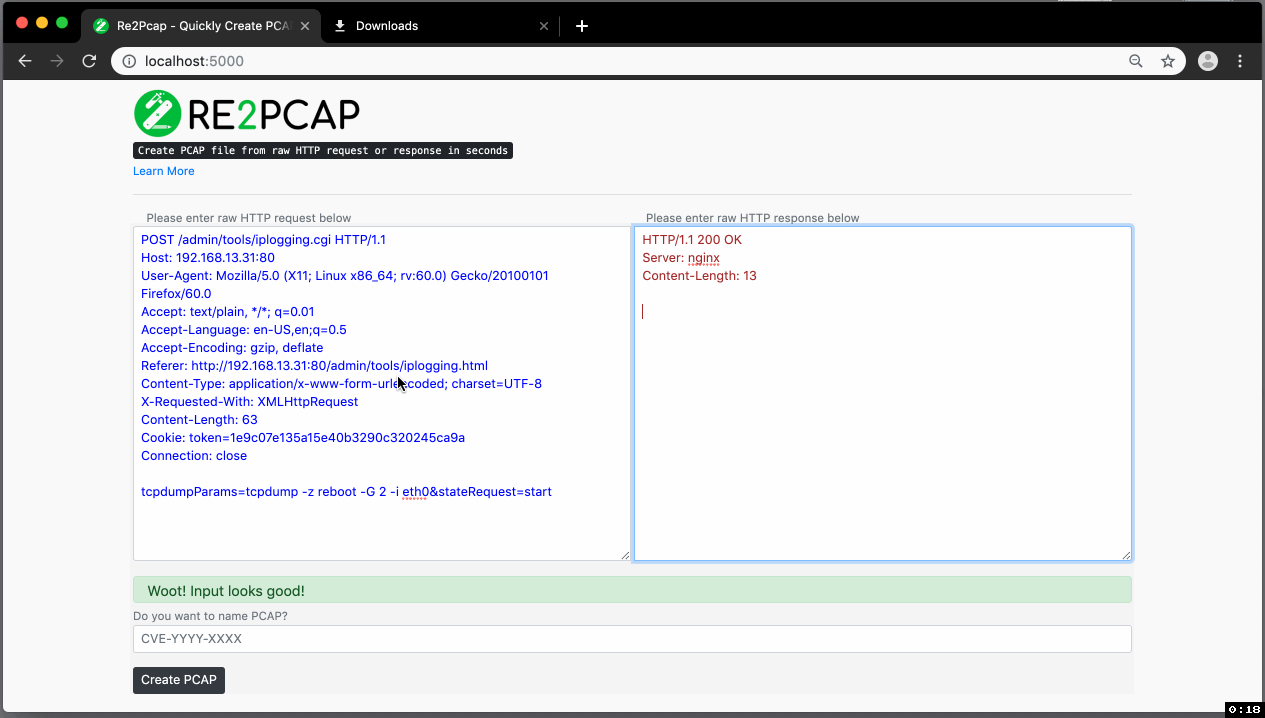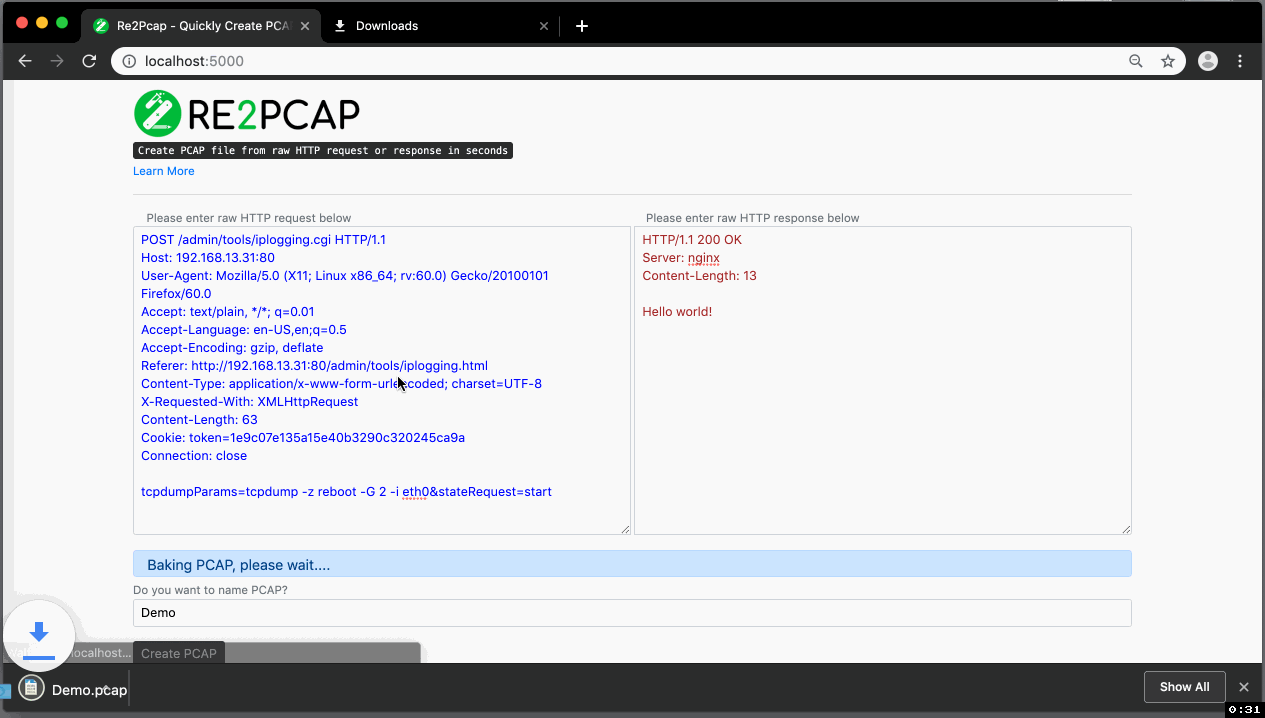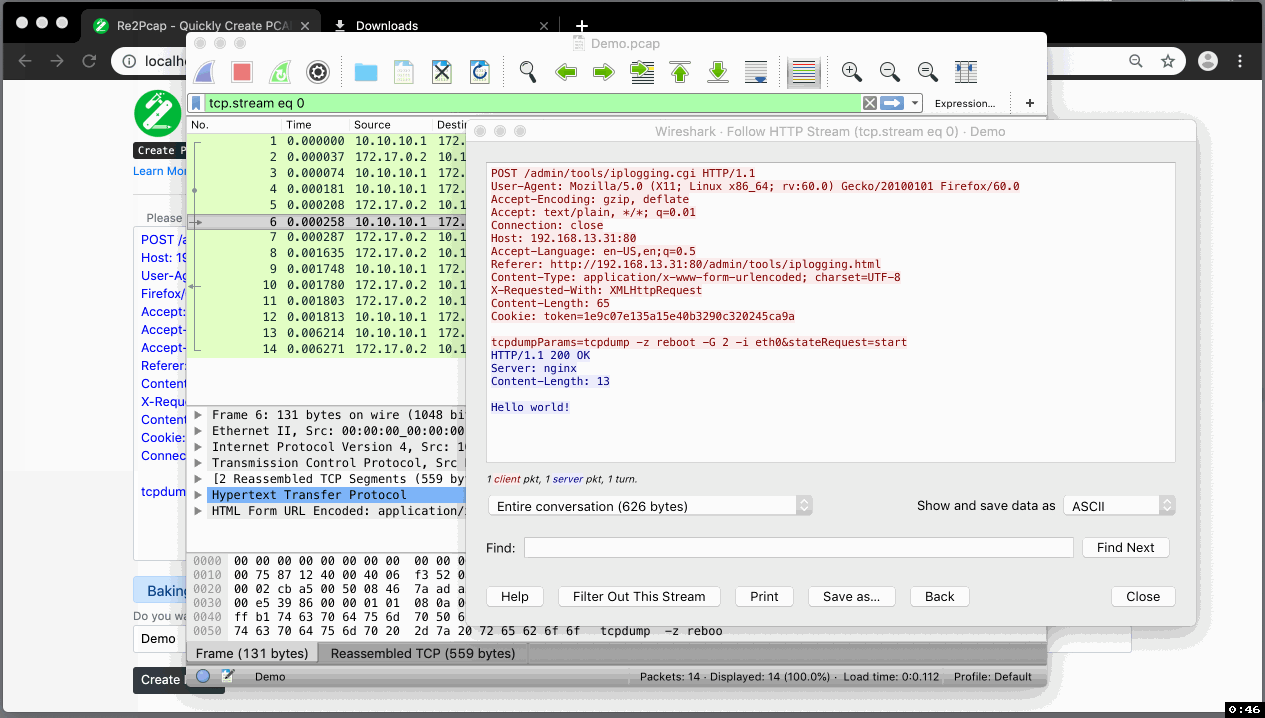 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
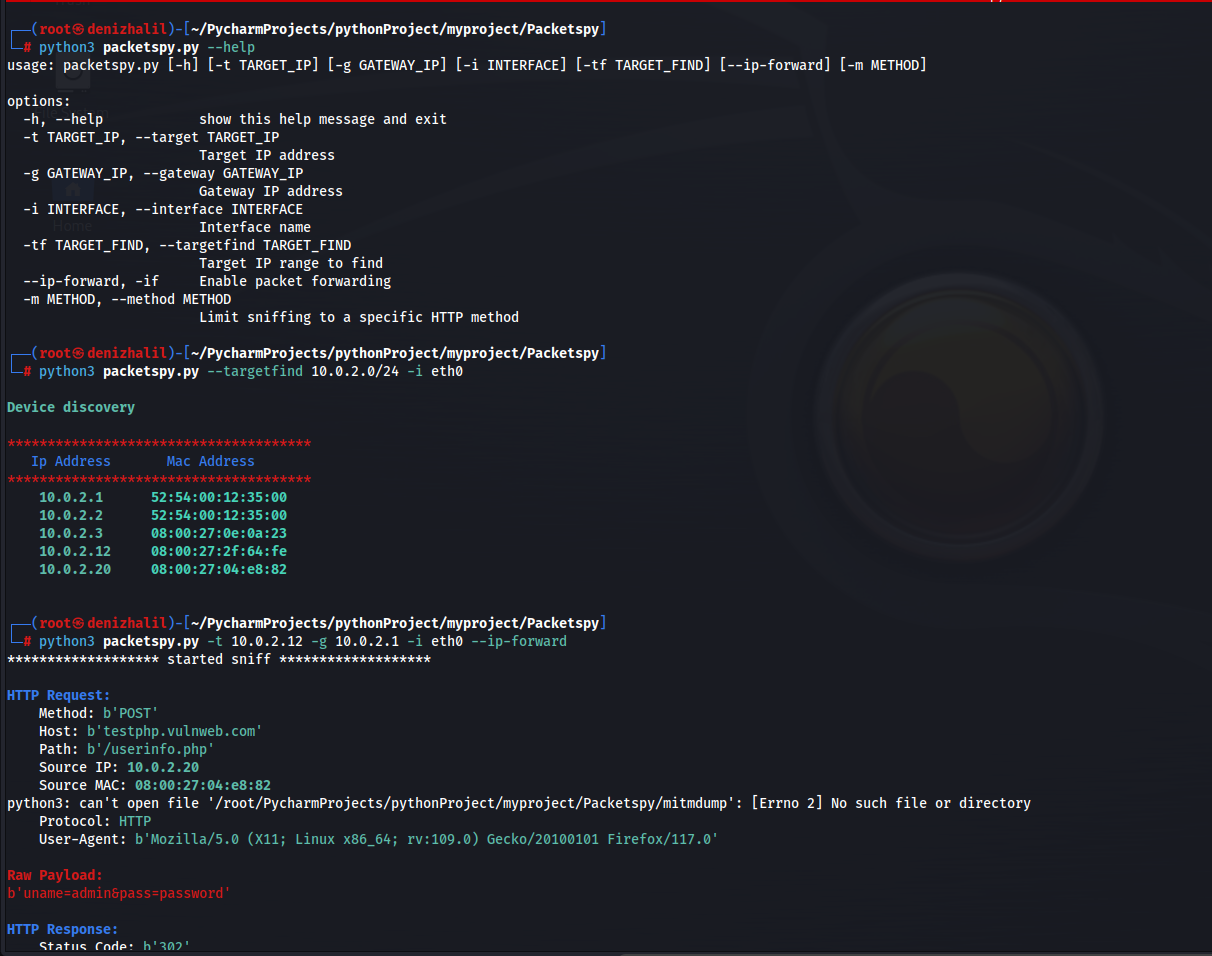 halildeniz/packetspy
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
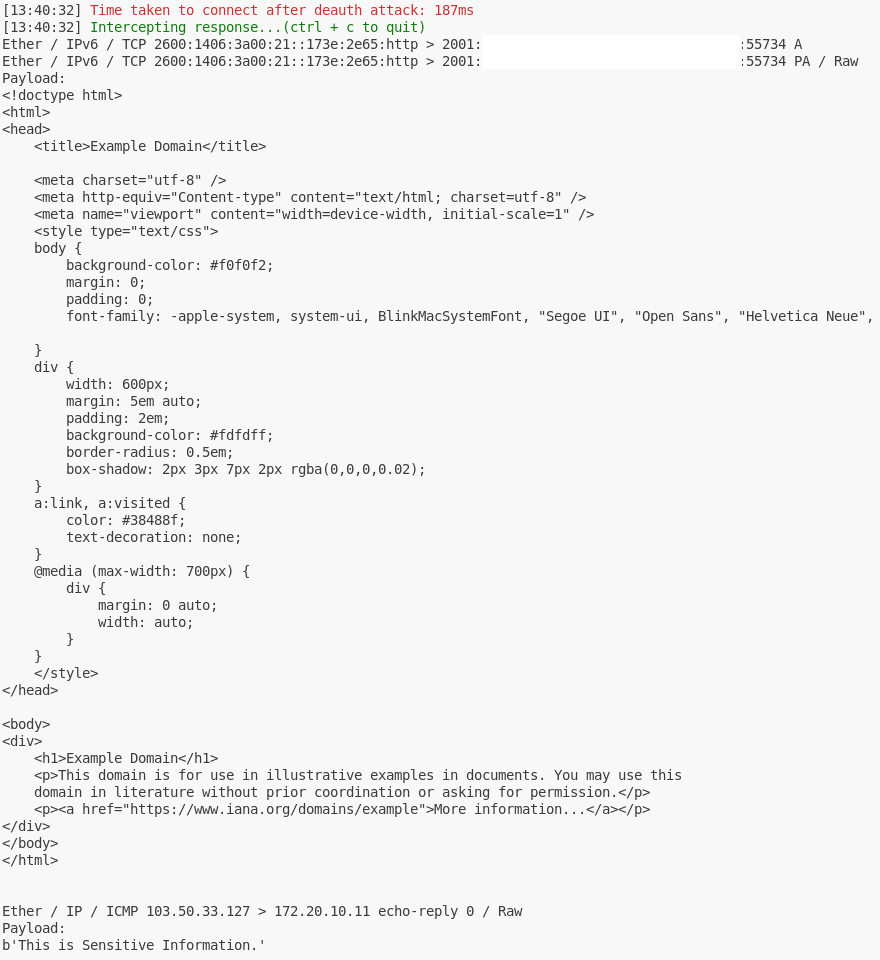 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 corelight/zeek-mercury-npf
Zeek plugin generating Mercury NPF fingerprints for TCP, TLS/DTLS, QUIC, HTTP, SSH, OpenVPN, and STUN to support network security monitoring.
 dannagle/packetsender
Network utility for sending / receiving TCP, UDP, SSL, HTTP
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 jlinebau/cve-2025-55315-scanner-monitor
Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors