

security-study-plan
 jassics/security-study-plan
Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
api-securitycloud-securitycryptography+8
5.1k
jassics/security-study-planComplete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 spidersuite/spidersuite
Advanced cross-platform web crawler for security professionals, enabling automated reconnaissance, information gathering, and OSINT data collection…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 wddadk/offensive-osint-tools
Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
 initstring/cloud_enum
Multi-cloud OSINT tool. Enumerate public resources in AWS, Azure, and Google Cloud.
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
 joda32/certcrunchy
Just a silly recon tool that uses data from SSL Certificates to find potential host names
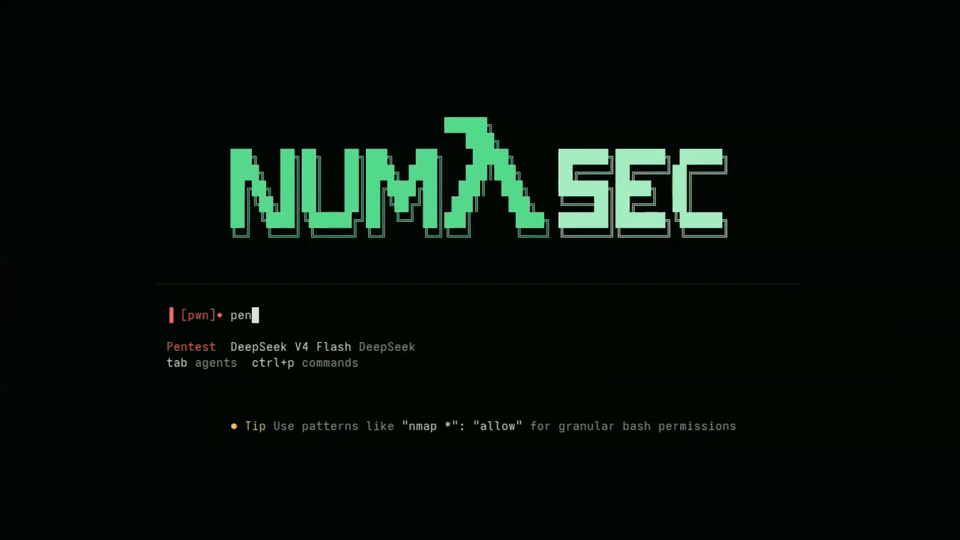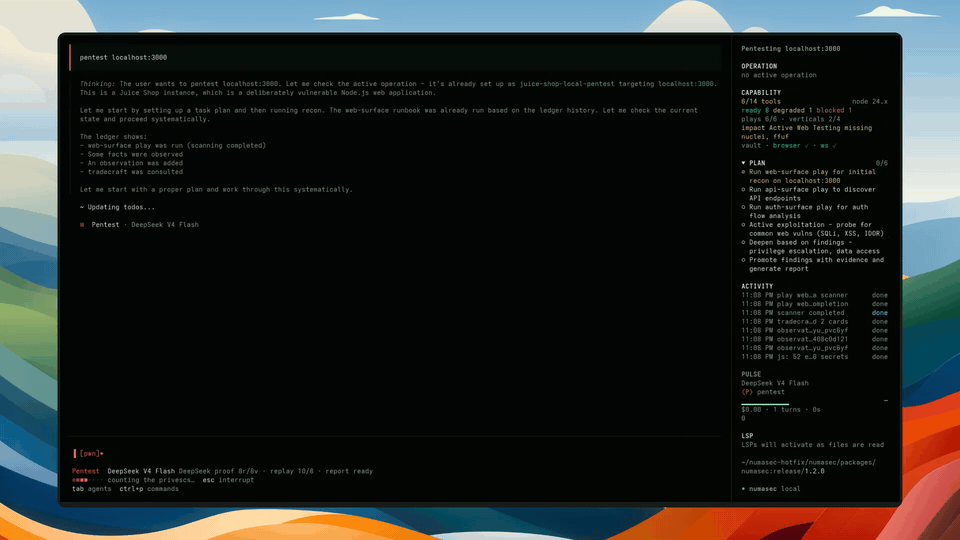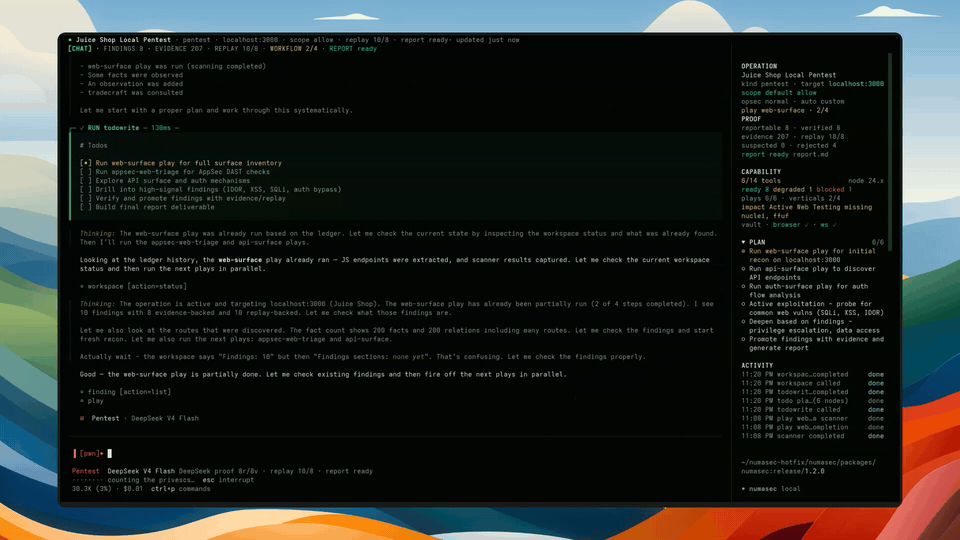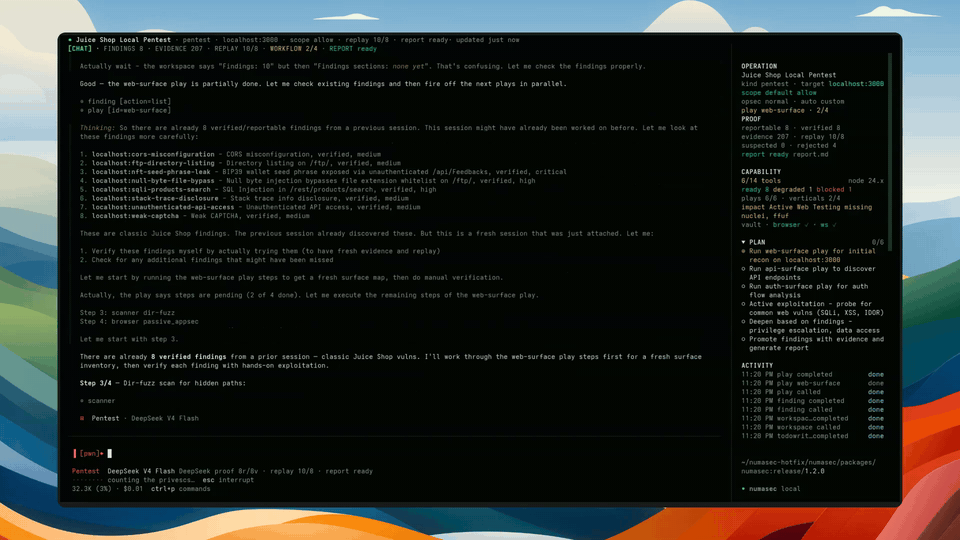 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 wyllowsec/magnohost-vulnerabilities-pentest
pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…
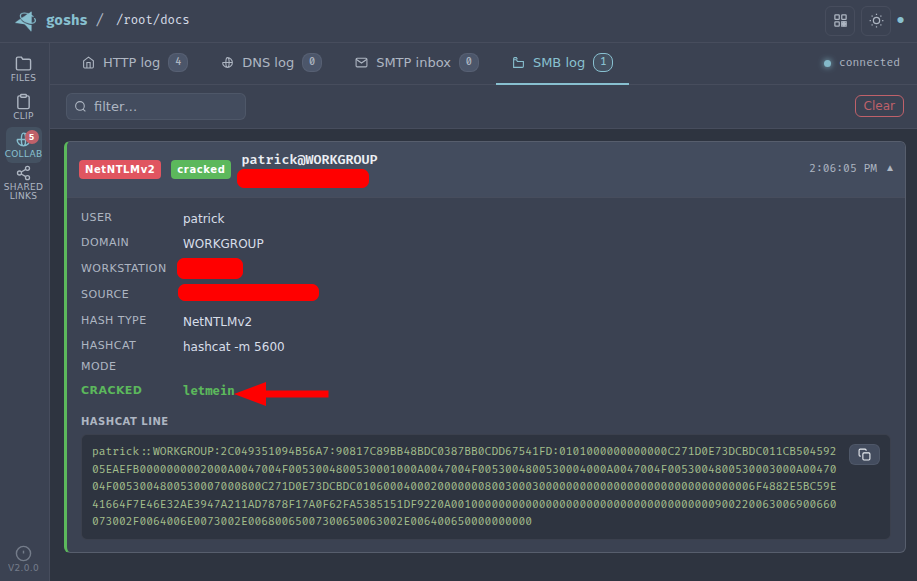 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing