
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CertCrunchy — Just a silly recon tool that uses data from SSL Certificates to find potential host names | Kitploit

Tools/GitHubGitHub/joda32/certcrunchy
OSINT (Open Source Intelligence)ReconnaissanceDNS & Subdomain EnumerationInformation Gathering
GitHubjoda32/certcrunchy

CertCrunchy

Just a silly recon tool that uses data from SSL Certificates to find potential host names

View Repository
2913435 months agoReviewed by Kitploit
Share
 _____           _   _____                       _
/  __ \         | | /  __ \                     | |
| /  \/ ___ _ __| |_| /  \/_ __ _   _ _ __   ___| |__  _   _
| |    / _ \ '__| __| |   | '__| | | | '_ \ / __| '_ \| | | |
| \__/\  __/ |  | |_| \__/\ |  | |_| | | | | (__| | | | |_| |
 \____/\___|_|   \__|\____/_|   \__,_|_| |_|\___|_| |_|\__, |
                                                        __/ |
                                                       |___/

Just a silly recon tool that uses data from SSL Certificates to find potential hostnames

What the?

It just a silly python script that either retrieves SSL Certificate based data from online sources, currently https://crt.sh/, https://certdb.com/, https://sslmate.com/certspotter/ and https://censys.io or given a IP range it will attempt to extract host information from SSL Certificates. If you want to use Censys.io you need to register for a API key.
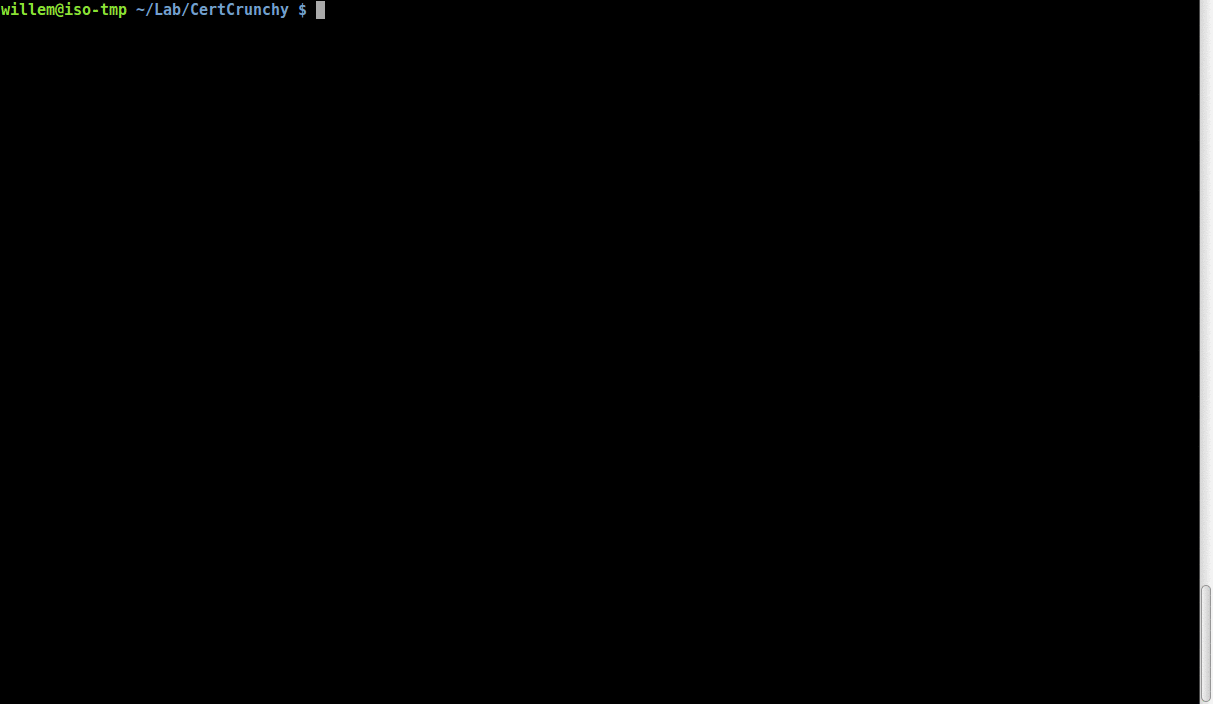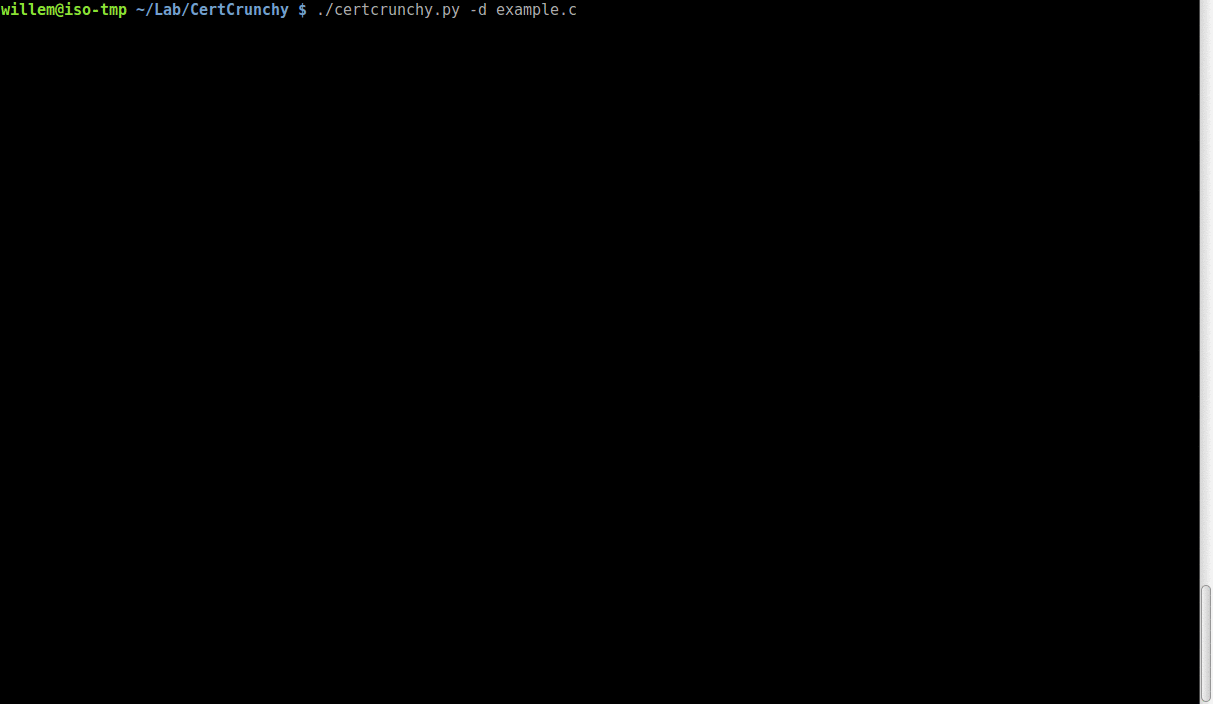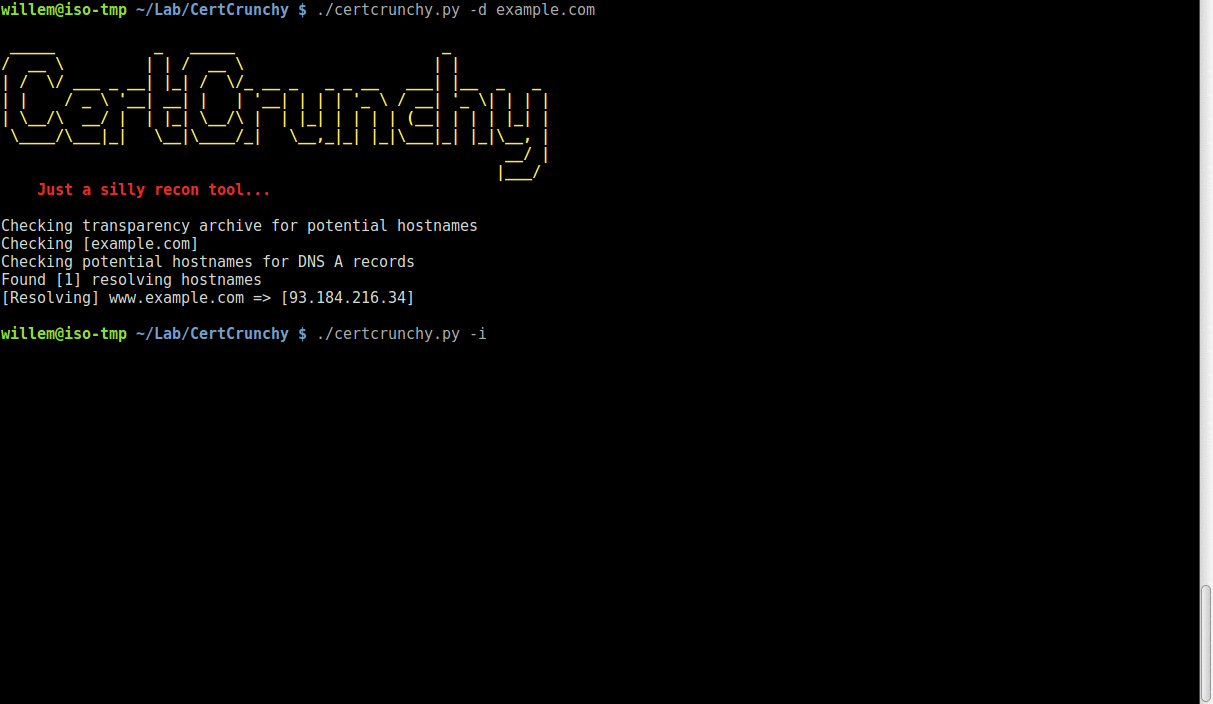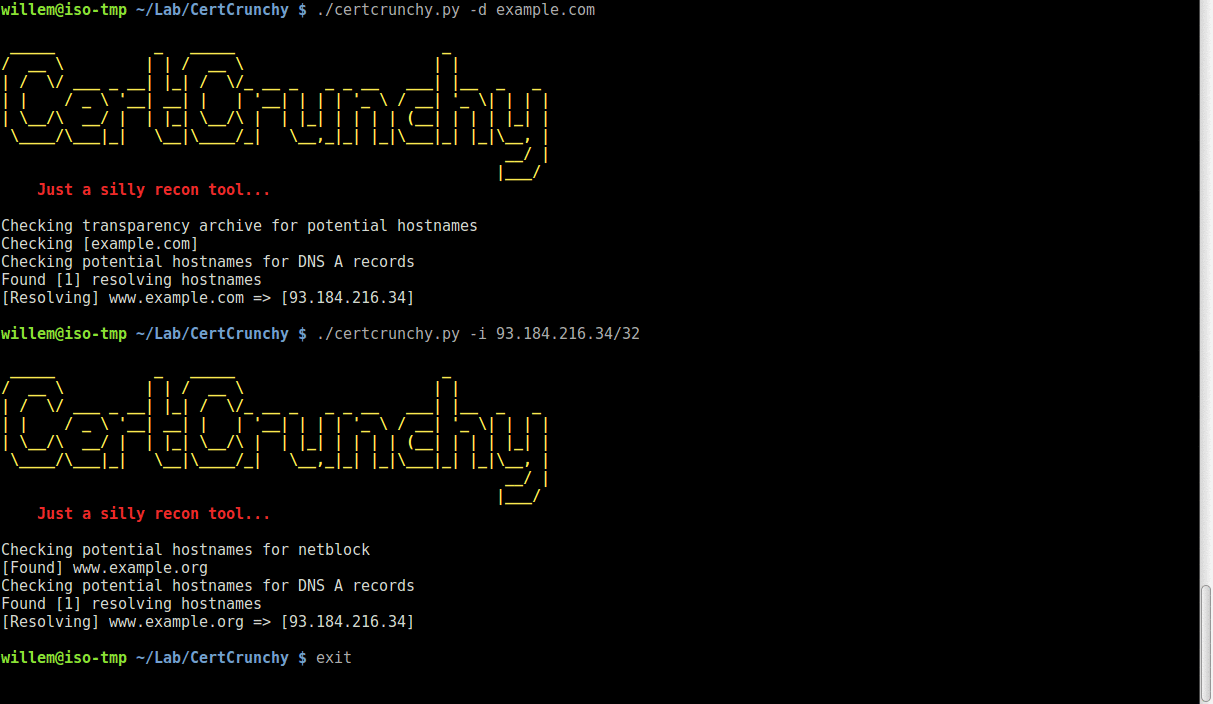
Demo

gif

How to install

git clone https://github.com/joda32/CertCrunchy.git
cd CertCrunchy
sudo pip3 install -r requirements.txt

How to use it?

Very simply -d to get hostnames for specific domain

-D to get hostnames for a list of domains (just stuff it in a line delimited text file)

-i to retrieve and parse certificates from hosts in a netblock / ip range (e.g. 192.168.0.0/24)

-T the thread count, makes stuff faster, but don't over do it

-O to set the timeout on HTTP api requests in seconds (default is 3 seconds)

-o Output file name

-f Output format csv or json, csv is the default

for the rest, I'm still working on those :)

API keys and configs

All API keys are stored in the api_keys.py file, below is a list of supported APIs requiring API keys.

  1. Censys.oi https://censys.io

  2. VirusTotal https://www.virustotal.com/en/documentation/public-api/

  3. PassiveTotal https://community.riskiq.com/registration

Todo:

  1. Better documentation
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    317
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    294

Explore all tools

Browse our collection of tools

View all tools →





