Awesome-Asset-Discovery

Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…

Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…

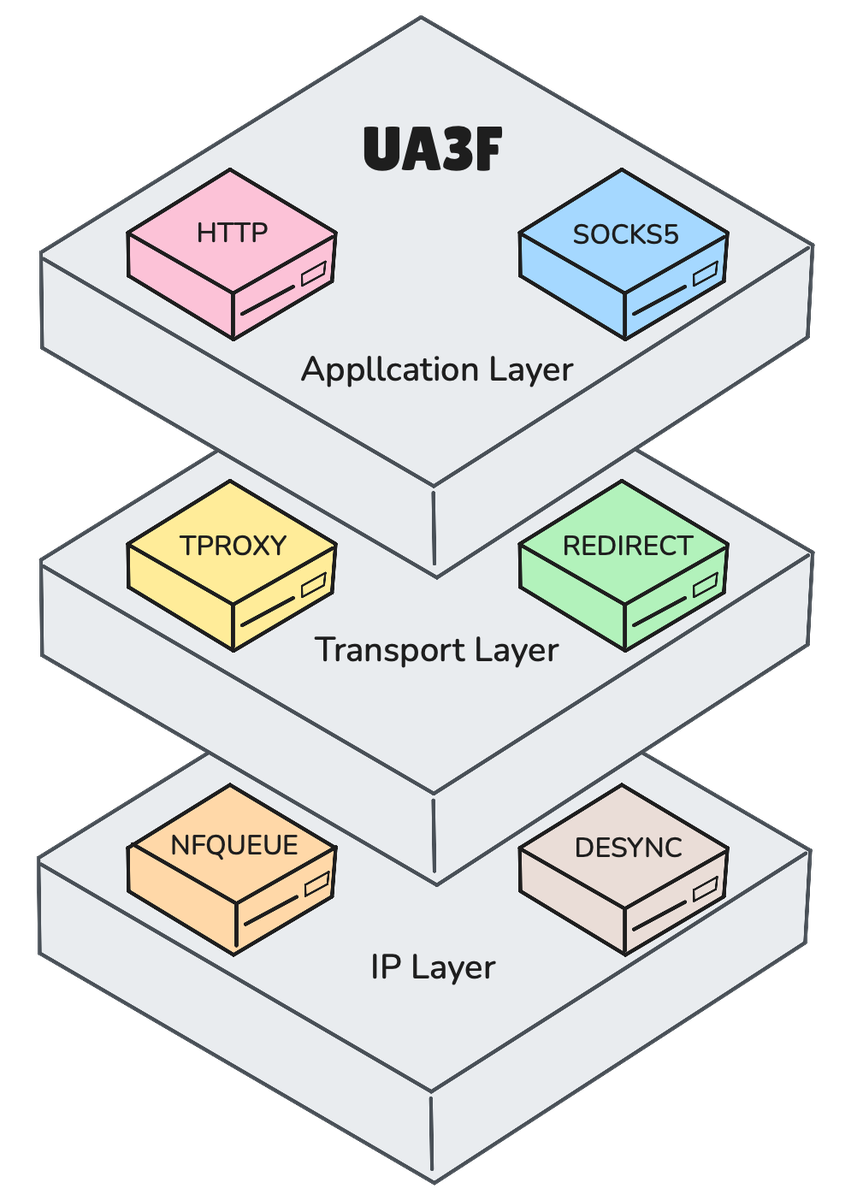
Transparent HTTP(S) rewriting proxy supporting HTTP, SOCKS5, TPROXY, REDIRECT and NFQUEUE modes with HTTPS MitM, rule-based header/body rewriting and…

Automated attack surface inventory for 800+ public bug bounty programs, running scheduled subdomain enumeration, permutation, DNS and web server…

Proof-of-concept and recon framework for CVE-2026-86426, a LibreNMS API authentication bypass via type confusion, extracting SNMP credentials and…

Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…

A Router WiFi key recovery/cracking tool with a twist.

About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers

Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…

Open source network measurement tool that runs standardized tests to detect internet censorship, traffic manipulation, and network interference…

Go measurement engine and CLI for detecting Internet censorship and network interference, running OONI network tests and reporting results to the…

AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.

Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…

MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…

Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.

Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.

Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…

Proof-of-concept and analysis for CVE-2023-5612, a GitLab CE/EE webhook SSRF. Includes curl PoC steps and custom NSE scripts to verify and…

Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…