

ARTEX
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
ai-securityinformation-gatheringnetwork-mapping+9
855
baarai/artexLLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 redhuntlabs/awesome-asset-discovery
Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…
 trickest/inventory
Automated attack surface inventory for 800+ public bug bounty programs, running scheduled subdomain enumeration, permutation, DNS and web server…
 guila95/cve-2026-86426
Proof-of-concept and recon framework for CVE-2026-86426, a LibreNMS API authentication bypass via type confusion, extracting SNMP credentials and…
 dedsecinside/torbot
Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…
 k0r0pt/project-tauro
A Router WiFi key recovery/cracking tool with a twist.
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
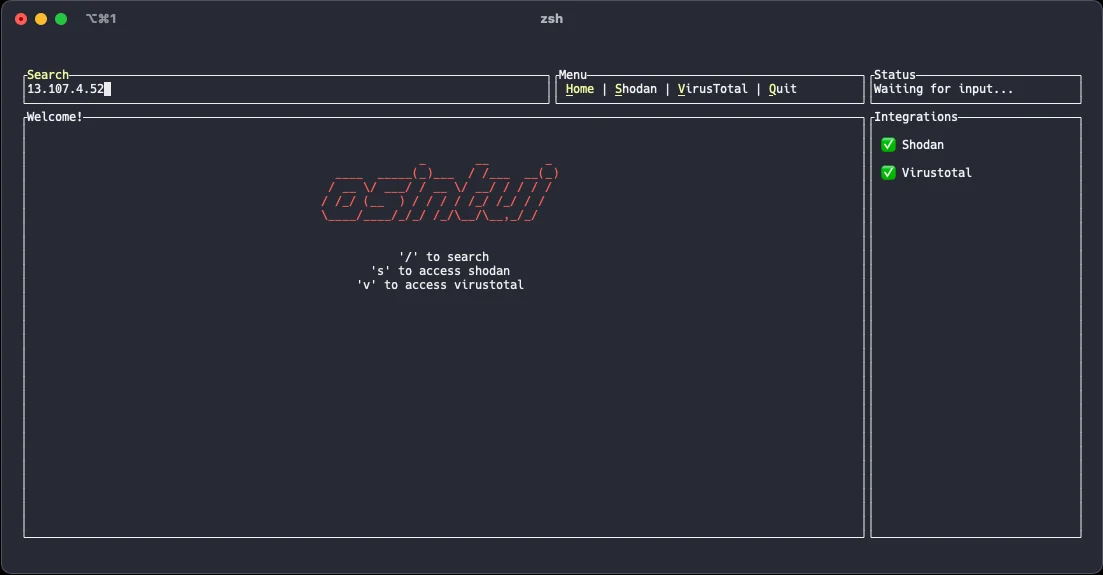 gmh5225/osintui
Open Source Intelligence Terminal User Interface
 ooni/probe
Open source network measurement tool that runs standardized tests to detect internet censorship, traffic manipulation, and network interference…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 gmh5225/ollama-hunter
Scans Shodan for publicly exposed Ollama and llama.cpp servers, enumerating hosts, locations, and available models for security research.
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 affolter-engineering/snmpen
SNMP enumeration tool that queries SNMPv1/v2c hosts to extract system information, TCP connections, and write access for penetration testing and…
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…