

Archived
frida-fuzzer
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
api-security-testingbinary-analysisdynamic-analysis-sandboxing+3
andreafioraldi/frida-fuzzerThis experimetal fuzzer is meant to be used for API in-memory fuzzing.
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 zhuyansen/awesome-ai-reverse-engineering
Open-source AI reverse engineering tools for coding agents: Ghidra MCP, IDA Pro MCP, jadx, Frida, skills and REA. 122 repos, each read and…
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
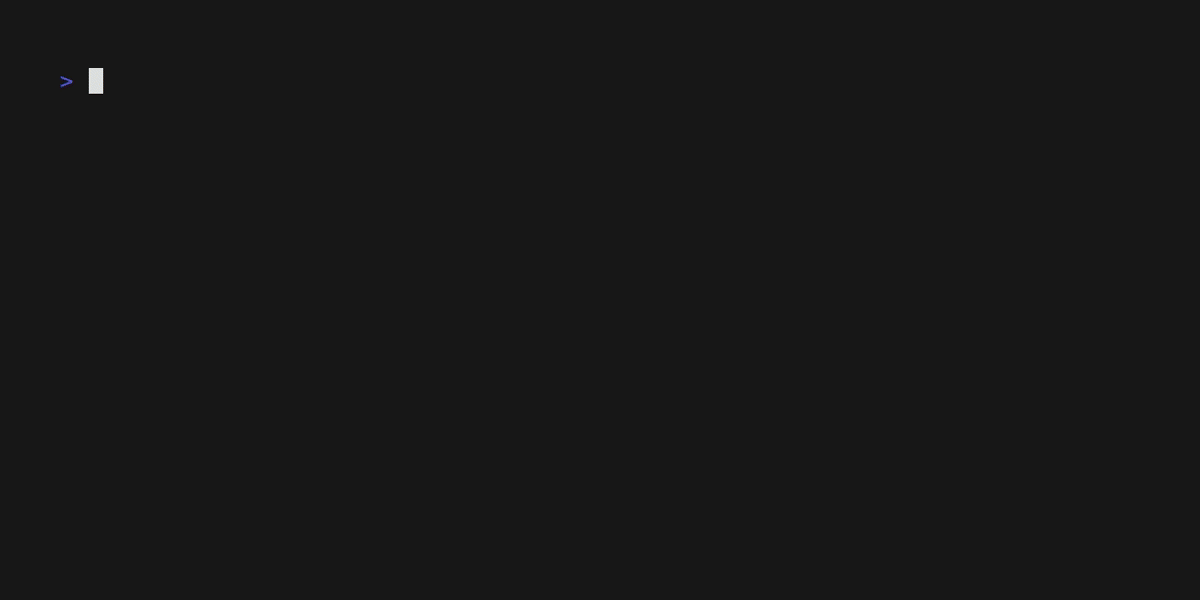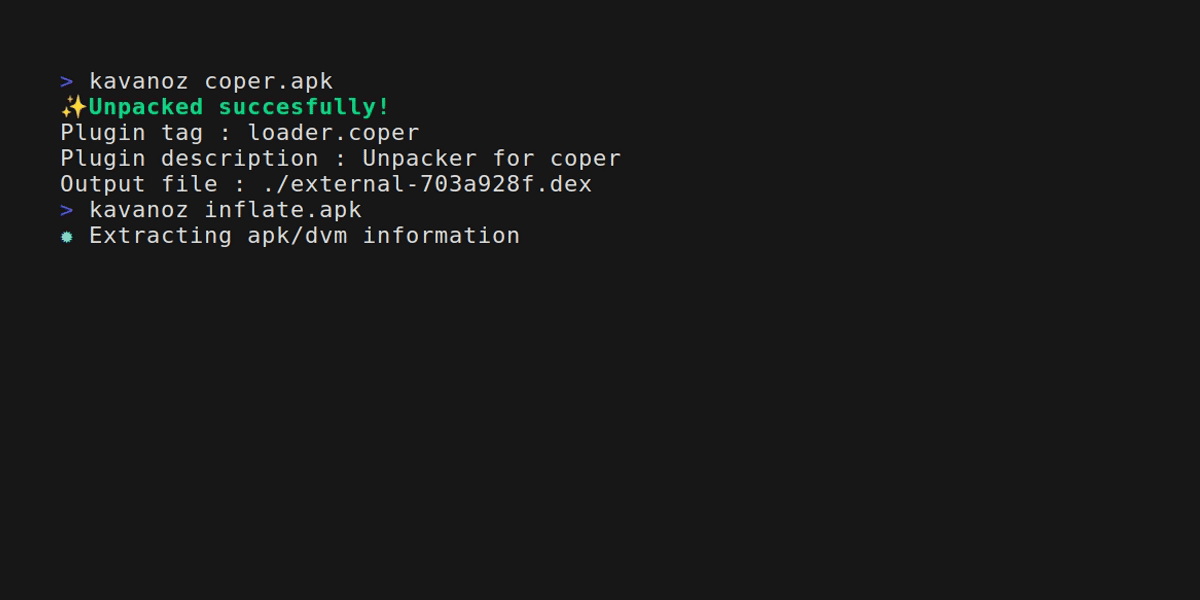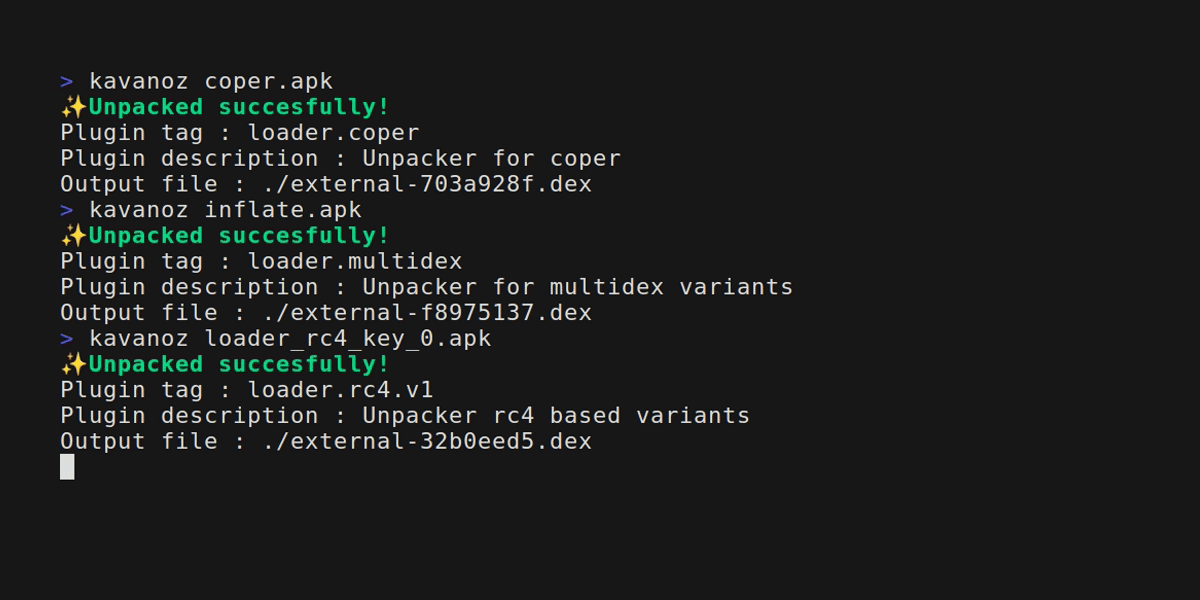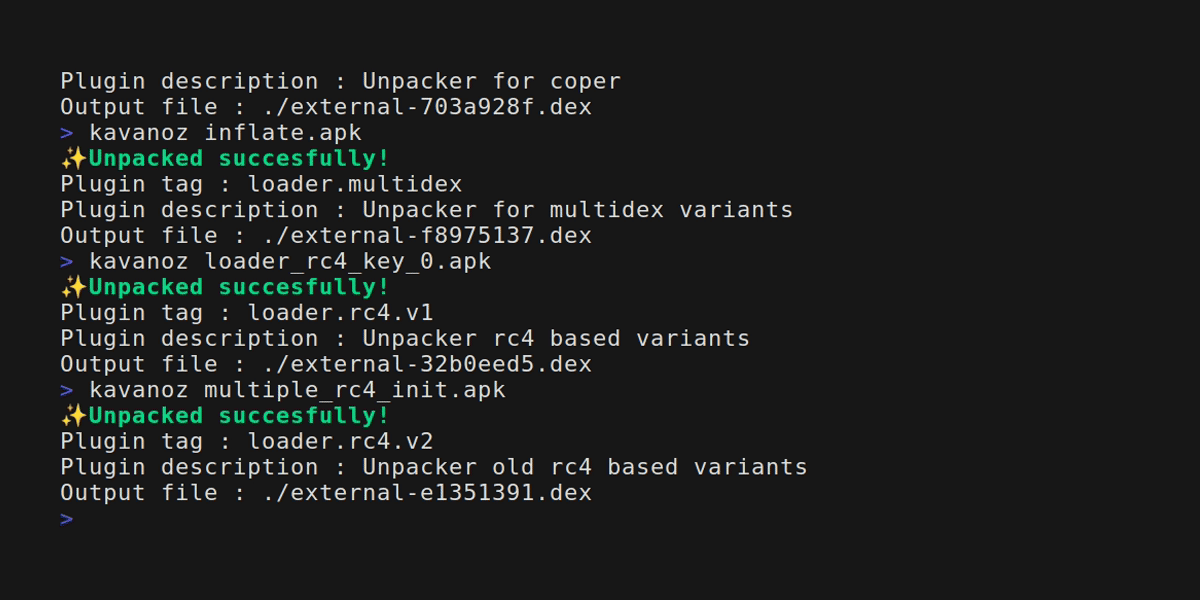 eybisi/kavanoz
Statically unpacking common android banker malware.
 morluto/awesome-reverse-engineering
Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.
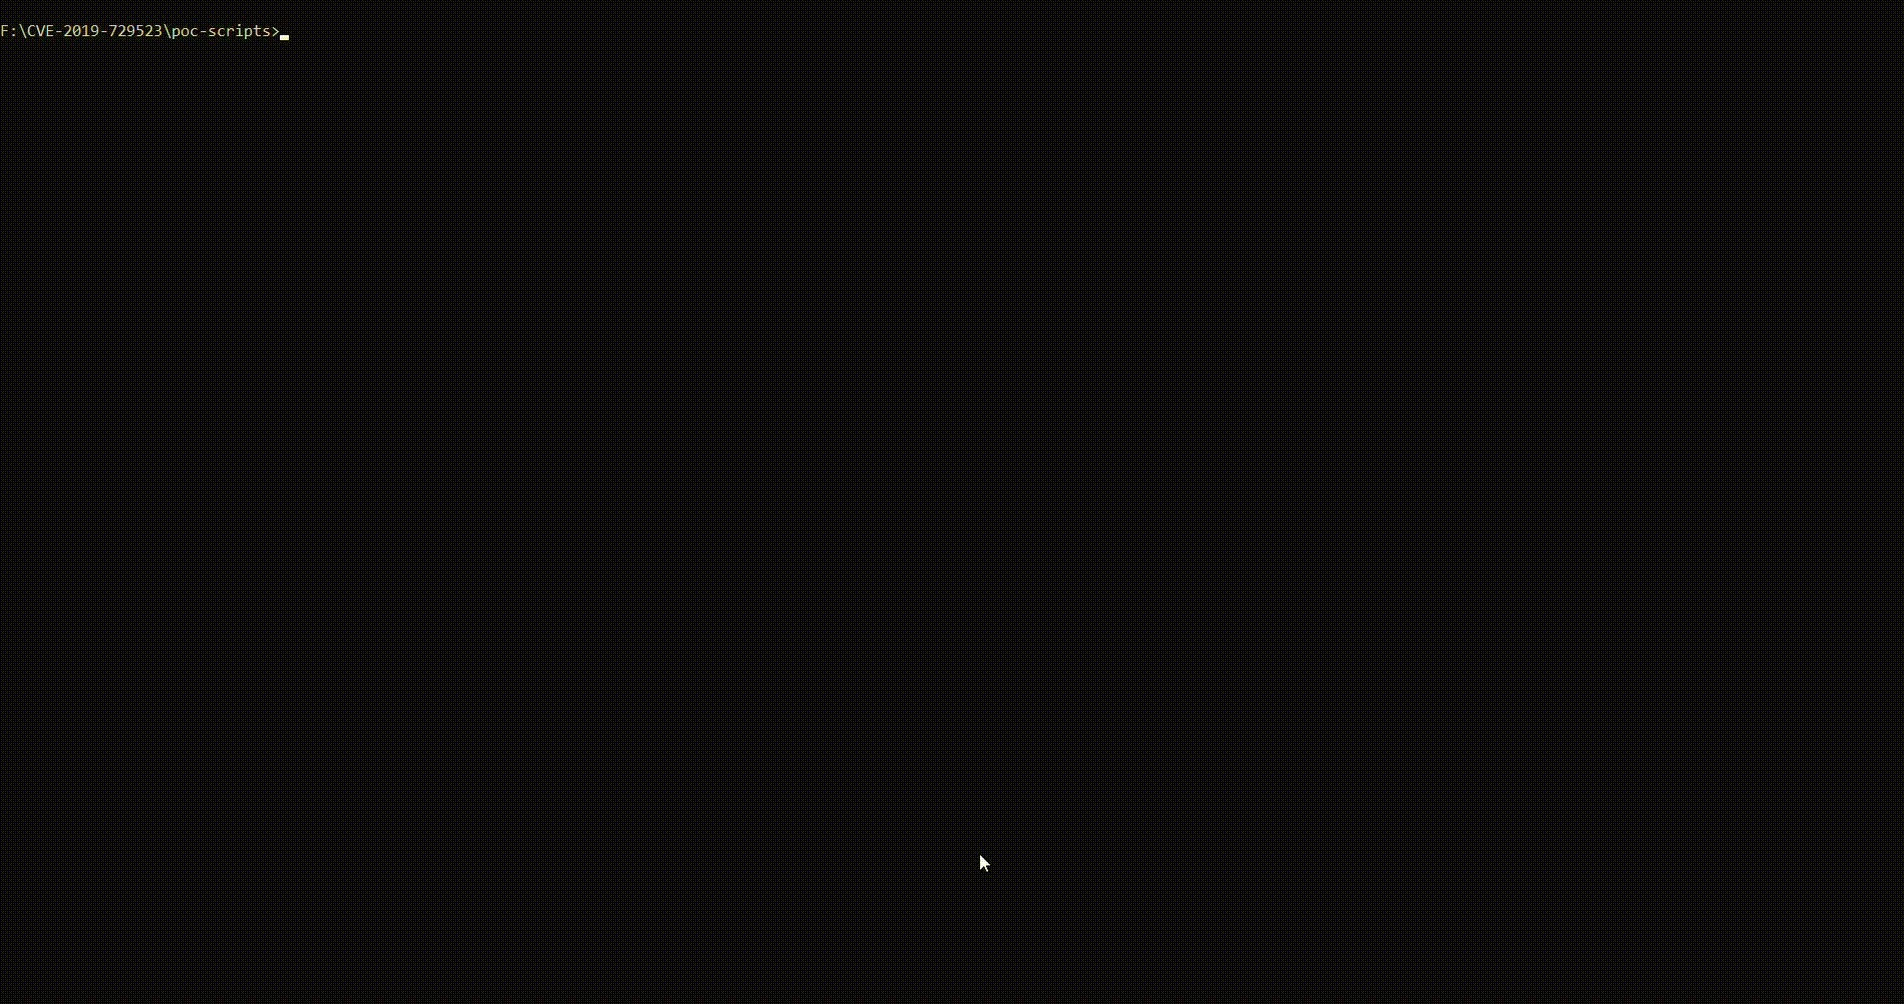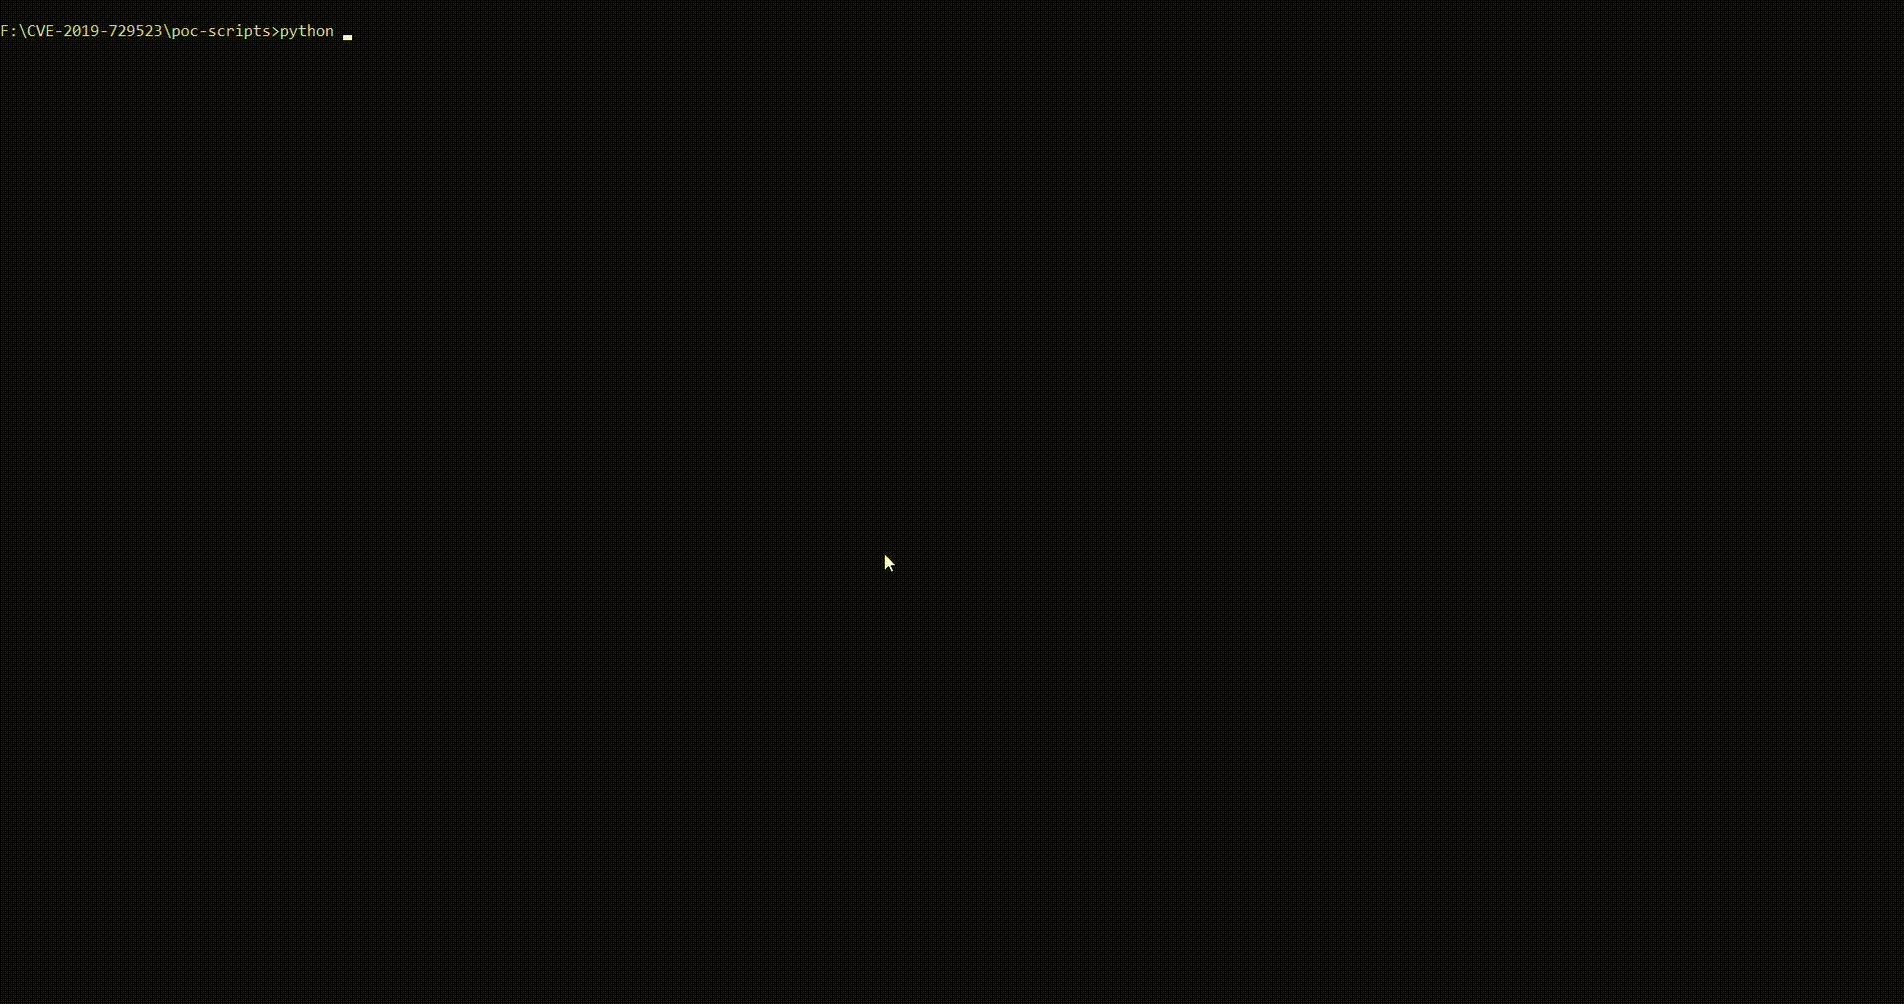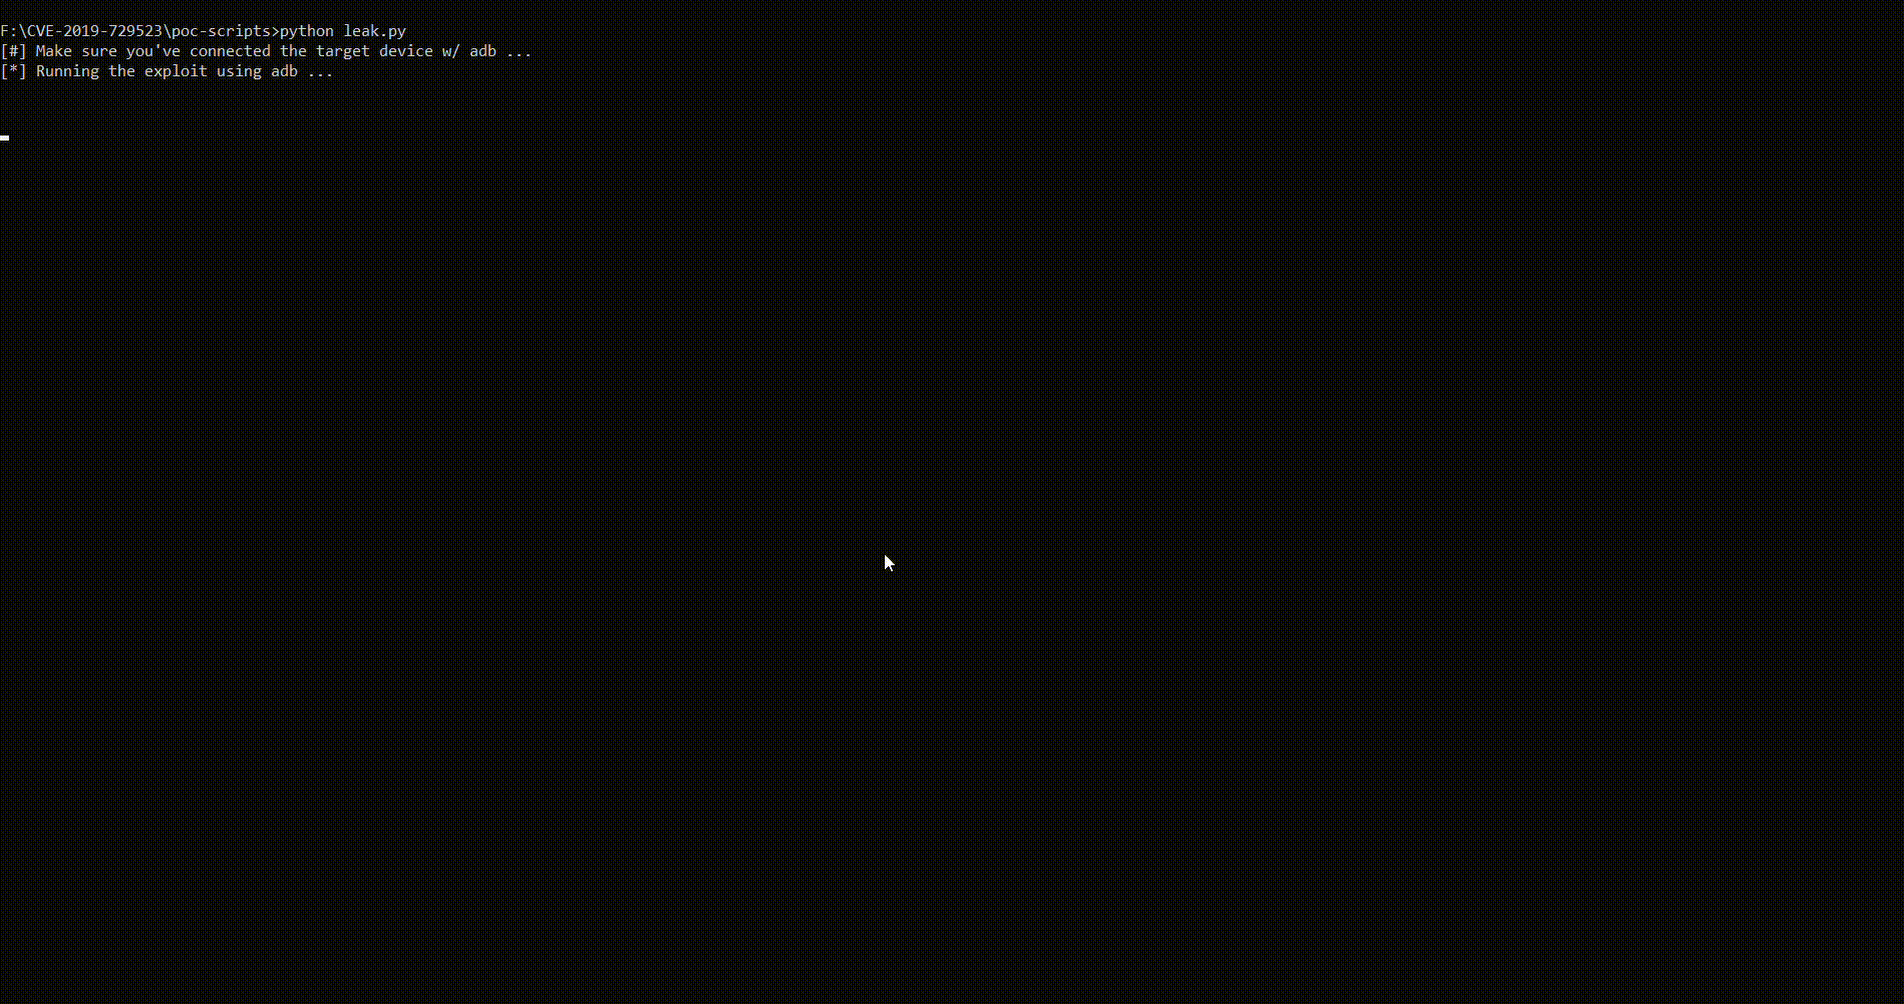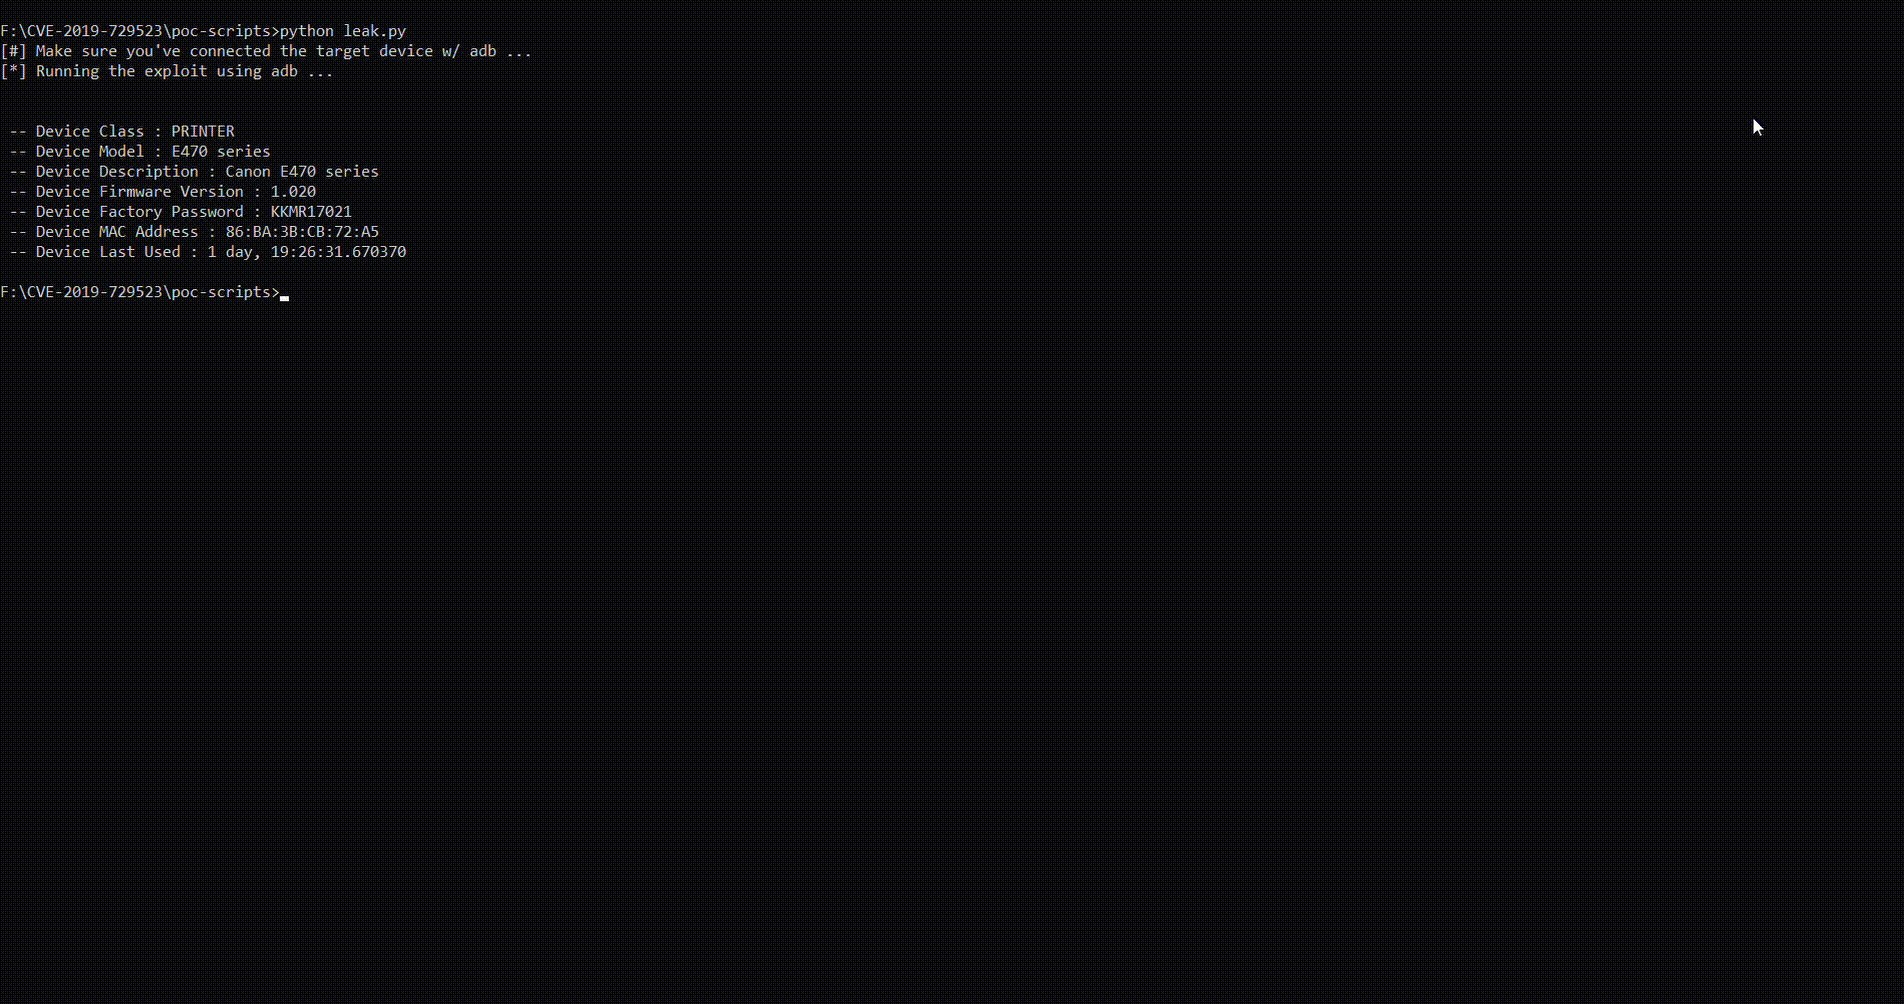 0x48piraj/cve-2019-14339
POC for CVE-2019-14339 Canon PRINT 2.5.5
 davidbuchanan314/cowroot
Universal Android root tool based on CVE-2016-5195. Watch this space.
 asdfugil/haxx
Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.
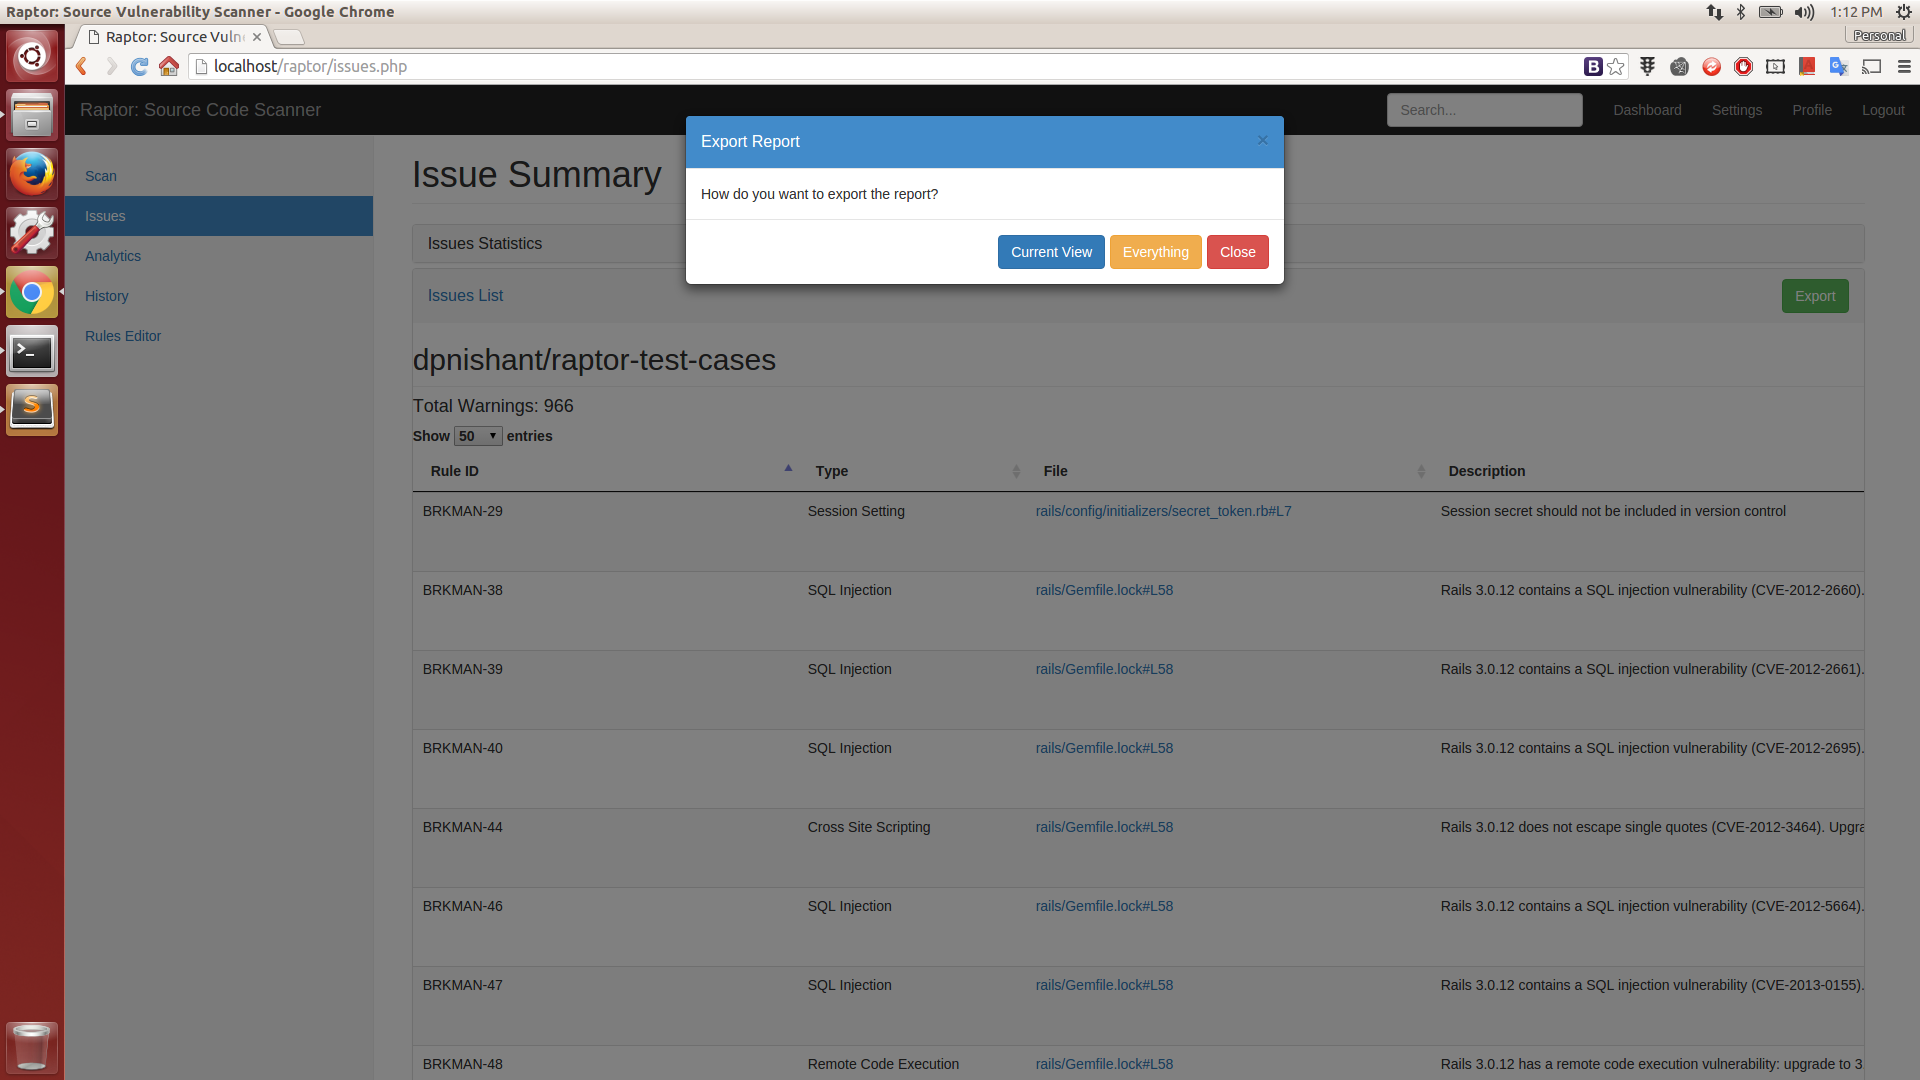 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
 lanrat/tethr
Android Tethering Provisioning Check Bypass (CVE-2017-0554)
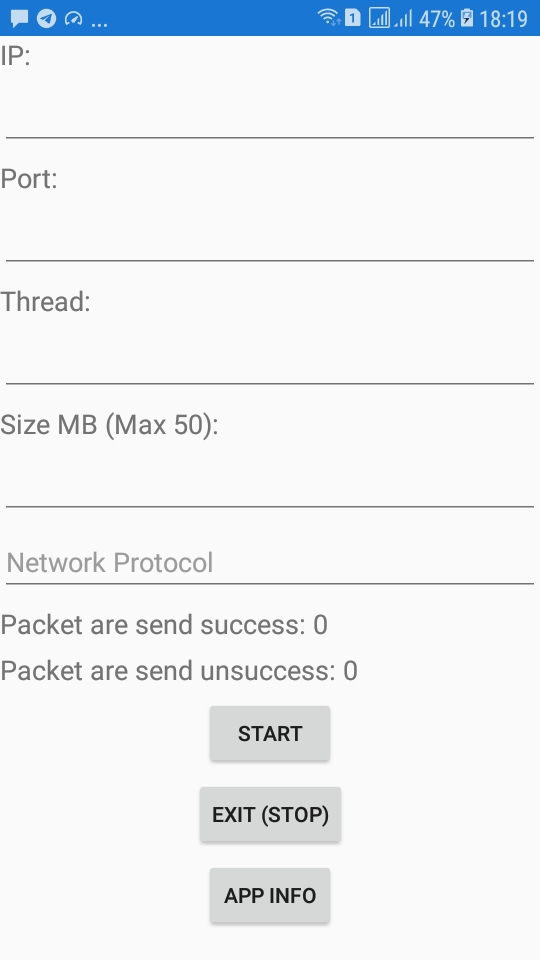 blueskychan-dev/ddospacket
Use own Phone to DoS Attack without Termux! (Android 5.1+)
 suffixing/apkscope
Android reverse engineering for humans and AI agents: typed Java in milliseconds, xrefs, API and secret recon, APK diff, re-signing, a native viewer…
 lauriewired/jadxecute
JADX-gui scripting plugin for dynamic decompiler manipulation
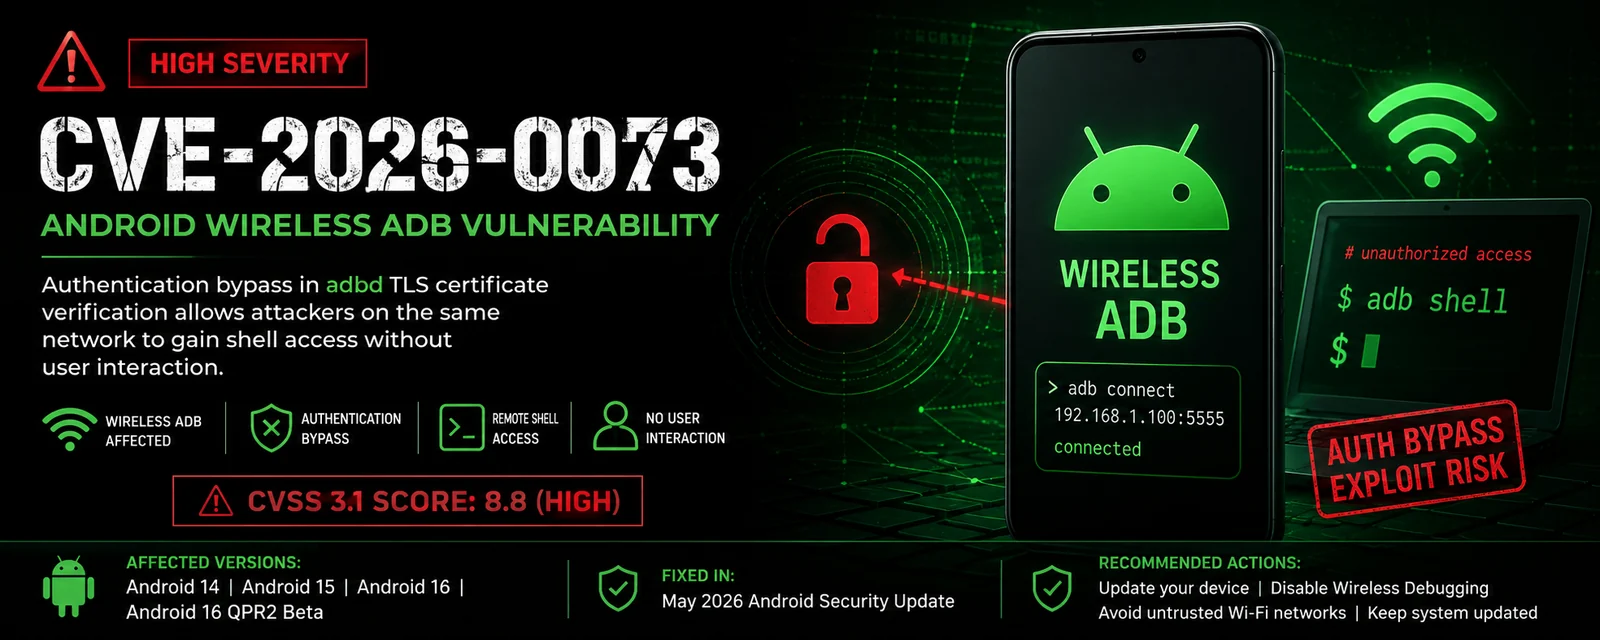 0xredash/cve-2026-0073
C++ proof-of-concept checker and exploit for CVE-2026-0073, an Android Wireless ADB authentication bypass allowing unauthenticated remote shell…
 ylh440104/infinitycore-android-cve-2026-89754
ARM64 Android port of the official PoC for CVE-2026-89754, a kernel MM subsystem race condition enabling local privilege escalation on 7.0/7.2…