

deep-C
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
ai-securityandroid-securitydynamic-analysis-sandboxing+8
91
kishorbal/deep-cAndroid deeplink misconfiguration detector and exploitation tool
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 abbbe/sslcaudit
Automated SSL/TLS client security testing tool for detecting MITM vulnerabilities in thick clients, mobile apps, and network appliances.
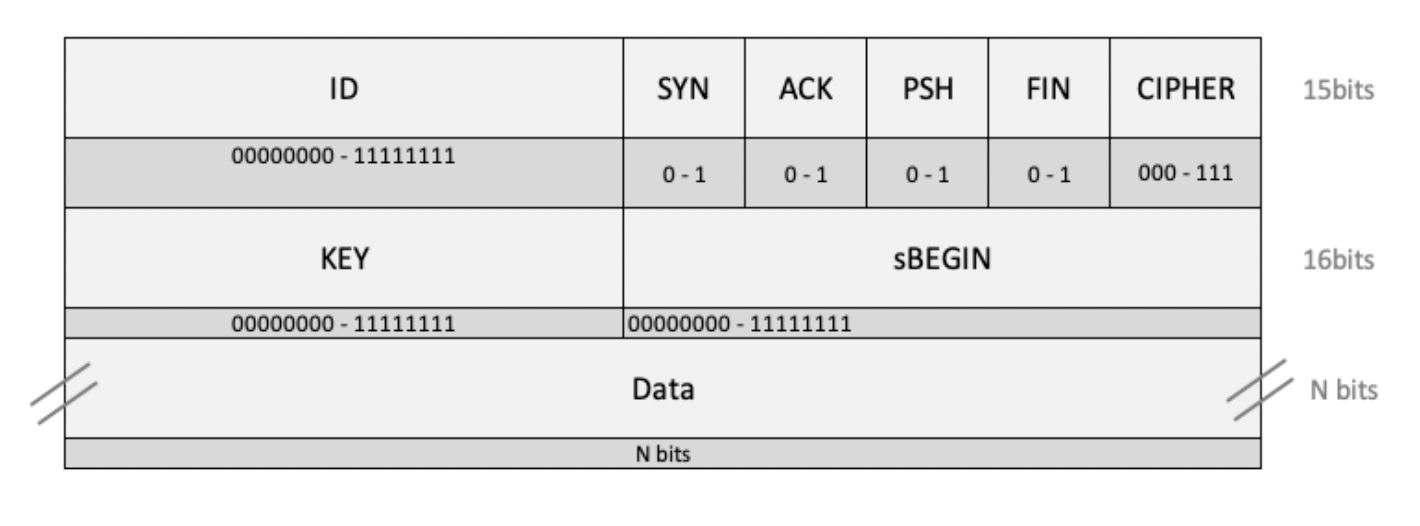 telefonica/sdk-sms-stack
Framework providing TCP/IP-like characteristics over GSM SMS with AES+CTR encryption, enabling secure, ordered message streams for device-to-device…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 darkz2012/qualcomm-vulnerability-scanner
A tool to scan Android devices for the recently exploited Qualcomm flaw CVE-2026-21385, providing a simple and efficient way to identify vulnerable…
 sc1341/instagramosint
An Instagram Open Source Intelligence Tool - Archive
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 google/nogotofail
An on-path blackbox network traffic security testing tool
 certcc/keyfinder
A tool for finding and analyzing private (and public) key files, including support for Android APK files.
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
 isecpartners/introspy-ios
Security profiling for blackbox iOS
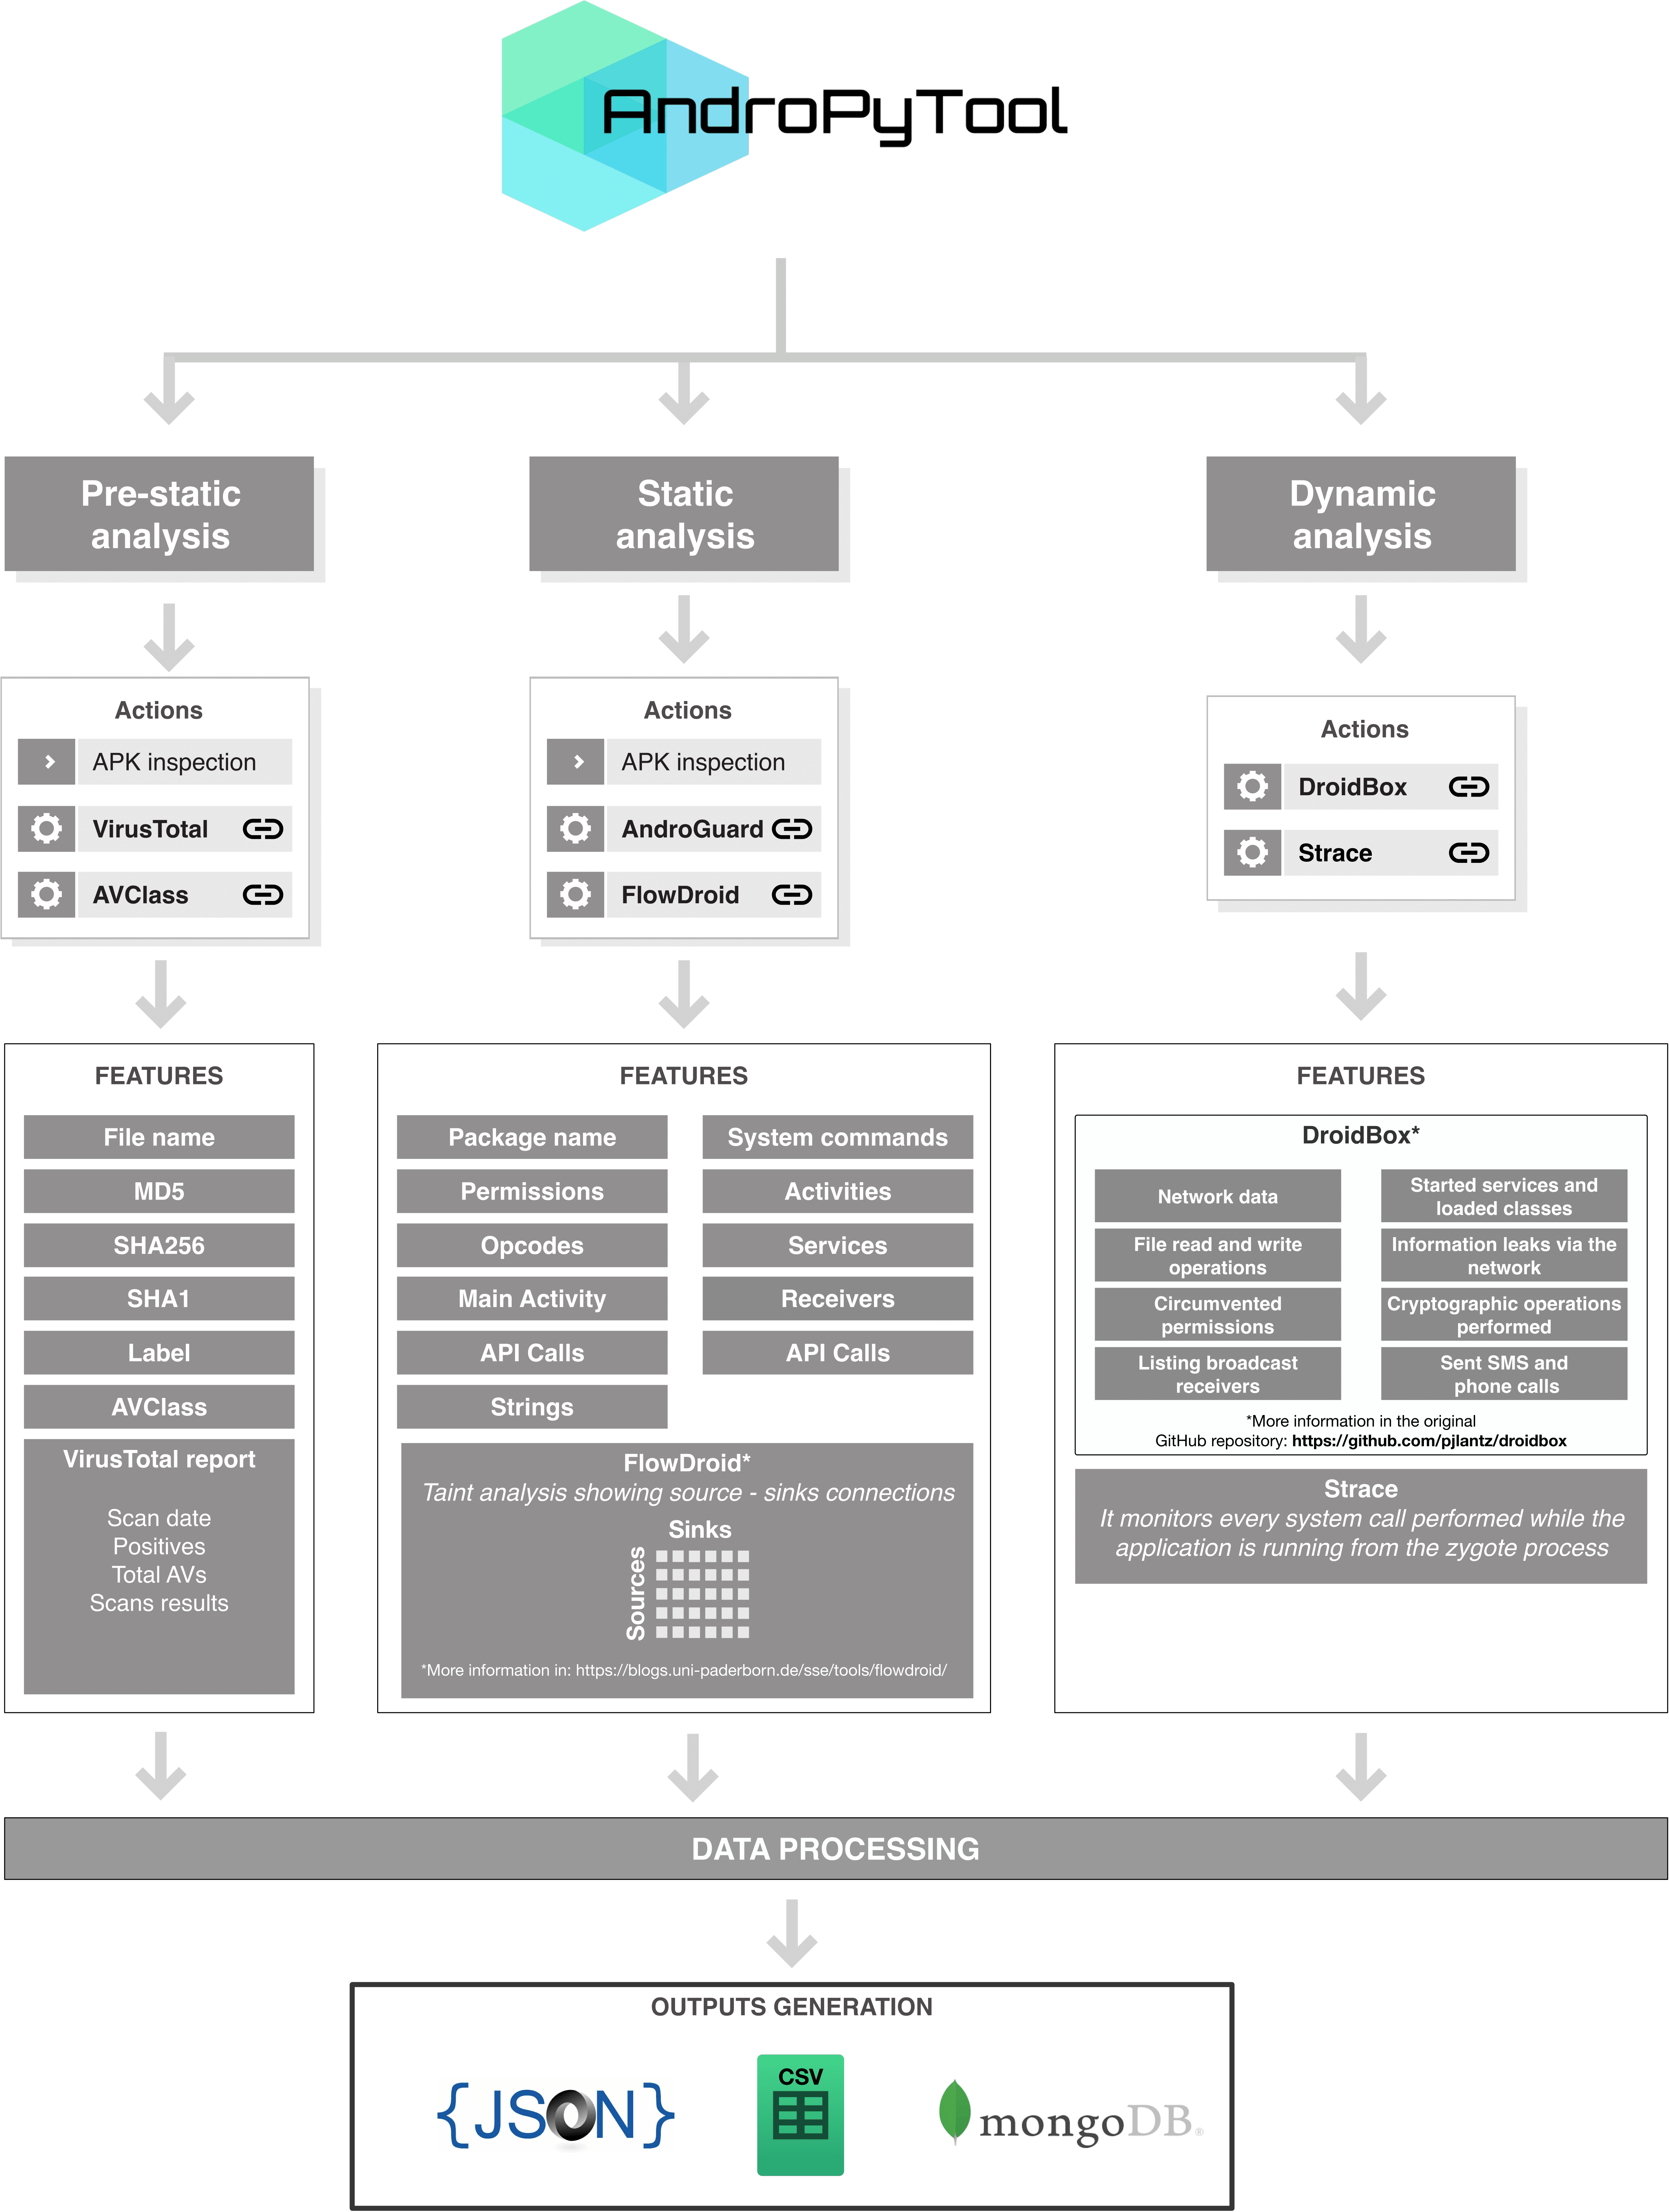 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…