MobileApp-Pentest-Cheatsheet

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

dex-vm used to protect the android classes.dex file

Unofficial frida extension for VSCode

Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…

Fermion, an electron wrapper for Frida & Monaco.

A native APK and DEX decompiler written in Rust

The ARTful library for dynamically modifying the Android Runtime

Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…

Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

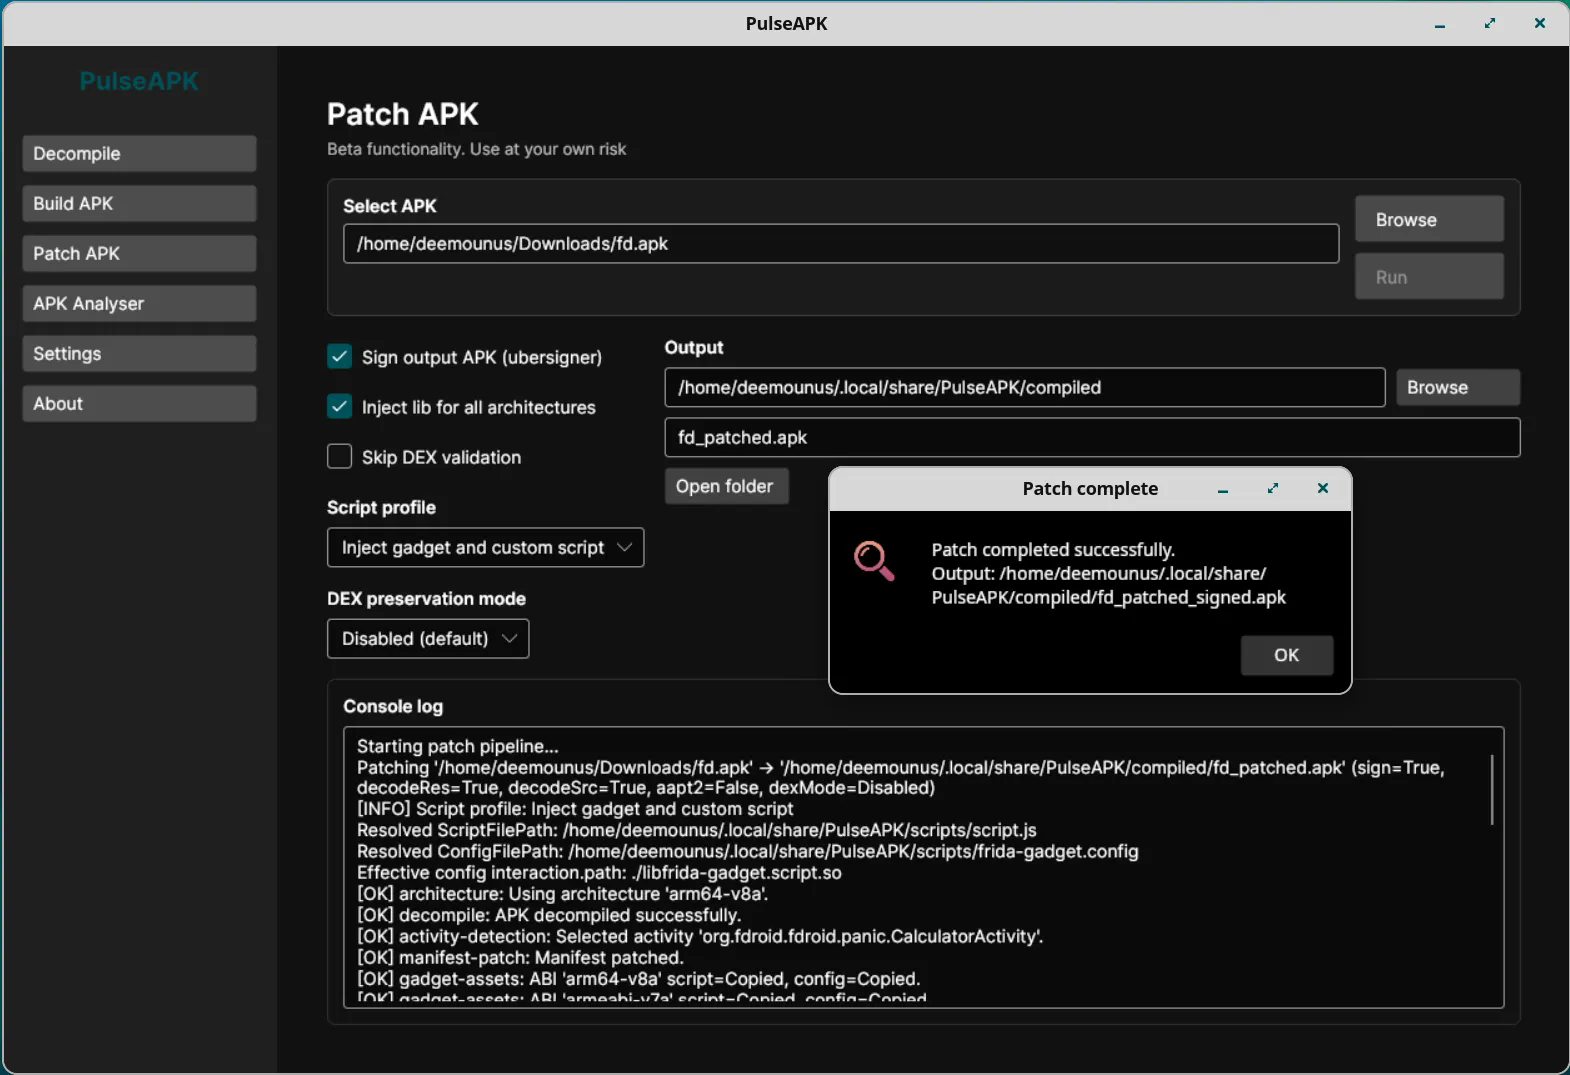
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building

a fully autonomous AI agent for reverse engineering

Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.

This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…