

cnspec
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
cloud-infrastructure-securitycloud-securityconfiguration-auditing+6
443
mondoohq/cnspecAn open source, cloud-native security to protect everything from build to runtime
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
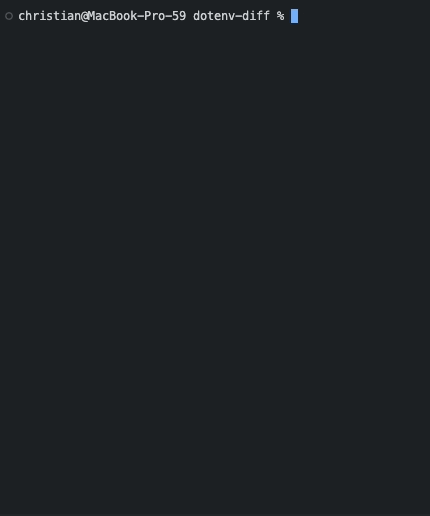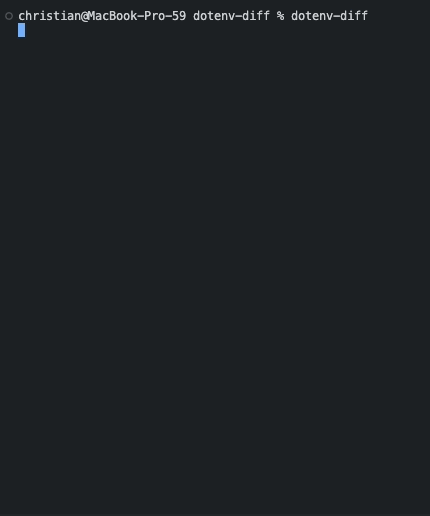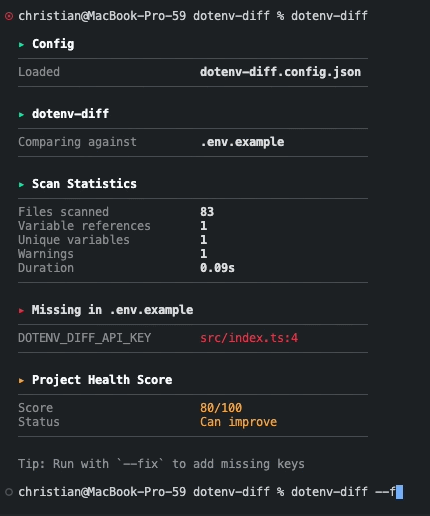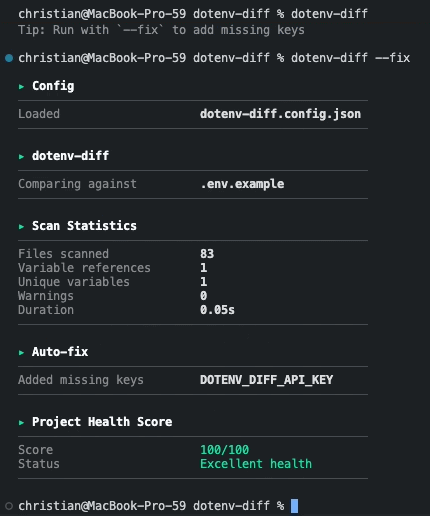 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 0x6d69636b/windows_hardening
HardeningKitty and Windows Hardening Settings
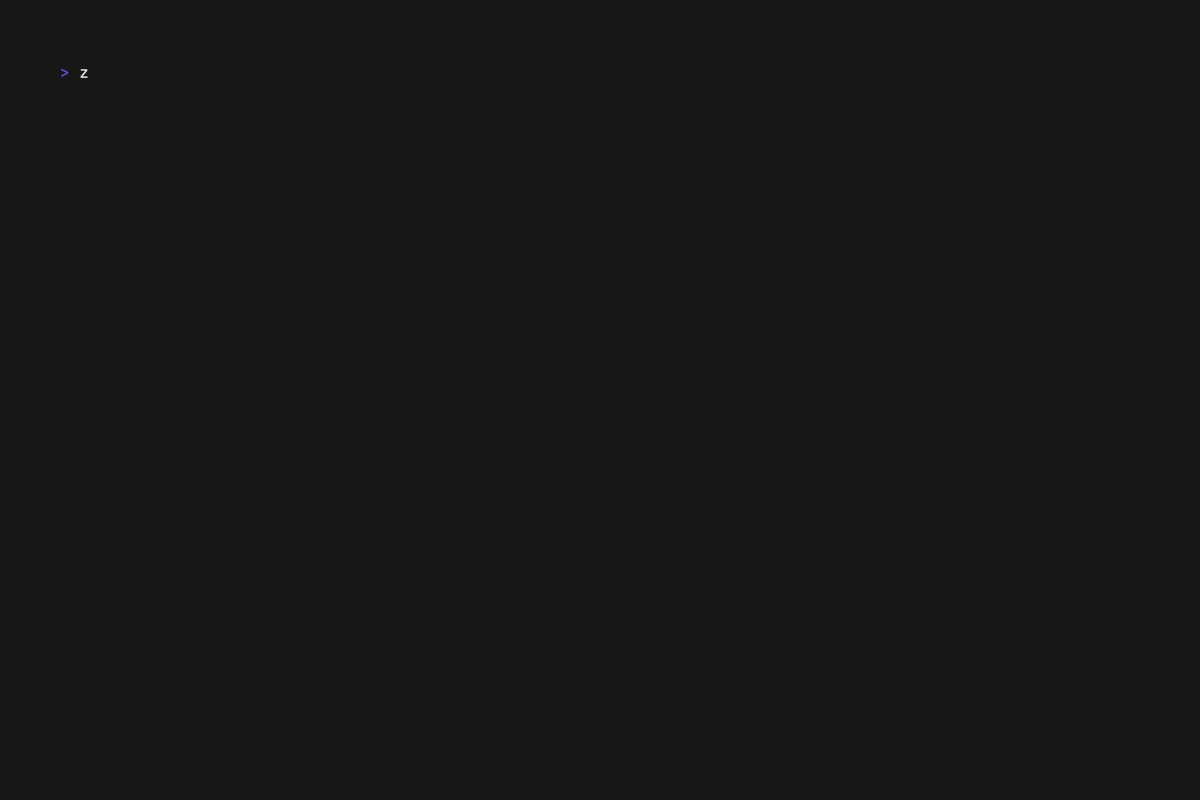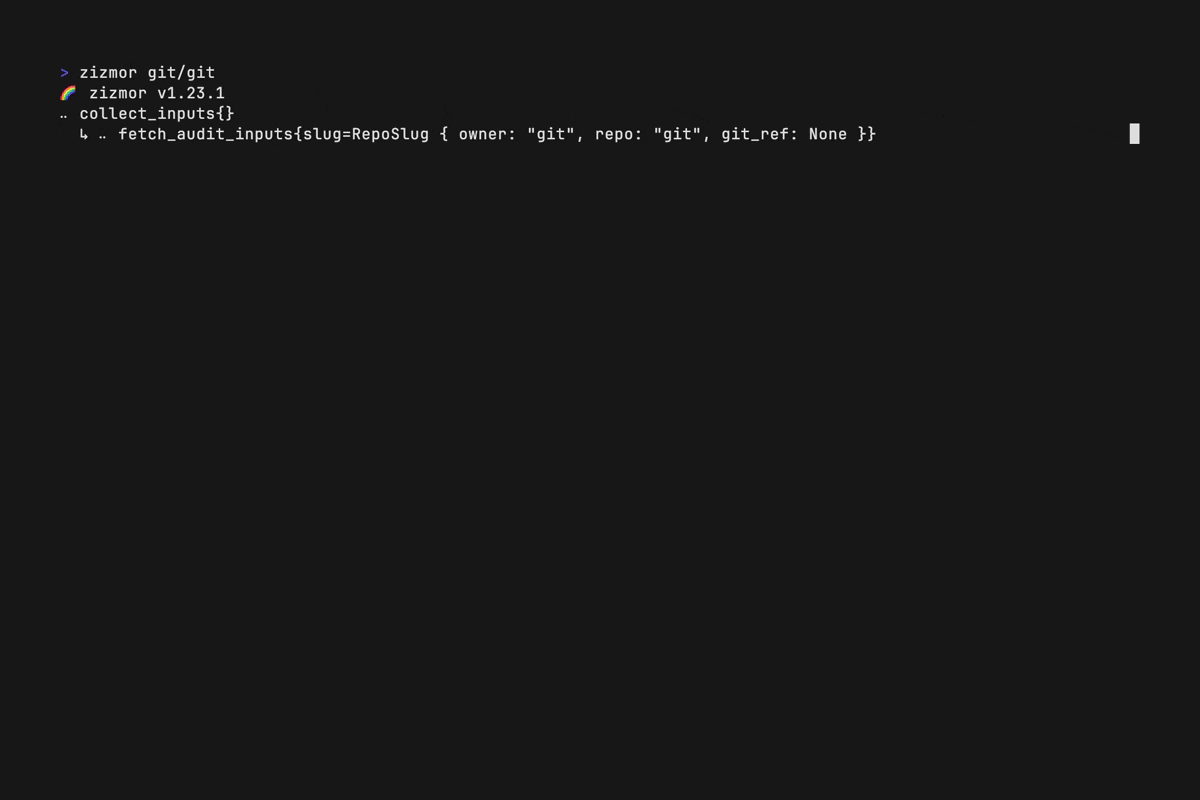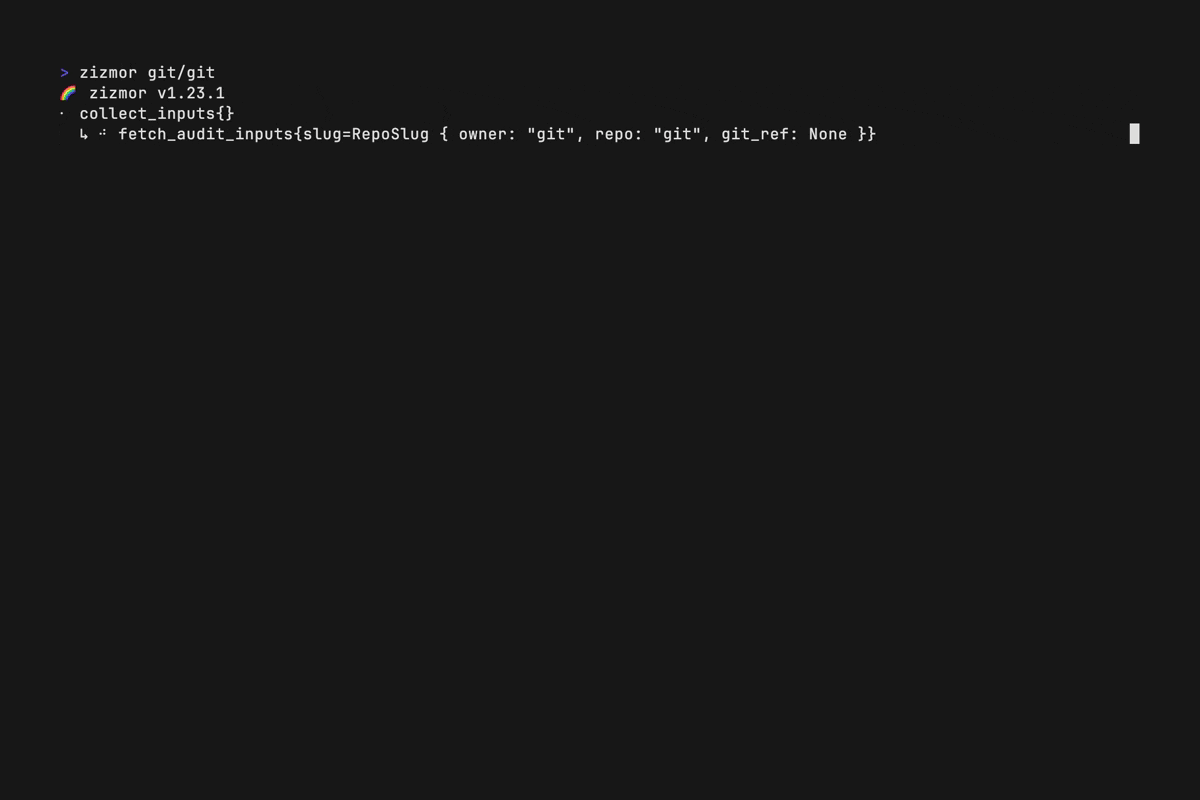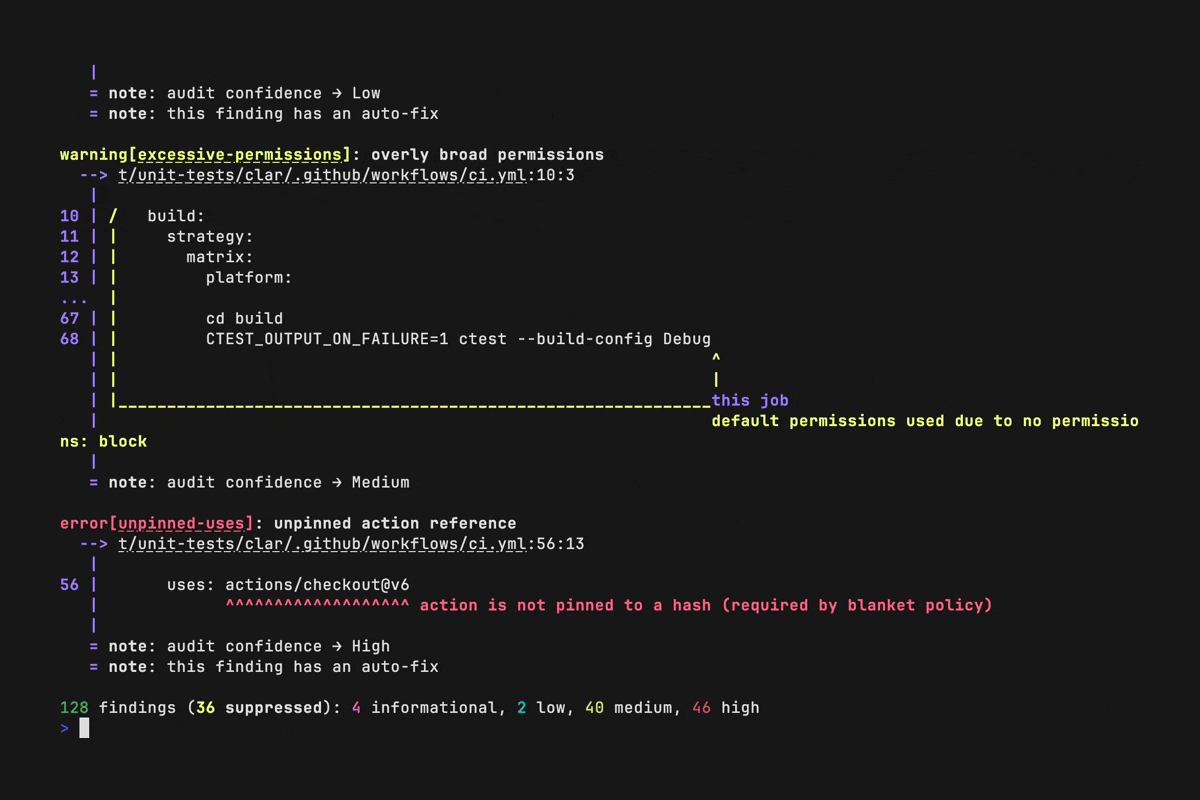 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 clearhandreview/vulnerpocalypse-containment
Open-source vulnerability analysis, CVE tracking, patch verification, and temporary security containment tools
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 g4bri-3l3/hostbadger
Windows host hardening auditor and remediation tool in PowerShell: CIS, DISA STIG, Essential Eight checks, reversible fixes, optional AI analysis
 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…