
prowler
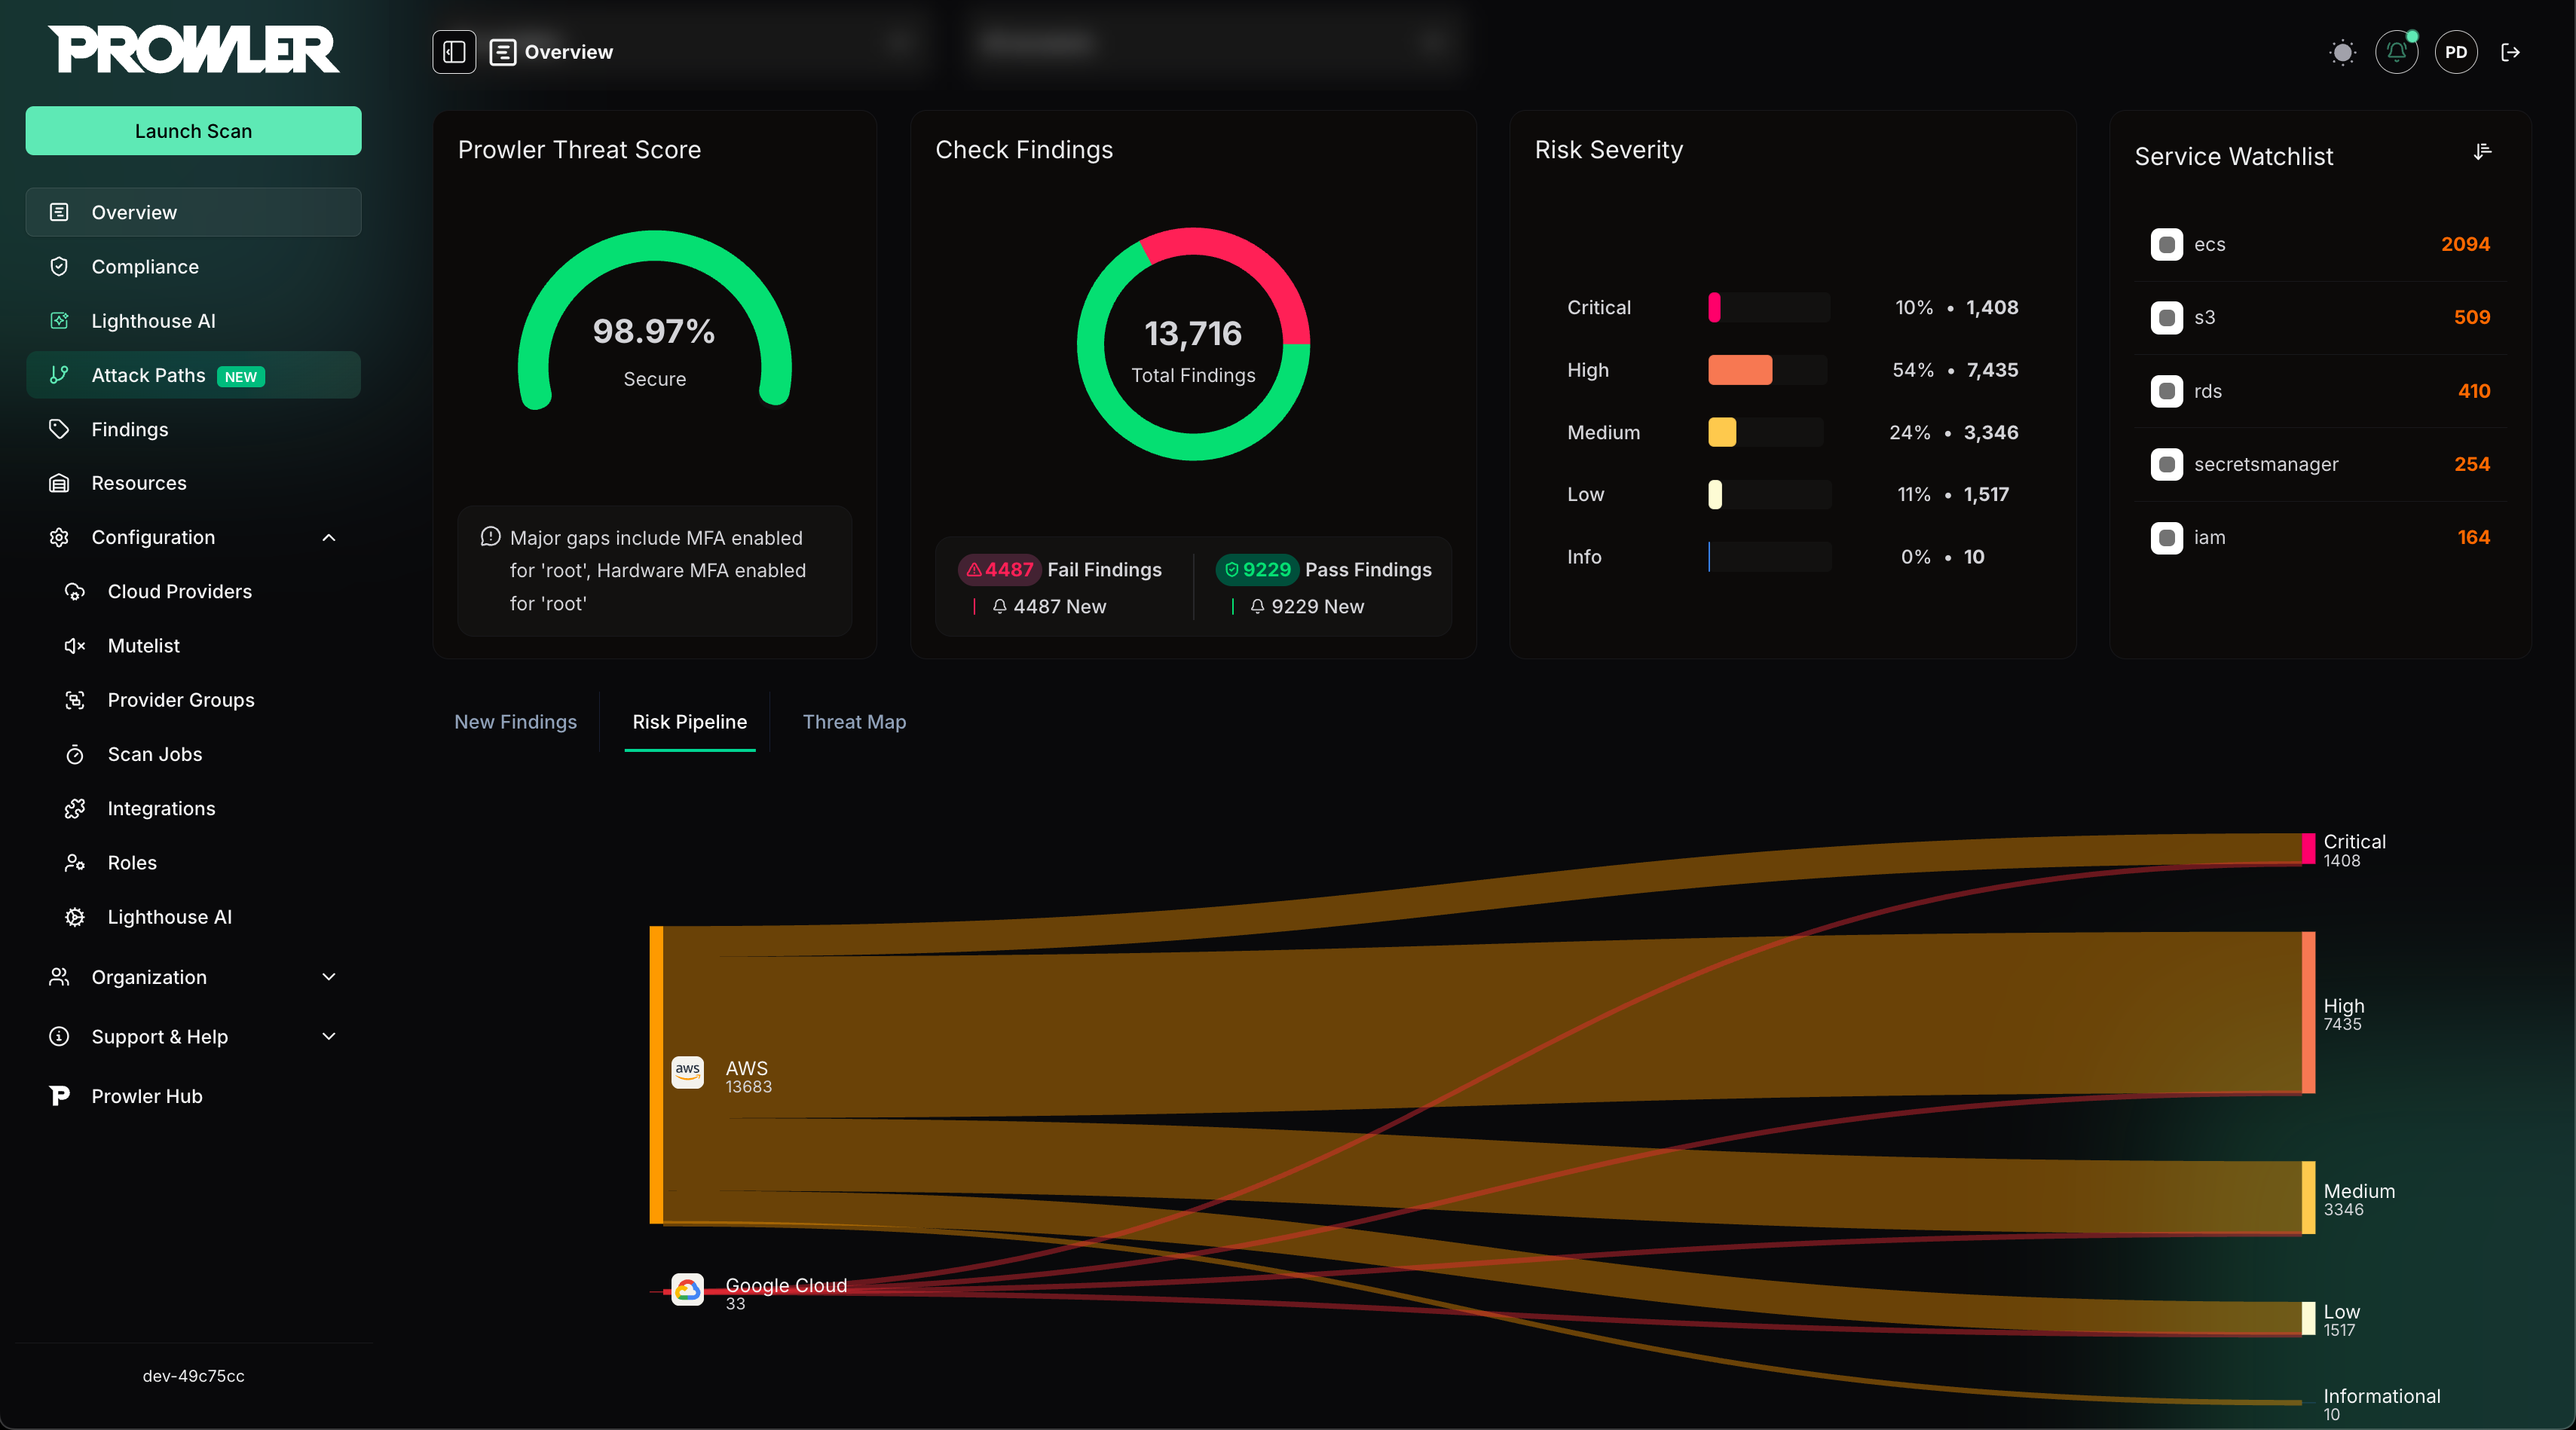
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Snyk CLI scans and monitors your projects for security vulnerabilities.

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

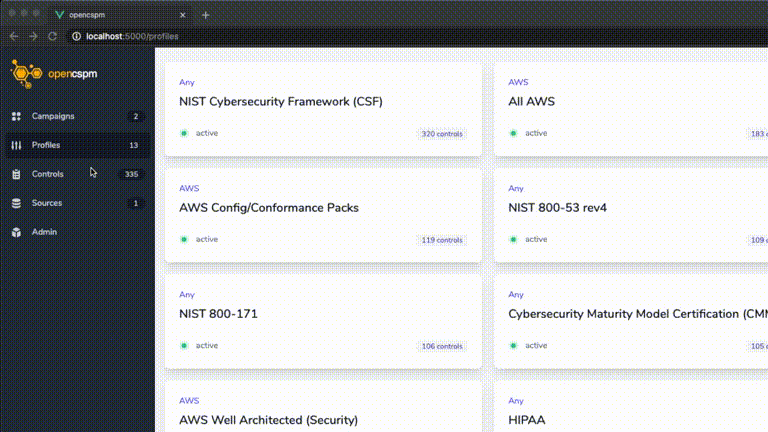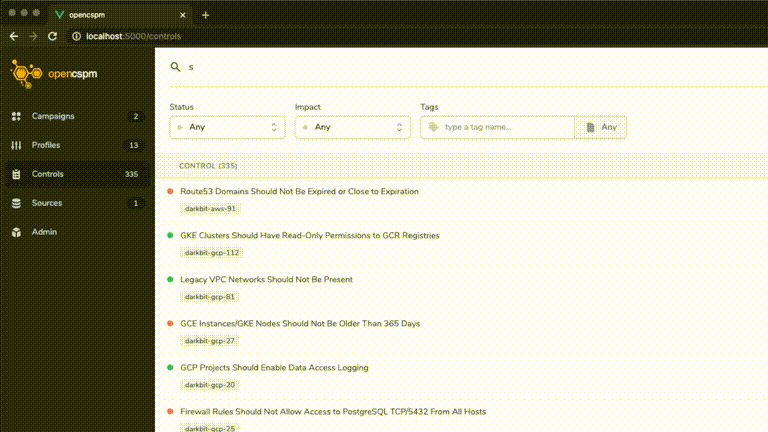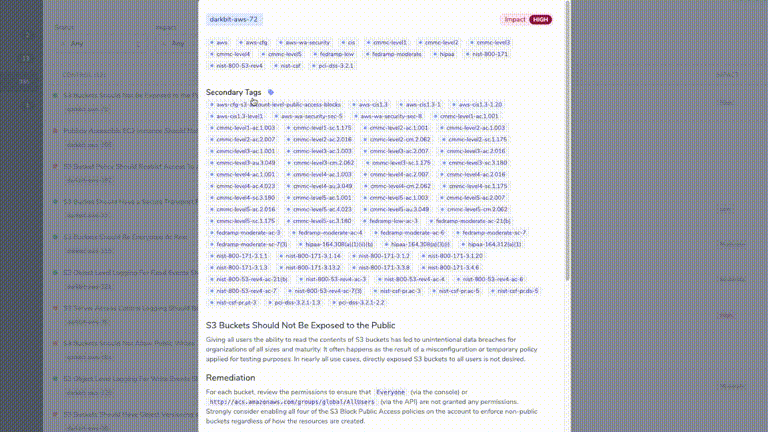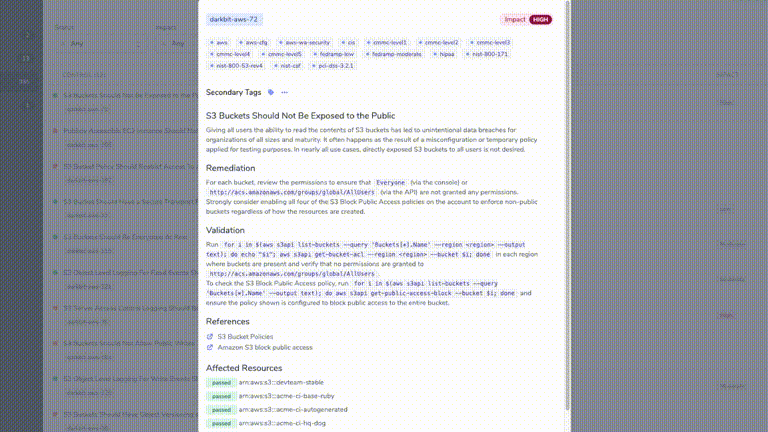
Open Cloud Security Posture Management Engine

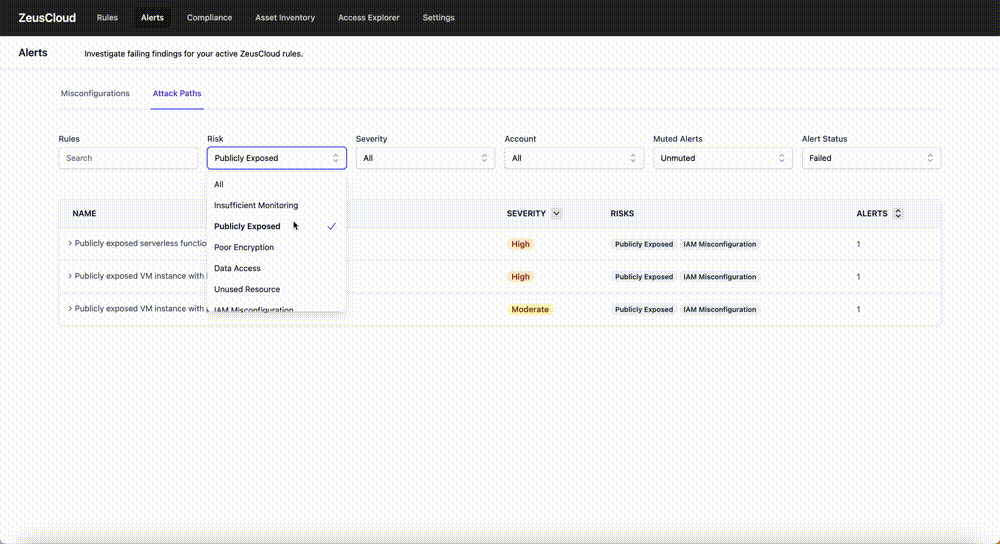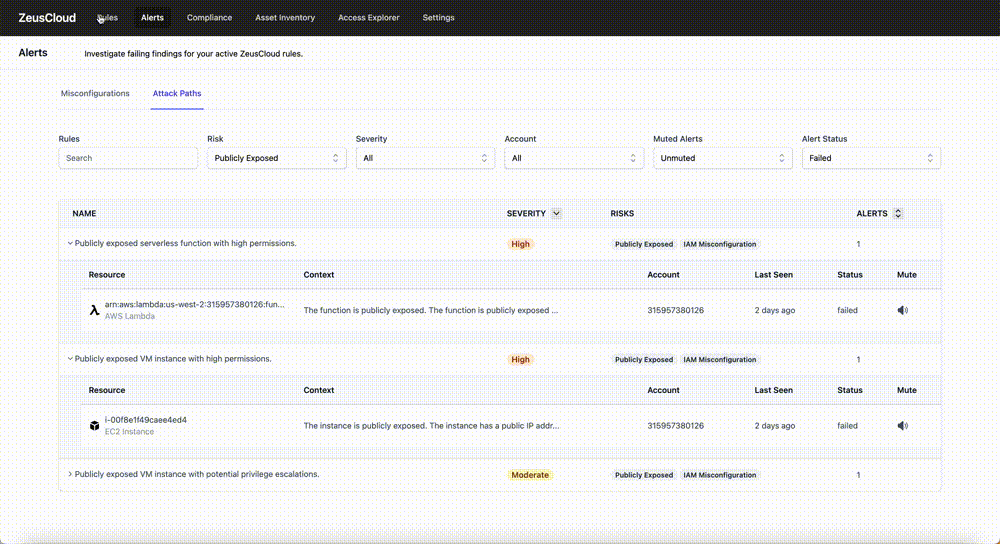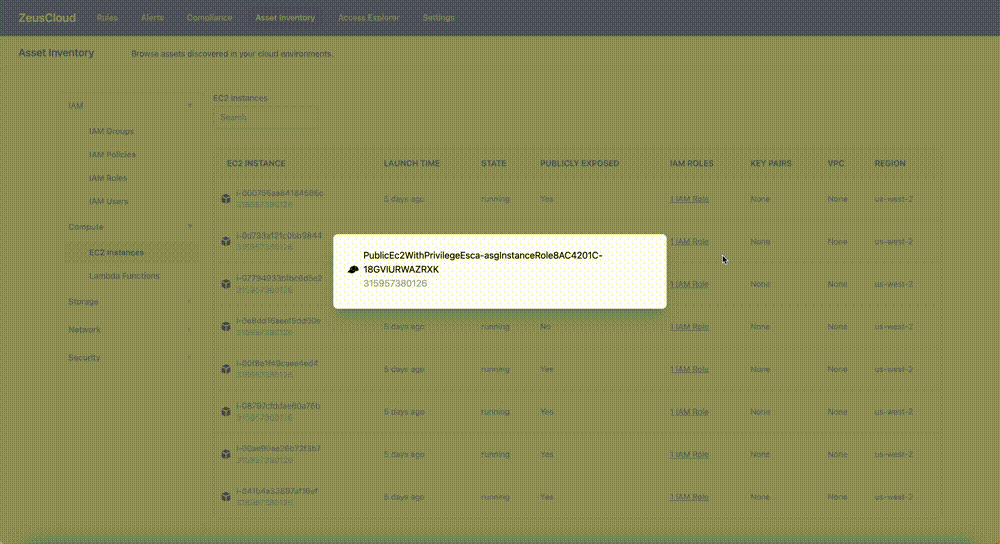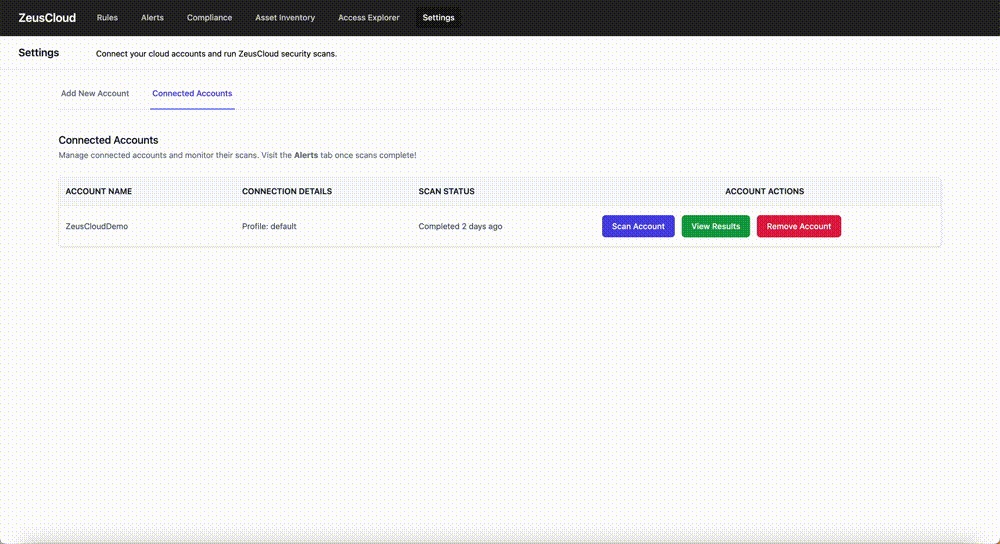
Open-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…

Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…

Bash script to detect vulnerable XZ Utils versions (CVE-2024-3094) and downgrade to a safe release, supporting multiple Linux distributions and…

Scans AWS IAM configurations for shadow admins by detecting misconfigured deny policies that fail to restrict user actions on groups, enabling…

Validation of best practices in your Kubernetes clusters

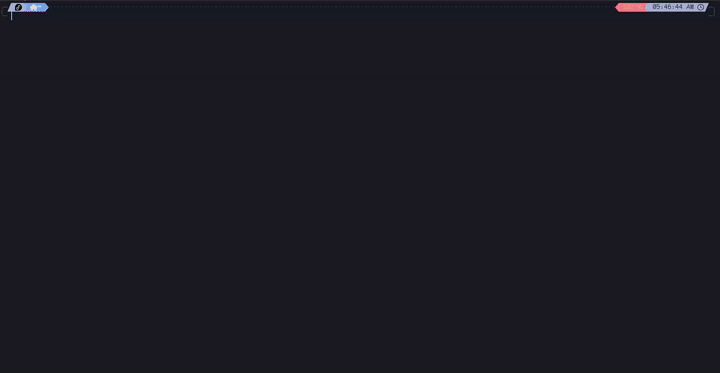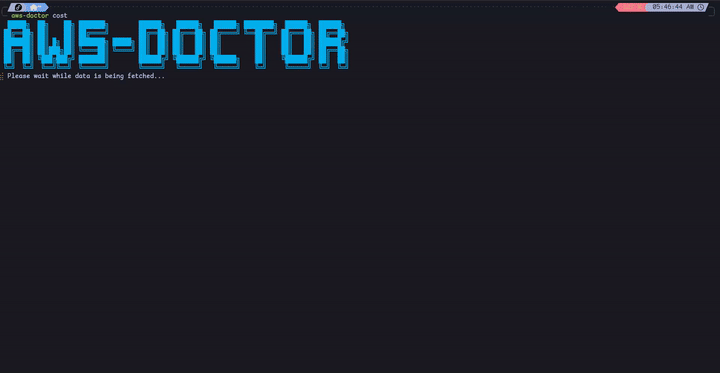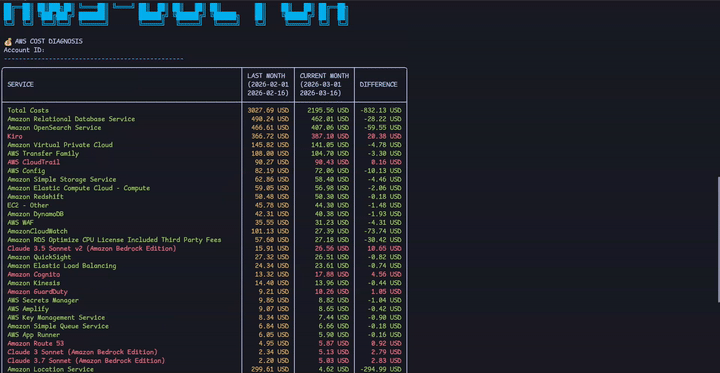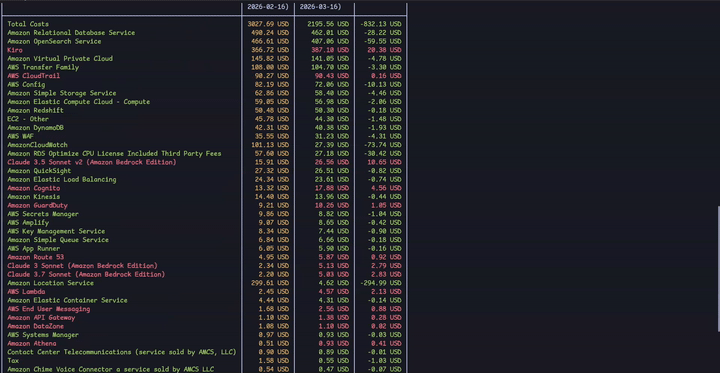
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️

Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…

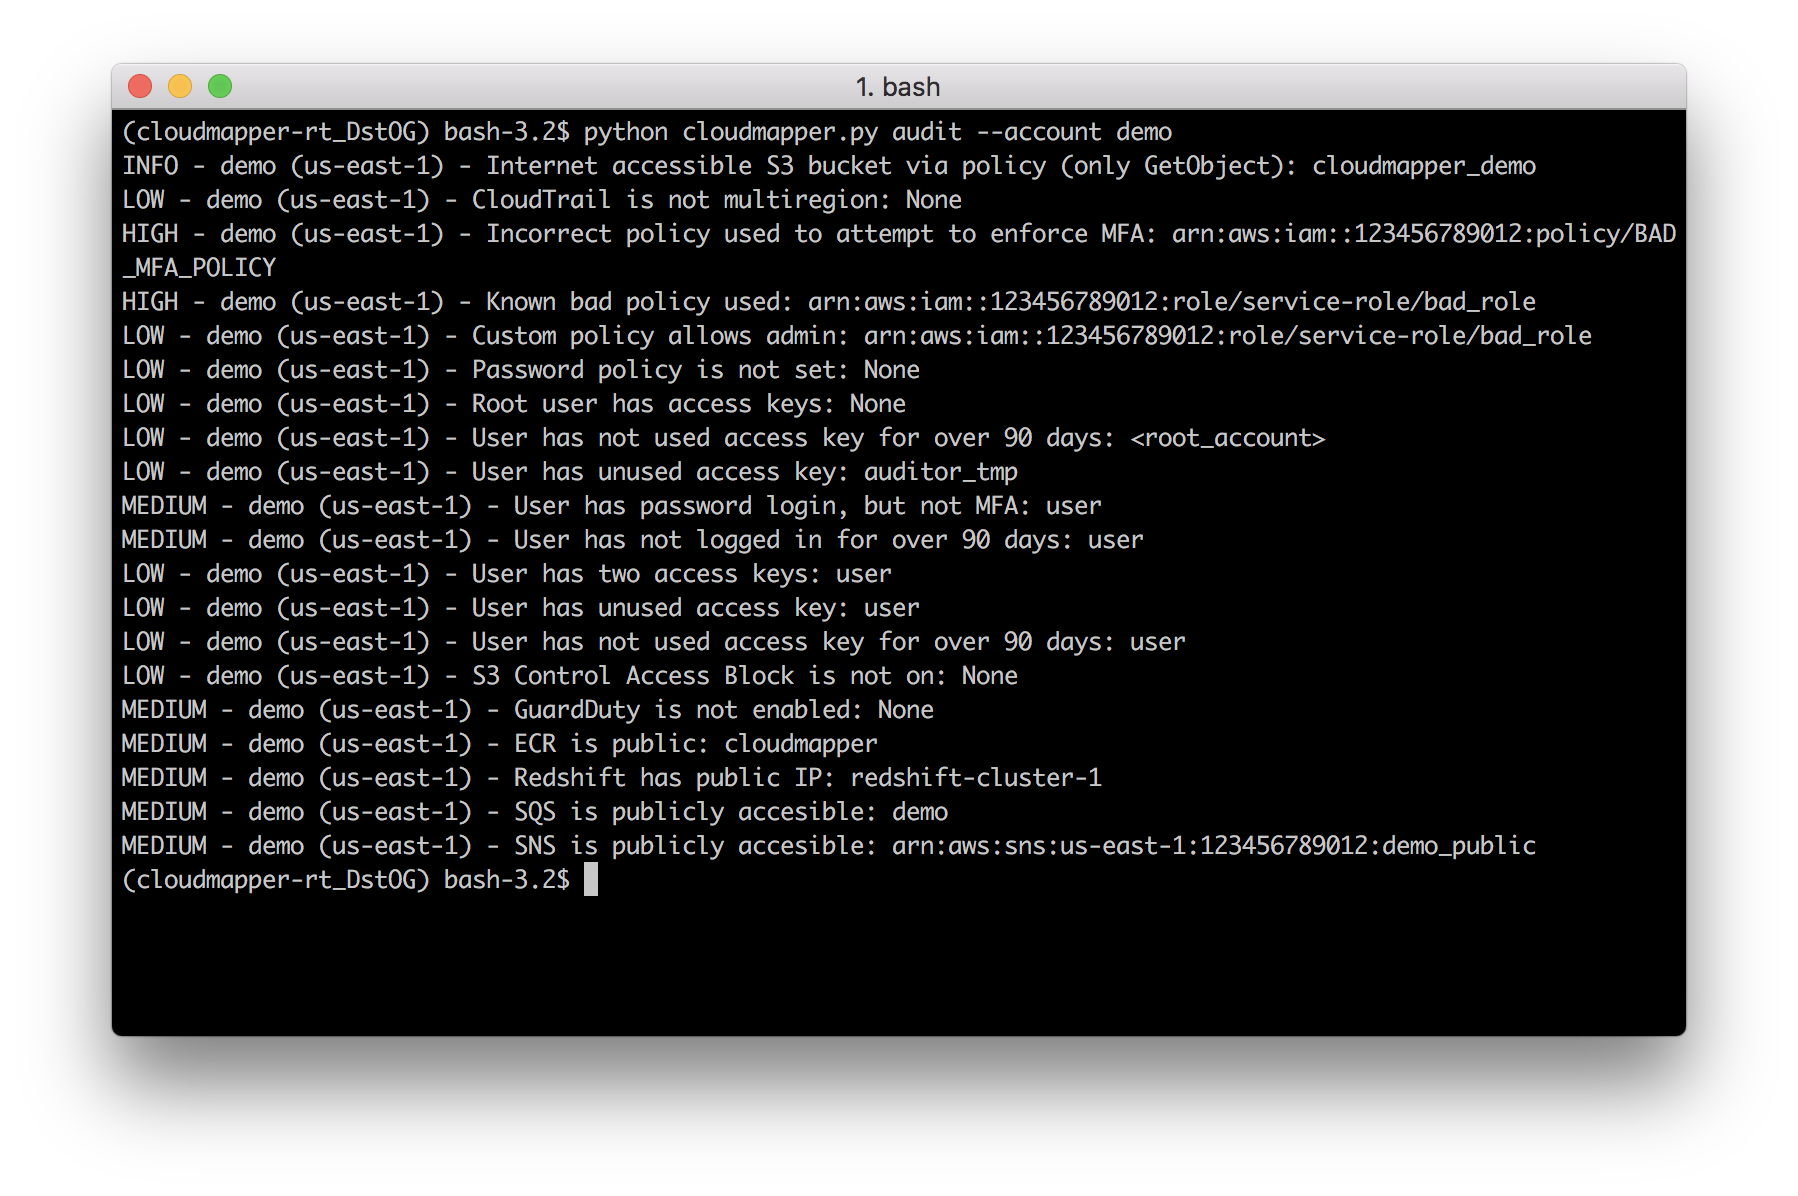
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.

Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…

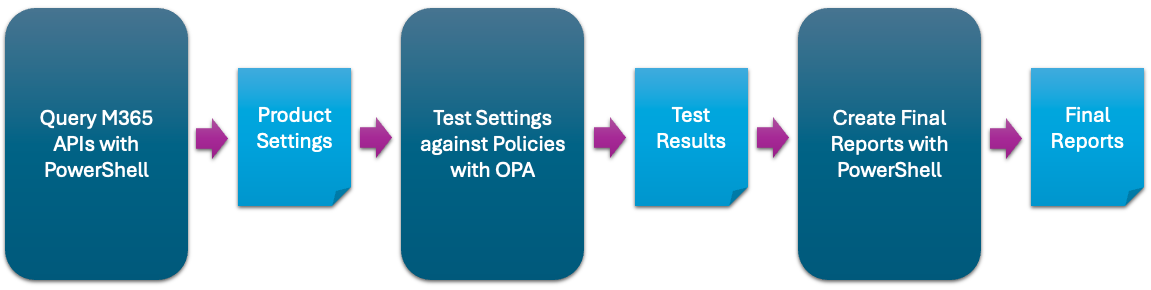
Automation to assess the state of your M365 tenant against CISA's baselines

kubeaudit helps you audit your Kubernetes clusters against common security controls

Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…

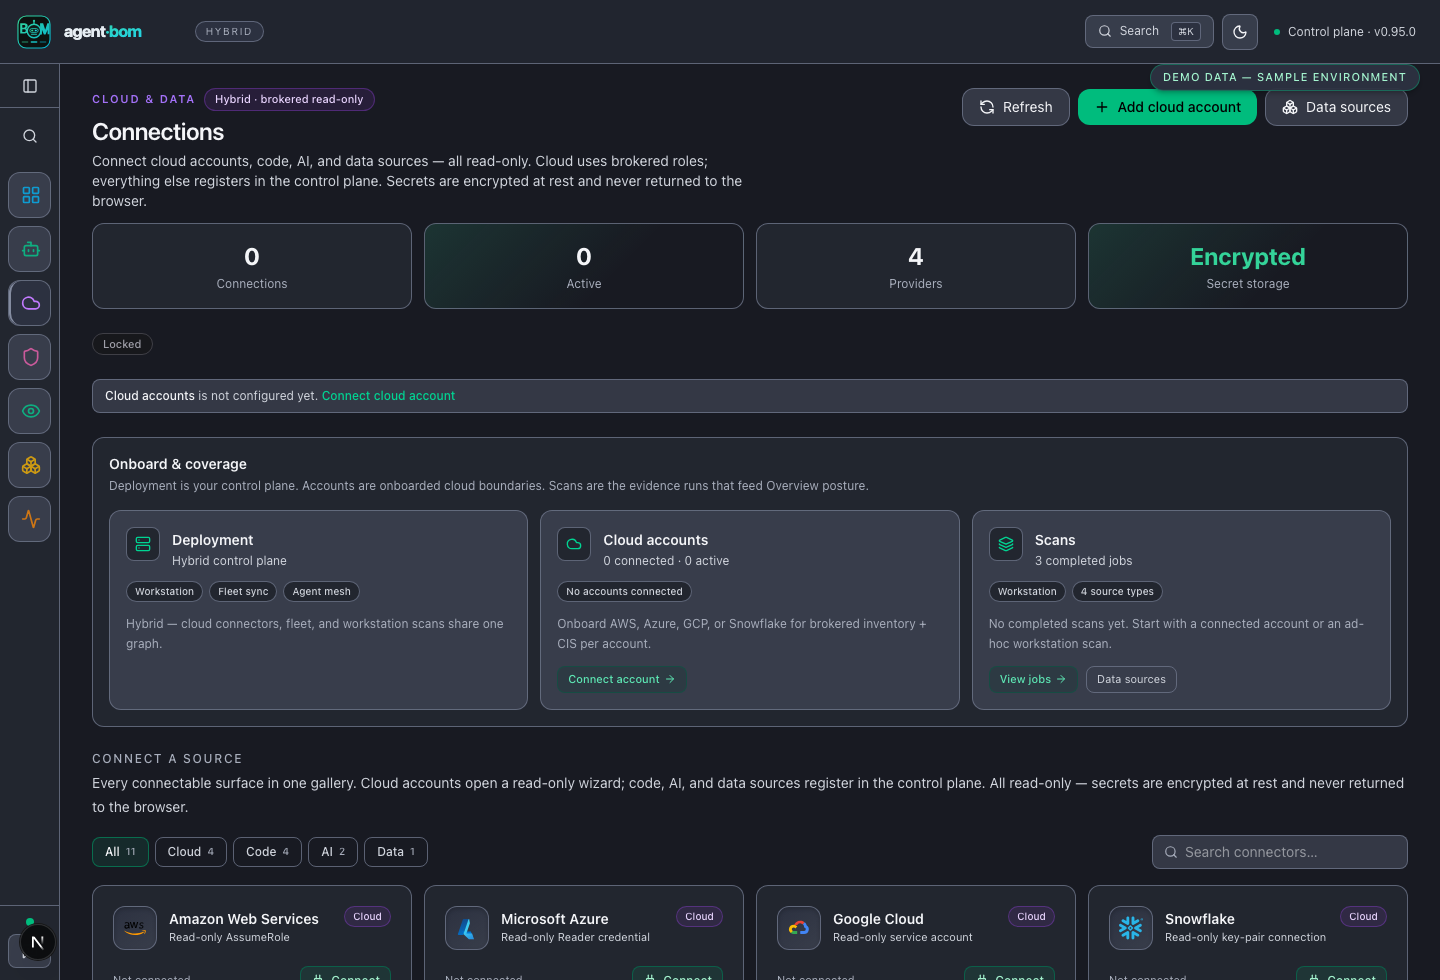
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…

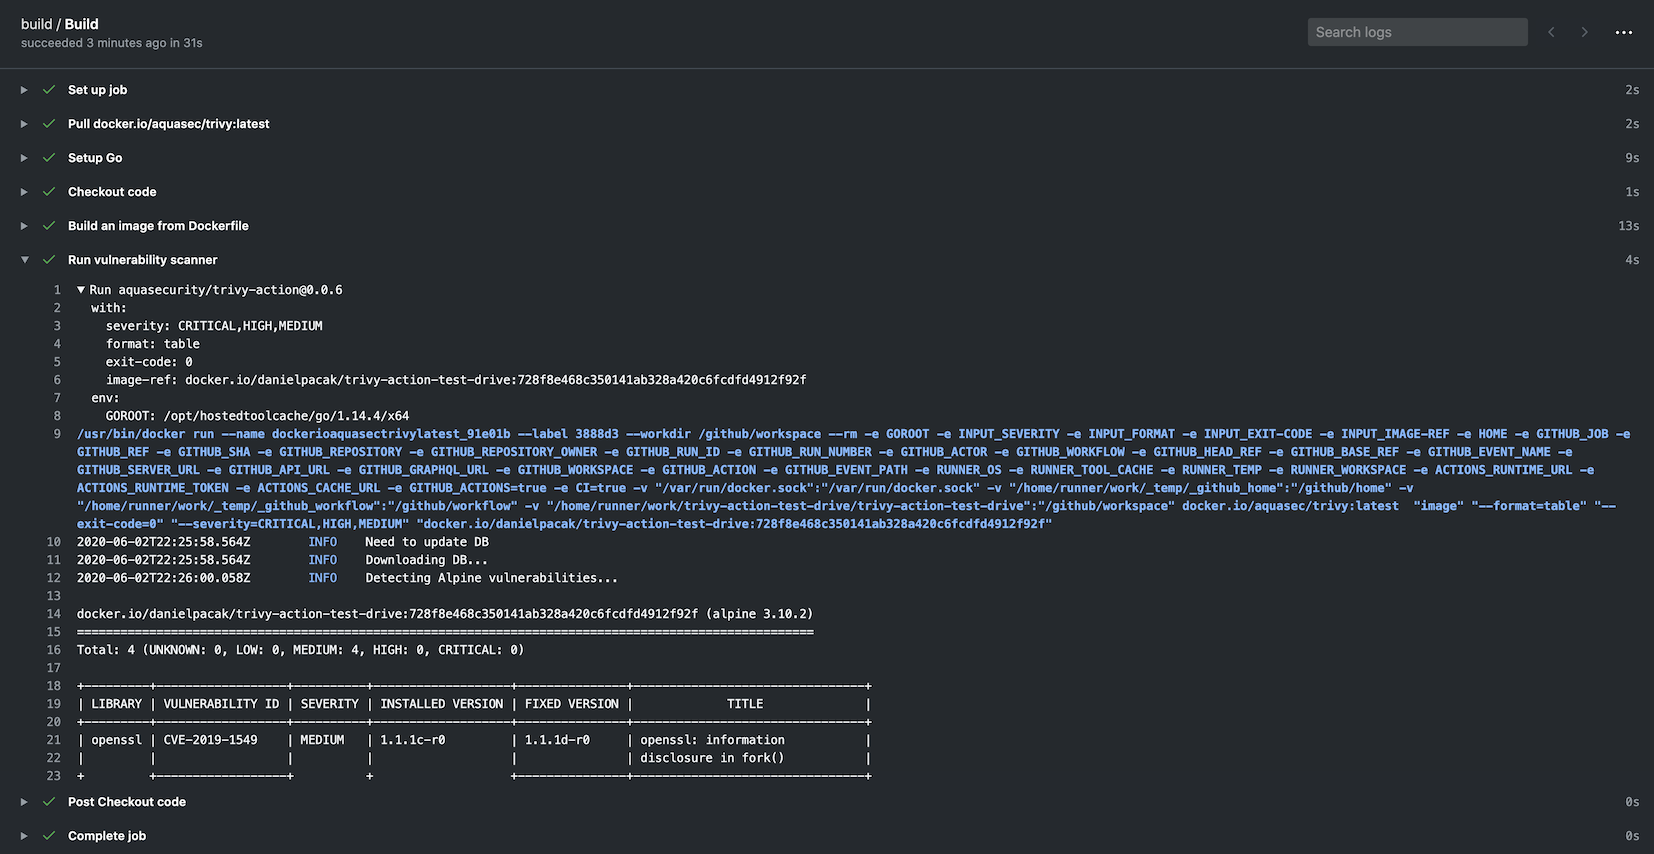
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities