
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
371 results
inception preview

inception

GitHubcarmaa/inception

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
digital-forensicsexploitationhardware-security+6
1.6k
1 year ago
frida-dexdump preview
Archived

frida-dexdump

GitHubhluwa/frida-dexdump

A frida tool to dump dex in memory to support security engineers analyzing malware.
android-securitybinary-analysisdynamic-analysis-sandboxing+5
4.6k3 years ago
clairvoyance preview

clairvoyance

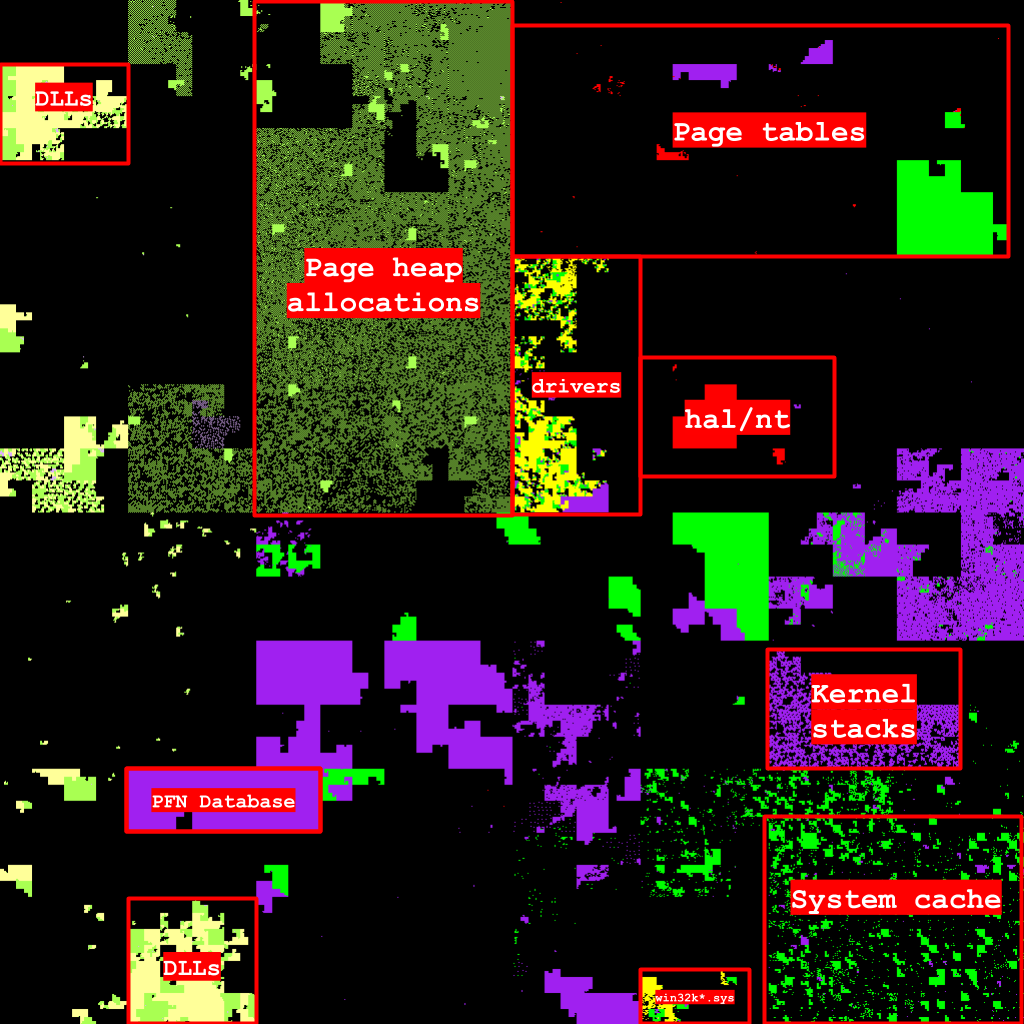
GitHub0vercl0k/clairvoyance

Visualize the virtual address space of a Windows process on a Hilbert curve.

digital-forensicsforensicsmemory-forensics
3115 years ago
Centry preview

Centry

GitHub0xpoly/centry

Panic button for protection against cold boot attacks

data-recoverydefensive-toolsencryption-decryption-tools+3
1464 years ago
POC-CVE-2023-32233 preview

POC-CVE-2023-32233

GitHuboferchen/poc-cve-2023-32233

Use-After-Free in Netfilter nf_tables when processing batch requests CVE-2023-32233

binary-exploitationexploitationmemory-forensics+4
533 years ago
CVE-2025-7771 preview

CVE-2025-7771

GitHublzty/cve-2025-7771

Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
binary-exploitationexploitationmemory-forensics+3
27 months ago
extra_recipe preview

extra_recipe

GitHubldebug/extra_recipe

Ian Beer's exploit for CVE-2017-2370 (kernel memory r/w on iOS 10.2)

binary-exploitationexploitationios-security+3
9 years ago
LAB-DFIR-cve-2023-38831 preview

LAB-DFIR-cve-2023-38831

GitHubra3edaj/lab-dfir-cve-2023-38831

d

digital-forensicsdisk-forensicseducation+6
1 year ago
PPLdump preview
Archived

PPLdump

GitHubitm4n/ppldump

Dump the memory of a PPL with a userland exploit

binary-exploitationexploitationmemory-forensics+3
8904 years ago
cve-2025-14847 preview

cve-2025-14847

GitHubkuyrathdaro/cve-2025-14847

MongoBleed: CVE-2025-14847 Memory Leak Discovery Tool
database-securityeducationexploitation+3
8 months ago
freebsd-dirent-info-leak-bugs preview

freebsd-dirent-info-leak-bugs

GitHubfarazsth98/freebsd-dirent-info-leak-bugs

CVE-2020-25578 and CVE-2020-25579: Some FreeBSD info leak bugs I found in 2020.
binary-analysisexploitationinformation-gathering+2
75 years ago
CVE-2025-14847 preview

CVE-2025-14847

GitHubjoshuavanderpoll/cve-2025-14847

CVE-2025-14847 (MongoBleed)

database-securityexploitationinformation-gathering+3
48 months ago
cve-2018-12798 preview

cve-2018-12798

GitHubsandi-go/cve-2018-12798

Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.

binary-exploitationexploitationmemory-forensics+2
6 years ago
wmi-static-spoofer preview

wmi-static-spoofer

GitHubalex3434/wmi-static-spoofer

Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
exploitationhardware-hackinghardware-iot-security+4
5167 years ago
Citrix-NetScaler-Memory-Leak-CVE-2025-5777 preview

Citrix-NetScaler-Memory-Leak-CVE-2025-5777

GitHubrootxsushant/citrix-netscaler-memory-leak-cve-2025-5777

Update the old POC of CVE-2025-5777 Citrix NetScaler Memory leak
exploitationmemory-forensicspenetration-testing+2
1 year ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3222 years ago
Collect-MemoryDump preview

Collect-MemoryDump

GitHublethal-forensics/collect-memorydump

Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
digital-forensicsforensicsincident-response+1
26510 months ago
apple-positional-audio-codec-invalid-header preview

apple-positional-audio-codec-invalid-header

GitHubzhuowei/apple-positional-audio-codec-invalid-header

CVE-2025-31200 - @Noahhw46 figured it out

binary-exploitationexploitationfuzzing+3
1161 year ago
Previous1…678…21Next