

VMInjector
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
authentication-authorizationbinary-exploitationexploitation+4
hzphreak/vminjectorDLL Injection tool to unlock guest VMs
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 0730nophone/cve-2022-22947-
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947) 注入哥斯拉内存马
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
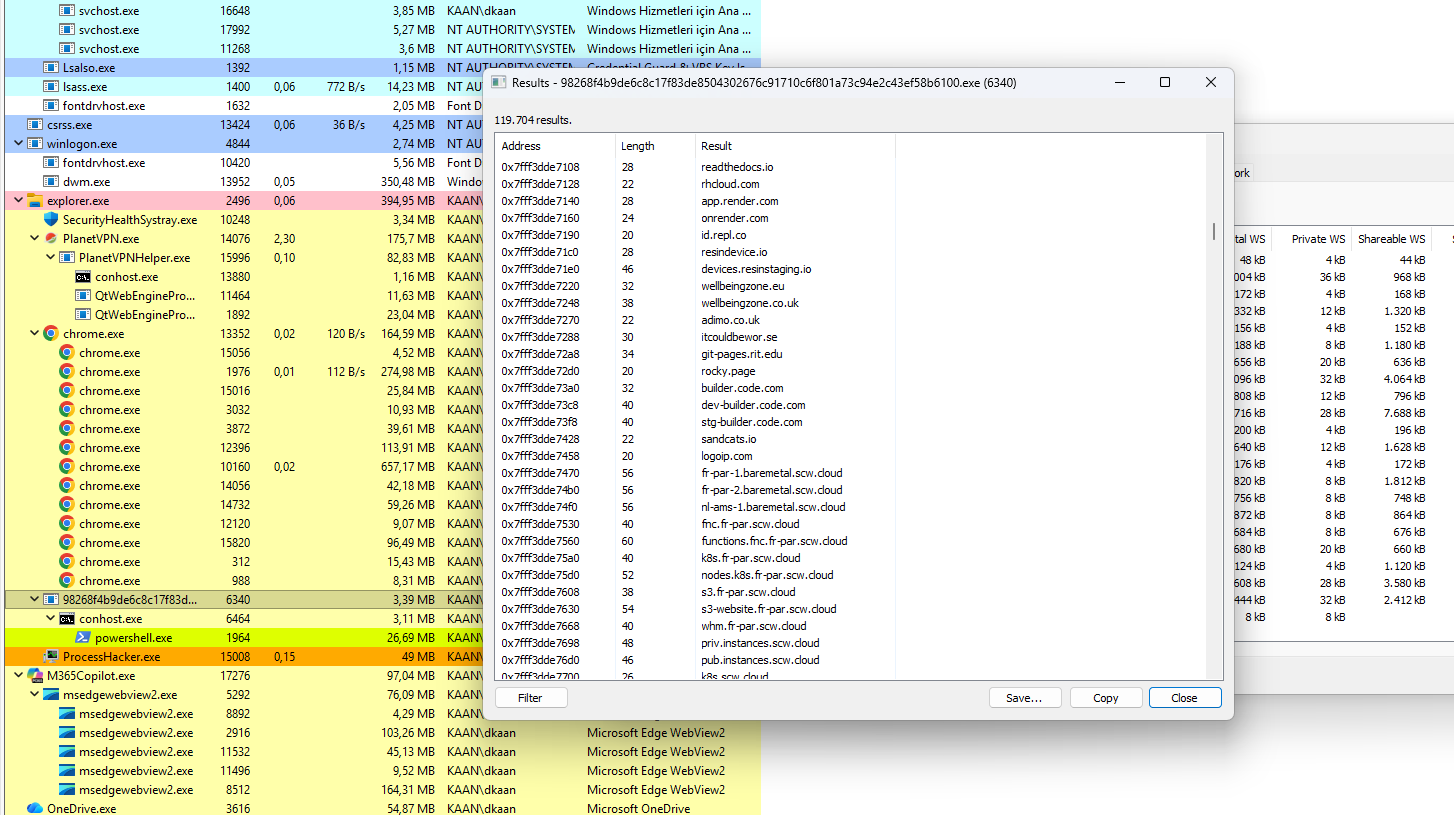 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
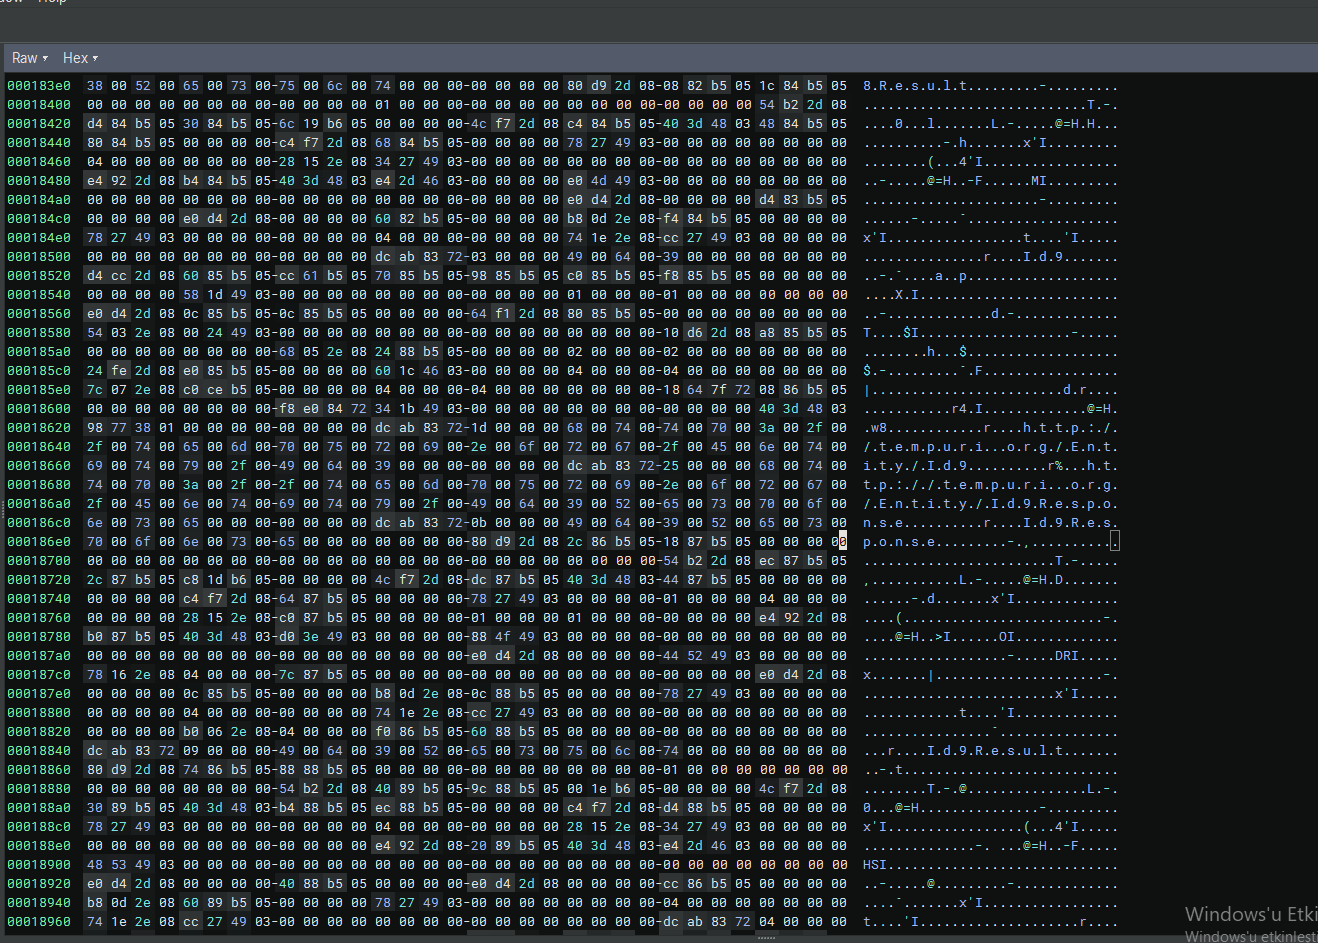 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
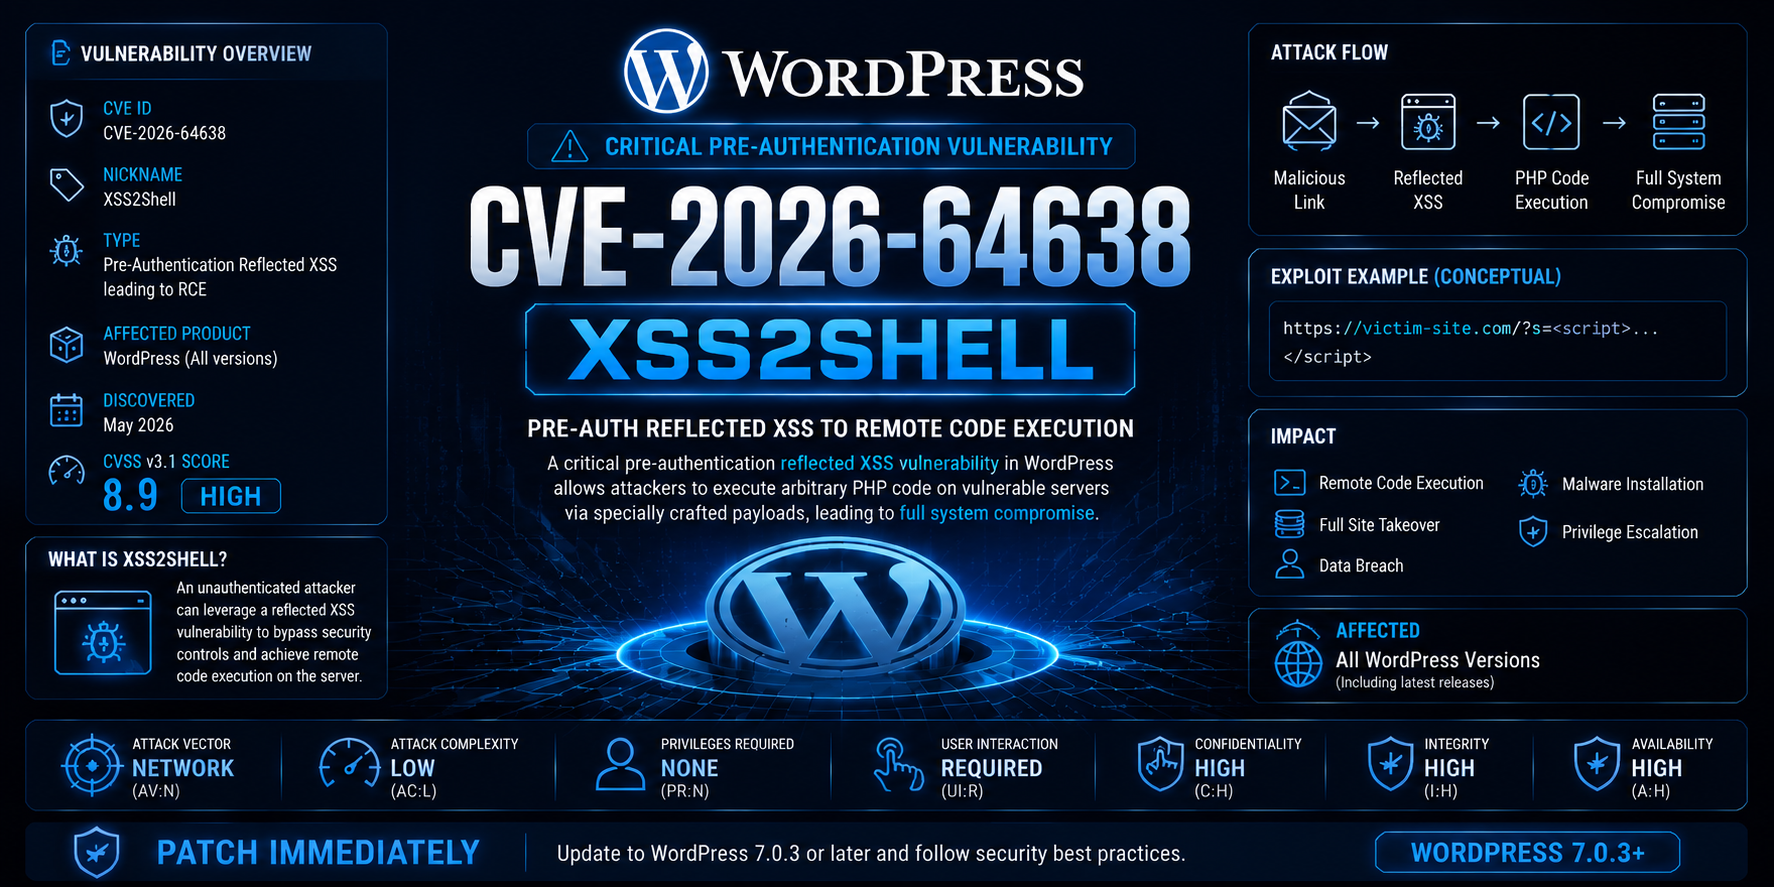 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
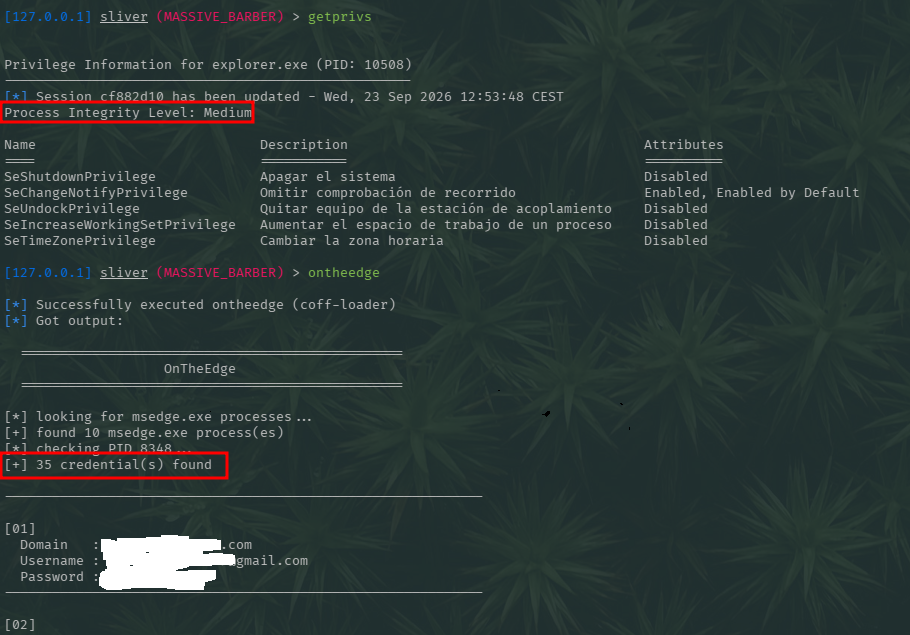 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…