

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
76.6k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 alfarom256/cve-2022-3699
Lenovo Diagnostics Driver EoP - Arbitrary R/W
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 rockrid3r/cve-2023-5178
Exploit for CVE-2023-5178
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 quasarbinary/cve-2024-43630-poc
NtCopyFileChunk stack buffer overflow POC
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
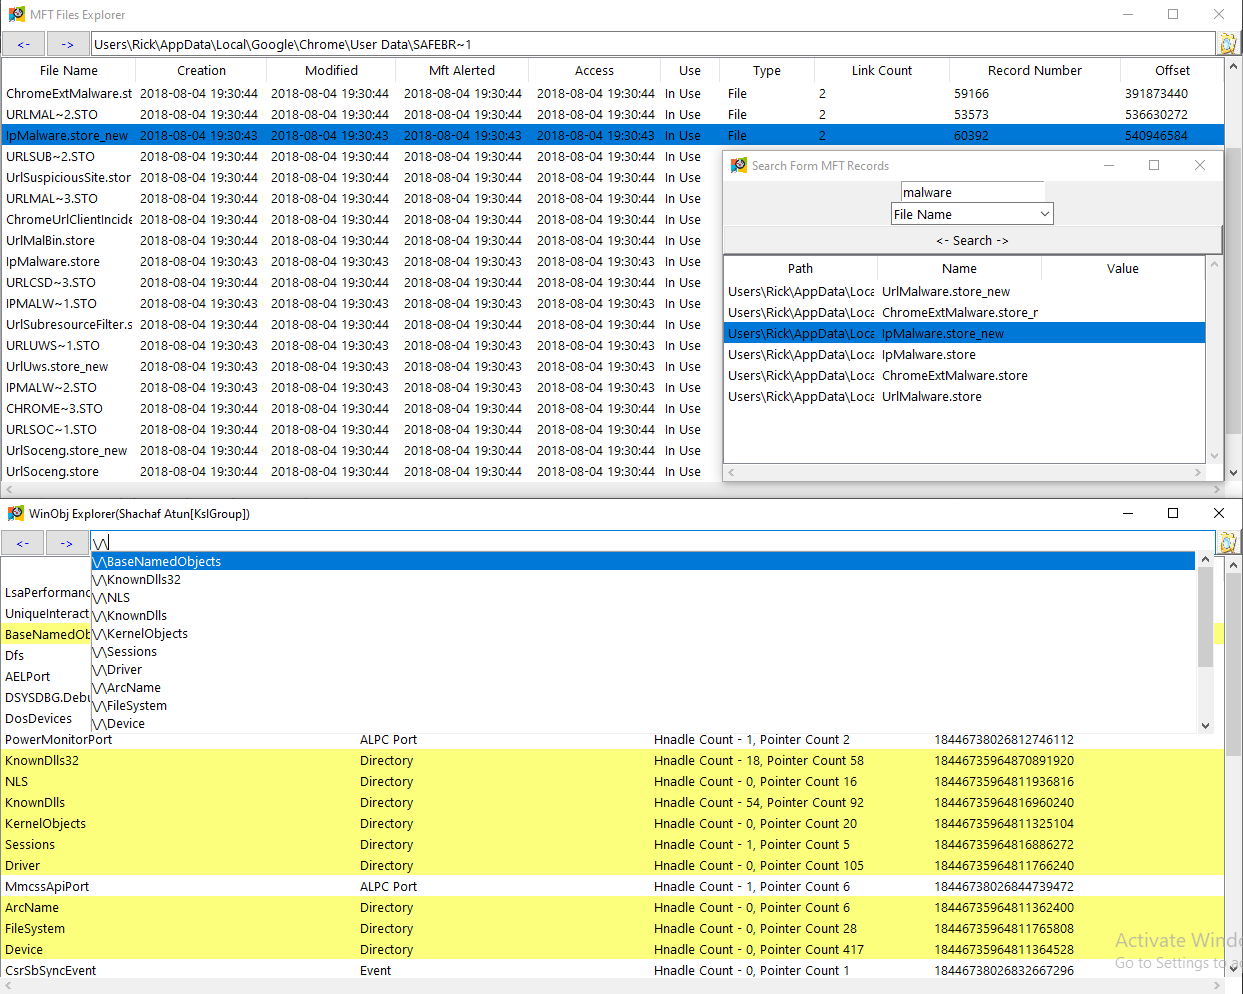 memoryforensics1/volexp
volatility explorer (volatility 2)
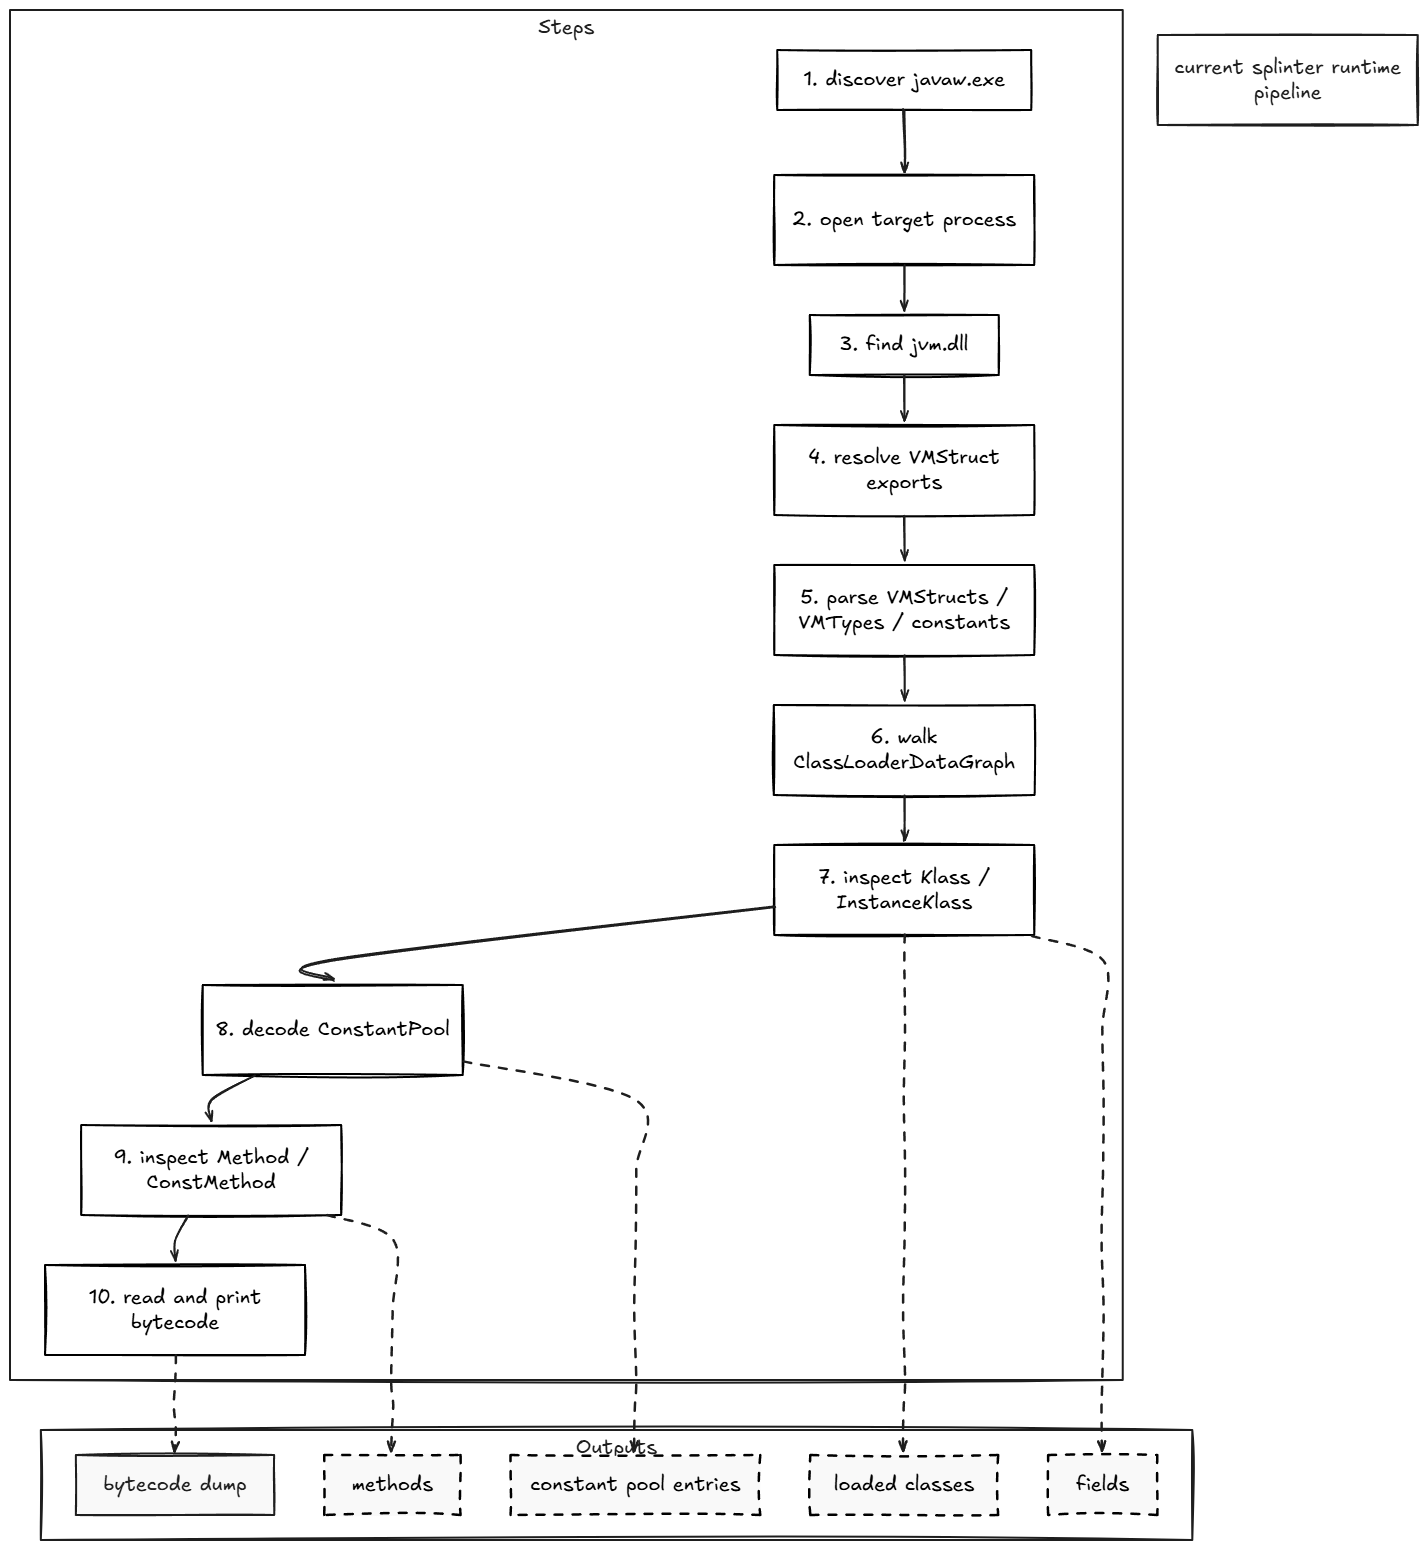 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 nccgroup/libdlmalloc
Heap analysis tooling for dlmalloc
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
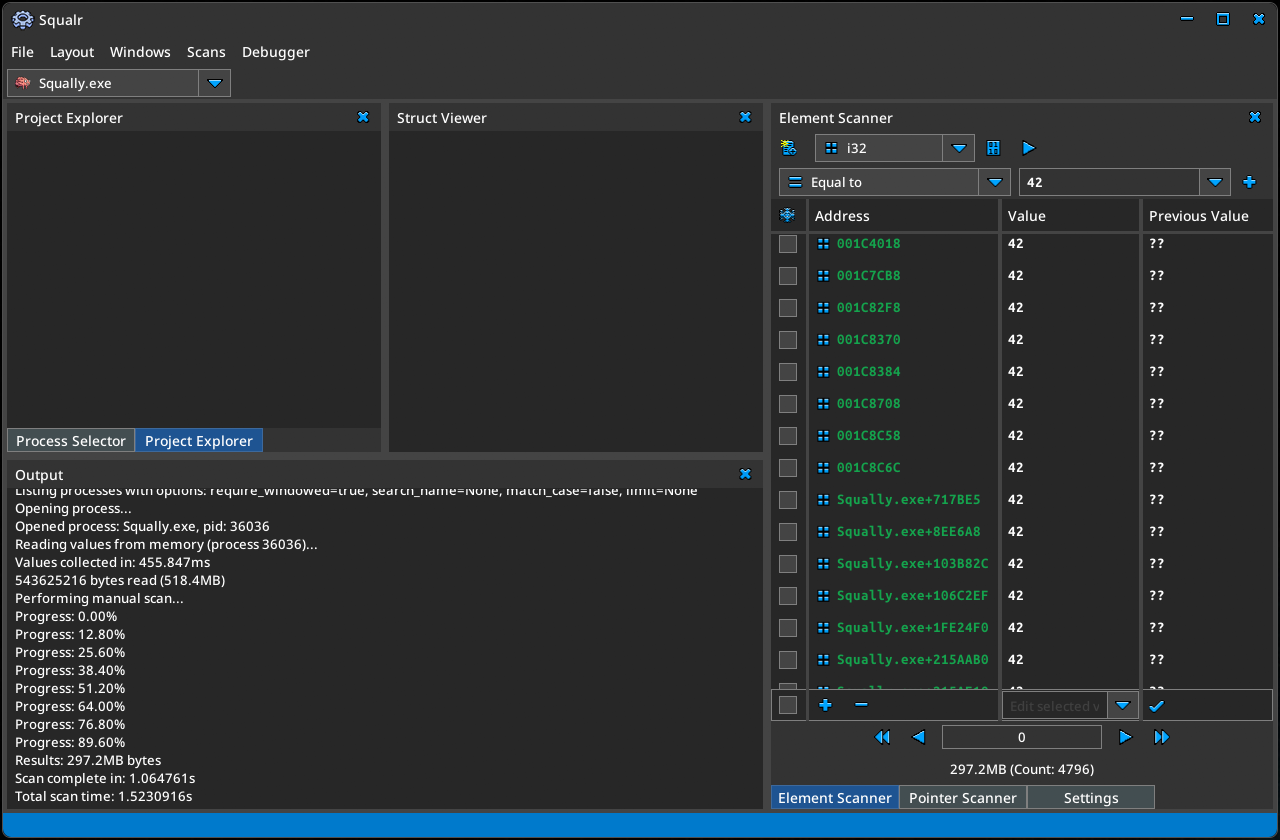 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 demining/ramnesia-attack
Scientific investigation of hardware vulnerabilities (CVE-2025-6202, CVE-2023-39910) enabling ECDSA key recovery from Bitcoin infrastructure via…
 hyhy100/chrome-skia-cve-2024-7966
PoC for a Chrome SKSL bypass + integer overflow -> OOB write vulnerability I reported to Google in Skia.
 d0rb/cve-2023-49606
Critical use-after-free vulnerability discovered in Tinyproxy
 star-laboratory/prism
PrISM: A Scalable Probabilistic RowHammer Mitigation (ISCA 2026). Ramulator2 source code and evaluation scripts.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.