The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run 11 advanced detection engines to uncover hidden payloads.
Hide encrypted data in images, audio, video, documents and executables.
Find it again, or find what someone else hid.




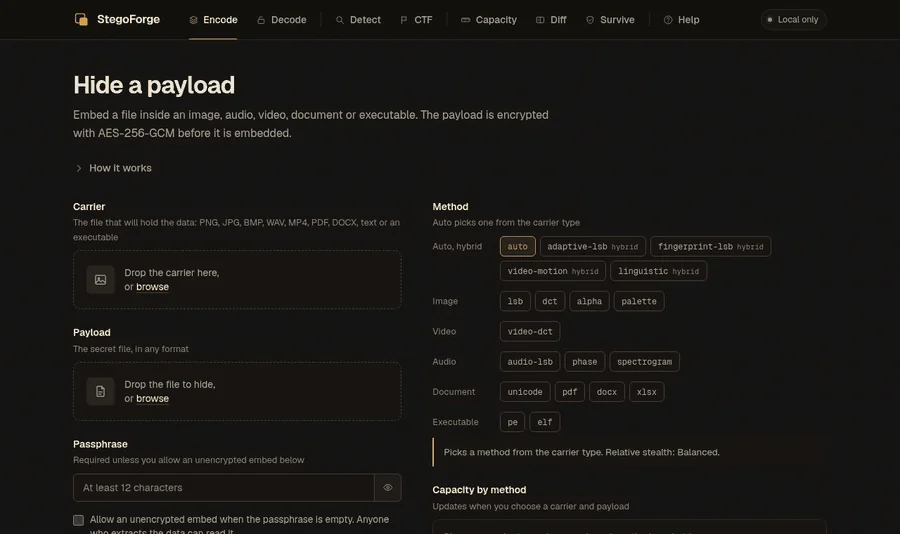
A real recording of the local web UI (stegoforge web): hide a file, extract it, run the detectors.
docs/DETECTOR-EVAL.md).--offline switches the network off entirely; StegoForge never downloads an executable or a model.--json; errors go to stderr with stable codes, so stdout stays clean for pipes.| You are on | Do this |
|---|---|
| Any OS, Python 3.10+ | pipx install stegoforge (add the browser UI with pipx install "stegoforge[web]") |
| Debian, Ubuntu, Kali | Download the .deb from Releases, then sudo apt install ./stegoforge_*_all.deb (uses your system Python libraries and installs a man page) |
| No Python, just a binary | Download stegoforge-linux-x86_64, stegoforge-macos-arm64 or stegoforge-windows-x86_64.exe from Releases |
| Docker | docker build -t stegoforge . then docker run -p 5000:5000 stegoforge (the UI is token-protected; the token is in docker logs) |
| From source | git clone https://github.com/Nour833/StegoForge && cd StegoForge && pip install -e ".[web]" |
Then check the installation:
$ stegoforge doctor
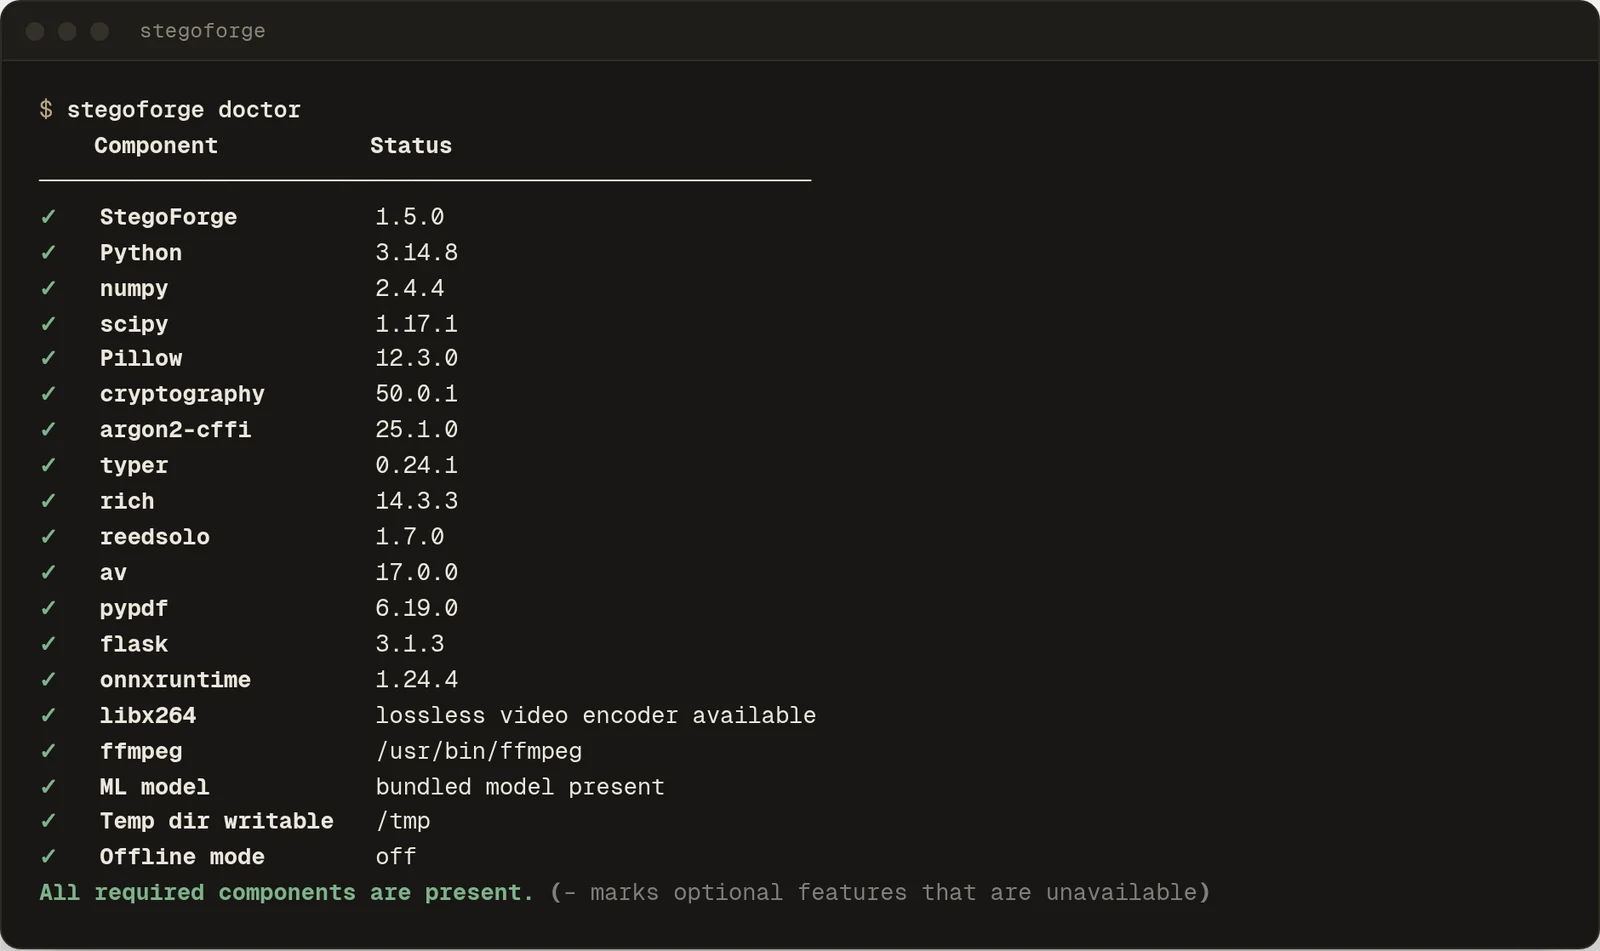
doctor lists what this machine can and cannot do (video support, FFmpeg for MP3/FLAC/OGG, the bundled ML model) and never touches the network.
Python 3.10: it works, but Pillow's image-decoder fixes (24 advisories in 12.3.0, patched in 13.0.0) need Python 3.11 or newer. Use Python 3.11+ when you analyse files you do not trust.
# Keep the passphrase out of your shell history and `ps` (a plain -k works, with a warning)
export STEGOFORGE_KEY="a long passphrase, not a short one"

stegoforge encode -c photo.png -p secret.txt        # method picked from the carrier type
stegoforge decode -f photo_stego.png                # -> photo_decoded.txt

stegoforge capacity -c photo.png --depth 2          # how much fits, and how stealthy each method is
stegoforge diff -c photo.png -s photo_stego.png     # heatmap of exactly which pixels changed
stegoforge detect -f photo_stego.png                # run the detectors on a file
stegoforge ctf -f challenge.png                     # every detector + extraction, one ranked report

# Will it survive an upload? Simulates the platform's recompression locally and tries to extract.
stegoforge encode -c photo.png -p secret.txt --target twitter --test-survival

# The same secret into every carrier in a folder
stegoforge batch -d ./carriers -p secret.txt --jobs 4

stegoforge web                                      # the local web UI on http://localhost:5000
An unencrypted payload (
--allow-plaintext) is refused unless you ask for it. That is on purpose: without a key the embedded bytes are readable by anyone who extracts them, and the CTF scene in the recording above shows how easily that happens.
Run stegoforge with no arguments for a guided menu (it opens with the boot screen above). STEGOFORGE_FAST_UI=1 skips the animation for instant starts, and STEGOFORGE_UI_STAGE_DELAY=0.4 tunes its pacing.
| Carrier | Methods | Good to know |
|---|---|---|
| PNG, BMP, TIFF, WebP | lsb, adaptive-lsb, fingerprint-lsb, alpha | Pixel LSBs are destroyed by lossy re-compression. adaptive-lsb writes into busy pixels first, which disturbs statistics less; fingerprint-lsb is camera-noise aware |
| JPEG | dct | Works in the frequency domain and keeps the output a JPEG. In the local survive simulation (1200×780 photo, 50 B payload) it survived 7 of 10 platform profiles; JPEG quality of about 80 and below (WhatsApp, Facebook, TikTok) destroyed it |
| GIF, indexed PNG | palette | A few bytes of capacity: too small for an encrypted payload (the envelope alone is 50 bytes) |
| WAV, FLAC, MP3, OGG | audio-lsb, phase, spectrogram | Output is WAV. spectrogram is a visual watermark, not a byte channel. MP3/FLAC/OGG input needs FFmpeg |
| MP4, WebM | video-dct, video-motion | Written as lossless H.264: files are large, play in ffmpeg-based players (VLC, mpv) rather than most browsers, and any later re-encode destroys the payload. Audio is kept. The encoder verifies its own output |
| TXT, PDF, DOCX, XLSX | unicode, linguistic, pdf, docx, xlsx | Zero-width characters, synonym substitution, or data the viewer ignores |
| ELF, PE (EXE, DLL) | elf, pe | Slack space; a stego'd binary still runs, but a signed PE loses its signature |
| Network traces | tcp-covert, timing-covert | Experimental: trace-file mode, or live send/capture with root and an explicit acknowledgement |
Every method, its capacity formula and what it survives is in docs/METHODS.md.