
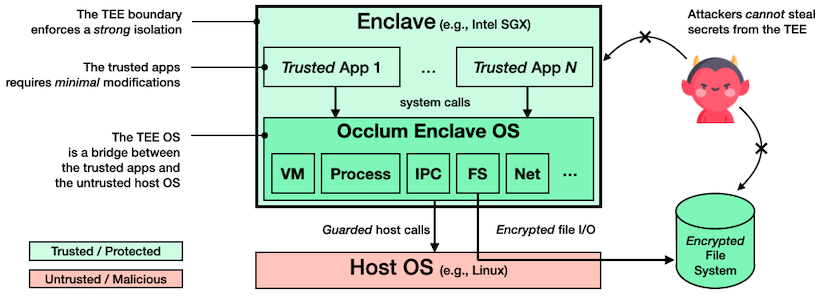
occlum
 occlum/occlum
Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
cloud-infrastructure-securitycloud-securitycryptography+5
1.5k
occlum/occlumMemory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 abraxas/php-oom-longjmp
PHP 8.4.26 - Critical - Remote - OOM longjmp - CVE-2026-109618 PHP2Shell. Unauth chunked multipart hits memory_limit before app code on Apache…
 abraxas/php-stale-global-uaf
PHP 8.5.11 - Critical - Remote - UAF - CVE-2026-109619 PHP2Shell. Same-worker fatal backtrace then INI diagnostic on Apache mod_php. Lab vs 8.5.12.…
 eqstlab/cve-2026-109619
Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…
 1llu50ry/mcp-gamehacking
MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
 r3n3r0/cve-2026-0006-step-2
Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
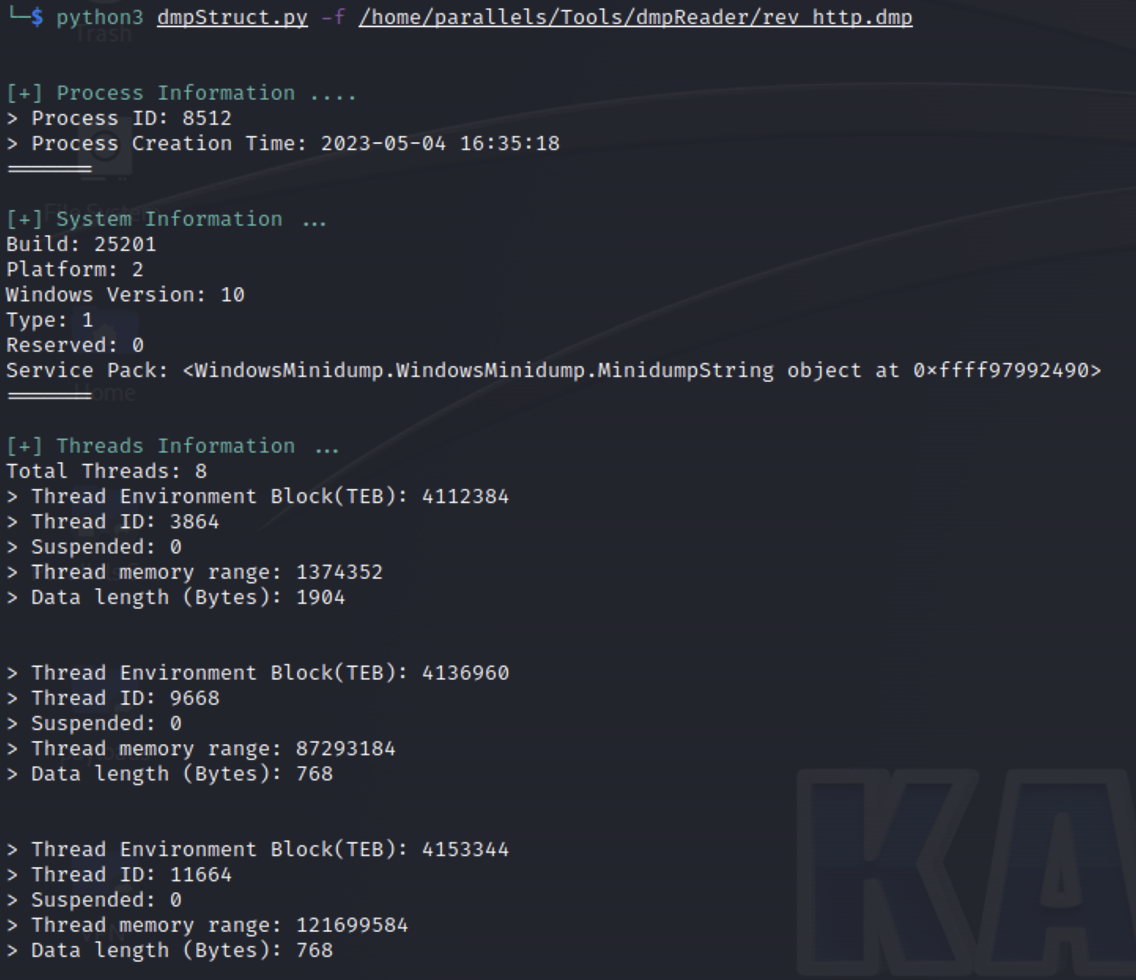 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
 0xblackash/cve-2026-110912
Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
 imeiplus/cve-2026-23111-poc
Working local privilege escalation exploit for CVE-2026-23111, a use-after-free in the Linux kernel nf_tables subsystem, with KASLR bypass and ROP…
 mein-0/gvcidrv64
Proof-of-concept exploit for Gigabyte's GVCIDrv64.sys kernel driver, achieving local privilege escalation via arbitrary physical memory and I/O port…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…