

fibratus
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
defensive-toolsforensicsincident-response+3
rabbitstack/fibratusSecurity sensor for realtime threat detection and protection
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
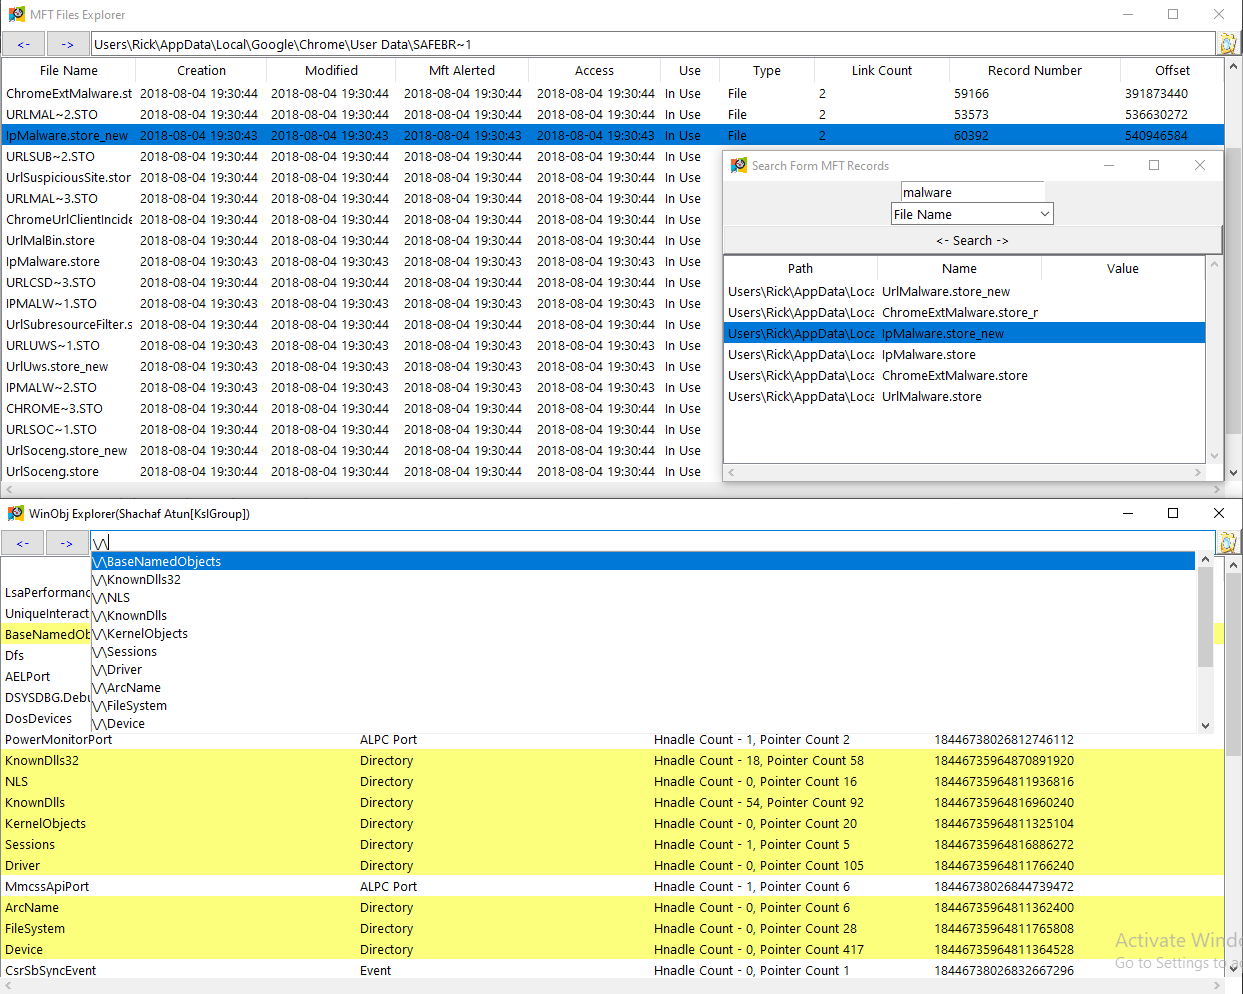 memoryforensics1/volexp
volatility explorer (volatility 2)
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
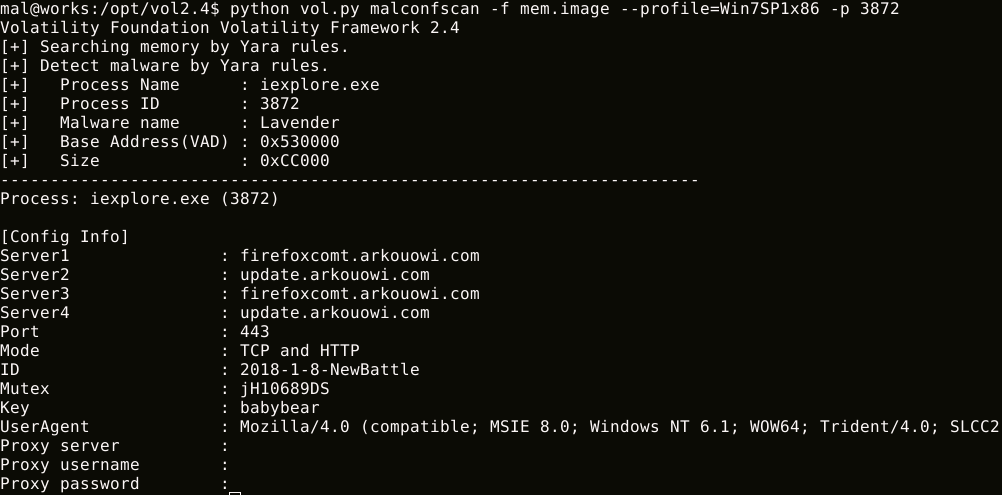 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
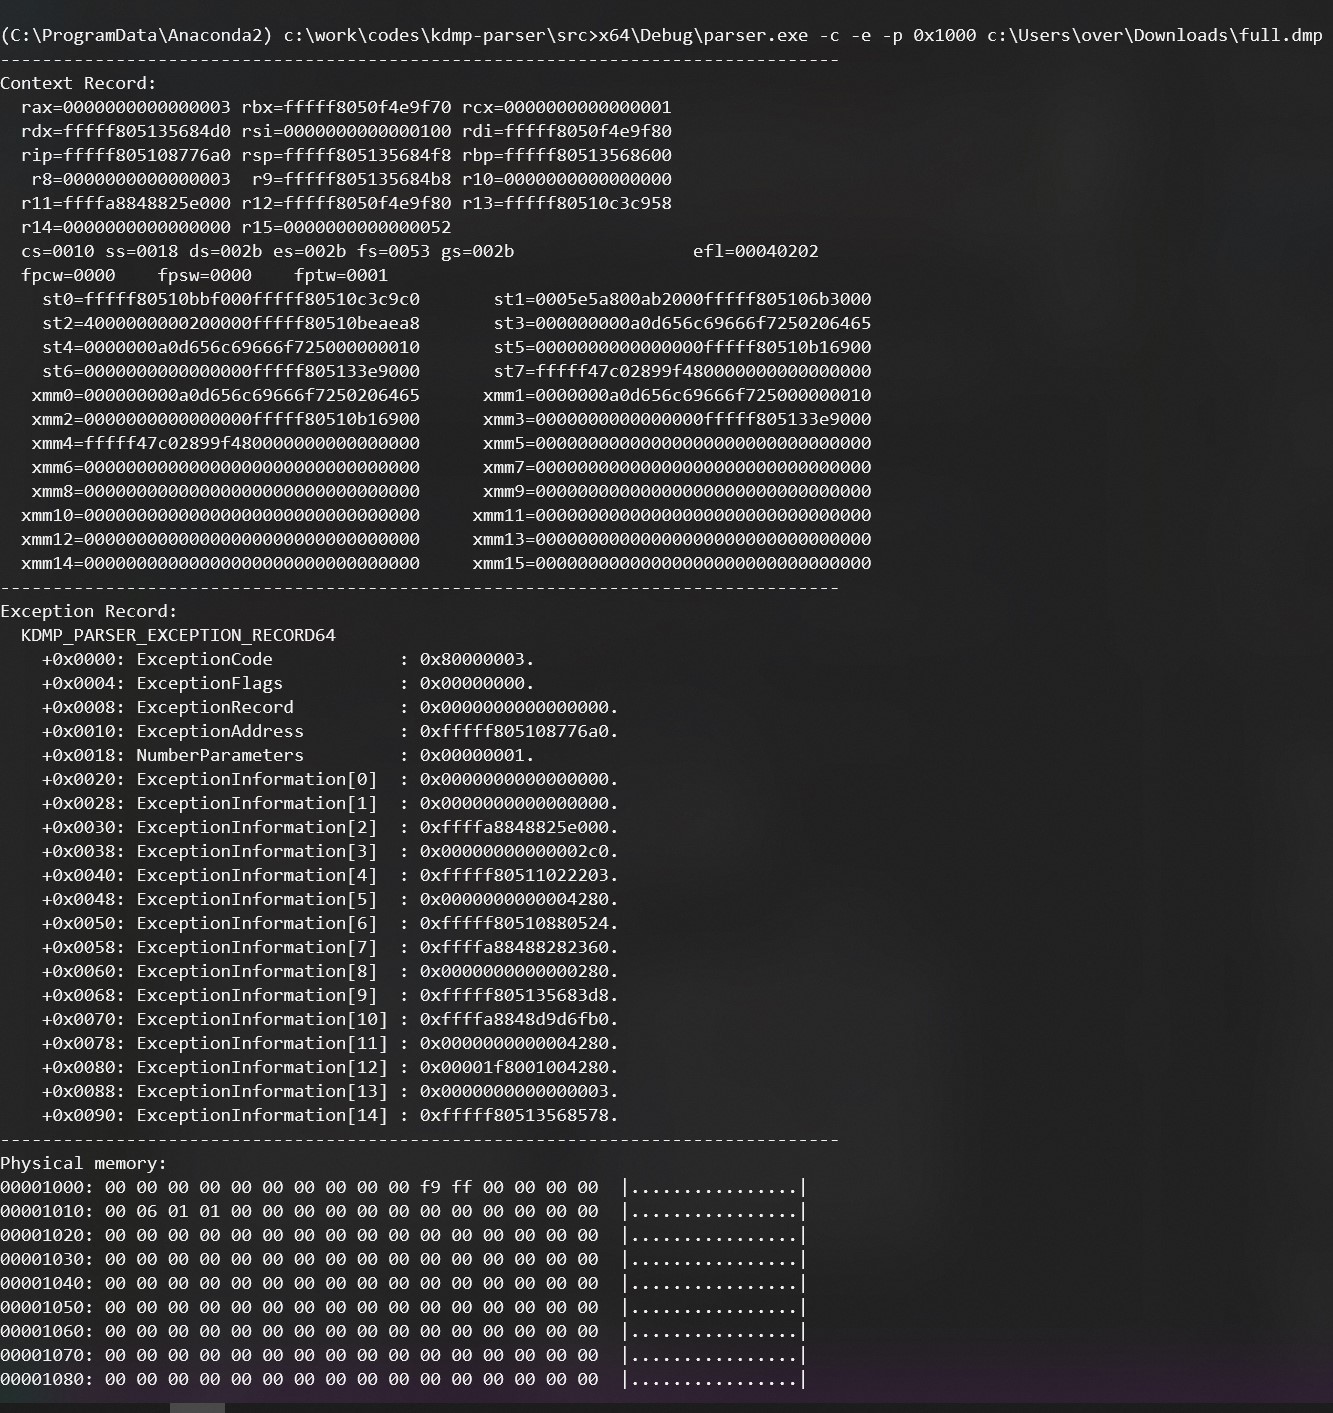 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
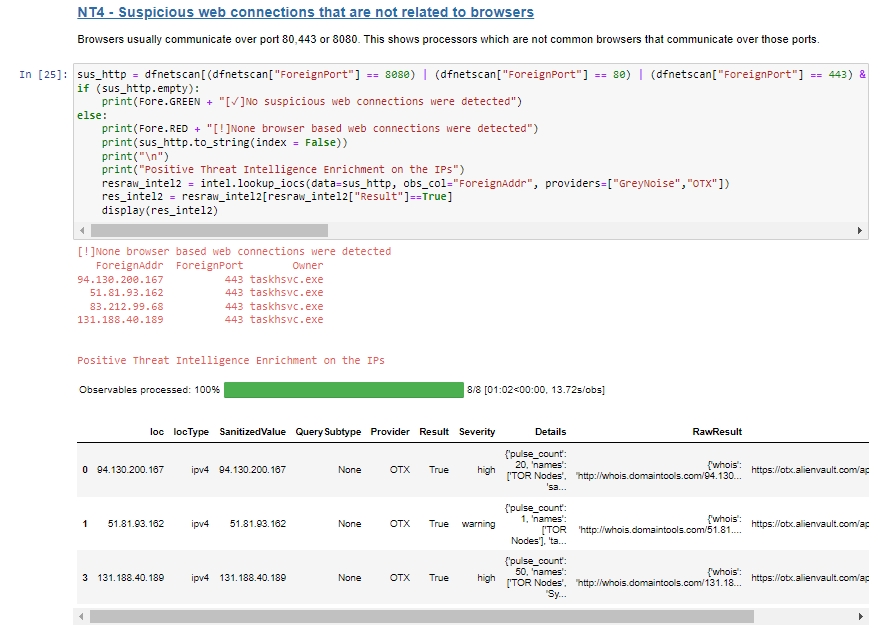 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.