

 blendin/3snake
Tool for extracting information from newly spawned processes
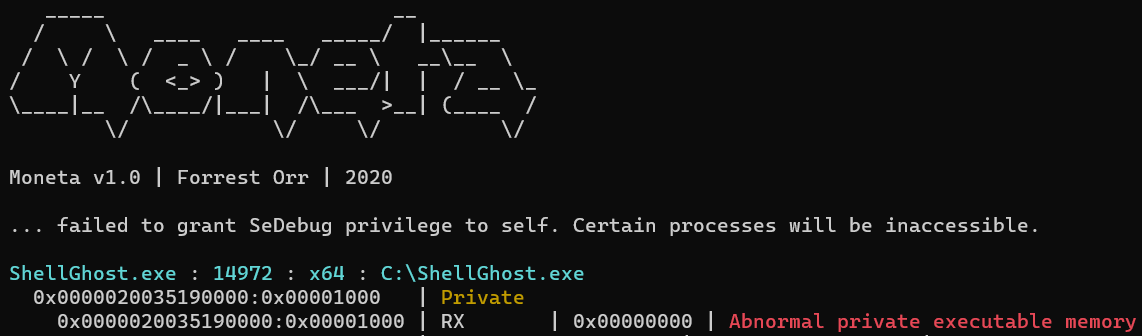 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
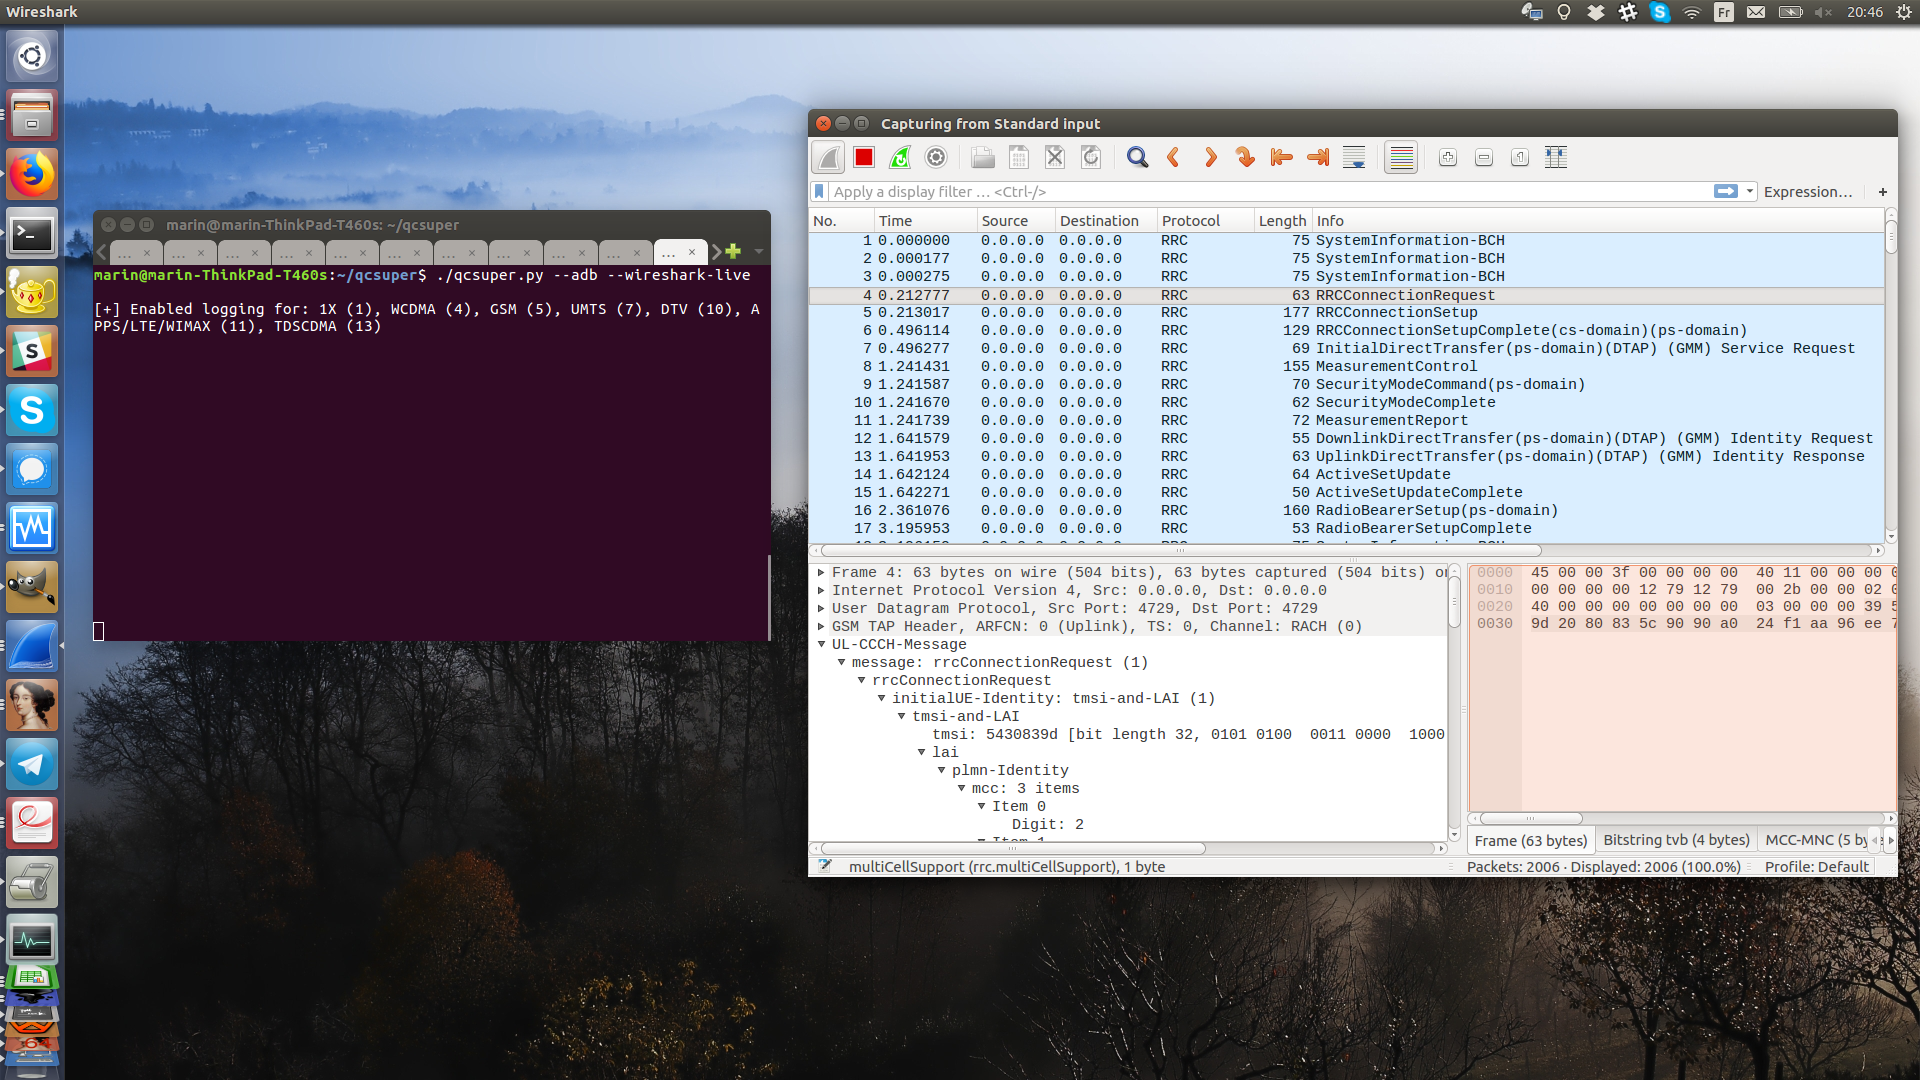 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
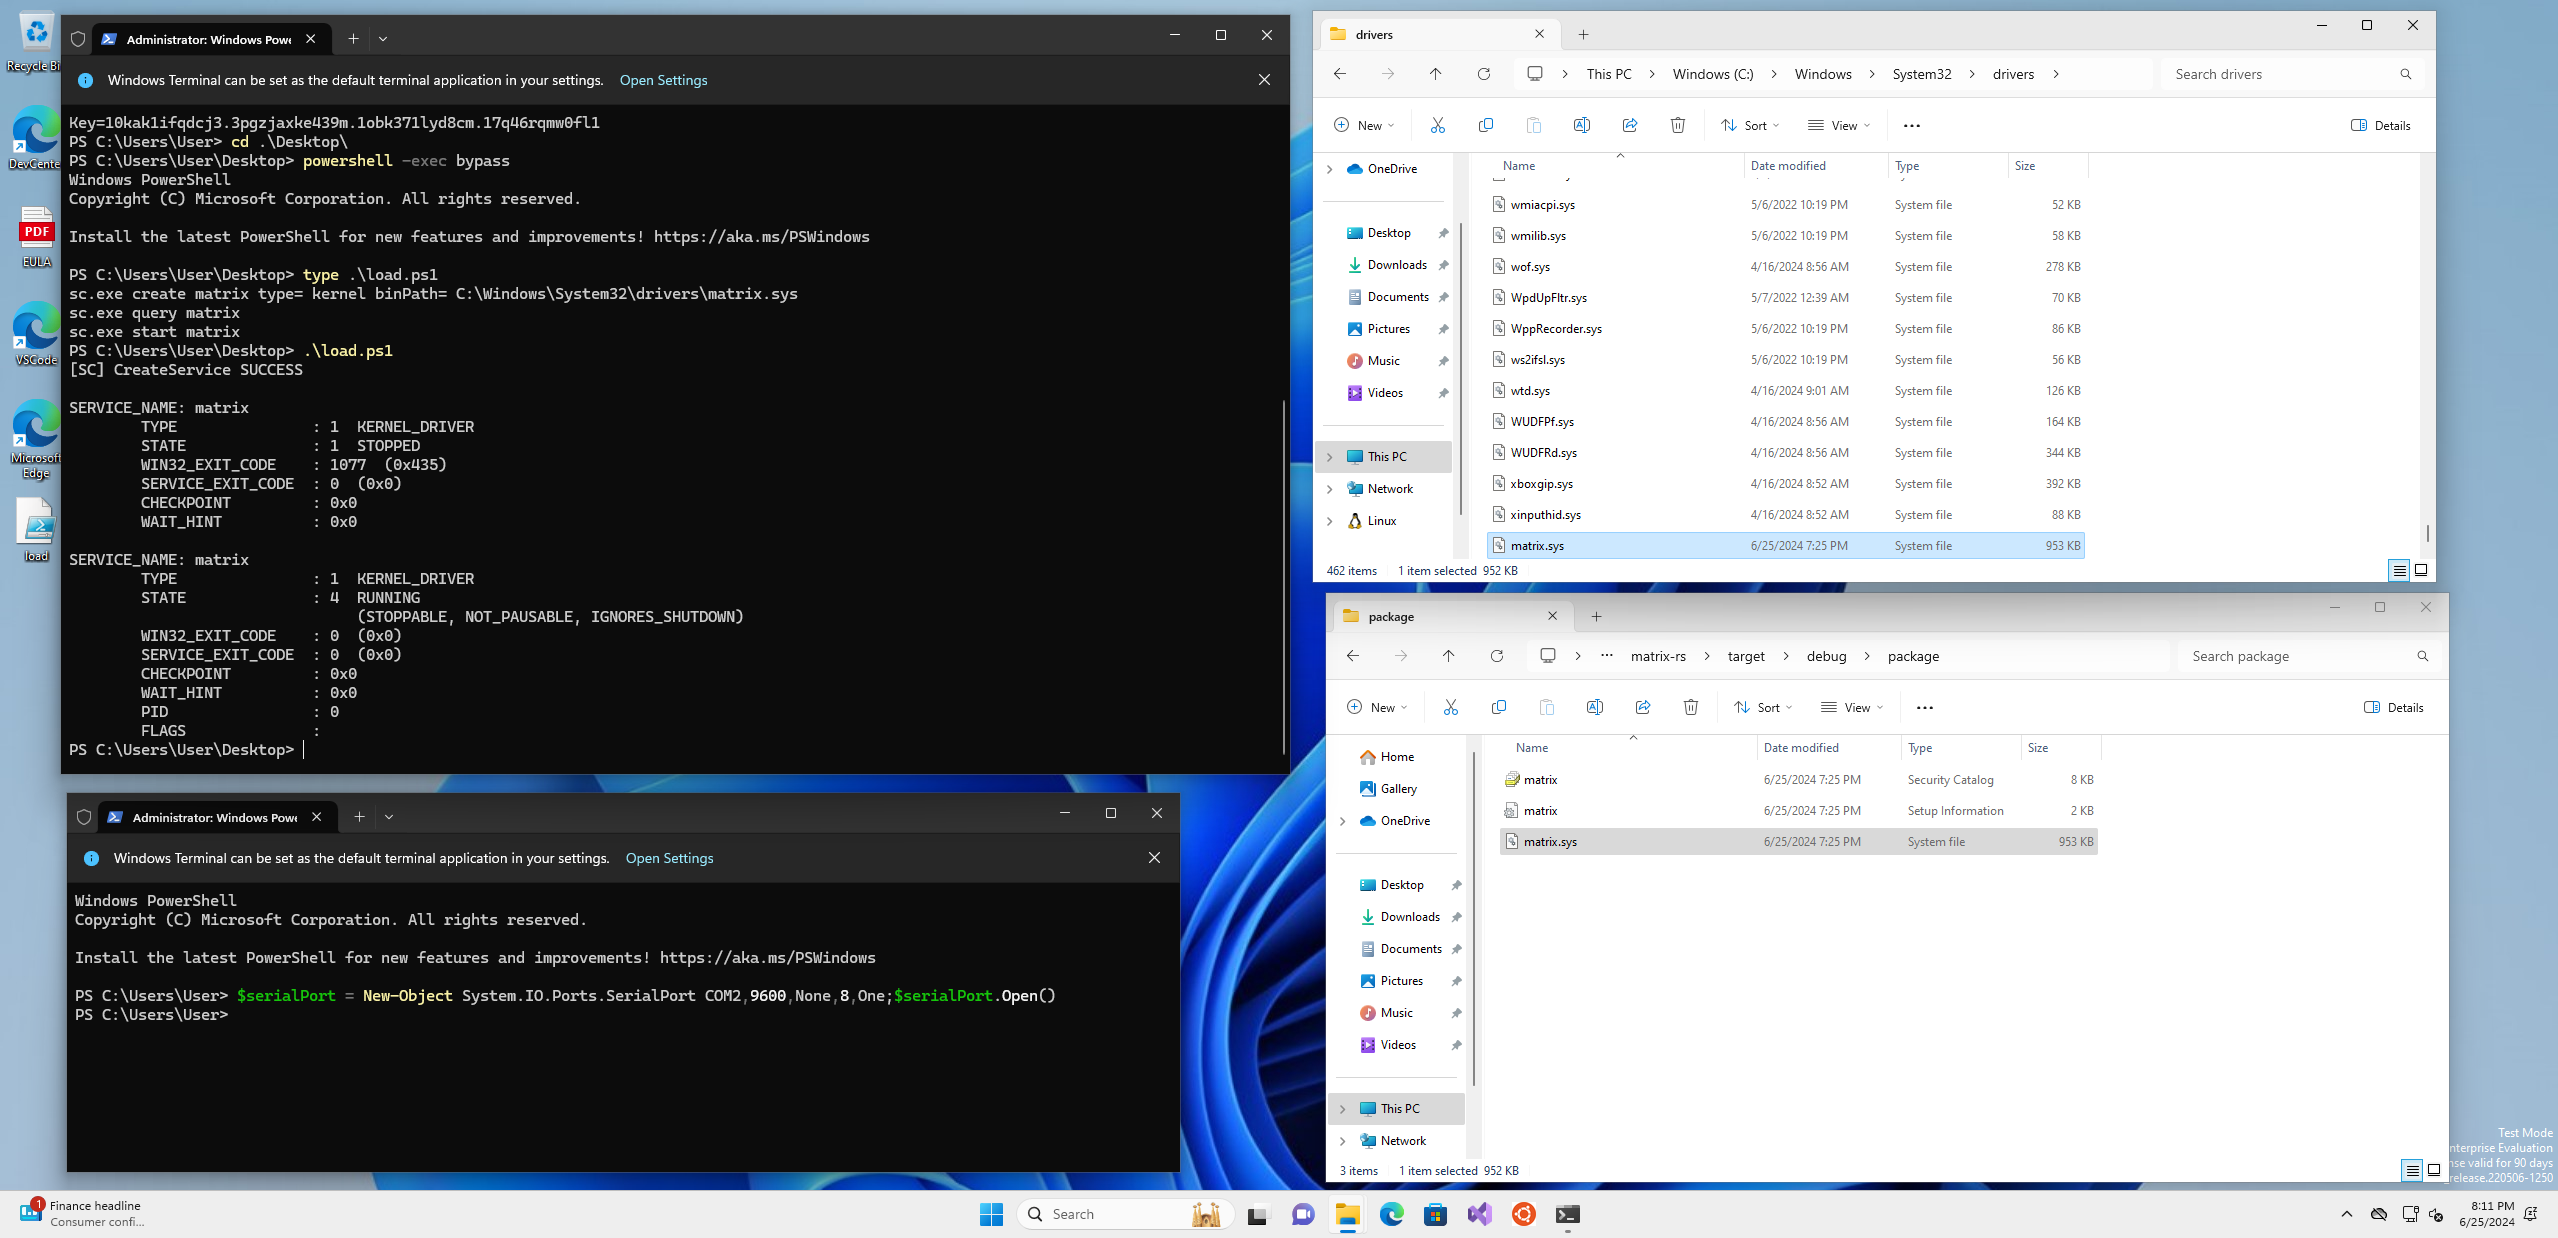 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 var77/cve-2026-2005
PoC for CVE-2026-2005
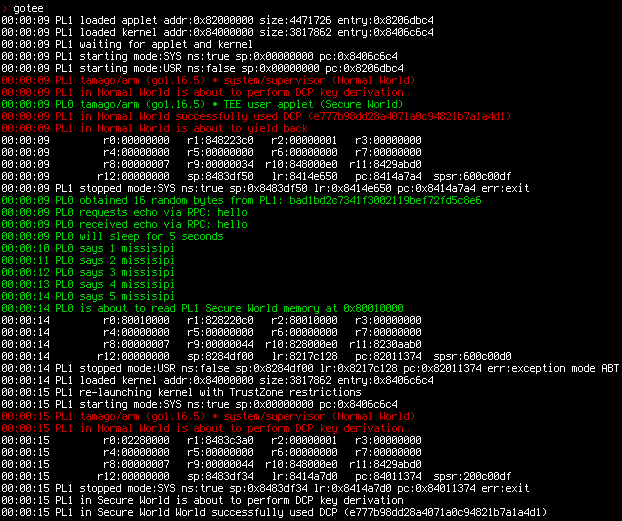 usbarmory/gotee-example
GoTEE - example application
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
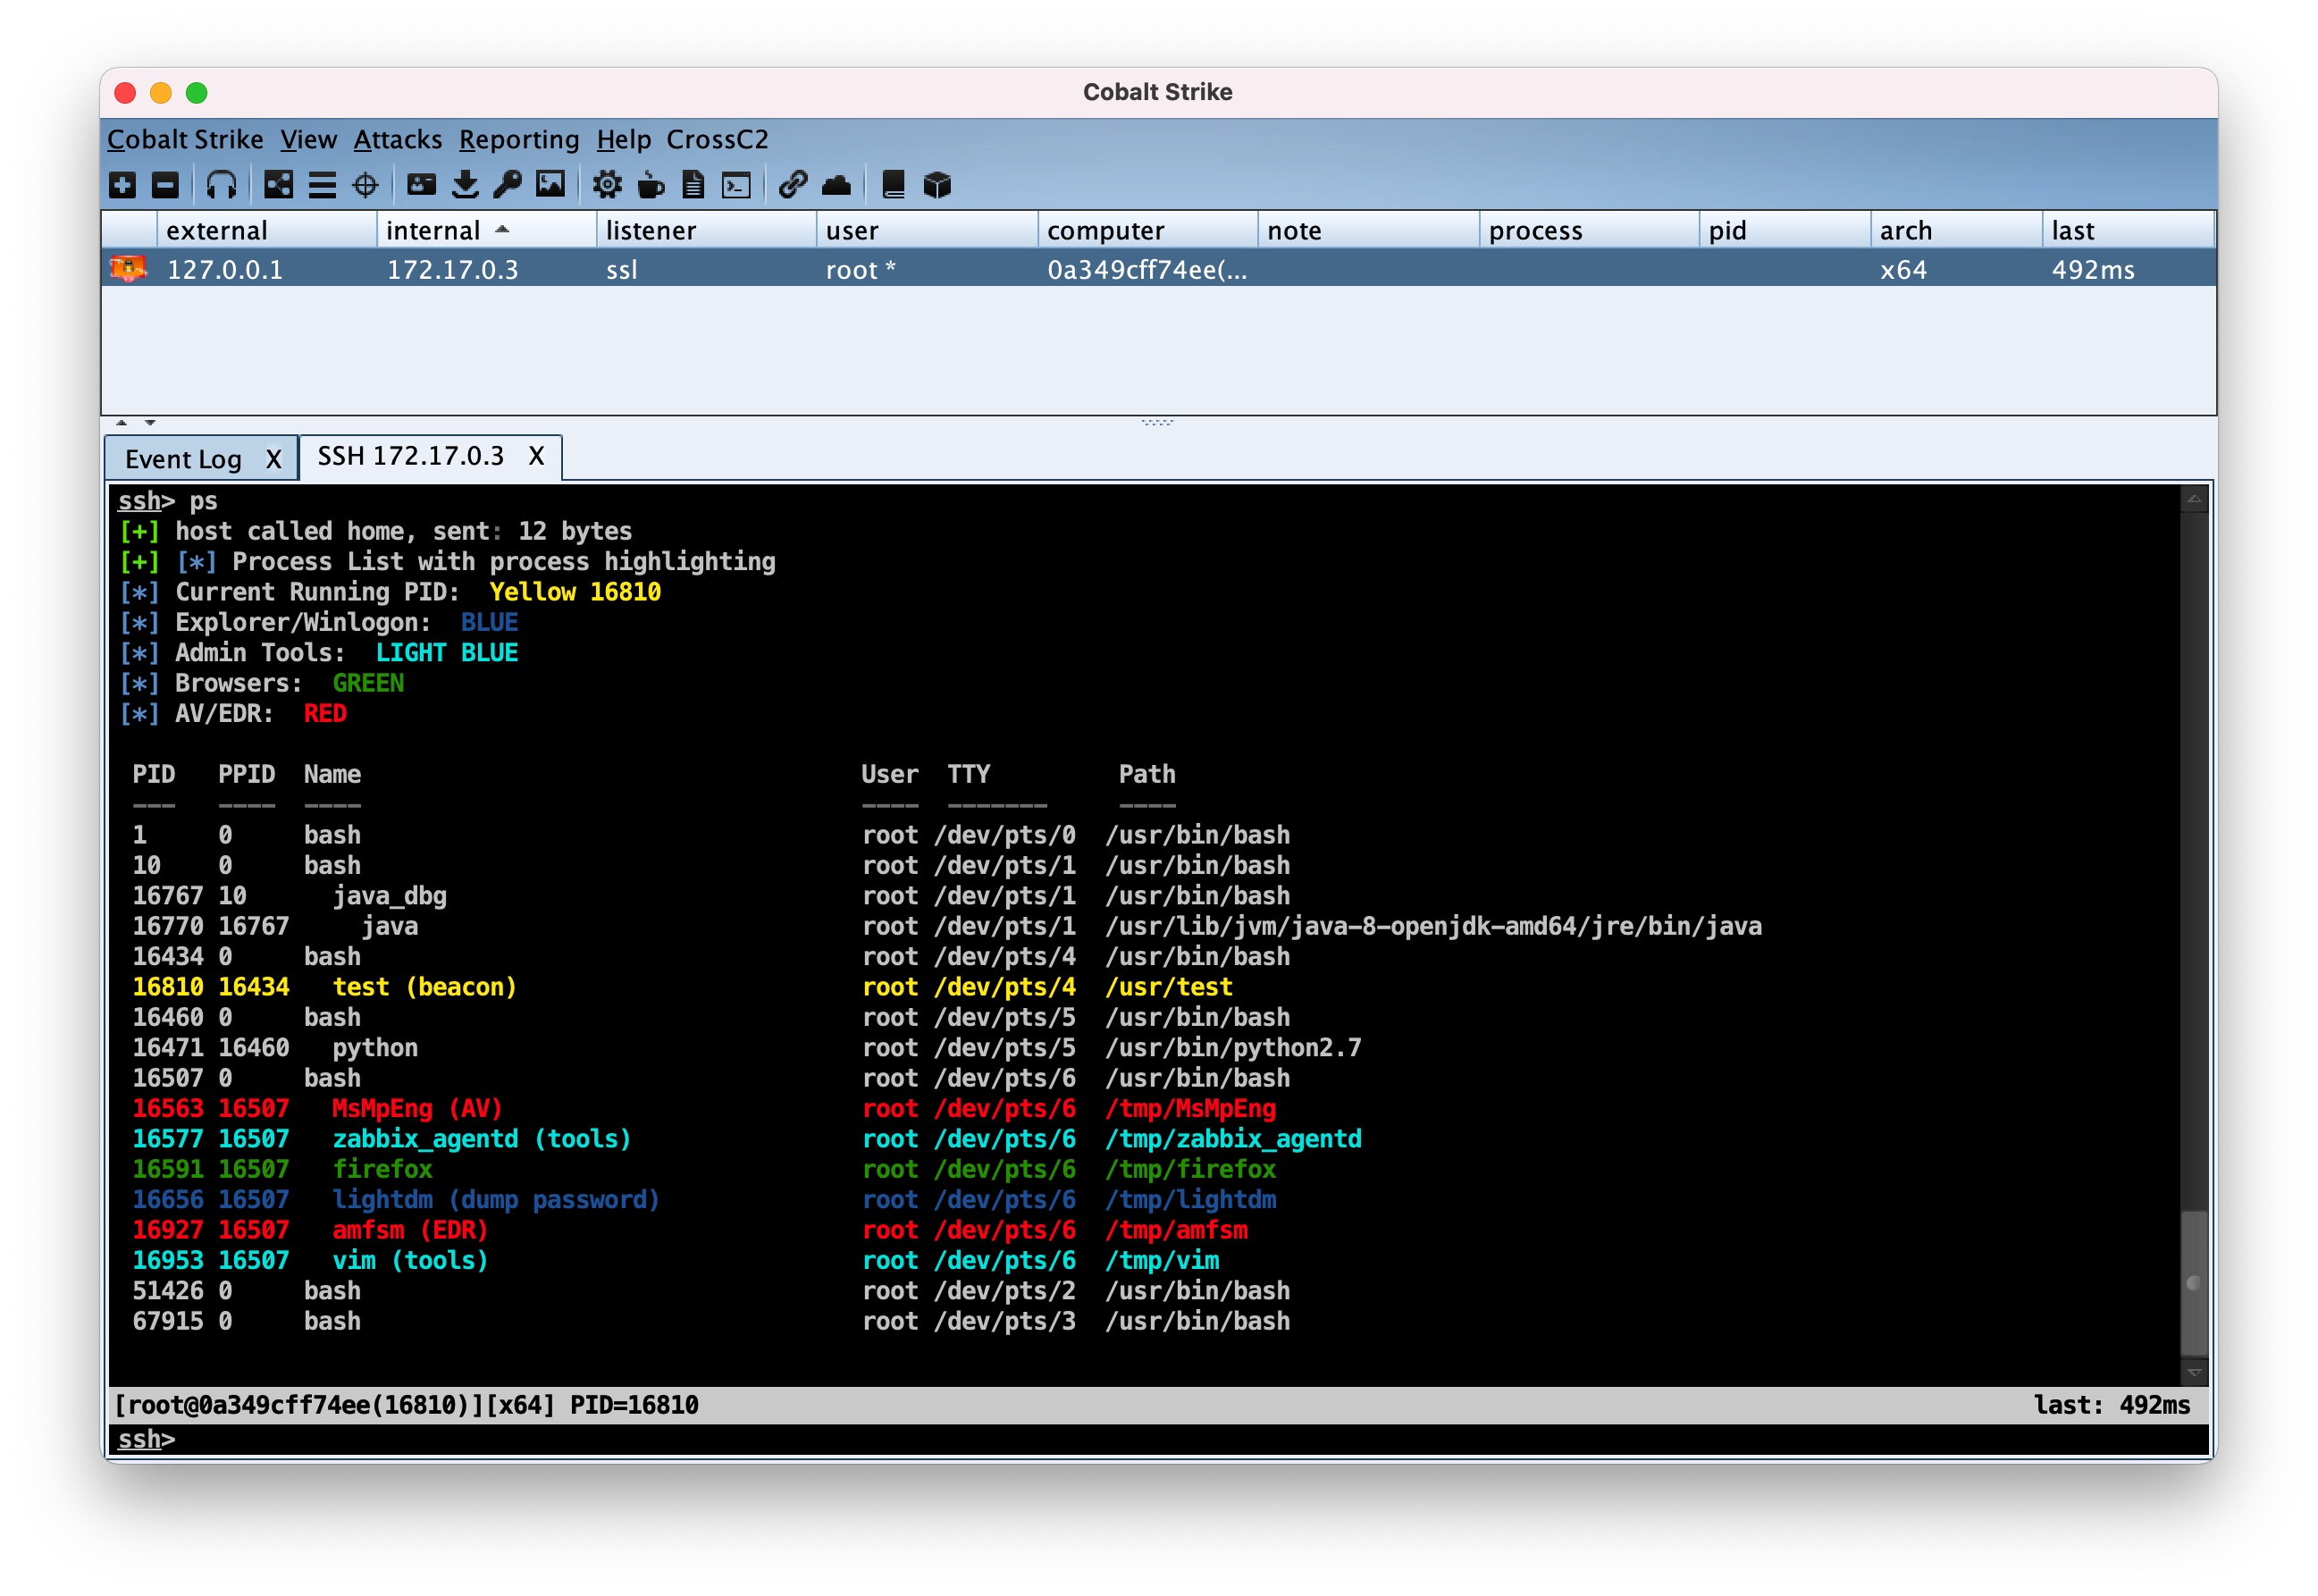 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…