

wafaray
 alt3kx/wafaray
Enhance your malware detection with WAF + YARA (WAFARAY)
defensive-toolslabs-practicemalware-analysis+4
alt3kx/wafarayEnhance your malware detection with WAF + YARA (WAFARAY)
 dhmosfunk/7-zip-cve-2025-0411-poc
This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
 sparshbiswas-ai/cve-2026-0596-reproduction
Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.
 an0nud4y/av-edr-lab-environment-setup
AV/EDR Lab environment setup references to help in Malware development
 zedocun/soc-investigation-powershell-edrfreeze
SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
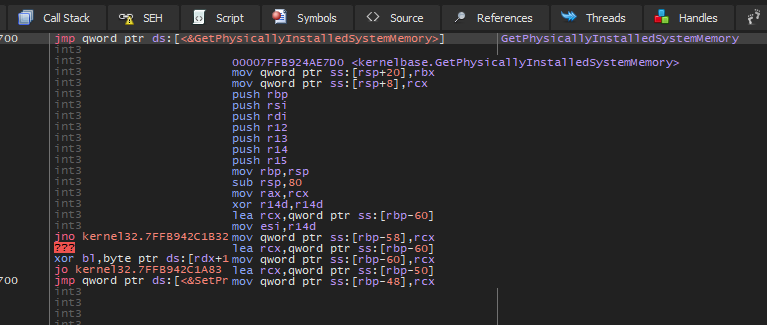 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 hackpatato/cve-2026-33057---mesop-unauthenticated-rce-poc-and-yara-rules
Proof-of-concept exploit for CVE-2026-33057, an unauthenticated RCE in Mesop, with accompanying YARA rules for detection.
 gracenolan/notes
Curated study notes and interview preparation guide for security engineering roles, covering networking, web security, cryptography, malware…

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
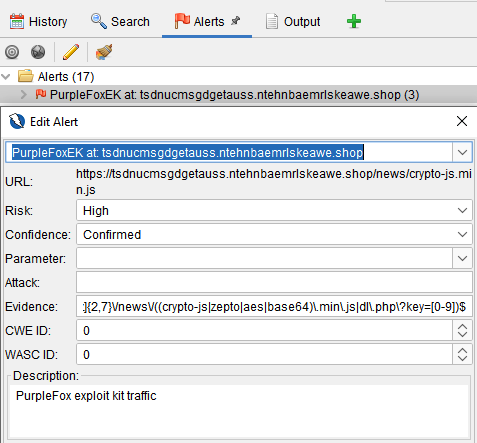 malwareinfosec/fiddlezap
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
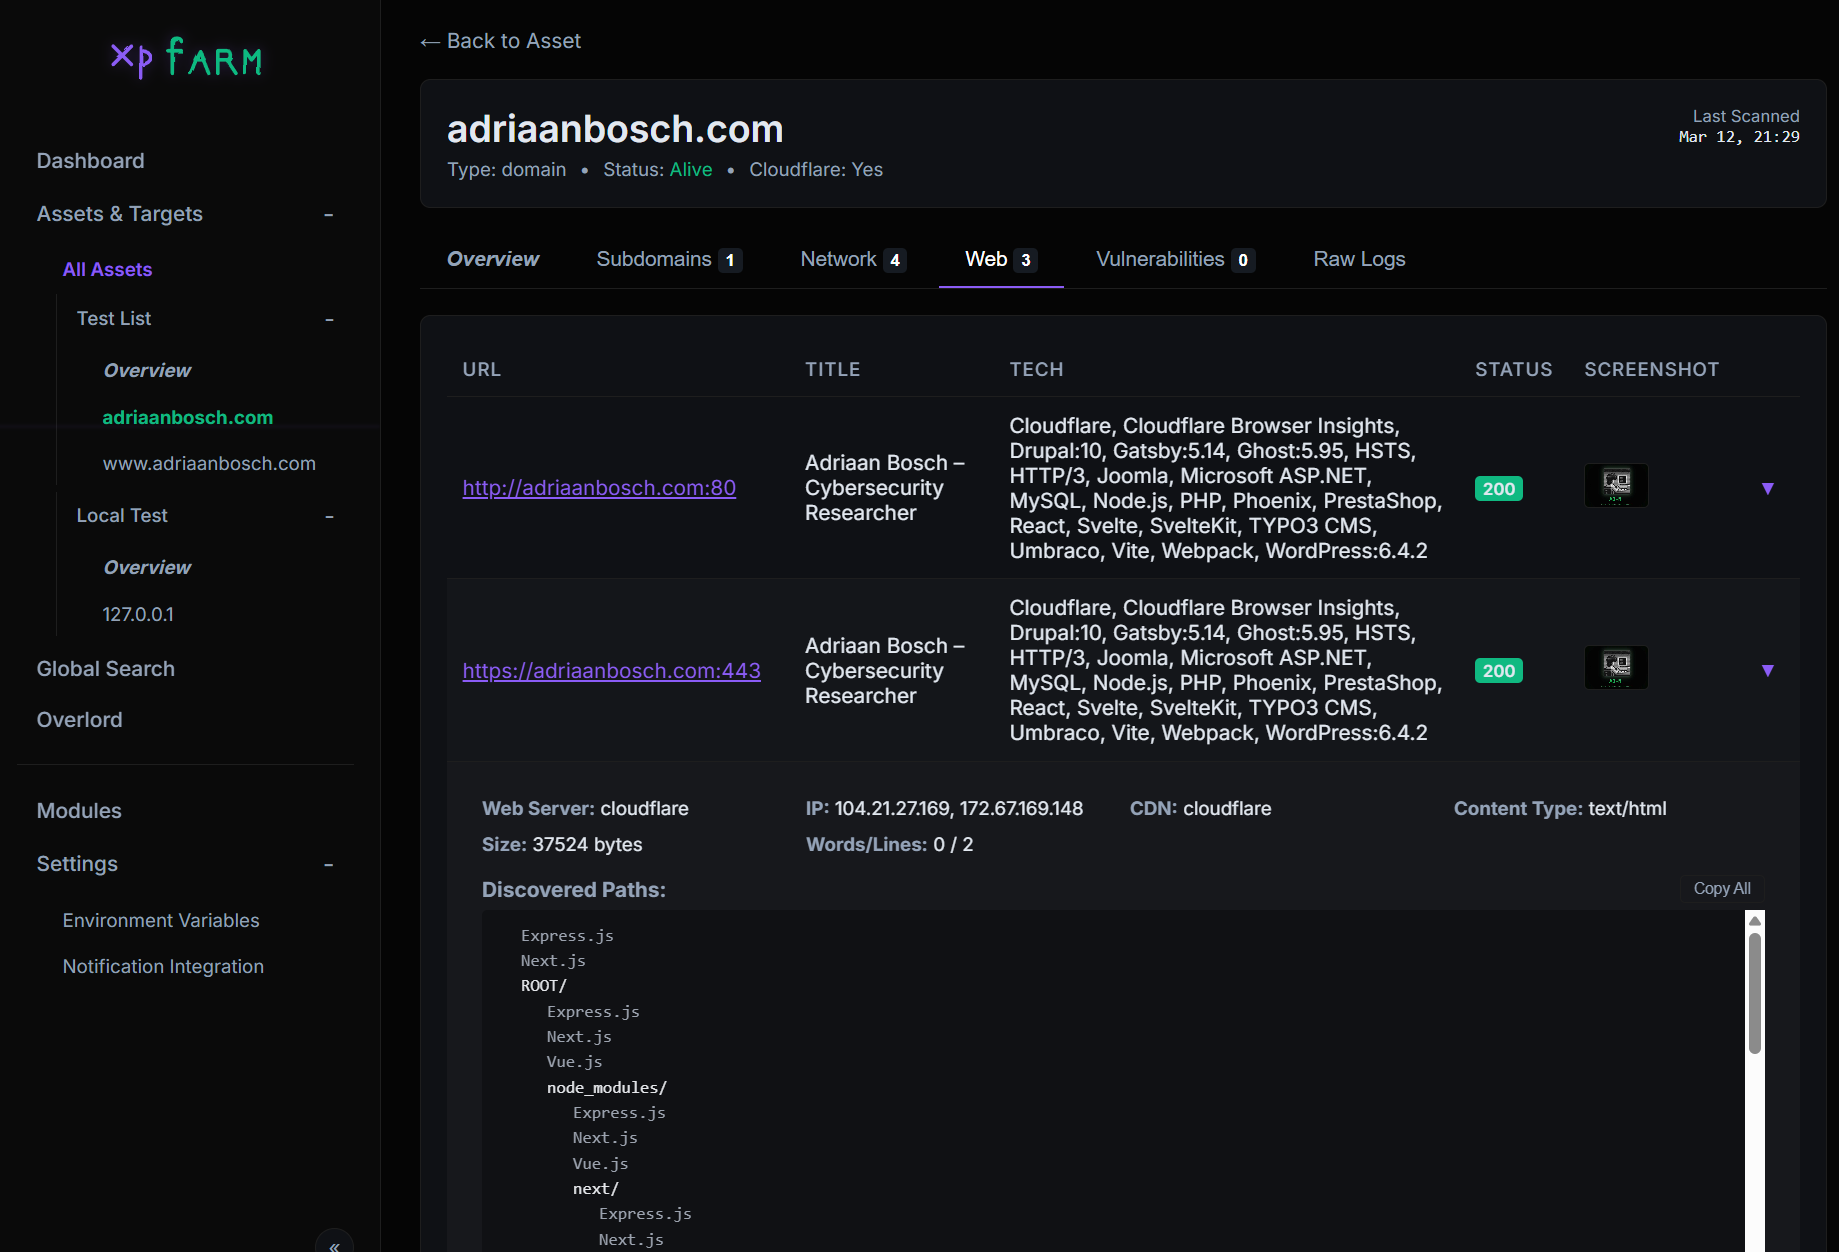 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 dissectmalware/yaradbg-frontend
Web-based Yara rule debugger with an editor, live match evaluation, matched-string details, and rule dependency visualization for detection…