
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
736 results
halogen preview
Archived

halogen

GitHubtarget/halogen

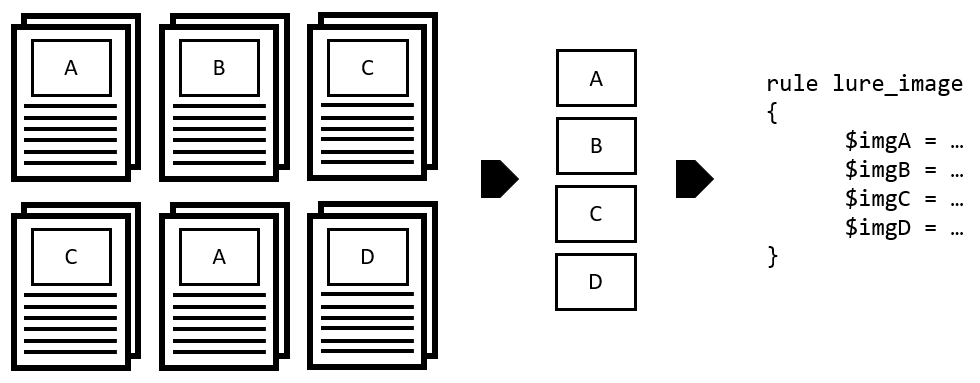
Automatically create YARA rules from malicious documents.

forensicsincident-responsemalware-analysis+2
210
4 years ago
Pesidious preview

Pesidious

GitHubcyberforce/pesidious

Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks

adversarial-attackai-securityexploitation+3
1745 years ago
certReport preview

certReport

GitHubsquiblydoo/certreport

A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.
hash-analysismalware-analysisthreat-intelligence
405 months ago
pisc preview

pisc

GitHubecomtech-oss/pisc

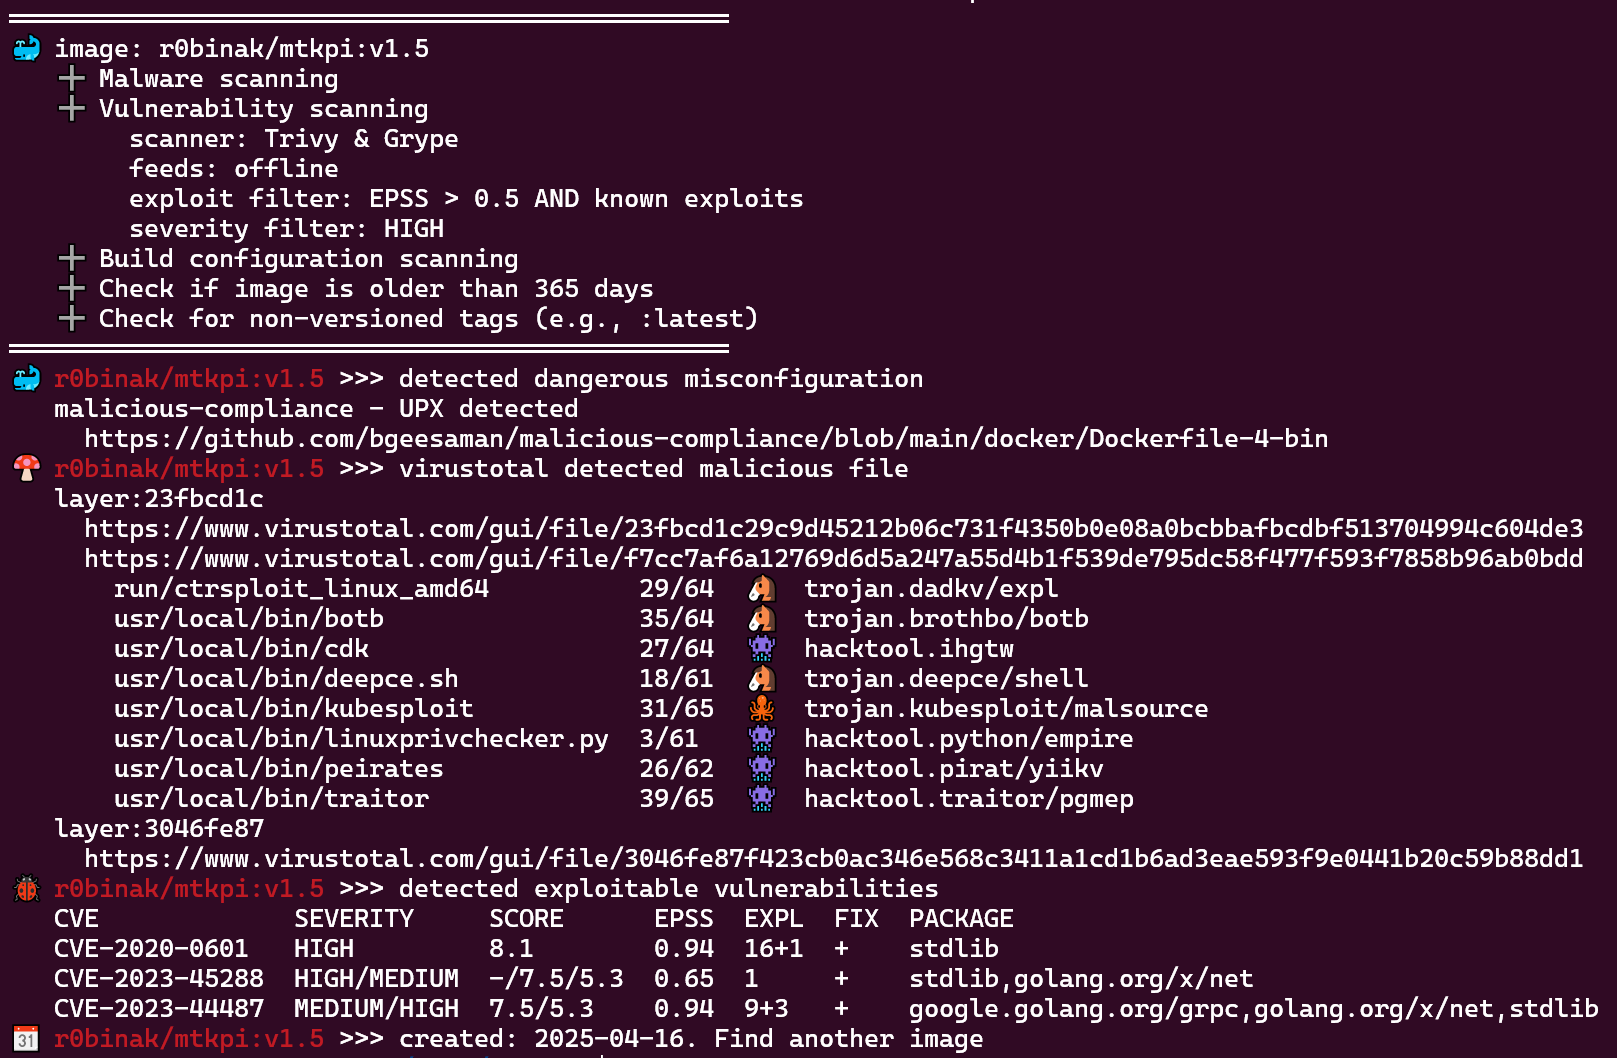
Public OCI-Image (docker image) Security Checker
container-securitydevsecopsmalware-analysis+3
217 months ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

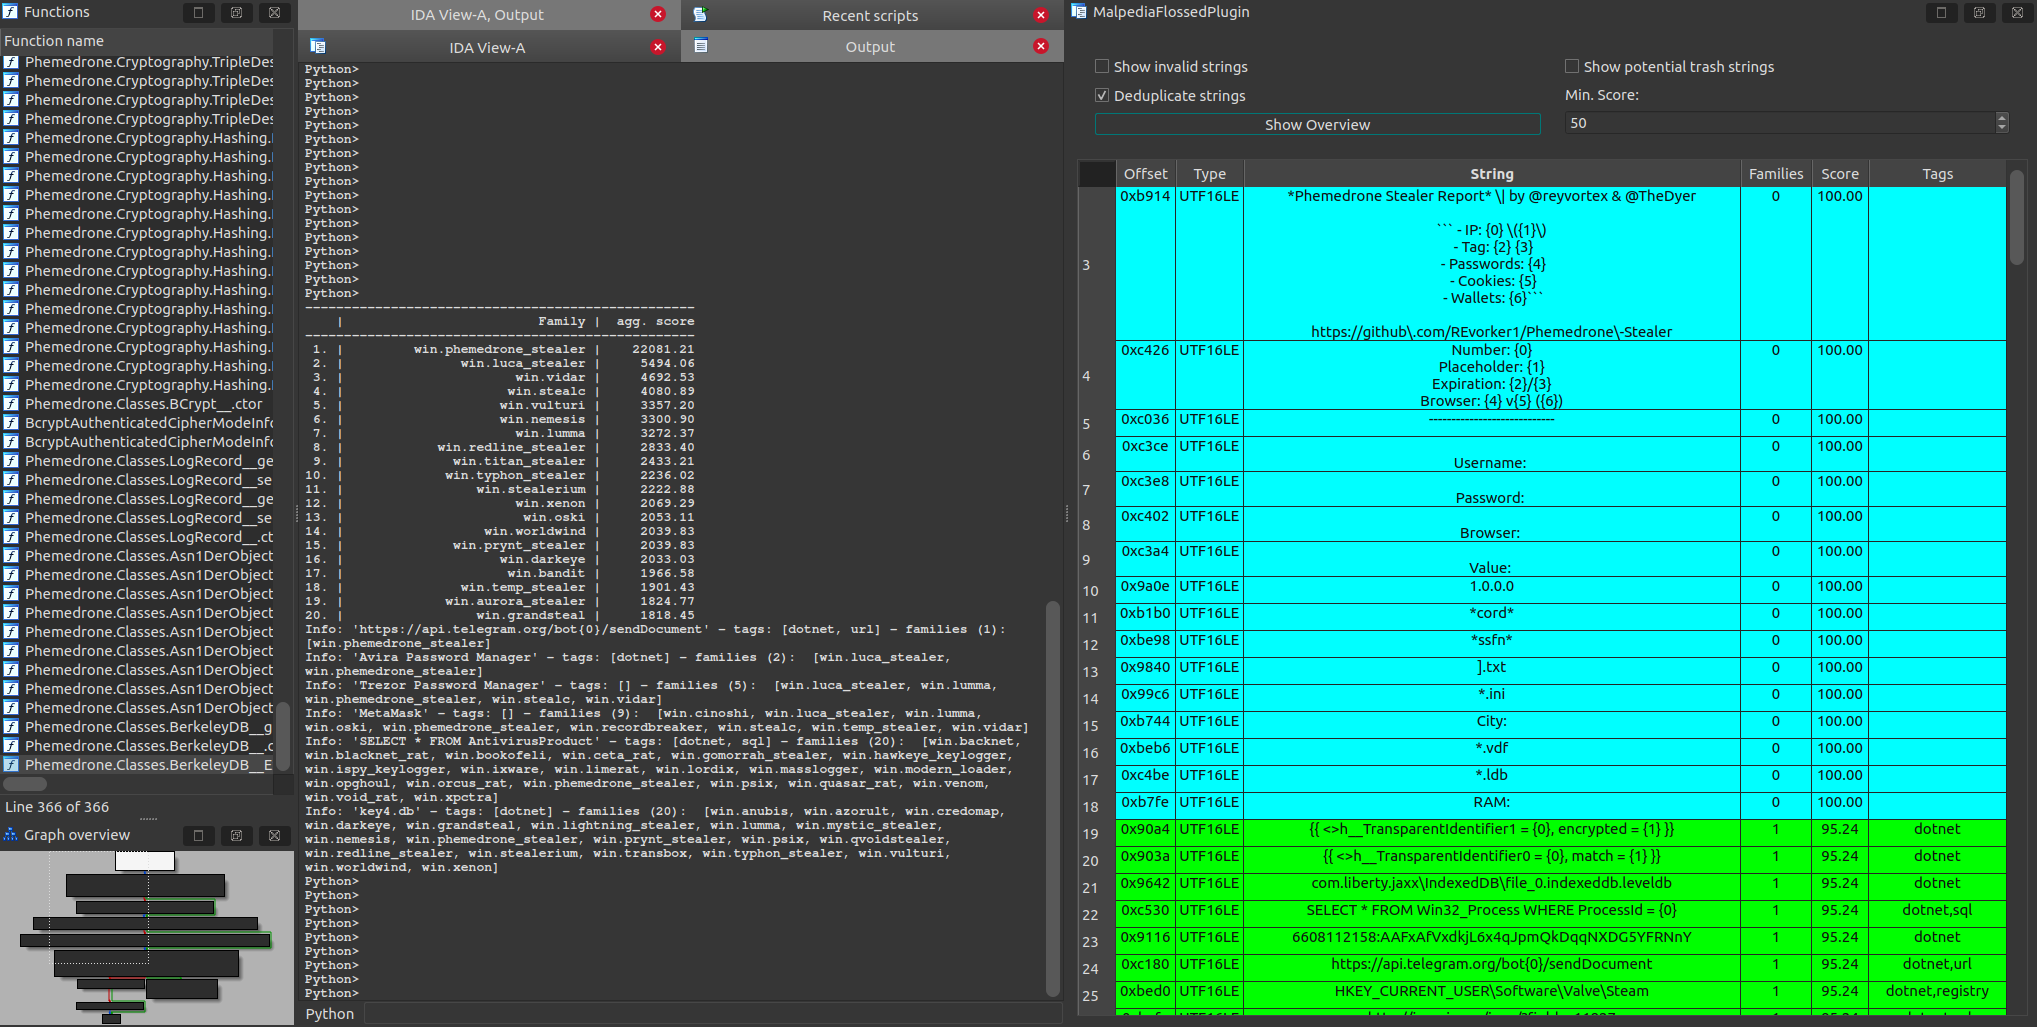
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
838 months ago
RansomLord preview

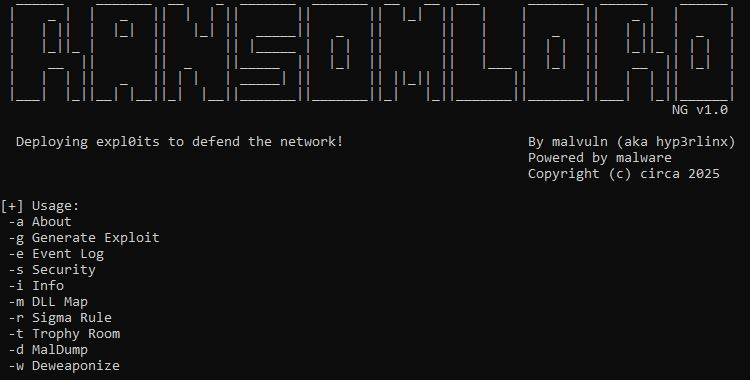
RansomLord

GitHubmalvuln/ransomlord

RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
5151 year ago
buttinsky preview

buttinsky

GitHubmushorg/buttinsky

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
information-gatheringintrusion-detectionmalware-analysis+2
8213 years ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4463 years ago
Jasmin-Ransomware preview

Jasmin-Ransomware

GitHubcodesiddhant/jasmin-ransomware

Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
command-and-controlencryption-decryption-toolsexploitation+5
2875 years ago
chepy preview

chepy

GitHubsecurisec/chepy

Chepy is a python lib/cli equivalent of the awesome CyberChef tool.

cryptographyctfforensics+2
1.1k4 months ago
apkinspector preview

apkinspector

GitHubhoneynet/apkinspector

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
android-securitybinary-analysiscode-analysis+7
85213 years ago
EXOCET-AV-Evasion preview

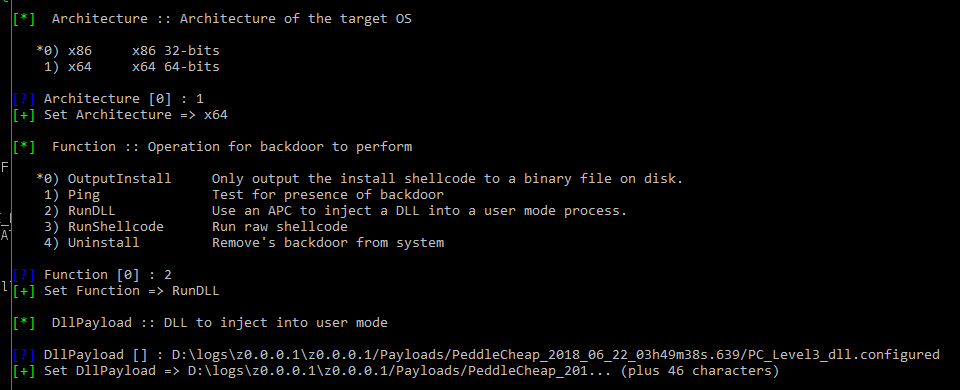
EXOCET-AV-Evasion

GitHubtanc7/exocet-av-evasion

EXOCET - AV-evading, undetectable, payload delivery tool
command-and-controlcryptographyeducation+9
8384 years ago
ransomware-simulator preview

ransomware-simulator

GitHubnextronsystems/ransomware-simulator

Safe ransomware simulation tool for testing antivirus detection. Simulates macro staging, volume shadow copy deletion, document encryption, and note…
defensive-toolseducationmalware-analysis+2
4834 years ago
maltrieve preview
Archived

maltrieve

GitHubkrmaxwell/maltrieve

A tool to retrieve malware directly from the source for security researchers.
crawlerinformation-gatheringmalware-analysis+2
5649 years ago
DanderSpritz_lab preview

DanderSpritz_lab

GitHubfrancisck/danderspritz_lab

A fully functional DanderSpritz lab in 2 commands
educationexploit-frameworkslabs-practice+5
4507 years ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k3 months ago
upx-recovery-tool preview

upx-recovery-tool

GitHubnozominetworks/upx-recovery-tool

Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…
binary-analysismalware-analysisreverse-engineering
1183 years ago
Uchihash preview

Uchihash

GitHubn1ght-w0lf/uchihash

A small utility to deal with malware embedded hashes.

binary-analysishash-analysismalware-analysis+2
522 years ago
Previous12…41Next